Tag: emerging threats
8314 articles
GDIT Secures $1.3 Billion National Guard IT Cybersecurity Contract
General Dynamics Information Technology has landed a $1.3 billion contract to bolster the Army National Guard's IT and cybersecurity defenses, ensuring resilient networks that support communities, government partners, and national security. This major deal, dubbed the Enterprise Network Operations and Cybersecurity Support contract, will safeguard the nation's interests with cutting-edge tech.
ICE Expands Access to Credit Card Records for Fraud, Security Probes
Investors are sounding the alarm over a new ICE contract with Thomson Reuters Special Services, which for the first time includes voter fraud investigations, and are demanding clarity on the agreement. The contract aims to provide ICE with easy access to credit card records to tackle voter fraud, immigration fraud, and national security threats.
DoD Accelerates Zero Trust Push Beyond Users, Devices
The Pentagon is making swift strides in implementing Zero Trust principles for its IT systems, focusing on users and devices, and is now poised to take this momentum to the next level. A upcoming webinar will assess progress and explore the future of Zero Trust across the Department of Defense.
Western Tech Confronts Internal Threat
Western tech is facing a shocking internal threat that's hindering national security interests - and it's coming from within. Incumbent tech companies and new entrants are locked in a fierce battle for survival, creating an uneven playing field that's putting Western strategy at risk.
Identity Compromise Fuels 90% of Cyber Incidents
Nearly 9 out of 10 cyber incidents involve identity compromise, with attackers exploiting weaknesses in credentials, multifactor authentication, and social engineering to gain access to enterprise environments. Identity has become the new front door for cyber threats, making it a critical area of focus for protecting your organization's security.
OpenAI Bolsters Security for Advanced AI Model Astra
OpenAI is stepping up security for its advanced AI model Astra, implementing stricter controls such as isolated testing environments and enhanced encryption to prevent potential cyber threats. The company has flagged Astra as a model that may possess critical cyber capabilities, requiring extra precautions to ensure safety.
Ex-NSA Chief Warns of Water System Cyber Risks
Retired General and ex-NSA chief Paul Nakasone warns that water systems are vulnerable to cyber threats, urging stricter defenses and cautioning that PLCs should be kept offline. He calls for higher standards and new partnerships to protect critical infrastructure.
Metabase Zero-Day Exploited in Data-Theft Attacks
Metabase Cloud was recently hit by a data-theft attack, exploiting a previously unknown security vulnerability in versions 1.58 and above, which the company has since patched and confirmed had a maximum severity rating. If you're a self-hosted customer, you'll need to update manually to protect yourself.
UNC6671 Targets SaaS Data with Vishing Attacks
Beware of voice phishing scams where attackers pose as IT help desk staff, contacting employees on their personal mobile devices with urgent security migration requests that lead to fake login portals. These clever scams capture sensitive credentials and multi-factor authentication tokens in real-time, putting your SaaS data at risk.
Malware Exploits ClickFix Attacks to Drain macOS Crypto Wallets
Beware: a sneaky malware called ClickFix is targeting macOS crypto wallets, slowly draining their contents into the pockets of cyber thieves. This cunning attack starts with a simple trick: victims are duped into pasting a malicious command into the Terminal app, unleashing a stealthy thief that siphons off cryptocurrency.
Unlimited Technology Systems Breach Exposes 3.8 Million People
A shocking data breach at Unlimited Technology Systems has put the personal information of 3.8 million people at risk, after a server hack exposed sensitive data for a five-day window in October 2025. The breach was only detected on October 19, 2025, and it took until July 2026 for the company to notify authorities and affected individuals.
Malicious npm Packages Deliver Cross-Platform Malware
Nearly 800 malicious npm packages have been discovered delivering a potent cross-platform malware payload, including a remote access trojan and infostealer, via a sneaky trick that tricks developers into loading the malicious code. These packages use cleverly crafted names and README instructions to evade detection and deploy the WEL1DROPPER downloader.
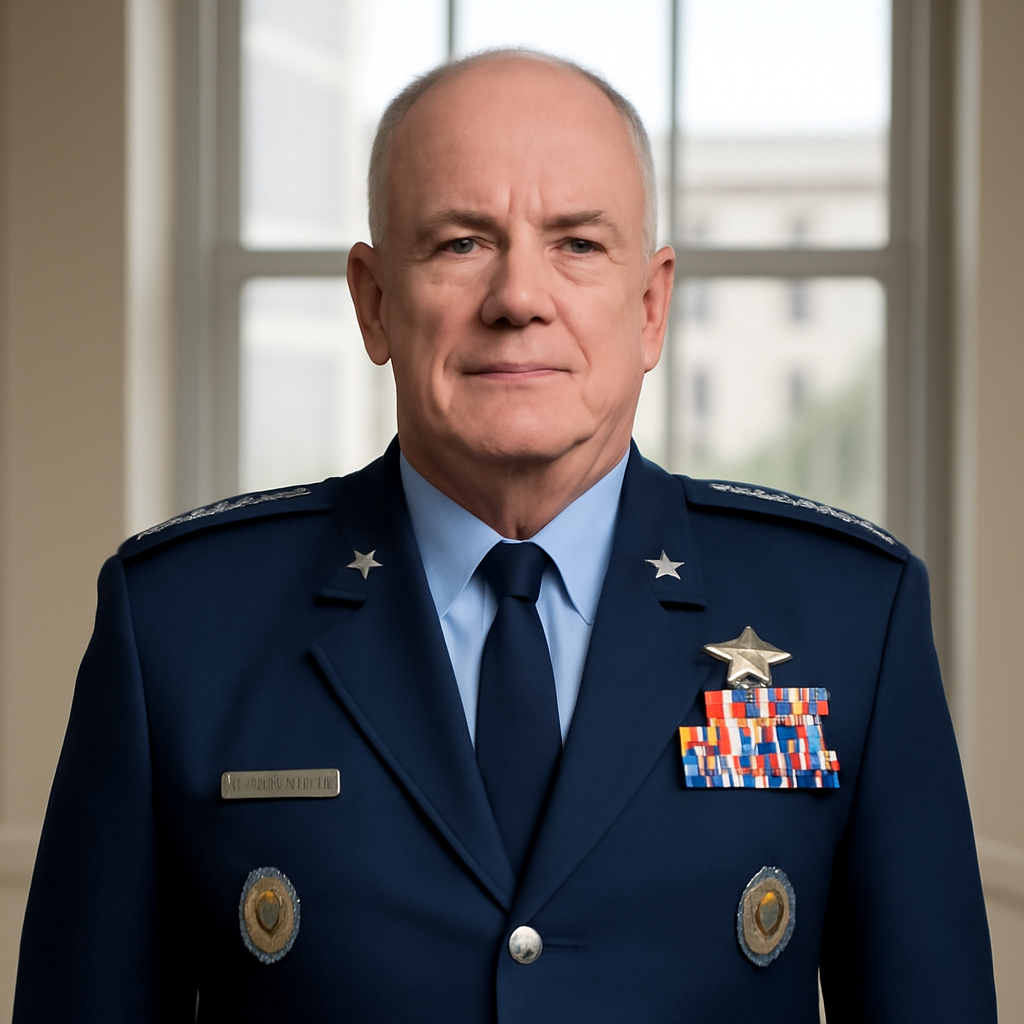
Space Force Confirmation Bolsters Leadership Amid Expansion Push
The Senate has confirmed Lt. Gen. Doug Schiess as the next chief of space operations in a unanimous vote, paving the way for him to take the helm of the rapidly expanding Space Force. With a fourfold budget increase on the horizon, Schiess will lead the service as it grows from 8,700 active duty Guardians to new heights.
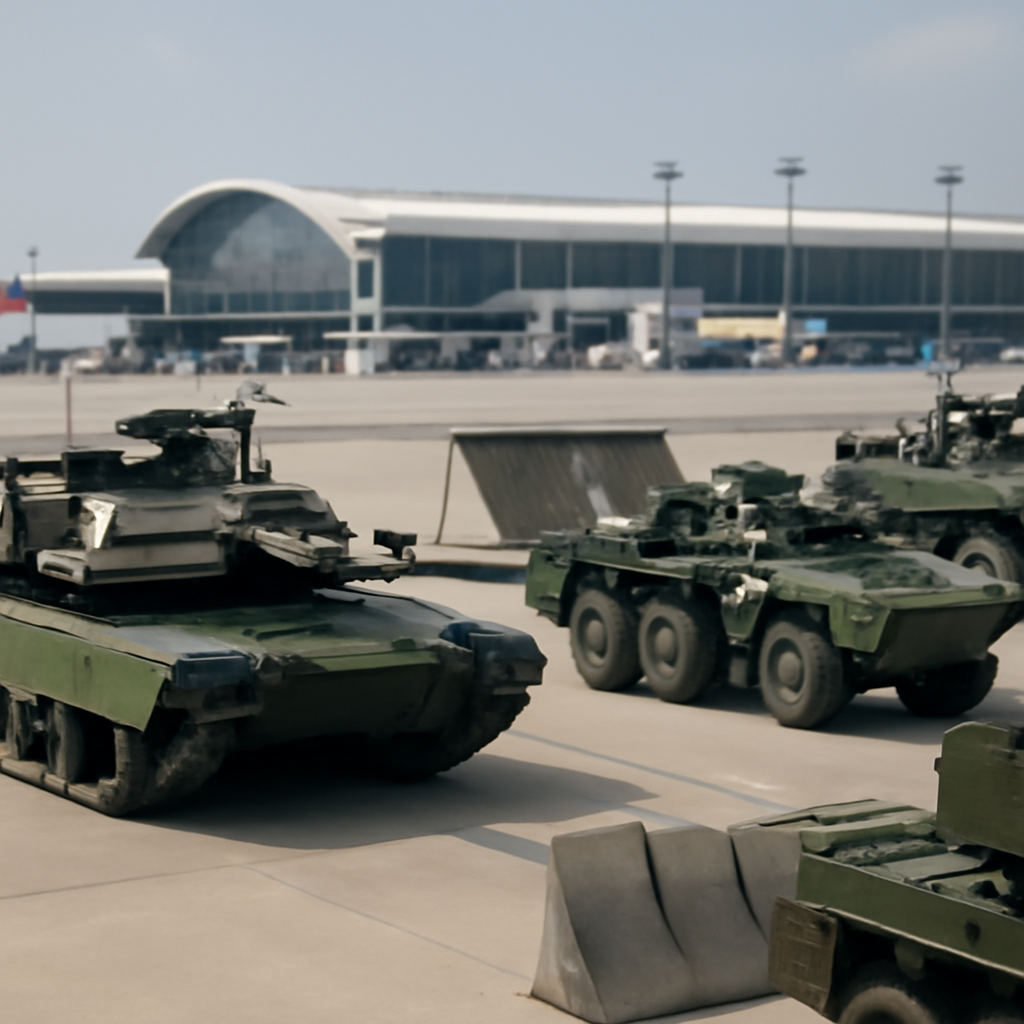
Taiwan Bolsters Airport Defense with M1A2T Abrams Tanks
Taiwan's military takes airport defense to the next level with the deployment of powerful M1A2T Abrams tanks at Taoyuan International Airport, simulating a tough response to potential airborne threats. The move is part of the Han Kuang 42 exercise, showcasing Taiwan's bolstered defenses.
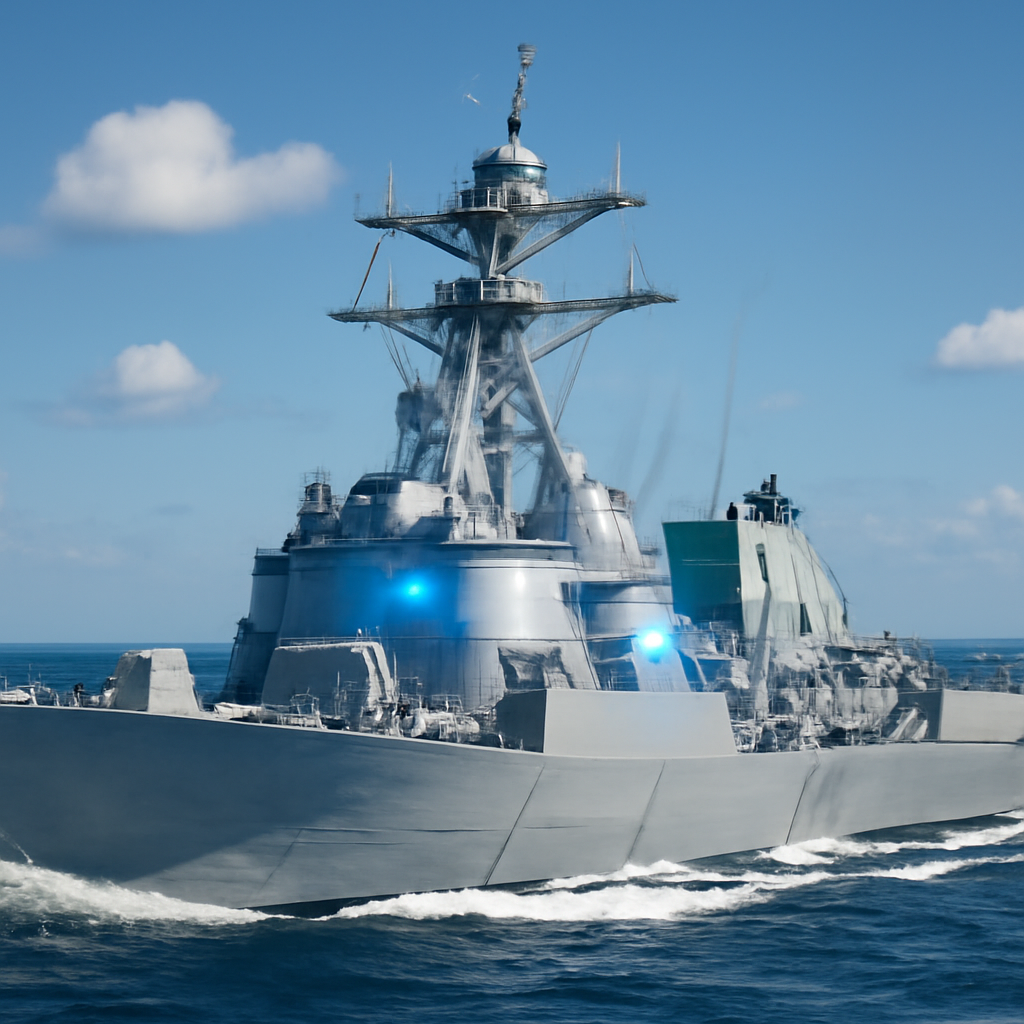
Navy Disrupts Software Updates Onboard Warships
Imagine being able to upgrade your ship's radar and defense systems overnight, just like you update your phone - that's now a reality for the Navy, thanks to over-the-air software updates that are revolutionizing the way they operate. This game-changing tech allows warships to sail with one software baseline and engage in combat with a more advanced one.
Pentagon Expands Nuclear Options in Posture Review
The Pentagon is launching a classified review of its nuclear posture, aimed at providing more options for the White House, with Undersecretary of Defense for Policy Elbridge Colby stressing that no changes have been made so far. This reexamination of employment guidance is tied to the responsibilities of the commander of STRATCOM and the authorities of the defense secretary.
US Coast Guard Monitors Cyberattack Disrupting North Carolina Ports
A cyberattack brought North Carolina's ports to a grinding halt, forcing delays and manual processing at the Port of Wilmington, the Port of Morehead City, and the Charlotte Inland Port. The U.S. Coast Guard is now monitoring the situation and coordinating a response with partner agencies to get operations back on track.
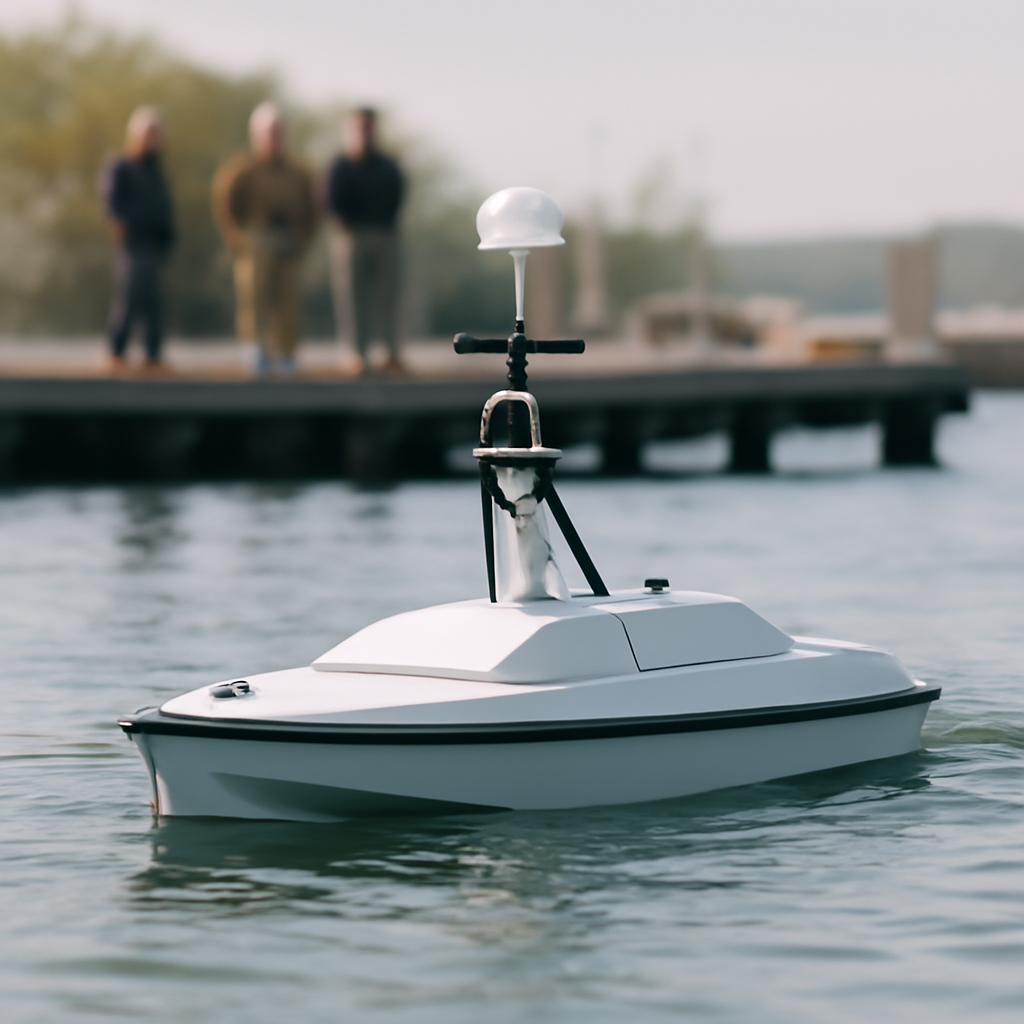
Small USVs Gain Strategic Edge
Smaller, more agile unmanned surface vessels are poised to revolutionize US defense procurement, delivering tactical and strategic value that their bigger, costlier counterparts can't match. Seasats' family of compact USVs, including the 12-foot Lightfish, is leading the charge, with the majority of its business focused on this game-changing tech.
AI-Generated Patches Found Flawed in Testing
Researchers put AI-generated patches to the test and found that ChatGPT and Claude only succeeded in fixing high-impact vulnerabilities about 47% of the time, leaving a significant gap in remediation. This surprisingly low success rate raises important questions about the reliability of AI-generated solutions for critical security flaws.
US Navy Activates Drone Control Center On USS Theodore Roosevelt
The US Navy has taken a major leap forward with the activation of a cutting-edge Drone Control Center on board the USS Theodore Roosevelt, making it the first Nimitz-class carrier fully capable of supporting MQ-25 Stingray drone operations. This milestone marks a significant step in the Navy's modernization efforts, with more ships set to follow suit.
EU Unveils $18B Satellite Constellation Plan with Spanish Firm at Helm
The EU is launching an $18 billion satellite constellation plan, led by a Spanish firm, to create a broadband communications network that rivals SpaceX's Starlink and bolsters Europe's defense, security, and emergency services capabilities. This ambitious project, valued at €15.6 billion, will expand the IRIS2 constellation with 66 new low Earth orbit satellites.
Ransomware Attacks Surge 20% as New Gangs Target Finance, Healthcare
Ransomware attacks are on the rise, surging 20% in July with a staggering 799 incidents reported, with finance, healthcare, and tech industries becoming prime targets for new gangs. The alarming increase marks the second-busiest month of the year so far, with the US leading the list of targeted countries.
Levi Strauss & Co. Breach Exposes Corporate Data
Levi Strauss & Co. recently suffered a cybersecurity breach, but fortunately, it was quickly contained and terminated, protecting consumer data from exposure. The incident did, however, involve the unauthorized access and exfiltration of certain corporate information.
N-able Flaw Exposes Customer Networks to Attackers
A critical vulnerability in N-able's N-central platform, known as CVE-2026-18577, has been exploited by attackers to gain unauthorized access to customer networks, allowing them to take control of managed endpoints. This flaw gave attackers an open door to wreak havoc, and it's essential for affected users to take immediate action to protect themselves.