Emerging Threats

Smartphone on a plain surface with blurred computer screen showing text messages in background.

Android Flaw Exploits SMS to Crash Unpatched Phones

A newly discovered Android flaw, dubbed the SMS of Death, allows attackers to remotely crash unpatched phones or disrupt cellular service with a single specially crafted text message, potentially even interrupting emergency calls. This zero-click vulnerability can wreak havoc without the victim even seeing the malicious message.

Analyst 207
Cryptocurrency office with employees in background, blurred screen in foreground.

Chainalysis Breach Exposes Customer Identity Data

A security breach at Chainalysis has compromised customer identity data, including user IDs, full names, email addresses, and organization role labels, after an external actor used AI-powered tools to gain unauthorized access to the company's internal systems. The incident highlights the vulnerability of even the most trusted players in the blockchain analysis space.

Analyst 207
Modern office setting with blurred data visualization on a wall-mounted display and personnel in the distance.

Chainalysis Exposes Data Breach from Sophisticated Agentic Techniques

Blockchain intelligence firm Chainalysis recently uncovered a sneaky data breach, where hackers used clever tactics to gain unauthorized access to its internal systems and sensitive user info. The breach exposed user metadata, including IDs, names, email addresses, and job roles, but thankfully, no evidence of compromised investigation content or login credentials was found.

Analyst 207
Industrial control system equipment fills a brightly-lit room, with a single device prominently displayed in the foreground.

Ivanti Flaws Chained to Yield Unauthenticated Root Access

A chain of Ivanti vulnerabilities can be exploited together to gain unauthenticated root access, posing a significant threat to security. This alarming exploit chain combines multiple flaws, including authentication bypass, remote code execution, and privilege escalation, to wreak havoc.

Analyst 207
Network operations center interior with rows of equipment and a single unoccupied workstation.

DDoS Attacks Surge as Threat Actors Exploit Booter Services

DDoS attacks are getting shorter and sneakier, with brief, low-bandwidth strikes under 10 minutes and 1 Gbps surging by a whopping 208%. This shift towards quick, compact attacks signals a new wave of automated and relentless threats.

Analyst 207
A somber older man sits in a formal setting with his hands clasped in front of him.

Defense Contractor Exposes North Korea's Remote Worker Scheme

Meet John Allen Kurrle Jr., a cleared defense contractor who got caught up in a shocking scheme: allowing others to use his identity and top-secret security clearance to land lucrative remote jobs with national security implications. He pleaded guilty to conspiracy to commit wire fraud after admitting to his role in a plot that produced 88 job applications and nine offers with salaries up to $190,000.

Analyst 207
Person sitting in quiet room with laptop, notebook, and coffee, with cityscape visible through window.

Apple Alerts 99 Countries to Mercenary Spyware Infections

Apple just alerted users in 99 countries to a sophisticated spyware threat that's targeting their devices, warning them of highly advanced digital attacks that are difficult to defend against. This latest notification wave brings the total number of countries affected to over 150.

Analyst 207
Modern tech lab with sleek workstation, laptop, and networked devices.

China-Backed Group Exploits AI Tool to Compromise 140 Targets

Meet Vapor Panda, a China-backed group that's taking threat actor tactics to the next level with AI-powered attacks, compromising 140 targets at lightning speed. This marks the first large-scale use of an "agentic" AI tool by a nation-state threat actor, and experts warn it won't be the last.

Analyst 207
Modern server room with rows of computer equipment and a partially open laptop in the center.

Ransomware Gang Exposes Tactics After $7K AI Splurge

A shocking security blunder has been uncovered: a ransomware gang spent over $7,200 on AI services, yet carelessly left their entire workspace exposed on a public server, revealing their clever - and questionable - tactics.

Analyst 207
Laptop and smartphone on a neutral surface with financial items nearby.

North Korea Targets Binance in $6.3B Crypto Heist

Binance revealed a staggering $6.3 billion crypto theft, but fortunately, deposits are still secure and the company is working to resume withdrawals soon. The hack was quickly addressed, with $3 billion in assets frozen and customer losses fully covered.

Analyst 207
Generic office building exterior with subtle network connectivity hints.

Chinese Hackers Deploy AI-Powered ARTEX to Breach 200 Global Targets

Meet Vapor Panda, a China-based hacking group that's been wreaking havoc on over 200 global organizations with an AI-powered tool called ARTEX, starting October 17, 2026. Their targets have included government ministries, defense agencies, and major industries across the globe.

Analyst 207
Developer workstation with laptop and monitor showing blurred coding interfaces in a quiet, empty space.

Anthropic Disputes Link to Malicious Claude Code Extension Compromise

Anthropic is investigating a malicious Claude Code extension with Cursor, confirming it wasn't a breach of their own systems or employee laptops. A bad actor hijacked Cursor's marketplace to publish a tampered extension, Anthropic says, which they didn't build or publish.

Analyst 207
Rows of rack-mounted servers and networking equipment in a brightly-lit server room with technicians working in the…

WordPress Sites Targeted in Widespread Exploitation of RCE Flaw

In just 24 hours, 62,969 attack attempts were blocked after patches were released for a high-severity WordPress flaw that allowed hackers to execute code on vulnerable sites. This widespread vulnerability, affecting WordPress Core versions 4.7 through 7.1.3, was fortunately fixed on October 28, 2026.

Analyst 207
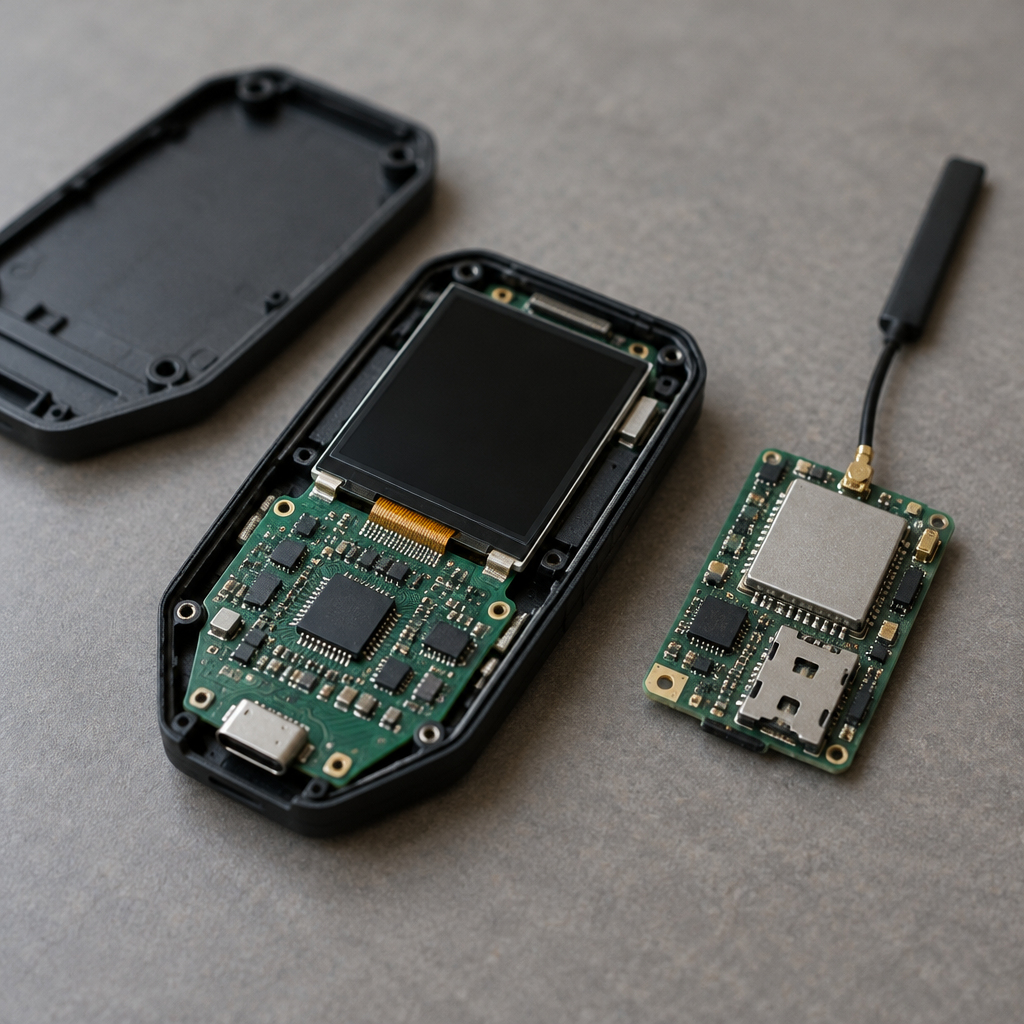
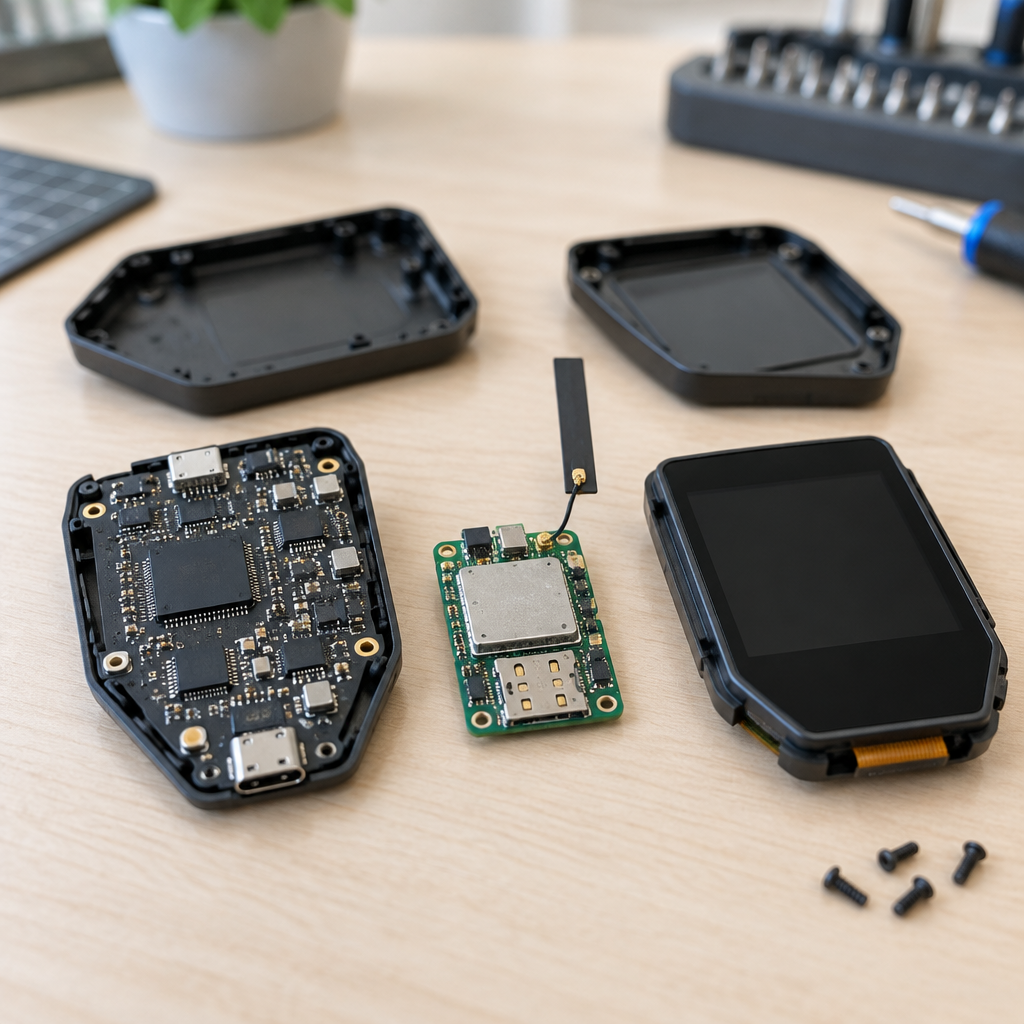
Disassembled Trezor hardware wallet with suspicious circuit board exposed.

Trezor Exposes Suspected Crypto-Theft Implant in Hardware Wallet Supply Chain

A Trezor Safe 5 hardware wallet purchased from a reseller in Southeast Asia was found to contain a suspicious extra circuit board with a cellular module and antenna, sparking concerns of a potential crypto-theft implant. This shocking discovery raises questions about the security of the supply chain and the safety of cryptocurrency storage.

Analyst 207
VS Code extension marketplace interface with blurred center panel on a developer's laptop screen.

Malicious Claude Code Extension Targets 5,000 Developers with SSH Backdoor

A malicious version of the popular Claude Code extension was compromised, putting 5,000 developers at risk of a persistent SSH backdoor malware that was served from a trusted VS Code marketplace for nearly 11 hours. The sneaky malware was cleverly hidden in a JavaScript loader, allowing it to execute immediately without requiring any user interaction.

Analyst 207
Dimly lit telephone booth with door ajar and phone off the hook.

Signaling Flaws Expose Millions to Phone Tracking, Hacking

Millions of people are vulnerable to phone tracking and hacking due to flaws in the signaling systems that route calls and texts, allowing attackers to intercept, impersonate, or silence phones without ever touching them. These attacks, uncovered by Citizen Lab, have targeted thousands of people in dozens of countries.

Analyst 207
Rows of computer servers and networking equipment in a brightly-lit server room with a single laptop in the foreground.

GitLab Flaw Exploited in Wild After CISA Warning

GitLab patched a critical flaw that allowed hackers to run malicious code on its servers, thanks to a warning from CISA. The vulnerability, known as CVE-2026-97229, was caused by a weakness in GitLab's CI/CD Regular Expression Compiler that wasn't properly validating user input.

Analyst 207
Disassembled Trezor wallet reveals suspicious extra circuit board with cellular module.

Trezor Exposes Possible Hardware Implant in Wallets Sold by CryptoBilis

Trezor has uncovered a potential security threat in some of its hardware wallets sold by CryptoBilis, revealing a possible hardware implant that could compromise users' sensitive information. A customer in Indonesia discovered an extra circuit board in their Trezor Safe 5 wallet, which could be sending confidential data, including wallet backups, over a mobile network.

Analyst 207
US government network operations room with concerned technicians amidst rows of computer servers and equipment.

Chinese Actor Exploits Chained Vulnerabilities to Breach US Government Network

In a shocking breach, a Chinese actor exploited a chain of vulnerabilities in under 15 minutes to gain persistent root access to 25 Palo Alto Networks servers and infiltrate a US government-affiliated Active Directory domain. The attack combined the PHP2Shell and Fragnesia exploits into a single, automated request, highlighting the devastating potential of chained vulnerabilities.

Analyst 207
Cryptocurrency exchange office with computer workstations and cityscape view.

Binance Discloses $6.3bn Hack, Foils $3bn in Stolen Funds

Binance revealed a massive $6.3 billion hack, but in a major win, the company managed to freeze around $3 billion of the stolen funds, ensuring customers won't bear the brunt of the loss. The crypto exchange is covering the losses from its own funds, reassuring users that their assets remain safe.

Analyst 207
Cluttered developer workspace with laptop and monitor, surrounded by coffee cups and notes near a window.

Malware Infects 5,000 via Compromised VS Code Extension

A malicious VS Code extension infected up to 5,000 users after the Cursor Marketplace was compromised, putting their systems at risk. The malware has since been removed and affected users will be contacted directly.

Analyst 207
E-commerce website backend on laptop with retail store background.

Drupal patches Commerce Core flaw under active exploitation

A critical flaw in the popular Commerce Core module, known as CVE-2026-118539, is under active exploitation - and Drupal is urging administrators to upgrade immediately to protect against potential financial losses. This vulnerability allows unauthenticated attackers to bypass access controls, putting your online store at risk.

Analyst 207
Laptop on cluttered workbench with blurred screen and city view through window.

Binance Crypto Heist Traced to North Korean Hackers

Binance's investigation reveals that the massive crypto heist, valued at $6.3 billion, was a sophisticated attack involving a compromised DevOps laptop and unauthorized access to a service container, rather than a simple one-click exploit. The exchange is still gathering facts, but has found no evidence of a leaked wallet private key.

Analyst 207
Retail checkout counter with terminal, cashier, and everyday shopping items.

Drupal Flaw Exploited Actively in Wild

Drupal warns of a highly critical flaw in its Commerce Core component that's already being exploited in the wild, allowing unauthorized access that could have serious financial implications. This vulnerability affects Commerce Core releases from 0.0.0 to 2.41 and 3.0.0 to 3.3.13.

Analyst 207