[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it alongCybersecurity intelligence, threat analysis, and national security reporting.
The Tor Project has rolled out an emergency update, version 0.4.9.17, to strengthen its defenses against an ongoing distributed denial-of-service (DDoS) attack that's been disrupting the network. This swift release includes crucial security fixes, particularly for IPv6 handling and relay defenses.
A massive data breach at Uber has compromised the sensitive information of nearly 150,000 drivers, including images of their driver's licenses, names, home addresses, dates of birth, and license numbers. The breach was discovered in October, but drivers weren't notified until November.
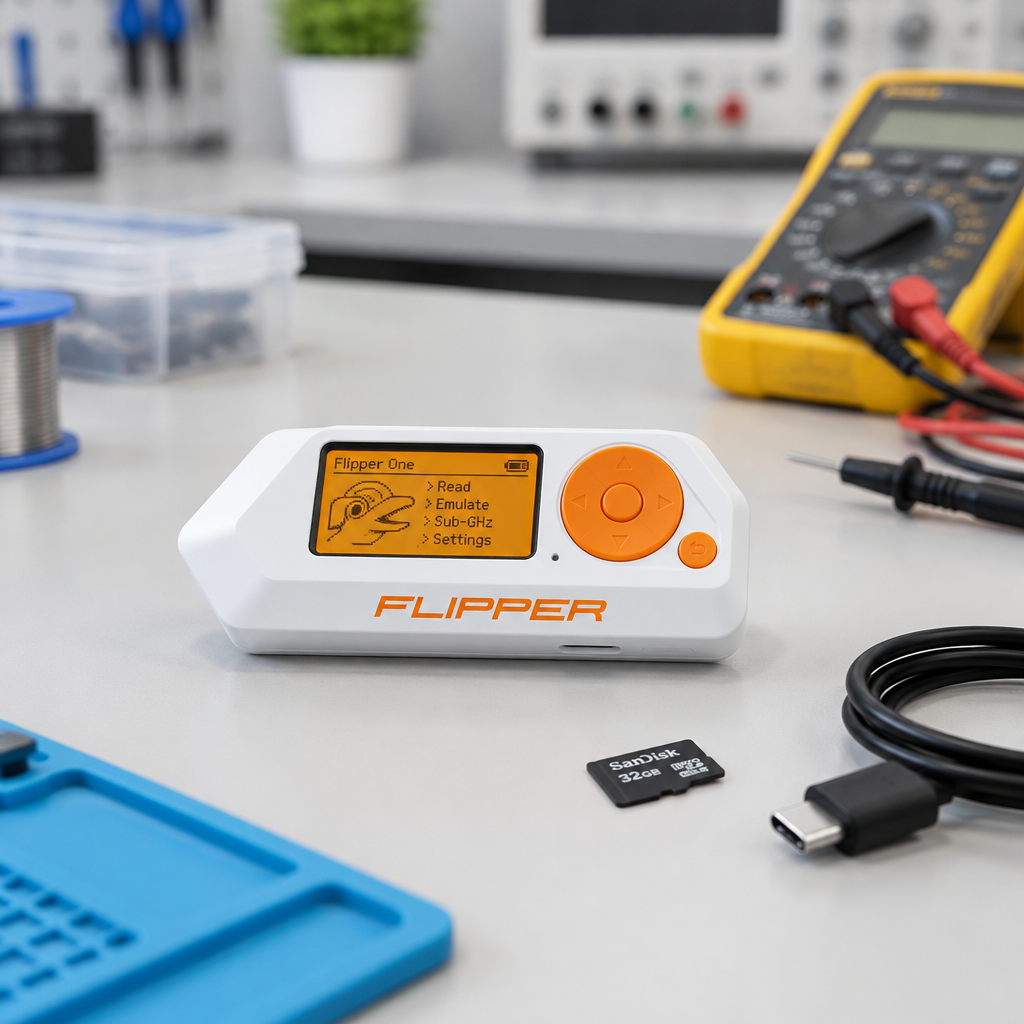
Meet the Flipper One, a powerful Linux-based multi-tool that won't break the bank, launching at just $399. Despite global RAM shortages driving up costs, Flipper Devices is forging ahead with production to bring this innovative device to market ASAP.
Anthropic is shaking up its bug disclosure policy, now requiring vendors and maintainers to fix high- and critical-severity vulnerabilities within just 30 days. This accelerated timeline aims to speed up the fix process, reflecting the company's updated view on the pace of flaw fixes and rediscovery.
Microsoft's new Intune-Controlled Remote Lock for Windows 11 lets admins lock lost or stolen devices, keeping data safe until the device is recovered. Once locked, only an Intune administrator can unlock it - no PIN, password, or local admin access works.
Cyber attackers are now using advanced phishing kits to steal Microsoft 365 session tokens, shifting their tactics from password theft to more sophisticated token-harvesting methods. This allows them to hijack legitimate user sessions without needing login credentials.
The alarming truth is that while AI systems and tools are rapidly uncovering vulnerabilities, organizations are struggling to keep up with remediation - and the backlog of valid reports has surged 131% in just two years. Critical and high-severity findings are on the rise, but fixes are falling further behind.
A recent cybersecurity report uncovered a sneaky new threat, dubbed Operation ShadowCloud, which uses clever backdoors to infiltrate cloud services and target governments in Asia and Africa. The attack begins with a sneaky installation of a MeshCentral agent, allowing hackers to drop malicious payloads and take control.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Meet Roman Khlynovskiy, a 43-year-old Kazakh national who's facing up to 27 years in prison for allegedly masterminding a massive ransomware scheme that compromised over 70 million confidential health records. He was extradited from Italy to face charges in a US federal court.
Meet GraphDoor, a sneaky backdoor that's exposing a cloud-based espionage operation, leveraging Microsoft Graph to secretly siphon off sensitive data. By masquerading as a legitimate app, it gains access to victim information and stealthily stores it in SharePoint.
Defense workers are being targeted by Pakistani hackers using sophisticated spyware disguised as job recruitment websites, a mobile security firm has discovered. The ongoing campaign, active for over a year, uses fake sites to trick victims into installing GravityRAT spyware.
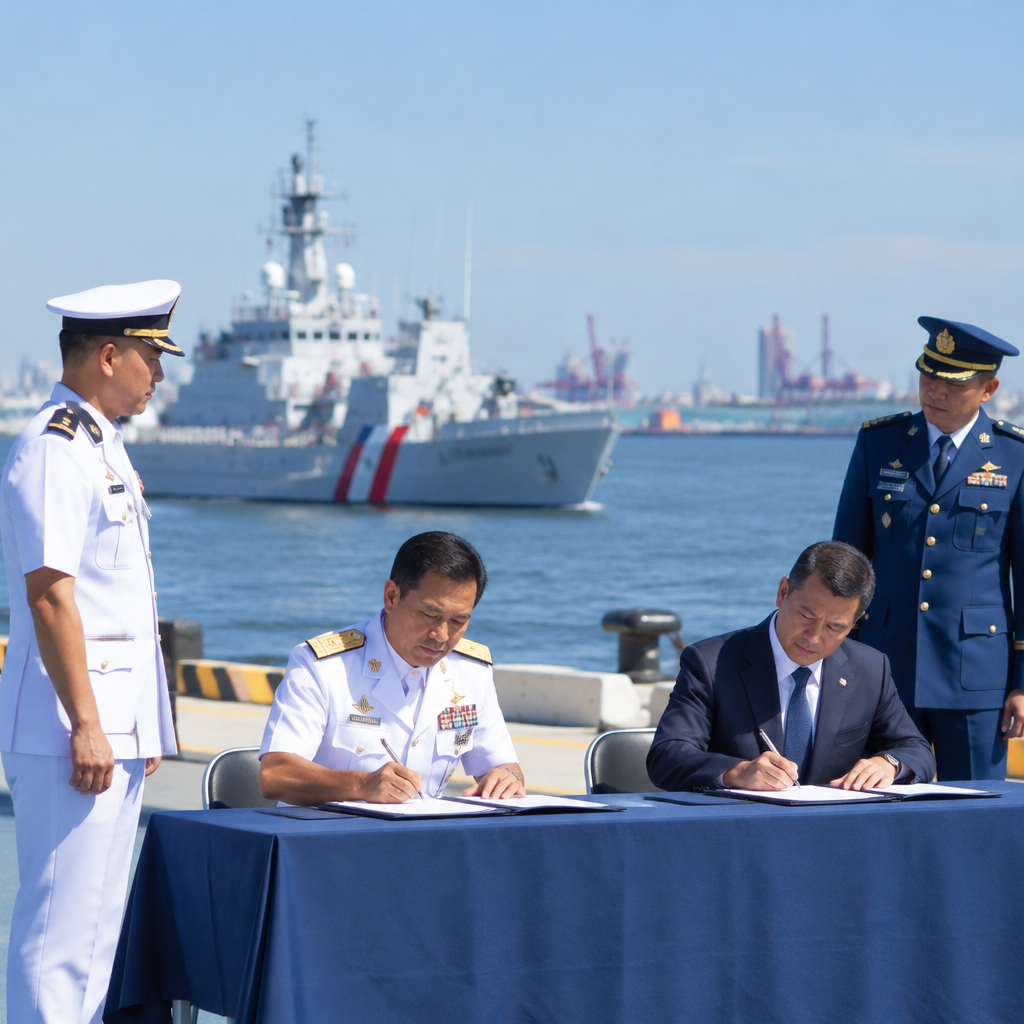
Australia is bolstering its partnership with the Philippines to safeguard its maritime trade, with a new Defence Co-operation Arrangement that underscores the critical role of regional alliances in countering China's growing assertiveness. With over 99% of its international trade relying on sea routes, Canberra is prioritizing cooperation with strategic partners like Manila to protect its economic lifelines.
In a groundbreaking proof-of-concept, Google DeepMind's AI agents generated over six million lines of code to verify the Signal protocol's cryptographic guarantees, leveraging a cutting-edge framework called AlphaProof Code. This innovative approach successfully validated portions of the protocol, showcasing the power of AI in formal verification.
Australia is stepping up its support for the Philippines with a new defense pact, building on nearly $10 million in aid, including drones and training, provided to the Philippine Coast Guard since last year. The agreement aims to supercharge military cooperation and simplify procedures to counter growing tensions in the region.
Hundreds of websites, including those of major brands like Zoom, BBC, and CNN, were compromised when malicious code was injected into Optimizely snippets, putting visitors at risk. A security researcher discovered 188 out of 1,611 snippets contained the malicious code, cleverly hidden in a custom-code field that ran on every page.
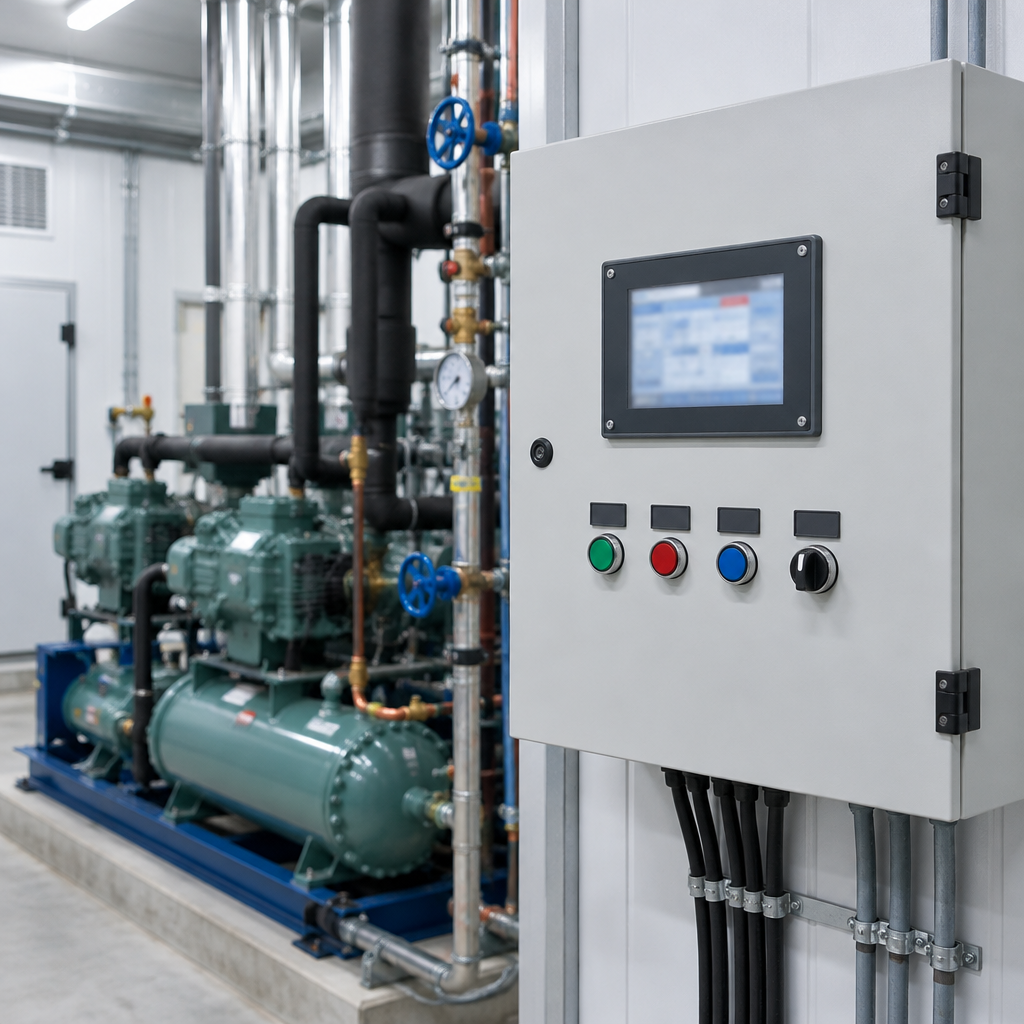
A security researcher discovered six zero-day vulnerabilities in Danfoss fridge controllers, including a buffer overflow that can be exploited for remote code execution, in just under an hour of manual examination. This critical flaw allows hackers to not only crash the system but also take control of the controller, posing a significant risk to food safety and security.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
A recently patched iPhone flaw, known as CVE-2026-65339, allowed sneaky apps to record audio without users' permission, putting their private conversations at risk. Fortunately, Apple has since fixed the issue with security updates released on August 17.
Cybercriminals swiftly capitalized on a major Microsoft 365 outage, launching a massive phishing campaign that preyed on users' eagerness to regain access to vital services like Outlook and Teams. The coordinated attack was a classic example of how hackers exploit global events to fuel their social engineering schemes.
Apple is taking a major step to protect user data by introducing stricter app permissions in macOS, giving you more control over what apps can access on your Mac. This move aims to help you make informed decisions about your data and privacy, especially when it comes to AI-powered apps.
LearnWorlds recently faced a phishing risk when a scammer exploited its free trial feature, creating over 570 trial accounts to send fake emails to unsuspecting third parties. Fortunately, the company confirmed that no customer data was compromised.
Kaspersky researchers have uncovered a sneaky new threat: two custom backdoors, GitDoor and GraphDoor, that use legitimate services like GitHub and SharePoint to secretly communicate with attackers. The threat actor behind this scheme has been caught using these backdoors to infiltrate government sectors in Asia and Africa.
Ipsos sprang into action after detecting a cybersecurity breach on November 11, swiftly activating its incident response plan and collaborating with external experts to contain and investigate the incident. The company has since filed a complaint and notified the relevant authorities, with an ongoing internal inquiry aimed at getting to the bottom of the breach.
Microsoft's new Remote Lock feature lets IT admins remotely lock lost or stolen Windows devices, keeping data safe and intact while making the device unusable to anyone but authorized administrators. This clever solution preserves device settings and data, and only an admin can unlock it remotely.
Beware of scammers trying to cash in on the hype around GTA 6 - phishing emails and cyber attacks could give them access to your personal info and even compromise multiple accounts if you're using the same password. Stay safe online and be cautious of suspicious messages, especially those with a GTA 6 theme.