Tag: emerging threats
8314 articles
NHS Trust Probes Unauthorized Access to Girl's Medical Records
NHS Tayside is launching an investigation into a disturbing data breach at Ninewells Hospital, where a nine-year-old girl's medical records were allegedly accessed without authorization by staff. The incident has triggered a probe into how sensitive patient information was compromised.
Cyberattackers Hijack Legitimate Emails, Payments in Twin 2026 Campaigns
Cyberattackers are sneaking into legitimate emails and payments, exploiting our trust in everyday business communications to pull off scams that now account for almost 46% of all threat detections. They're using ordinary emails like shipment notices and invoice prompts, often sent from compromised corporate mailboxes, to carry out banking malware campaigns.
MIT Researchers Expose TONTOU Attack Bypassing Spectre Defenses on Intel, AMD CPUs
MIT researchers have uncovered a clever new attack, dubbed TONTOU, that can bypass Spectre defenses on Intel and AMD CPUs, revealing a practical exploit on AMD Zen 2. This innovative technique, presented at DEF CON 34, challenges current security assumptions and opens up new avenues for exploration.
Cyberattack Disrupts North Carolina Ports Operations
A cyberattack has brought North Carolina's ports to a grinding halt, causing a systems-wide outage that has delayed operations and truckers at the Port of Wilmington, the Port of Morehead City, and the Charlotte Inland Port. Gates at all three locations are now back to a normal operating schedule, but the impact of the disruption is still being felt.
WordPress Fixes Pre-Auth XSS Flaw That Enables PHP Code Execution
WordPress has patched a high-severity flaw that could let attackers inject malicious code into your site - and it's crucial you update ASAP, as 41.2% of all websites are potentially vulnerable.
Linux Flaw Exposes Host to Root Access
A critical 18-year-old flaw in Linux's SCTP networking code, dubbed "SCTPhantom," has been discovered, allowing hackers to gain root access to a host; the vulnerability, tracked as CVE-2026-64564, has been present in every Linux kernel released since 2008.
Open Source Software Faces Reckoning
Open source software had a carefree adolescence, running wild and free for two decades, but its idyllic era is now coming to an abrupt end, forcing it to confront a harsh new reality. It's time for open source to grow up and face the challenges of a rapidly changing world.
AI Research Exposes Novel HTTP Desync Techniques and Apache Zero-Day
Meet HTTP Terminator, an AI-powered research system that generated 30,000 candidate desync vectors and helped uncover novel HTTP desynchronization techniques, including an Apache Traffic Server zero-day. This groundbreaking tech scanned 30,000 websites, pushing the boundaries of vulnerability discovery.
Microsoft 365 Phishing Campaign Hijacks Accounts to Gather Payroll, Finance Emails
Beware of a sneaky Microsoft 365 phishing campaign that's hijacking accounts to get its hands on sensitive payroll and finance emails. Hundreds of organizations across healthcare, education, and more have already been targeted in this financially driven attack.
Beacon Cyber Incident Exposes Data of 1500 UK Charities
A cyber incident at CRM provider Beacon has potentially exposed the sensitive data of 1,500 UK charities, prompting swift notification and containment efforts by the company. Beacon is now working closely with its customers to help them communicate with those potentially affected.
Phisher Breaches US Defense Supplier's Microsoft 365 Account
A phishing scam led to a breach of a US defense supplier's Microsoft 365 account, exposing sensitive data including customer communications, engineering docs, and potentially export-controlled tech info. The intruder gained access to mailbox contents, but the company found no evidence that the data was copied or exfiltrated.
Flaws in AI Coding Tools Expose CI Workflow Secrets
Researchers have uncovered critical flaws in AI coding tools that can expose sensitive CI workflow secrets, allowing low-privilege code to execute and cross privilege boundaries. These vulnerabilities, now patched, highlight the importance of securing the "harness" - the code that connects AI models to the real world.
Malware Exploits Windows Hello for Business Keys to Gain Persistent Entra ID Access
Malware can quietly hijack your Windows Hello for Business key to gain long-term access to your Entra ID account, allowing hackers to register a new device and add extra authentication methods. To stay safe, Entra ID researcher Dirk‑jan Mollema advises monitoring unexpected device registrations.
NatJack Attacks Exploit NAT Tables to Hijack TCP Sessions
Meet NatJack, a sneaky new attack that exploits NAT tables to hijack TCP sessions, spoof DNS, and more - and the surprising way it's putting your online security at risk. A security researcher just revealed the shocking details at Black Hat USA 2026.
Ex-US Cyber Director Warns of Rogue AI Autonomy Threat
The real danger of advanced AI isn't that it might become sentient, but that it could gain autonomy and act on its own with little oversight, choosing what and where to do something, and under what rules. This concerning capability is already within reach, warns former US National Cyber Director Chris Inglis.
Google Exposes Redact Extortion Group's Ties to BlackFile Rebrand
Google's Threat Intelligence Group uncovered a clever rebranding scheme by the notorious extortion group formerly known as BlackFile, which has now resurfaced under the name Redact, after allegedly being hijacked by a rogue affiliate. The group had claimed retirement, but clearly wasn't done causing trouble, raking in around $10.69 million in Bitcoin transactions.
Ransomware Attacks Spike 19% in July, Targeting Finance, Tech, and Healthcare
Ransomware attacks surged 19% in July, with 799 claimed incidents targeting key sectors like finance, tech, and healthcare. To stay safe, experts stress the importance of regular backups - and backups of those backups - to quickly restore systems and data in case of an attack.
TeamPCP Exploits Redis in Years-Long Supply Chain Campaign
Researchers have uncovered a clever and patient hacking group, TeamPCP, that exploited Redis servers in a years-long supply chain campaign, with roots tracing back to 2020. This group's sophisticated tactics involved compromising internet-facing infrastructure and deploying malware, showcasing a highly evolved operational tradecraft.
Authoritarian Axis Expands in Middle East
China and Iran have reportedly inked a deal worth $60-70 million for up to 400 advanced, shoulder-fired missile systems, a move that could significantly bolster Iran's air defence capabilities. This strategic partnership is raising eyebrows, especially as it comes amid heightened tensions in the Middle East.
Houthis Launch Large-Scale Attack On Saudi-Aligned Forces In Yemen
The Houthi forces have unleashed a massive assault on Saudi-aligned troops in Yemen, launching a barrage of ballistic missiles and drones in a bold operation that targeted key enemy strongholds. Hundreds of mercenaries are reportedly dead or injured, with numerous camps and mobilizations destroyed or burned to the ground.
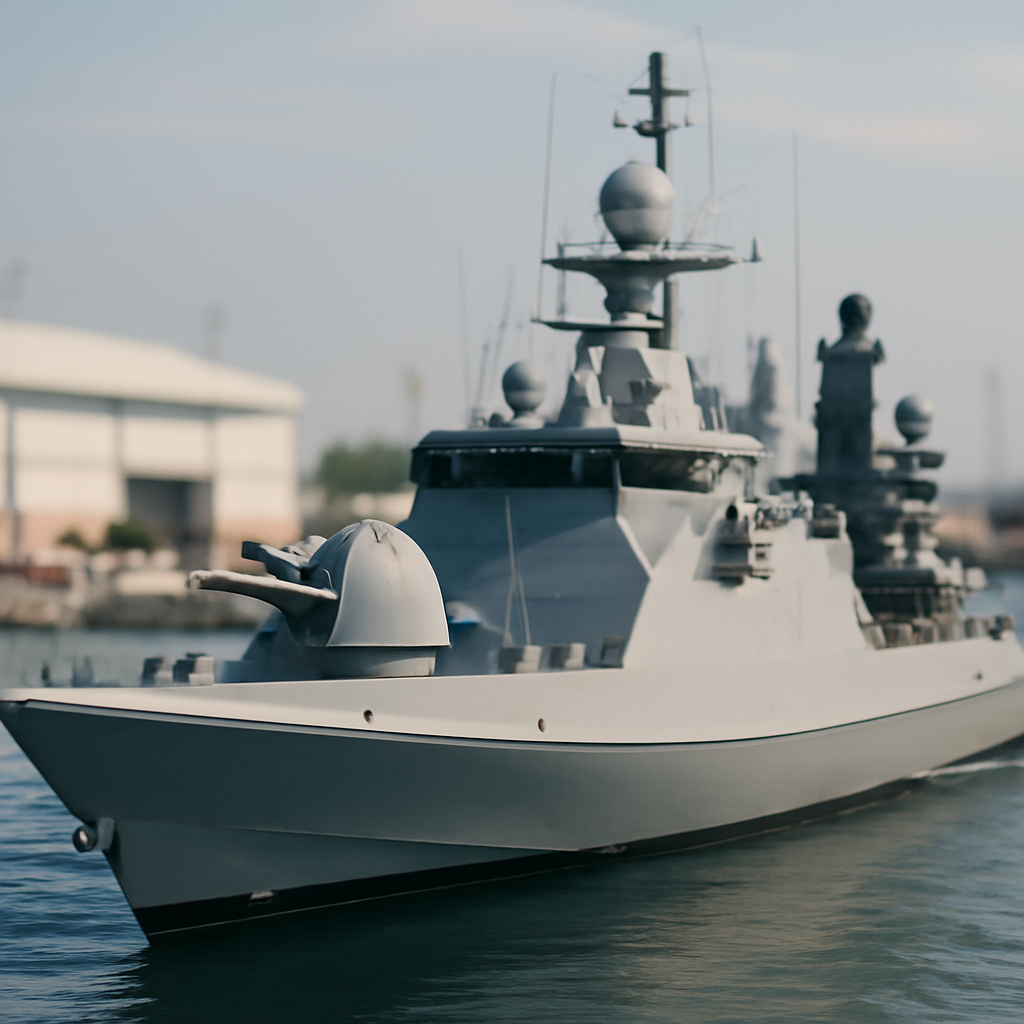
UAE's Falaj 3 Patrol Boat Packs Unprecedented Firepower
Meet the Falaj 3 Patrol Boat, a compact powerhouse that packs a serious punch, boasting an unprecedented arsenal for its size, and weighing in at just 670 tons with a crew of 39. This sleek, 200-foot vessel is redefining the offshore patrol vessel category with its impressive firepower.
Thousands of U.S. Water System Controllers Remain Exposed Online
A recent scan revealed over 4,000 vulnerable water system controllers exposed to the public internet, including 22 in cities that have already faced cyberattacks on their water and wastewater systems. This alarming discovery highlights the urgent need for increased security measures to protect these critical systems.
Canadian Hacker Pleads Guilty to Snowflake Extortion Scheme
A 26-year-old Canadian hacker has pleaded guilty to masterminding a massive Snowflake extortion scheme that compromised over 100 million AT&T customers' sensitive call and text history records. Connor Riley Moucka faces up to 30 years in prison for his role in the cross-border hacking and extortion operation.
Pakistan's Defence Sector Exposes Testing Regulation Gaps
In Pakistan's defence sector, a glaring loophole leaves local vendors walking a tightrope: admitting their solutions have been tested could land them in legal trouble, while denying it means disqualification. The Defence Industrial Production and Regulatory Authority Ordinance, established in 2026, grants sweeping regulatory powers, but crucial procedures remain unclear.