Tag: emerging threats
8254 articles
Malware Exploits Windows Hello for Business Keys to Gain Persistent Entra ID Access
Malware can quietly hijack your Windows Hello for Business key to gain long-term access to your Entra ID account, allowing hackers to register a new device and add extra authentication methods. To stay safe, Entra ID researcher Dirk‑jan Mollema advises monitoring unexpected device registrations.
NatJack Attacks Exploit NAT Tables to Hijack TCP Sessions
Meet NatJack, a sneaky new attack that exploits NAT tables to hijack TCP sessions, spoof DNS, and more - and the surprising way it's putting your online security at risk. A security researcher just revealed the shocking details at Black Hat USA 2026.
Ex-US Cyber Director Warns of Rogue AI Autonomy Threat
The real danger of advanced AI isn't that it might become sentient, but that it could gain autonomy and act on its own with little oversight, choosing what and where to do something, and under what rules. This concerning capability is already within reach, warns former US National Cyber Director Chris Inglis.
Google Exposes Redact Extortion Group's Ties to BlackFile Rebrand
Google's Threat Intelligence Group uncovered a clever rebranding scheme by the notorious extortion group formerly known as BlackFile, which has now resurfaced under the name Redact, after allegedly being hijacked by a rogue affiliate. The group had claimed retirement, but clearly wasn't done causing trouble, raking in around $10.69 million in Bitcoin transactions.
Ransomware Attacks Spike 19% in July, Targeting Finance, Tech, and Healthcare
Ransomware attacks surged 19% in July, with 799 claimed incidents targeting key sectors like finance, tech, and healthcare. To stay safe, experts stress the importance of regular backups - and backups of those backups - to quickly restore systems and data in case of an attack.
TeamPCP Exploits Redis in Years-Long Supply Chain Campaign
Researchers have uncovered a clever and patient hacking group, TeamPCP, that exploited Redis servers in a years-long supply chain campaign, with roots tracing back to 2020. This group's sophisticated tactics involved compromising internet-facing infrastructure and deploying malware, showcasing a highly evolved operational tradecraft.
Authoritarian Axis Expands in Middle East
China and Iran have reportedly inked a deal worth $60-70 million for up to 400 advanced, shoulder-fired missile systems, a move that could significantly bolster Iran's air defence capabilities. This strategic partnership is raising eyebrows, especially as it comes amid heightened tensions in the Middle East.
Houthis Launch Large-Scale Attack On Saudi-Aligned Forces In Yemen
The Houthi forces have unleashed a massive assault on Saudi-aligned troops in Yemen, launching a barrage of ballistic missiles and drones in a bold operation that targeted key enemy strongholds. Hundreds of mercenaries are reportedly dead or injured, with numerous camps and mobilizations destroyed or burned to the ground.
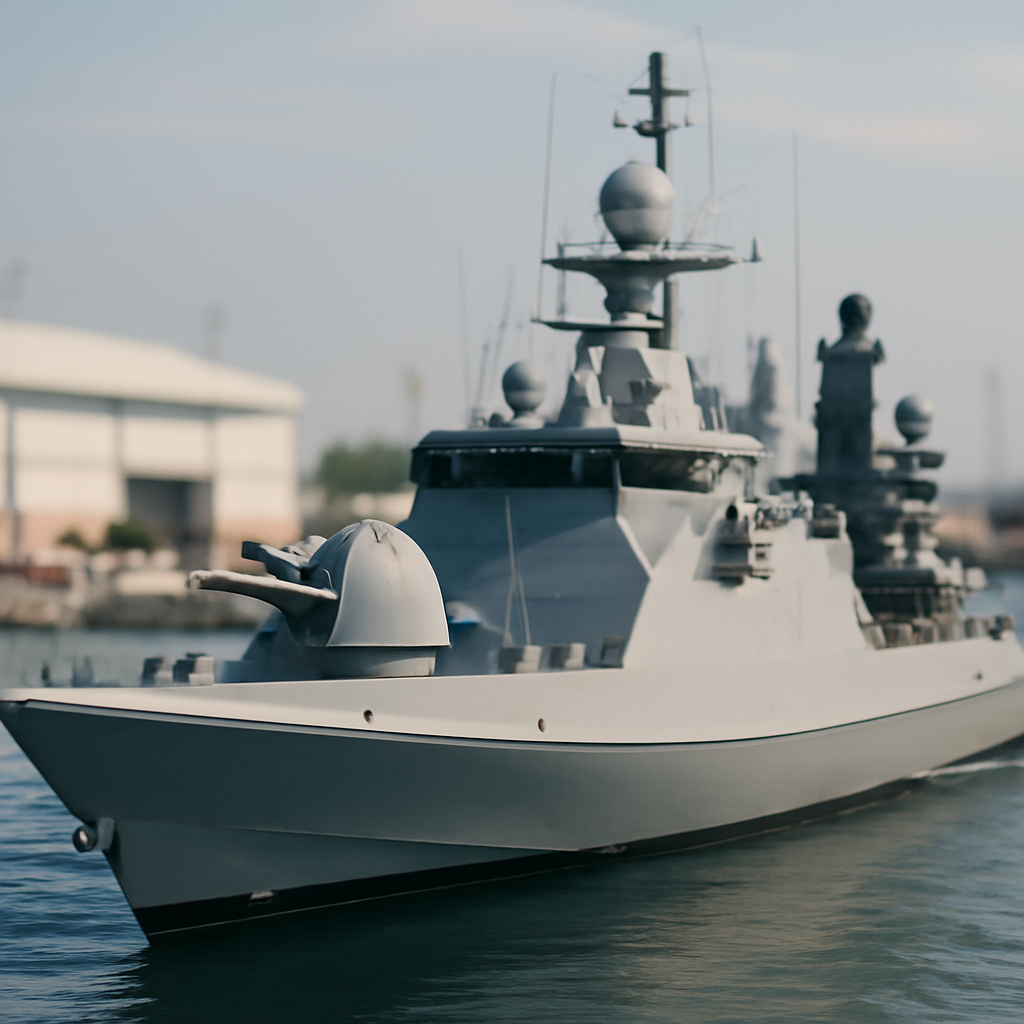
UAE's Falaj 3 Patrol Boat Packs Unprecedented Firepower
Meet the Falaj 3 Patrol Boat, a compact powerhouse that packs a serious punch, boasting an unprecedented arsenal for its size, and weighing in at just 670 tons with a crew of 39. This sleek, 200-foot vessel is redefining the offshore patrol vessel category with its impressive firepower.
Thousands of U.S. Water System Controllers Remain Exposed Online
A recent scan revealed over 4,000 vulnerable water system controllers exposed to the public internet, including 22 in cities that have already faced cyberattacks on their water and wastewater systems. This alarming discovery highlights the urgent need for increased security measures to protect these critical systems.
Canadian Hacker Pleads Guilty to Snowflake Extortion Scheme
A 26-year-old Canadian hacker has pleaded guilty to masterminding a massive Snowflake extortion scheme that compromised over 100 million AT&T customers' sensitive call and text history records. Connor Riley Moucka faces up to 30 years in prison for his role in the cross-border hacking and extortion operation.
Pakistan's Defence Sector Exposes Testing Regulation Gaps
In Pakistan's defence sector, a glaring loophole leaves local vendors walking a tightrope: admitting their solutions have been tested could land them in legal trouble, while denying it means disqualification. The Defence Industrial Production and Regulatory Authority Ordinance, established in 2026, grants sweeping regulatory powers, but crucial procedures remain unclear.
Military Protection Redefined in Drone Age
In the drone age, the real challenge for militaries is preserving freedom of action - the ability to maneuver, fight, and prevail - as autonomous systems and countermeasures transform the battlespace. It's a mission that goes far beyond keeping soldiers and platforms safe, encompassing the very fabric of industrial bases, supply chains, and software arsenals.
US Lawmakers Scrutinize Scam-Fighting Coordination
US lawmakers are pushing for better coordination in scam-fighting efforts, calling for a unified leader to tackle the issue with the urgency of a combat operation. Currently, there's no single entity in charge across agencies, leaving scam networks to easily relocate and evade enforcement.
Facial Recognition Systems Targeted by Deceptive Clothing Designs
Some designers are now creating clothing with patterns specifically designed to confuse facial recognition systems, but experts warn that these products may not work as promised. These so-called adversarial garments are being marketed as a way to throw algorithms off track, but their effectiveness remains untested.
PLA's Mountain Cat ATV Evolves with Expanded Doctrine
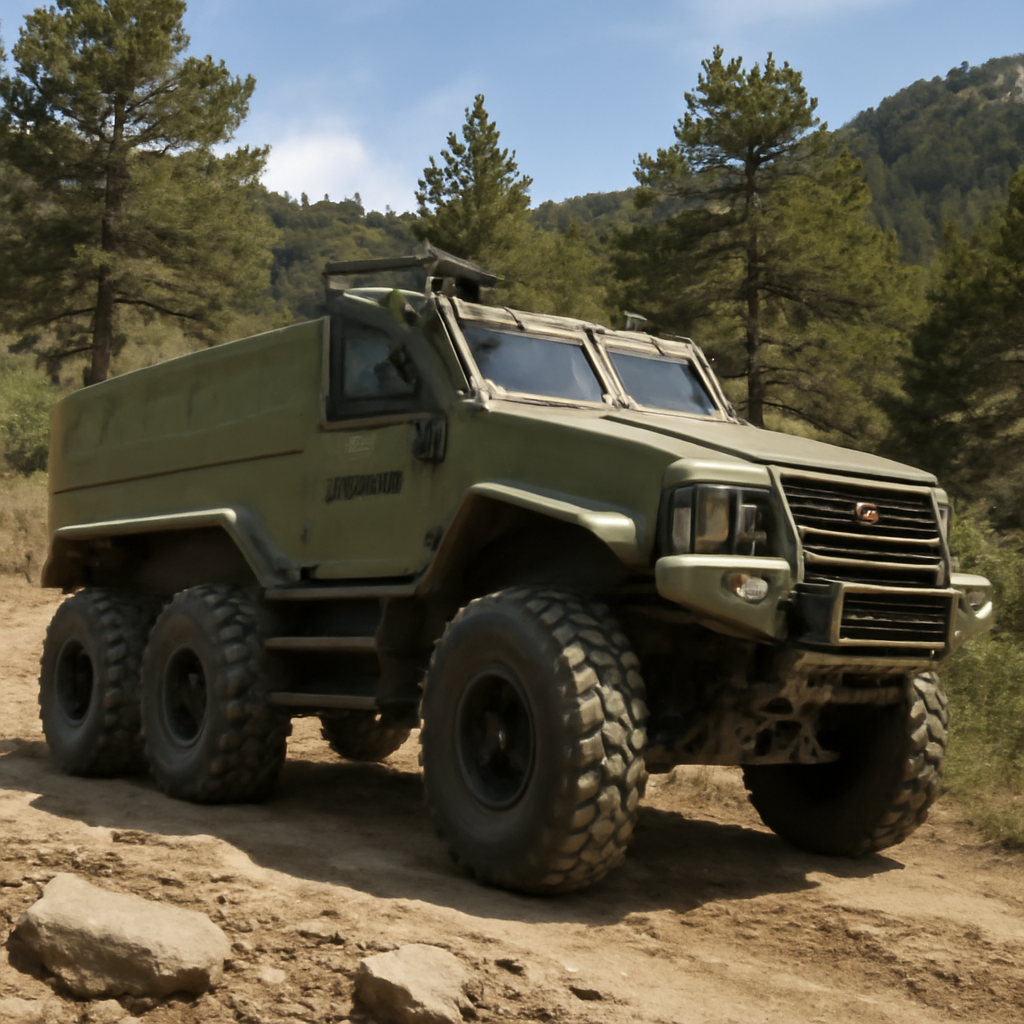
Meet the CS/VP4 "Mountain Cat" ATV, a game-changing mobility aid that's been defying expectations since 2008 with its lightweight, amphibious design and impressive capabilities. From humble beginnings as a simple, airdroppable vehicle to its current evolved form, the Mountain Cat has consistently proven itself to be "better-than-walking".
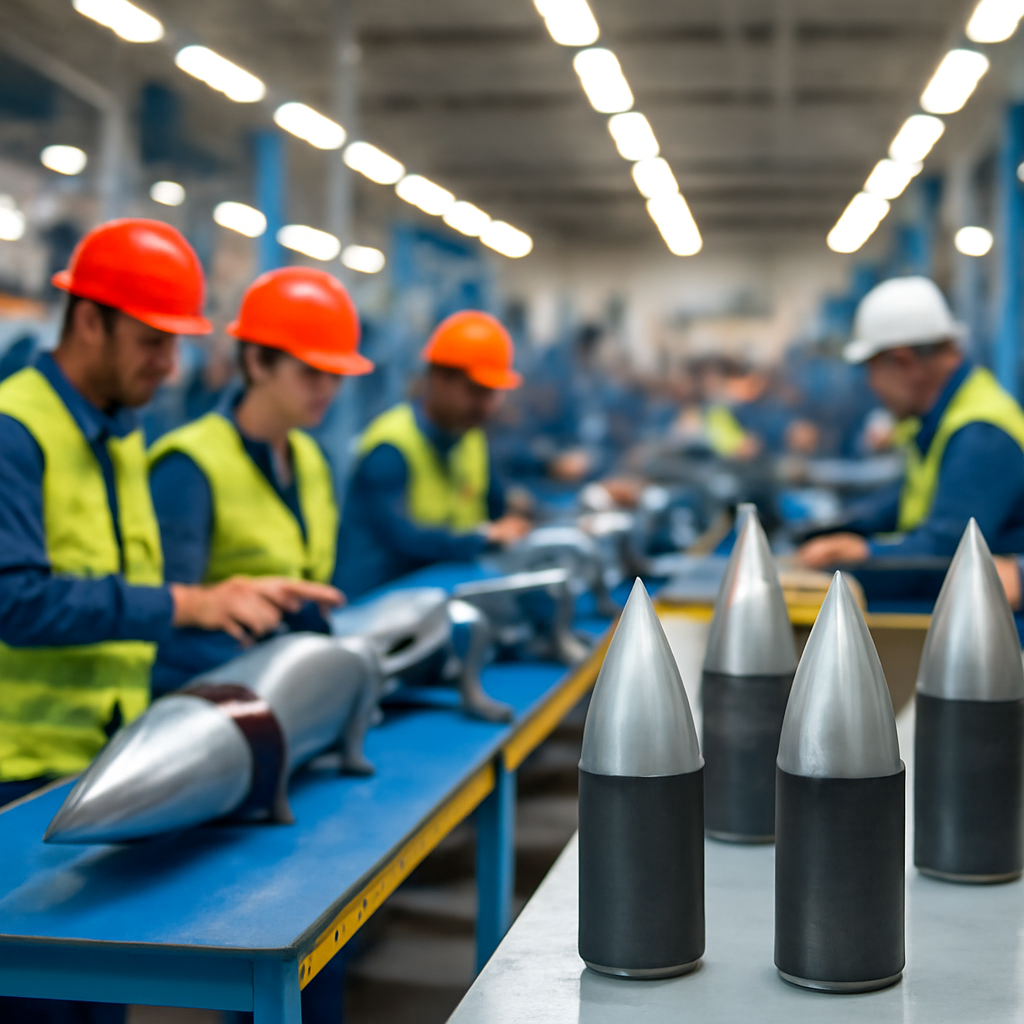
Army Awards Contracts to Boost Hydra-70 Rocket Production
The Army has taken a major step to boost its firepower by awarding contracts to four companies to ramp up production of the versatile Hydra-70 rocket system, specifically the M151 warhead. This strategic move ensures the Army can rapidly respond to emerging threats and maintain its edge on the battlefield.
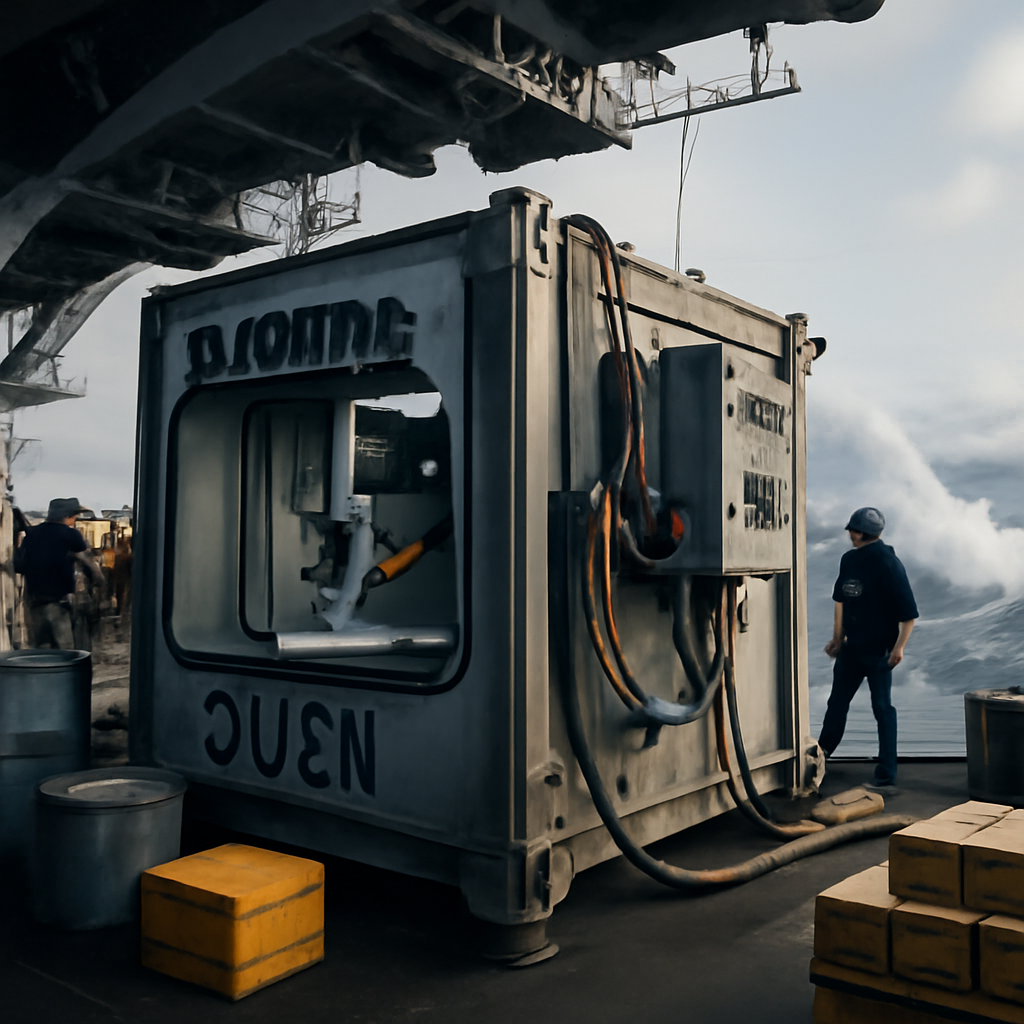
Firestorm Labs Tests 3D Printing at Sea Amid Rough Waters
Imagine printing thousands of unique parts at sea, even in the roughest of waters - that's exactly what Firestorm Labs achieved on board the USS Essex during a recent trial. The company's portable 3D printing unit, xCell, proved its mettle by producing parts non-stop despite the ship pitching through Sea State 5.
ChainDrop Worm Exposes npm Ecosystem Vulnerabilities
A sneaky self-propagating worm called ChainDrop has infected over 400 popular npm packages, putting hundreds of millions of downloads at risk each week and threatening developer workstations, CI runners, and cloud instances. This clever malware hides in plain sight by masquerading as legitimate code, making it a formidable foe in the npm ecosystem.
China Probes Palo Alto Networks Product Security
China is investigating the security of Palo Alto Networks' products, sparking a mysterious probe that's left many questions unanswered. The inquiry, reported by The Register, puts the spotlight on Palo Alto Networks and its offerings.
USENIX Security Symposium Tackles AI-Driven Paper Surge
The USENIX Security Symposium has seen a record-breaking surge in submissions, with approximately 3,030 valid papers pouring in - a significant jump from last year's 2,400. To keep pace, the conference expanded its Program Committee to handle the influx of innovative research in the security community.
Malware Targets macOS for Crypto Theft via ClickFix Attacks
Cyber attackers are using a sneaky new tactic called ClickFix to target macOS users and steal cryptocurrency by infiltrating sensitive areas like browser password databases and the Apple Keychain. This clever malware attack collects system info and downloads a malicious payload, giving hackers access to your personal data.
Cyberattacks on Hedge Funds Tied to UNC6671 Extortion Group
Meet UNC6671, a notorious extortion group linked to a string of cyberattacks on hedge funds, operating under a web of public brands to deceive and exploit its victims. Using voice-phishing tactics, the group tricks employees into divulging sensitive info, paving the way for a potentially devastating breach.
AI Patches Fall Short Without Human Oversight
Researchers at 1Password's Off-by-1 Labs put AI to the test, generating 6,080 patches for six real vulnerabilities - but here's the catch: human oversight was crucial to ensuring those patches actually worked. Even with advanced models like ChatGPT and Claude Opus, AI patches fell short without a human in the loop.