Tag: command and control
68 articles
Army Awards $94M for NGC2 Applications to Bolster Command and Control
The Army is taking a major leap forward in command and control capabilities, awarding $93.6 million in contracts to nine top companies to develop core software applications for its Next Generation Command and Control (NGC2) initiative. This critical investment lays the groundwork for rapid scalability, training, and unified force operations.
Malware Exploits AI Systems with 'Adversarial Poetry
Meet the first-ever malware that uses a clever trick - a poem - to hijack AI systems and steer them to its command center, cleverly hidden in a forked GitHub repository. This sneaky tactic was uncovered by Lumen's Black Lotus Labs, revealing a new level of sophistication in cyber threats.
PoeLLM Malware Exploits Poem to Fuel Growing Botnet
Meet PoeLLM, a sneaky malware that's hijacked over 3,400 servers since April by cleverly extracting command-and-control addresses from a harmless-sounding poem on GitHub. This cunning botnet uses a poem-based system to stay one step ahead - but its unique approach also makes it vulnerable to takedown.
Unified IT Foundation Drives Golden Dome's Speed to Mission
The real challenge lies in breaking down silos and bringing together disparate capabilities into a unified architecture - and that's exactly what the Golden Dome program aims to achieve as a "system of systems". By integrating sensors, interceptors, and other elements across services and agencies, Golden Dome is revolutionizing the way we operate.
CloudSyncD Backdoor Exploits Zoom Installer to Infiltrate MacOS Systems
Meet CloudSyncD, a sneaky backdoor that's exploiting the Zoom installer to secretly infiltrate MacOS systems. This cleverly disguised malware can masquerade as a legitimate Zoom installer, putting your system at risk.
US Army Accelerates C2 Superiority to Counter Electronic Warfare Threats
Recent conflicts, like those in Ukraine, have shown that disrupting enemy communications and command networks can give forces a game-changing advantage without needing to destroy a large number of enemy platforms. This insight was shared by Joshua Carson, Director of Business Development at Chenega IT Enterprise Solutions (CITES), at the TechNet Augusta 2026 conference.
US Army Bolsters Counter-Drone Arsenal with $7 Billion Contracts
The US Army is ramping up its defense against rogue drones with a $7 billion contract haul, aiming to bolster its counter-drone capabilities with cutting-edge sensors, effectors, and command systems. This massive investment will enable the Army to stay ahead of emerging threats and protect its personnel and assets more effectively.
RatHat Malware Evolves with AI-Powered Command Center
RatHat Malware is rapidly evolving with an AI-powered command center, having undergone three major command-and-control infrastructure updates in just six months, with nearly 100 deployments since April 2026. This malware-as-a-service model is getting smarter and more aggressive by the day.
PamStealer Malware Evolves with Live C2 Decryption and Enhanced Persistence
Meet the latest variant of PamStealer malware, which has evolved with a sneaky new trick: it can only be decrypted through a live command-and-control session, making it even harder to track and stop. This fresh threat uses a fake cryptocurrency wallet site, wavel.app, to lure victims into downloading a malicious disk image file.
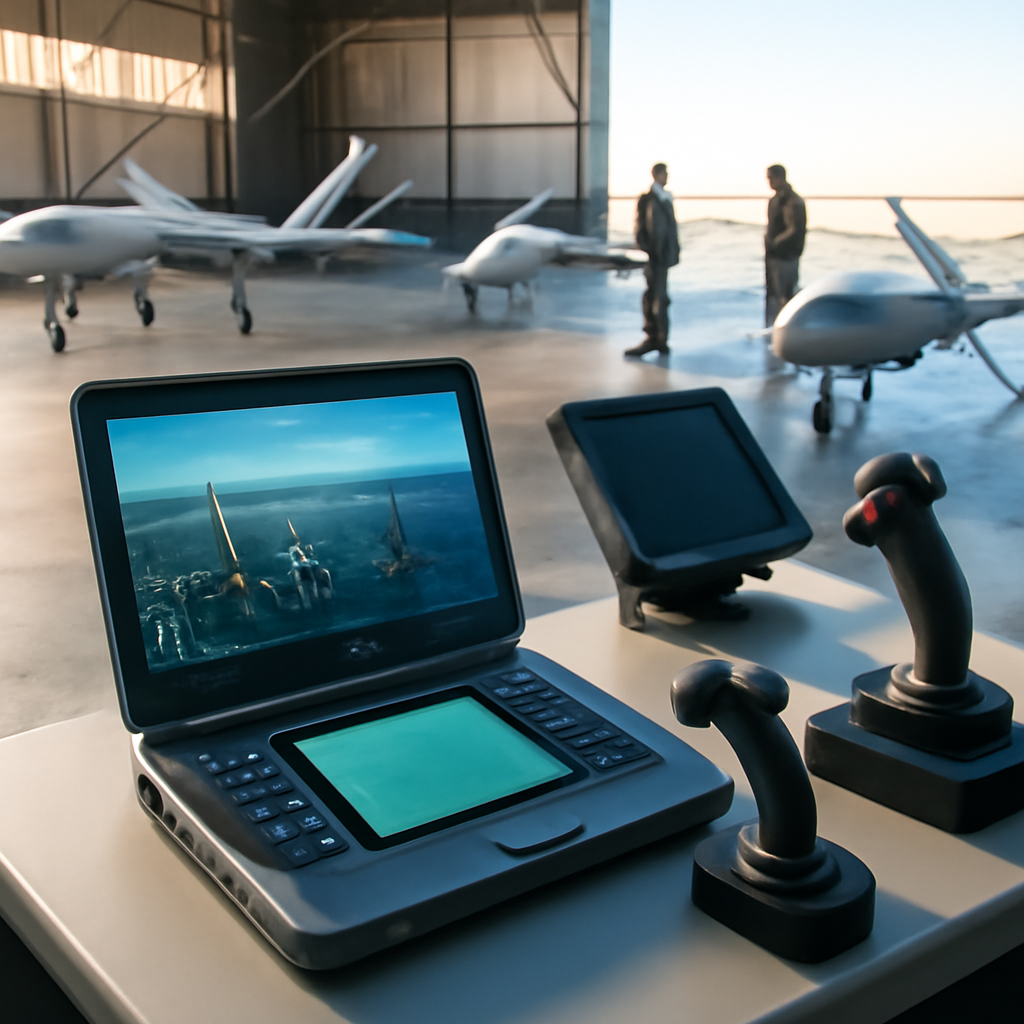
US Military Expands ISR Capabilities with Drones, Satellites, and Common Controls
Imagine being able to operate multiple aircraft with just a few mouse clicks and keyboard strokes - that's the future the US Military is working towards with its Massed Modular Aircraft initiative, aiming to rapidly expand its drone fleet to 500 by 2032. Lt. Gen. Christopher Niemi envisions a world where a single operator can seamlessly fly various aircraft designs with a common interface.
Malware Exploits Chinese Casino Sites for Espionage
Uncover the dark side of Chinese-language casino sites: a vast network of seemingly harmless online casinos and adult sites is secretly harboring malware, facilitating espionage, and laundering money - with ties to major US cloud providers. These sites cleverly disguise themselves as legitimate entertainment hubs, using common templates and relying on the house edge to turn a profit.
BambooToken Malware Exploits MQTT for Global Command-and-Control
Meet BambooToken, a sneaky new malware framework that's been secretly weaponizing the Internet of Things messaging protocol MQTT to control servers worldwide since 2023. Its operators have cleverly leveraged MQTT's lightweight design to pull off global command-and-control attacks on both Windows and Linux servers.
US Nuclear Control Mission Set for Drastic Overhaul with Looking Glass-Next
The US nuclear control mission is on the brink of a major transformation with the introduction of Looking Glass-Next, a next-generation system that will overhaul the nuclear command, control, and communications (NC3) architecture. This overhaul is crucial, as the NC3 is the backbone of America's nuclear deterrent, tying strategic platforms to decision-makers and enabling a secure, survivable, and interoperable nuclear force.
Lockheed Martin Bolsters Australia's Air Defense with $950M Contract
Lockheed Martin is bolstering Australia's air defense with a $950M contract to sustain and expand its joint air battle management system, strengthening the country's integrated air and missile defense system. This major deal is a significant step forward in modernizing Australia's air and missile defence capabilities.
Pentagon Expands AI-Powered Maven System Across Operations
The Pentagon is supercharging its decision-making with the AI-powered Maven Smart System, which is being expanded across operations to help officials make faster, data-driven decisions. What started as a tool to connect intelligence and operations is now being used to analyze logistics, supply chain, and budgeting data, and more.
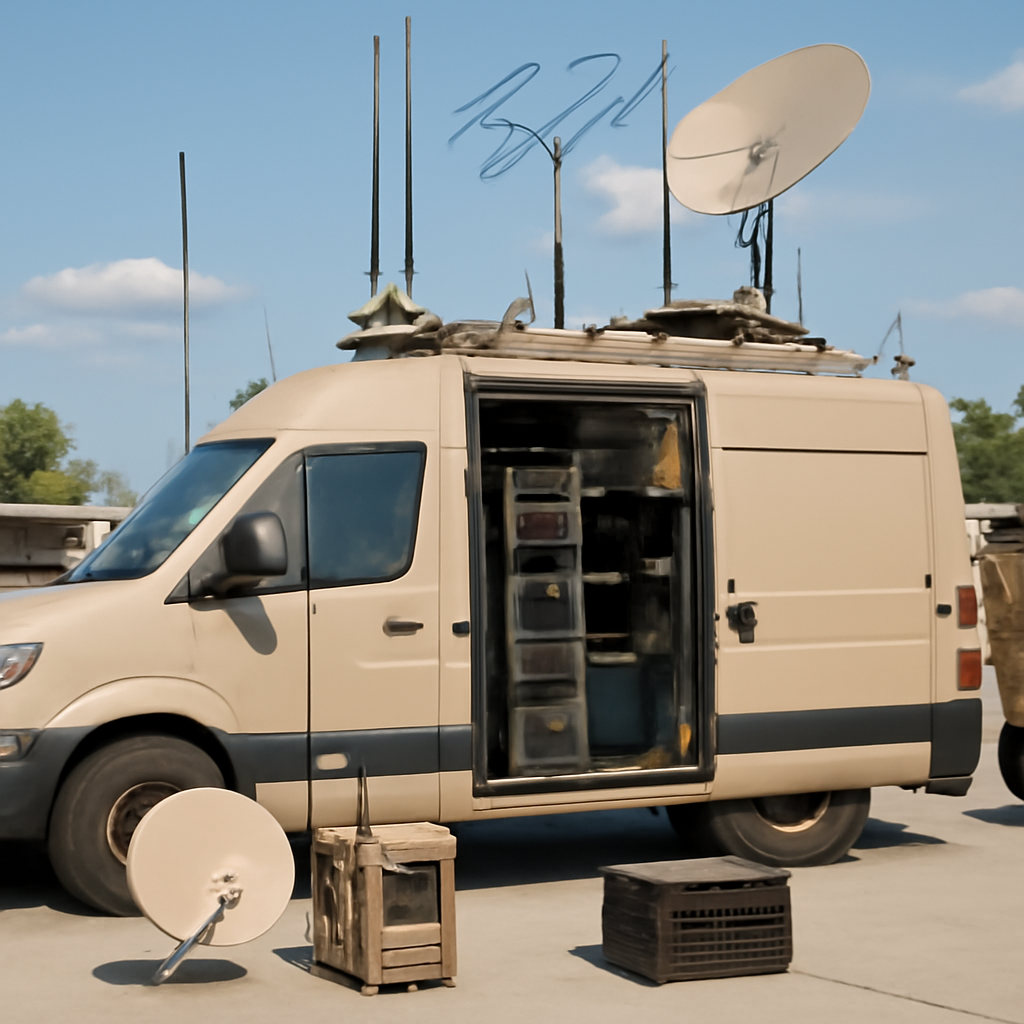
Air Force Overhauls Command and Control Comms After Epic Fury Lessons
The Air Force is revolutionizing its command and control communications, ditching its old model of bulky, 10-pallet comms packages that required 40-person teams to deploy, and embracing a leaner, more agile approach. Brig. Gen. Jeffrey Phillips, deputy chief of staff for warfighter communications and cyber systems, is spearheading the change.
GoCaracal Malware Exploits Ethereum for Covert C2 Communications
Researchers have uncovered a sneaky new malware, GoCaracal, that uses Ethereum to secretly communicate with its controllers, and with medium confidence, they've linked it to the notorious Dark Caracal group. This clever malware was used in a recent attack on a Venezuelan communications organization.
Military Software Must Operate Offline to Ensure Reliable Decision Support
When communications links break down in the heat of combat, military decision-support software must be able to keep providing critical guidance - and that's only possible if it can operate offline. By doing so, it enables lower-level commanders to take charge and make informed decisions, even when higher officers are out of the loop.
Army Taps Striveworks to Build AI Layer for NGC2 Command System
The Army has partnered with Striveworks to develop a game-changing AI layer for its Next Generation Command and Control (NGC2) system, which will rapidly transform vast amounts of battlefield data into actionable insights, compressing hours of staff work into mere seconds.
US Army Overhauls Battlefield Comms Plans to Counter Jamming Threats
The US Army is overhauling its battlefield communications plans to counter jamming threats, as traditional Primary, Alternate, Contingency, and Emergency (PACE) plans are no longer effective. Current sequential PACE plans are brittle and can't withstand concurrent, multi-band jamming, says Lt. Gen. Matthew McFarlane.
Army Seeks New Intel Tools with Guiding Document
The Army is shaking up its approach to intelligence gathering with a new guiding document that outlines key problems to be solved, and they're turning to industry for innovative solutions. This fresh "characteristics of need" approach is a deliberate departure from traditional requirement-driven methods, and a decision on its implementation is expected soon.
Iranian Hackers Evolve Cavern C2 with Google Apps Script Evasion
Meet the sneaky new tactic Iranian hackers are using to evade detection: blending malicious traffic with everyday services like Google Apps Script. By leveraging DNS A-record responses, they're able to switch between direct HTTPS channels and Google Apps Script relays, making it harder to track their moves.
US Army Urges Comprehensive Missile Defense Overhaul Amid Stockpile Strains
The US Army needs a major missile defense overhaul, and simply stockpiling more interceptors won't cut it, says Lt. Gen. John Rafferty, who is calling for a comprehensive missile defeat strategy.
CAV3RN Espionage Framework Evolves With Google Apps Script C2 Relay
Meet the sneaky CAV3RN Espionage Framework, which just got a clever upgrade - it can now use Google Apps Script as a relay to secretly communicate with its controllers, all while hiding in plain sight within DNS traffic. This clever tactic lets the malware decide on a per-transaction basis whether to connect directly to its masters or take a detour through Google's services.