[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it alongCybersecurity intelligence, threat analysis, and national security reporting.
Berlin's administrative network has been hit by a massive Rhysida ransomware attack, with hackers claiming to have stolen a whopping 5.79 TB of sensitive data, including 1.44 million files, and are now threatening to publish it unless paid a ransom. The breach exposes a vast array of confidential records, from government and financial data to personal info like names, email addresses, and phone numbers.
Anthropic just dropped a bombshell, revealing major gaps in AI agent governance with its new Compliance API - and it's a game-changer for cloud security. By introducing local session transcripts, Anthropic is shining a light on what really happens when AI agents interact with your systems.
Aurora ransomware operators are using AI tool Cursor to plan and execute targeted attacks, even going so far as to instruct it in Russian to exclude certain regions and domains. This sophisticated approach has enabled the group to breach over 20 organizations across nine countries in just a few months.
Meet Silver Fox, a sneaky threat actor that's been using adware to disguise a powerful backdoor called ValleyRAT, which can give attackers full control over your computer. They've even hijacked a legitimate Chinese desktop wallpaper tool to spread their malicious software.
A Mandarin-English interpreter's ties to Chinese universities have raised red flags about potential national security risks, sparking scrutiny of his work with successive Australian prime ministers. Charles Qin's affiliations with high-risk institutions have experts questioning whether his role compromised sensitive information.
Meet ValleyRAT, a sneaky backdoor that's been evading detection with the help of adware, infecting over 1500 users in China and India with a staggering 100,000 detections in 2026 alone. Its clever disguise was uncovered when researchers dug deeper into a suspicious installer initially labeled as ordinary adware.
Taiwan's parliament has greenlit a whopping $7.57 billion drone funding package as part of a broader strategy to bolster its defenses, despite analyst warnings that the compromise could create uncertainty for local manufacturers. The approved budget allocates $40 billion annually for six years, falling short of President Lai Ching-te's request for immediate access to a larger special budget.
A surprising case of accidental AI guidance has emerged: someone apparently embedded instructions for artificial intelligence into a court filing, sparking intriguing questions about the intersection of law and machine intelligence. This unusual incident raises important implications for those involved.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along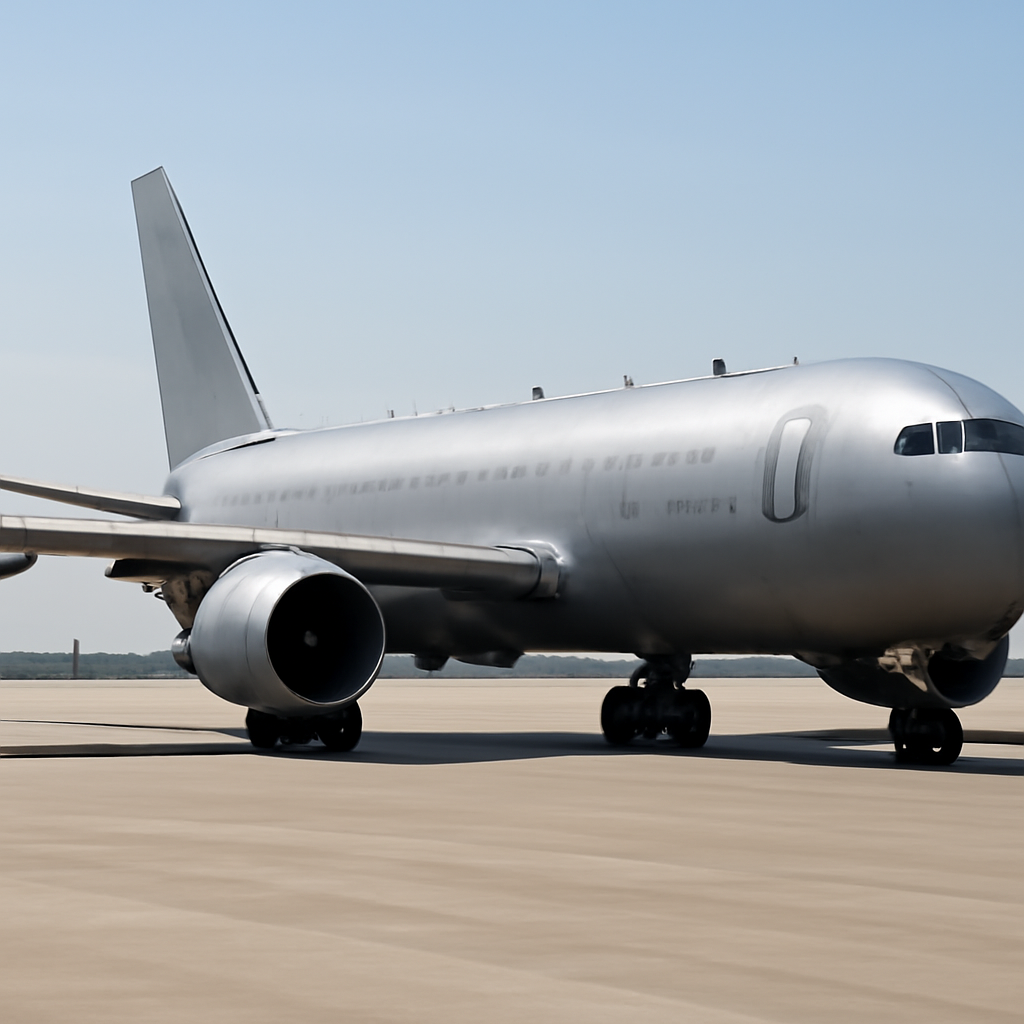
The US is shaking up its military partnerships in the Middle East with a potential $4.5 billion deal to sell four KC-46A refueling aircraft to Qatar, a move that highlights the region's evolving military-commercial landscape. This massive sale is just one piece of a larger puzzle that includes a new multinational drone force initiative.
Policymakers are racing to prevent AI disasters, but a proposed kill switch law may be backfiring - mirroring the flawed design of a notorious 90s surveillance chip. The AI Kill Switch Act could give a federal agency sweeping powers to shut down cutting-edge AI systems, but is it a solution waiting for a problem?
Beware of voice phishing scams on Microsoft Teams! A recent campaign, dubbed Spring Ring, used fake IT help desk accounts to trick over 150 employees across 10 organizations into granting remote access.
When hackers take control of routers like Cisco's IOS XR, they don't just gain access - they gain a bird's-eye view of the entire network, allowing them to harvest sensitive credentials and fly under the radar. The notorious Fire Ant group recently exploited these routers to turn them into intelligence collection platforms, putting countless networks at risk.
If you've customized your Windows 11 mouse settings, beware: the latest update, KB5120998, may be reverting them to default, causing frustrating losses in personalization. Microsoft is investigating the issue and asking affected users to report their experiences through the Feedback Hub.
The FBI and DOJ have brought two Nigerian men, Adebola Festus Adekunle and Mudasiru Afeez Olawale, back to the US to face charges for their roles in a sextortion scheme that tragically led to the deaths of two young victims. This case is a stark reminder that sextortion is a heinous crime that the FBI is committed to stopping, no matter where the perpetrators hide.
The US Department of Justice made a telling edit to their recent press release, quietly changing the wording from "victims" to "among the targets" of a China-linked hacking group that hit several high-profile US agencies. This subtle shift highlights the scope of a brazen cyber espionage operation that compromised sensitive government networks.
If you've recently updated Microsoft Defender Antivirus, you might be seeing annoying false alarms claiming it's turned off - but don't worry, it's still working hard to protect you. These pesky alerts are affecting all supported Windows versions, including Windows 11 26H1 and Windows Server 2025.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Leaders from across the Pacific have gathered in Koror, Palau, for the 55th Pacific Islands Forum Meeting, united by a bold vision to build stronger economies and transform lives. With nearly 30% of the world's exclusive economic zones lying beneath the Pacific's waves, the stakes are high for creating jobs, infrastructure, and opportunities that can overcome the region's unique challenges.
As the Shanghai Cooperation Organization celebrates 25 years, its impressive trade growth - intra-SCO trade hit $725 billion in 2024, up from $463 billion in 2021 - belies internal tensions and security challenges that threaten its future. Can the SCO overcome its rivalries and deliver on its promise, or will its achievements remain largely symbolic?
Manchester Airports Group swiftly sprang into action after a hack, reassuring customers that they've taken robust measures to safeguard their info and reaching out to those affected, including those with upcoming bookings, to offer extra support. Meanwhile, hackers FulcrumSec claimed responsibility, boasting of swiping 86 GB of sensitive data.
Beware of infostealer malware that's hijacking Claude sessions! Anthropic is taking swift action to protect users, including signing them out of compromised accounts, removing saved payment methods, and offering refunds for unauthorized charges.
Malicious Chrome extensions have been caught stealing cryptocurrency and browser data, with a recent investigation uncovering a sophisticated malware campaign that may have been active since early 2024. The attack used 16 distinct modules to deliver a modular malware framework to unsuspecting Chrome and Edge users.
As strategic threats escalate, Australians are crying out for a unified voice to guide them through uncertain times, with many still unclear about the real nature of China's intentions. Despite 62% fearing China could become a military threat, 61% still see them as a vital economic partner, revealing a jarring disconnect between concern and understanding.
An overwhelming 93% of British adults believe they have a right to keep their online conversations private, with 89% agreeing that their personal messages should be off-limits without a court order.
Beware of fake Cloudflare CAPTCHAs that can lead to a sneaky backdoor invasion, giving attackers direct access to your organization's internal network. A new variant of malware, called TerminalFix, tricks victims into executing a malicious PowerShell command, allowing hackers to gain control.