Tag: emerging threats
8355 articles
NATO Unveils Massive Defence Contracts at Ankara Summit
NATO Secretary-General Mark Rutte promises a huge boost in defence spending, with "tens of billions" of dollars in new contracts set to be unveiled at the Ankara summit, marking a major step from commitment to action. The move aims to show the alliance is delivering on its pledges, not just making promises.
Japan Air Force Renamed to Reflect Expanded Space Domain Role
Japan is taking a giant leap in its defense strategy, renaming its air force to the Japan Aerospace Self-Defense Force to reflect its expanded role in the space domain. This move, approved by parliament on June 26, 2026, will take effect on April 1, 2027, and marks a significant shift in Tokyo's military capabilities.
Massive Passport Leak Exposes Sensitive Traveler Data
A staggering leak of almost a million passport records from around the world has put sensitive traveler data at risk. The breach, linked to a low-security ID verification system for cannabis dispensaries, exposed passports as a vulnerable weak point in authentication processes.
Burnham's Rise Poses Test for UK Defense Spending Pledge
As Andy Burnham rises to prominence with his decisive by-election win in Makerfield, the UK's defense spending pledge is about to face its biggest test yet. With Labour's future leadership potentially in his hands, Burnham's next moves will be closely watched, especially given the ambitious targets to increase defense spending to 3.5 percent of GDP by 2035.
Threat Actors Exploit OpenAI Invitations to Target Cybersecurity Firms
Threat actors are cleverly exploiting OpenAI invitations to scam cybersecurity firms, creating fake tenants that mimic legitimate companies and sending convincing emails that pass authentication checks. These targeted phishing attacks allow scammers to spread malicious content through a trusted channel.
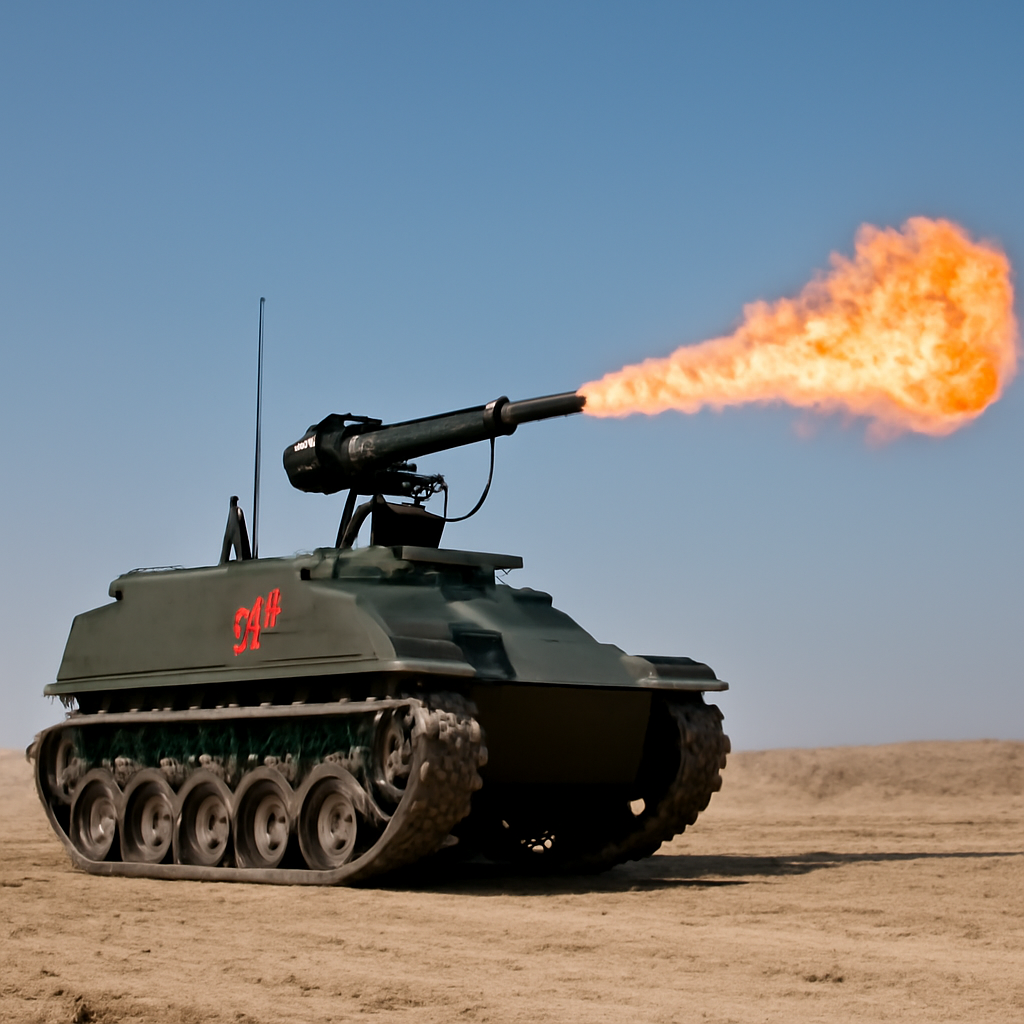
China's PLA Deploys Flamethrowers on Unmanned Ground Vehicles
China's PLA is supercharging its unmanned ground vehicles with flamethrowers, combining the brutal power of the Type 74 flamethrower with the cutting-edge ZRY222 Unmanned Ground Equipment platform for a safer, more lethal combo. This game-changing tech allows soldiers to clear trenches and bunkers from a safe distance, minimizing risk to personnel.
Australia Boosts Deterrence with Nuclear-Powered Submarines
Imagine having a game-changing asset on the battlefield that can single-handedly shift the balance of power - that's the unparalleled impact of nuclear-powered submarines, as Vice Admiral Mark Hammond aptly puts it, a remarkable difference-maker in combat. With a proven track record of success, these submarines have consistently demonstrated their ability to deter and dominate in multi-domain warfare.
India Accelerates Drone Production Amid Regional Security Push
India is taking a cue from Ukraine's playbook, aiming to turbocharge its drone production to marry mass manufacturing with real-time battlefield feedback, and transform its national industrial policy. By leveraging policy tools like import curbs, the Production Linked Incentive scheme, and the Drone Shakti Mission, New Delhi is aggressively pushing to become a major drone producer.
Crypto-Agile Infrastructure Bolsters US Military's Edge in Space Domain
In the high-stakes world of space domain warfare, the US military's edge hinges on its ability to sift through vast amounts of data in seconds, enabling leaders to make smarter decisions faster than the enemy can react. By pairing rapid AI-enabled analysis with equally rapid cryptographic protections, the military can gain a decisive advantage.
Hackers Inject Malicious Script in Polymarket Supply-Chain Attack
Polymarket has pledged to fully reimburse customers who lost around $3 million in a shocking supply-chain attack that injected malicious JavaScript into the platform's frontend via a third-party vendor breach. The incident highlights the vulnerability of even major players to these types of attacks.
AM General Counters JLTV Funding Threat with Transition Woes
AM General is pushing back on lawmakers' plans to cut funding for the Joint Light Tactical Vehicle (JLTV) program, citing the complexities of transitioning major defense production from one manufacturer to another. The company attributes delivery delays to a tough handoff, inheriting an uncertain technical baseline and navigating supplier transition issues.
Texas Hunting License Data Breach Exposes Millions
A recent data breach at the Texas Parks and Wildlife Department may have exposed over three million hunting and fishing license customers, putting sensitive information like driver's license numbers and passport data at risk of being used for account takeover, synthetic identity fraud, and targeted phishing. This breach is just the beginning, as stolen data can be used for a range of malicious activities.
Amazon AI Coding Tool Exposes Cloud Credentials to Malicious Git Repos
A security vulnerability in Amazon's AI coding assistant, tracked as CVE-2026-12957, allowed malicious Git repositories to access sensitive cloud credentials, raising concerns about informed consent and user security. The flaw enabled automatic execution of commands with no user prompt required.
Amazon Q Developer Flaw Lets Malicious Repos Run Code via MCP Configs
A high-severity flaw in Amazon Q Developer, tracked as CVE-2026-12957, allowed malicious repositories to run commands and steal cloud credentials simply by being opened in an IDE. This vulnerability put developers at risk of having their sensitive AWS keys, cloud CLI tokens, and API secrets compromised.
AI Agents Expose Governance Gap in Enterprise Identity Infrastructure
Traditional enterprise identity systems are struggling to keep up with the dynamic nature of AI agents, which can autonomously execute complex tasks, chain calls across multiple systems, and continuously act on inherited credentials. This has exposed a significant governance gap in current identity infrastructure.
Linux Kernel Flaw Exposes Local Users to Root Privilege Escalation
A newly discovered Linux Kernel flaw, CVE-2026-43503, allows local users to easily escalate their privileges to root level, putting systems at risk. This vulnerability, dubbed DirtyClone, lets attackers corrupt file-backed memory and gain unrestricted access with just a few clever steps.
CISA Flags Exploited PTC Windchill Flaw Amid Web Shell Attacks
PTC has confirmed that attackers are exploiting a high-severity flaw, CVE-2026-12569, in its Windchill software to drop malicious web shells on vulnerable systems, allowing them to execute arbitrary code remotely. The company has reported heightened threat activity, urging users to take immediate action to protect themselves.
Miasma Malware Poisons Over 20 npm Packages
In a lightning-fast attack, hackers poisoned over 20 npm packages with Miasma malware, completing the coordinated operation in under three seconds. The attackers compromised an npm maintainer account to publish tainted updates to popular packages.
Linux Kernel Flaw Enables Unprivileged Root Access
A shocking Linux kernel flaw, dubbed pedit COW, allows unprivileged users to gain root access on vulnerable hosts by cleverly corrupting an in-memory cached copy of a setuid binary. This stealthy exploit requires no disk changes, making it nearly undetectable.
Miasma Malware Targets npm, GitHub in Expanded Supply Chain Attack
Over 550 GitHub repositories have been compromised in a massive supply-chain attack, with malware harvesting developer credentials and spreading across package registries and workflows. The attack has already infected numerous npm packages and one Go module, putting developer data at risk.
China-Linked Hackers Deploy TinyRCT Backdoor in Southeast Asian Infrastructure Attacks
For years, a stealthy China-linked hacking group has been quietly targeting critical infrastructure in Southeast Asia, with a clear strategic interest in disrupting or monitoring key regional industries. Their sophisticated attacks have zeroed in on state-owned energy and government sectors, using a potent tool called the TinyRCT backdoor.
Microsoft Uncovers ZIP Phishing Campaign Targeting Hotels with Node.js Implant
Microsoft warns of a sneaky ZIP phishing campaign that's been targeting hotels across Europe and Asia since April 2026, using photo-themed attachments to deliver a Node.js implant to front-desk machines. The cleverly crafted emails, often written in Japanese, Danish, or Dutch, use urgent and reputation-focused themes to trick recipients into opening the malicious attachments.
Cellebrite Tool Used by Russia on Jailed Activist's iPhone Despite Sales Cutoff
Despite Cellebrite's claims to have cut off sales to Russia, a shocking forensics trail on a jailed activist's iPhone reveals that the company's tool was used to extract data as recently as June 2021. This alarming discrepancy raises serious questions about Cellebrite's control over its technology.
Turla Unveils STOCKSTAY Backdoor in Ukraine Espionage Campaigns
Russian hackers, specifically the state-sponsored group Turla, have unleashed a new and stealthy backdoor called STOCKSTAY in a recent espionage campaign targeting Ukraine. This sneaky malware uses a secure WebSocket connection to communicate with its command center, making it a formidable tool for cyber spies.