[SPONSOREDNUBIVANCE]
Know a small business winging it on security?
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it alongCybersecurity intelligence, threat analysis, and national security reporting.
The Pentagon is gearing up to adjust its FY27 priorities due to funding uncertainty, with Comptroller Jules Hurst hinting that the department may revisit its requests with appropriators if the $350 billion reconciliation package isn't passed. This potential shift could impact high-priority programs like Golden Dome, munitions buys, and Defense Autonomy.
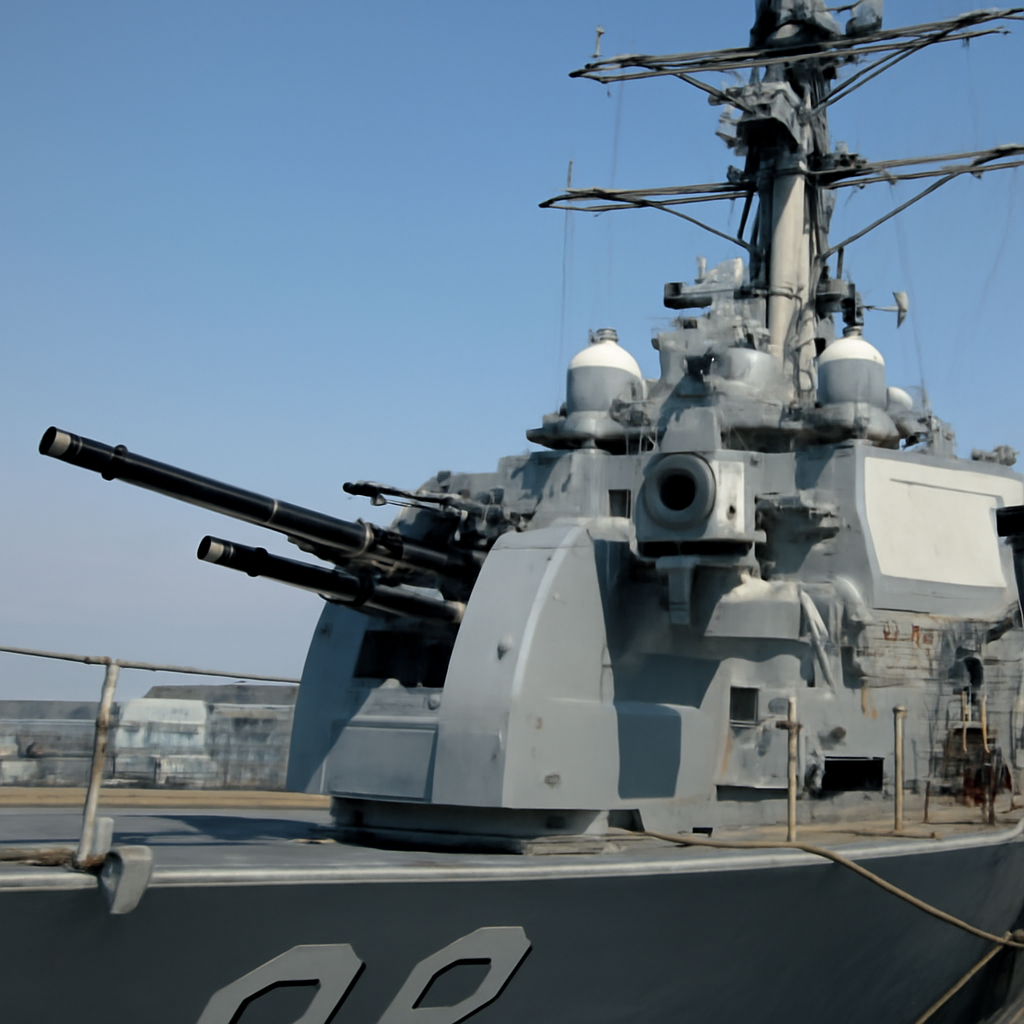
The US Navy has upgraded its Point Defense System with the Mk 38 Mod 4 Machine Gun System, a game-changing combo that tackles threats from unmanned aerial systems with precision and firepower. This cutting-edge system pairs a 30mm chain gun with a .50 caliber machine gun, ready to take on emerging challenges.
Federal CIOs are shifting their focus from technology for its own sake to delivering real business value, with a clear emphasis on centering citizens and driving meaningful outcomes. By adopting this approach, they're finding a balance between modernizing IT and ensuring responsible stewardship.
Microsoft's latest security update, KB5002914, has caused frustration for some Excel users, disrupting basic workflows like copy-and-paste and autofill. The update, part of September's Patch Tuesday, has left many users, including entire teams, scrambling to find workarounds.
We might be so busy worrying about AI-enabled catastrophes like asteroid impacts that we overlook a more immediate threat - terrorists using AI to launch lethal attacks right under our noses. The real danger may not be the Hollywood-style doomsday scenario, but the probable and more sinister misuse of AI that could be happening in plain sight.
National Cyber Director Sean Cairncross warns that the rapid spread of AI is creating a pressing cybersecurity time crunch, framing it as a high-stakes race between innovation and securing critical systems. Governments are scrambling to "buy time" to bolster defenses before AI-driven threats overwhelm them.
The US Department of War is turbocharging its AI capabilities by integrating top commercial tools like ChatGPT and Grok into its GenAI.mil platform, now used by over 1.7 million personnel. This move marks a major leap from experimentation to enterprise-wide adoption of artificial intelligence.
A configuration mistake made by Surfshark's engineering team left an internal test server vulnerable to the internet, exposing sensitive data due to human error. The incident highlights the importance of robust security measures, even for trusted services.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Meet the AI super sleuths that can uncover software vulnerabilities with just a whisper of a rumor. With minimal input, these agents can sniff out working exploits, potentially beating the patch cycle and leaving security teams scrambling to keep up.
When a host is compromised, the damage runs deep: attackers can exploit identity mechanisms to access all authorized identities on that node, essentially collapsing machine identity and putting your entire system at risk. This is the stark reality of a SPIFFE/SPIRE security breach, where short-lived workload identities can become a double-edged sword.
Meet GI Zhou, who's getting cozy with the QBU-202, a cutting-edge sniper rifle chambered in 8.6×70mm Lapua Magnum - and it's clear China's armed forces are taking their long-range precision capabilities to the next level. This high-tech rifle is getting the personal touch, with soldiers treating it like a trusted companion.
Europe's defence industry is shifting towards low-cost air defence solutions, with a focus on scalable surface-to-air missiles that can take down drones and cruise missiles with equal effectiveness. This pivot is driven by the lessons of the Russia-Ukraine War, where Ukraine has seen Russia increasingly favour jet-powered Geran-4/5 drones over piston-powered Geran-3s.
Get ready for a new frontier in cyber threats: AI agents are emerging as a prime target for hackers, with experts warning that attacks against these autonomous agents will become the next big threat vector. As AI agents gain access to sensitive data, organizations are essentially handing hackers the keys to the kingdom.
The Pentagon's new cyber strategy is shifting gears, focusing on high-impact offensive operations that drive real results, not just defense for its own sake. It's about delivering big, muscular blows that produce tangible outcomes, according to Brig. Gen. William Wilburn, the Department of Defense's deputy principal cyber advisor.
Twenty-five years after 9/11, Al-Qaida is a shadow of its former self, with its core operations severely diminished and a leadership crisis unfolding. The group's operational reach has been crippled, and its top leaders have been decimated by US drone strikes, leaving only a handful of senior figures remaining.
Google just patched 200 security flaws in Android, including a critical Wi-Fi vulnerability that could let hackers take control of your device - and it's a stark reminder to stay vigilant about the risks lurking in ordinary access and trusted services.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
The FBI is taking a bold new approach to combating cyber threats, shifting from a reactive to an active disruption strategy that aims to proactively disrupt and impose costs on cyber adversaries. This move marks a significant departure from traditional law enforcement methods, embracing a more interventionist posture in cyberspace.
A massive data breach at AdaptHealth has compromised the sensitive information of 4.1 million people, including names, contact details, demographics, and health and insurance data. The cyberattack exposed a wide range of personal records, putting millions of individuals at risk.
The Cybersecurity and Infrastructure Security Agency (CISA) has updated its Insider Threat Mitigation Guide to tackle today's complex risks, offering fresh insights and resources to help organizations stay ahead. This update acknowledges that insider threats are no longer just about disgruntled employees, but also about adapting to emerging trends like AI and remote work.
Cisco FMC vulnerabilities are being exploited by threat actors, including state-sponsored groups and crimeware attackers, to fuel ransomware and advanced persistent threat (APT) attacks. These bad actors are using recently patched flaws to gain initial access, run scripts as root, and escalate privileges.
In a shocking display of speed, an AI-powered attack exploited PaperCut flaws to compromise at least 11 organizations in just 26 seconds, with the entire campaign unfolding in a matter of hours. The attackers used "hundreds of AI agents" to automate the exploitation effort, combining AI models with commodity tools to target vulnerable PaperCut NG/MF servers.
A sneaky app, "Vice Streets: Open World", racked up over 1 million downloads on Google Play without a single public review or rating, taking advantage of the platform's Early Access feature. This feature, meant to help developers gather feedback, can also shield them from criticism - and warn signs - that might scare off users.
A massive data breach at IDScan has exposed a staggering 153 million driver's license scans, which were allegedly advertised for sale on a dark-web forum, compromising sensitive information on a huge scale. The identity verification firm has confirmed unauthorized access to its cloud platform and is working with specialists to investigate the incident.
Malicious hackers targeted identities in nearly half of all confirmed attacks, with session hijacking and replay emerging as the most effective tactics for gaining unauthorized account access. This alarming trend highlights the growing threat of identity theft in today's digital landscape.