[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
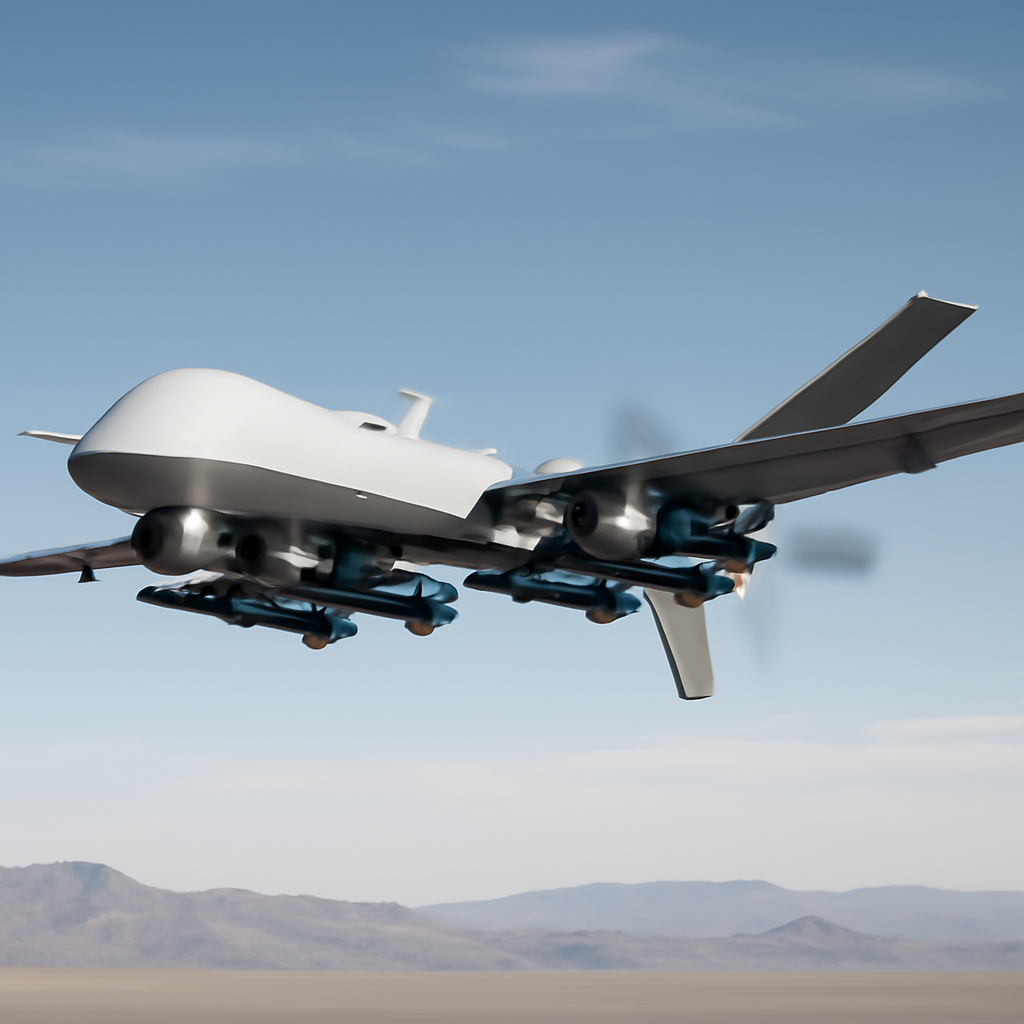
The Air Force's MQ-9 Reaper drone just proved its mettle in a live demo, successfully taking down aerial targets with the help of laser-guided Advanced Precision Kill Weapon System (APKWS) missiles. This milestone test at the Nevada Test and Training Range brings new firepower to the fight against one-way attack drones.
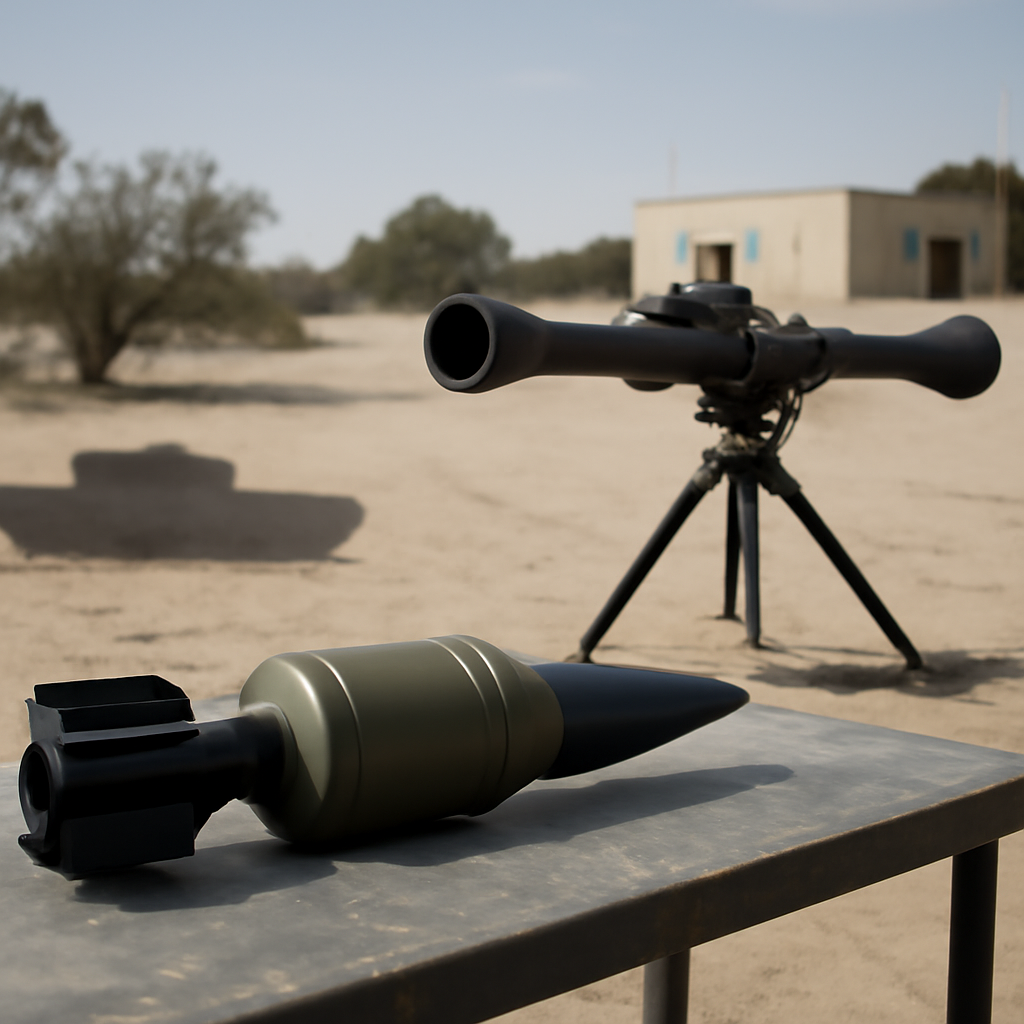
Saab has unveiled its powerful HEAT 758 round, a tandem-warhead munition capable of penetrating even the toughest tank hulls, as demonstrated by a live firing test against a Russian T-80 main battle tank. The impressive display showcases the round's potential to revolutionize modern warfare.

Australia is set to supercharge its cyber defence capabilities with a bold investment of A$27-38 billion over the next decade, empowering the country to tackle the growing threat of espionage, foreign interference, and cyber attacks head-on. This significant boost will enable Australia to develop enhanced offensive capabilities to protect its critical infrastructure from increasingly sophisticated cyber threats.
The US Navy is taking its Trump class battleships to the next level by ditching traditional propulsion for nuclear power, giving these massive surface combatants the comprehensive capabilities they need to stay ahead. This game-changing upgrade is part of the Navy's new shipbuilding plan, which includes acquiring 15 nuclear-powered battleships over the next few decades.
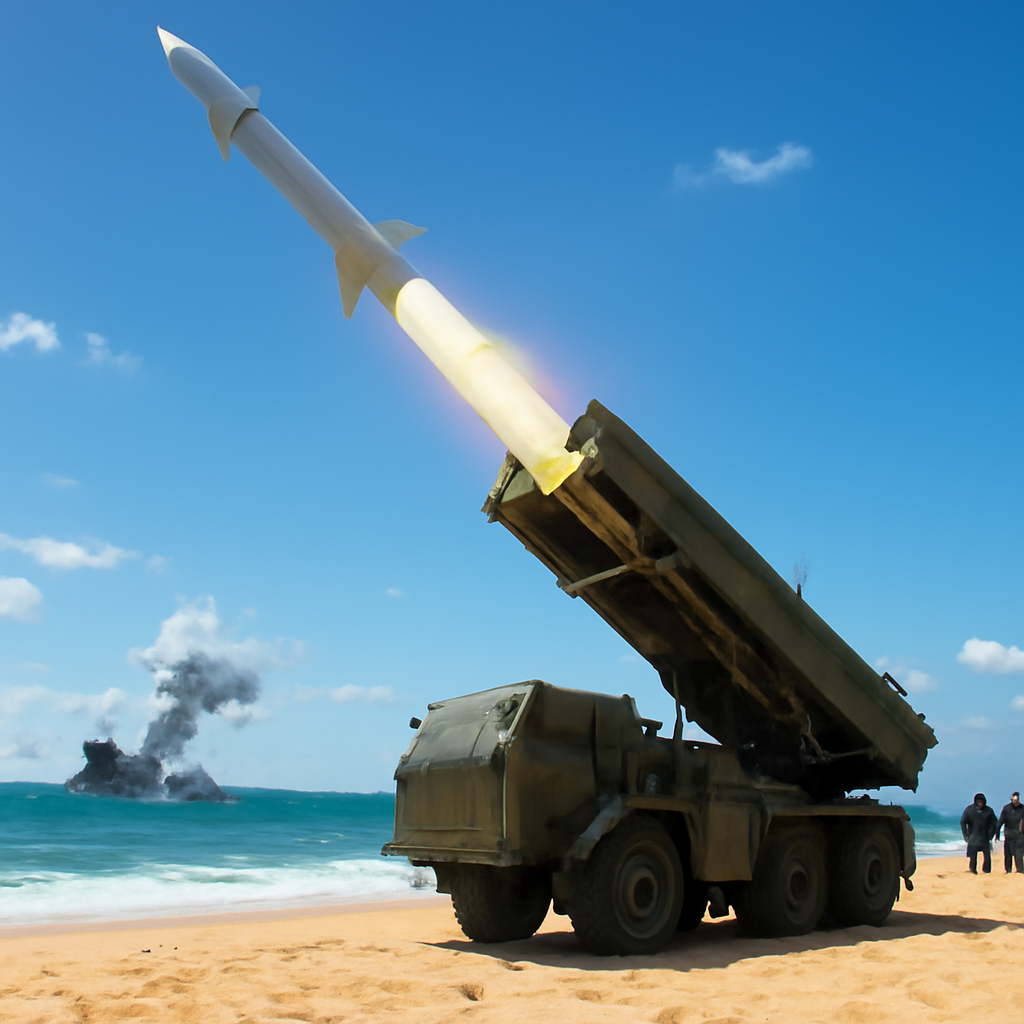
In a stunning display of regional defense power, Japan fired Type 88 surface-to-ship missiles at a Philippine vessel, sinking it with precision and accuracy in a live-fire exercise. This marked a historic first for Japan, as it launched the Type 88 outside its own borders, showcasing its growing military capabilities.

The traditional logistics problem of the "last mile" has morphed into a far larger threat, now spanning 1,700 km or more, as persistent surveillance and precision strike capabilities turn large supply ships into vulnerable targets. The era of concentrating ships in big logistics formations is rapidly becoming a relic of the past.
Malicious actors are exploiting weaknesses in Active Directory Certificate Services (AD CS) to secretly escalate privileges, often disguising their attacks as routine administrative actions. This stealthy tactic allows them to blend in with normal operations, making it a high-impact threat that's often under-monitored.

ShinyHunters has made a brazen move, claiming to have stolen a massive 3.65 terabytes of data from Canvas, putting 275 million records across 8,809 school systems at risk. The cybercriminal group is now demanding an undisclosed ransom from Instructure, escalating threats by hijacking login pages at hundreds of institutions.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
The Turkish defence sector made a powerful statement at SAHA 2026, securing a whopping $8 billion in export contracts within just three days - a significant leap from $6.2 billion at SAHA 2024. This impressive showcase of deep-strike capabilities drew in 30,000 industry professionals and 140 official delegations from over 120 countries.

Want to hide text in plain sight? Try using white text on a white background or black text on a black background - simple yet effective visual tricks that can evade human eyes while remaining readable by machines.
SkyFi is revolutionizing real-time satellite imagery for warfighters with a cutting-edge prototype for SOCOM, delivering unclassified commercial imagery directly to mobile devices via a web-based platform. This innovative Sovereign Intelligence Platform connects users to a vast network of 150+ satellite providers, empowering them with actionable insights in the field.

In a shocking security breach, Instructure, the creator of Canvas, revealed not one, but two separate intrusions into its system, leaving thousands of schools and students scrambling for access to crucial course materials during final exams. The breaches come as an extortion group, ShinyHunters, threatens to leak a massive 3.65 TB of stolen data.

General Motors has been hit with a record $12.75 million penalty for selling California drivers' data without their consent, despite promising to protect their privacy. This landmark case marks a major victory for data protection, with California's Attorney General Rob Bonta leading the charge.
Stay ahead of the threats: are you managing cloud risk effectively, or is it still siloed and vulnerable to AI-driven attacks? Recent research from Google Threat Intelligence Group reveals a new wave of AI-augmented operations that are scaling and accelerating compromises.
In a shocking revelation, hackers secretly lurked on South Staffordshire Water's corporate network for 20 months, evading detection until a performance issue sparked an investigation in July 2022. The stealthy attackers gained unauthorized access via a September 2020 phishing attack, harvesting credentials and even attempting to deploy ransomware before being finally uncovered.
Meet GhostLock, a proof-of-concept that cleverly exploits Windows API to disrupt file access, causing operational downtime without data loss, similar to the impact of ransomware. By manipulating the CreateFileW sharing parameter, GhostLock effectively locks files, leaving other processes in the dark with a sharing violation error.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Cloudflare and Arctic Wolf are shaking things up with a major AI-driven overhaul, cutting staff to make way for a world-class, high-growth operation that's harnessing the power of artificial intelligence. This move isn't about cost-cutting, but about revolutionizing how these companies create value in the agentic AI era.
A rogue version of Checkmarx's Jenkins Application Security Testing plugin was compromised by the TeamPCP hacker group, who left a taunting message in the about section, claiming another supply-chain attack success. The group has been linked to a string of similar breaches, delivering credential-stealing malware.

A recent data breach has exposed the inner workings of the notorious Gentlemen ransomware group, revealing a treasure trove of sensitive information, including chats, images, and operational practices. This rare glimpse into the ransomware ecosystem could provide valuable insights for cybersecurity experts and researchers.
Malware is masquerading as a legitimate software installer, tricking developers into spilling their secrets by exploiting the Chromium interface. A simple search ad has become the conduit for this malicious campaign, leading unsuspecting devs down a path of deceit.

Researchers have made a breakthrough in streamlining SIEM migration with an innovative automation tool called ARuleCon, which can slash months of manual rule rewrites into mere batch operations. This game-changing system uses a three-stage conversion pipeline and large language models to rapidly translate complex rules, cutting conversion time to just 140 seconds.
If you're using the Checkmarx Jenkins AST plugin, make sure you're on a safe footing by using version 2.0.13-829.vc72453fa_1c16 or earlier, published on December 17, 2025, as newer versions may be vulnerable. Checkmarx has since released a patched version, 2.0.13-848.v76e89de8a_053, available on GitHub and the Jenkins Marketplace.

Over 2,000 attacker source IPs worldwide are currently involved in automated attacks exploiting a critical cPanel vulnerability, CVE-2026-41940, which allows remote attackers to gain elevated control and deploy malicious backdoors. This flaw has been targeted by multiple actors for a range of malicious outcomes, including cryptocurrency mining and ransomware.

The UAE successfully countered over 80-85% of incoming drones using its homegrown counter-drone technology during the recent Iran conflict, showcasing the country's reliance on locally developed solutions. This locally grown tech, including jammers and spoofers, allowed for an immediate response, operating from day one without delays.