[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
In a brazen ransom email, the attackers boldly declared, "IMPORTANT: WE STOLE THE DATA, CONTACT UMMEDIATELY," leaving no doubt about their malicious intentions. The hackers infiltrated the retailer's network through a clever help-desk ploy, tricking staff into resetting passwords and gaining control of critical accounts.
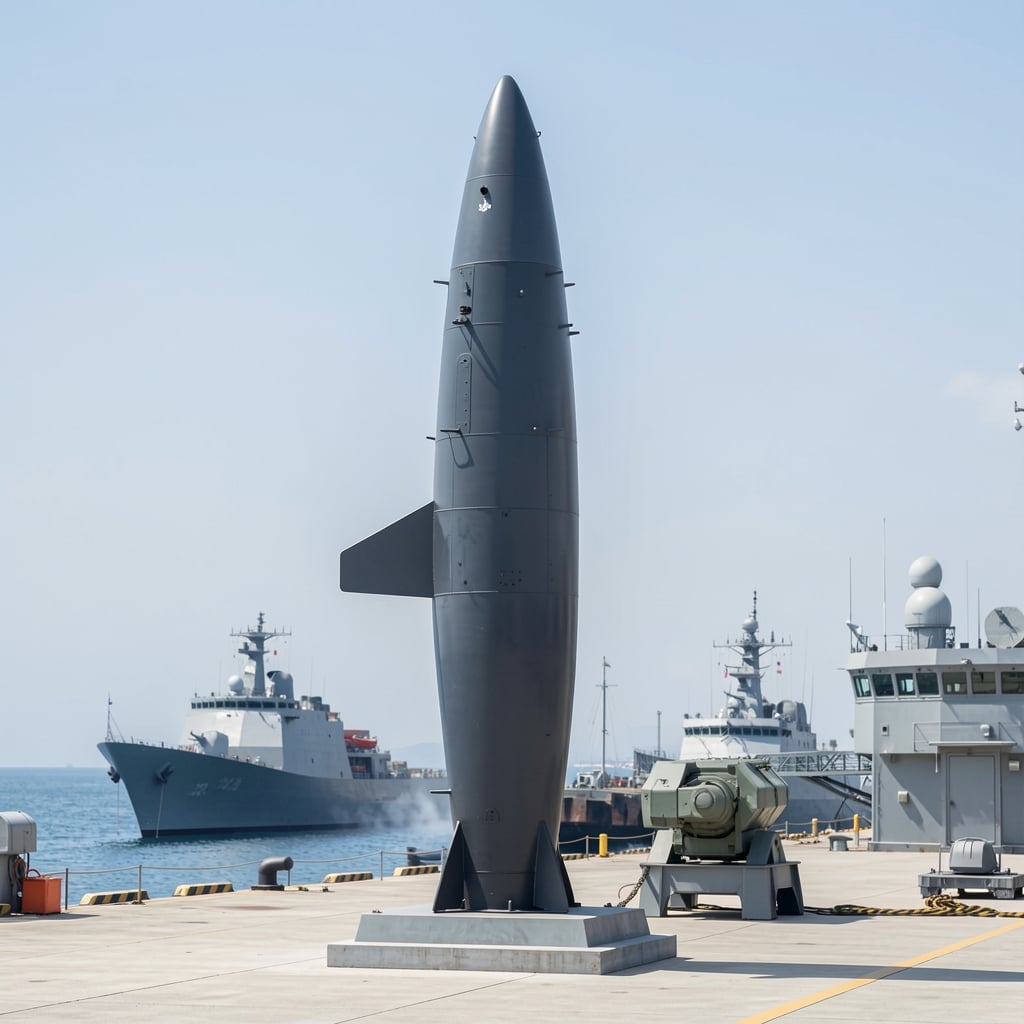
China has just revealed its latest game-changer: the JL-3, or 'Giant Wave 3', a third-generation intercontinental-range submarine-launched ballistic missile that's set to take the country's military capabilities to new depths.
A single misstep in a GitHub Actions workflow can become a four-step chain to permanent credential exposure, putting your entire CI/CD pipeline at risk. Researchers have uncovered a class of vulnerabilities, dubbed Cordyceps, that can be exploited in a surprisingly simple way.
Google is taking a stand against scammers, suing a group called Outsider Enterprise that uses its Gemini AI feature to create fake websites and scam people through text messages. The group, which operates on Telegram, offers phishing-as-a-service, making it easy for non-tech-savvy scammers to target victims.
Meet Scattered Spider, a notorious cybercrime collective that's evolved into a decentralized network of independent clusters, sharing tactics and tools to wreak havoc online. This fresh analysis by Group-IB shatters the traditional view of a single, unified gang, revealing a more complex and dynamic threat.
Most enterprises are facing a harsh reality: a majority are reporting AI-related security incidents or vulnerabilities, highlighting a growing concern that can't be ignored. This stark statistic sets the tone for a crucial conversation about the intersection of AI and security.
The software supply chain security landscape has dramatically shifted in just 20 months, with AI tools and models now integral to building, deploying, and running software - and bringing new risks to the table. The old question of "what's in your code?" has given way to a more complex concern: what happens when AI coding assistants and autonomous agents start suggesting or producing code?
A newly disclosed 16-year-old Linux kernel vulnerability, dubbed Januscape, allows hackers to easily escape virtual machines and compromise their host systems - all with just a few clicks from within the guest system. This shocking security flaw, tracked as CVE-2026-53359, has been lurking in the kernel for nearly two decades.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Hacktivists aligned with Russia are wreaking havoc on UK organizations with denial-of-service attacks that may be simple, but have a significant impact by disrupting essential services. These attacks can overwhelm important websites and online systems, leaving people unable to access the services they rely on daily.
Beware of fake IT support scammers on Microsoft Teams who are tricking unsuspecting workers into installing malware by posing as tech support staff. These impostors are using the popular collaboration platform to deceive and compromise employee devices.
The UK government's Cyber Resilience Pledge has gained momentum with 60 signatories, demonstrating a united front against cyber threats. By signing the pledge, businesses acknowledge that cyber resilience is a top priority, not just an IT issue, but a business imperative.
China-aligned hackers are exploiting vulnerabilities in Roundcube email servers to gain access to sensitive university networks, specifically targeting physics and engineering departments with national security ties. They've cleverly designed their attacks to fly under the radar, using tactics like compromised senders and spoofed domains to reach their targets.
Joining forces to combat cyber threats, the UK government has launched a groundbreaking Cyber Resilience Pledge, signed by over 60 organisations, to strengthen board-level accountability and supply chain security. By making three key commitments, signatories can bolster their defences and stay ahead of emerging threats.
Microsoft is shaking things up for enterprise systems by enabling Windows settings backup by default for eligible devices running Windows 11, version 26H2, making it a breeze to restore settings after a device reset or upgrade. This move streamlines the process, giving enterprises a seamless way to maintain their users' customized settings.
Critical software flaws in BeyondTrust's Remote Support and Privileged Remote Access products could allow hackers to bypass authentication and gain unauthorized access, potentially putting your system integrity at risk. Two vulnerabilities, CVE-2026-40138 and CVE-2026-40139, have been identified, highlighting the urgent need for an update.
With 775 exposed ColdFusion instances online, a newly patched flaw is being exploited by attackers, putting countless systems at risk. Adobe has urgently warned customers to apply updates immediately to protect against this and 10 other critical vulnerabilities.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
A critical vulnerability in Tenda router firmware, tracked as CVE-2026-11405, allows hackers to bypass password verification and gain full administrative control of your device. This hidden backdoor puts your online security at risk, and a patch is still pending.
Say goodbye to tedious reinstallation processes! Microsoft is testing a game-changing Cloud Rebuild feature in Windows 11, allowing users to restore their PC to a clean state with a simple, full OS reinstall - even if Windows won't boot.
BeyondTrust has patched critical flaws in its Remote Support and Privileged Remote Access software that could let hackers take control of affected systems - but you can safeguard yours with a simple update to version 25.3.3 or higher.
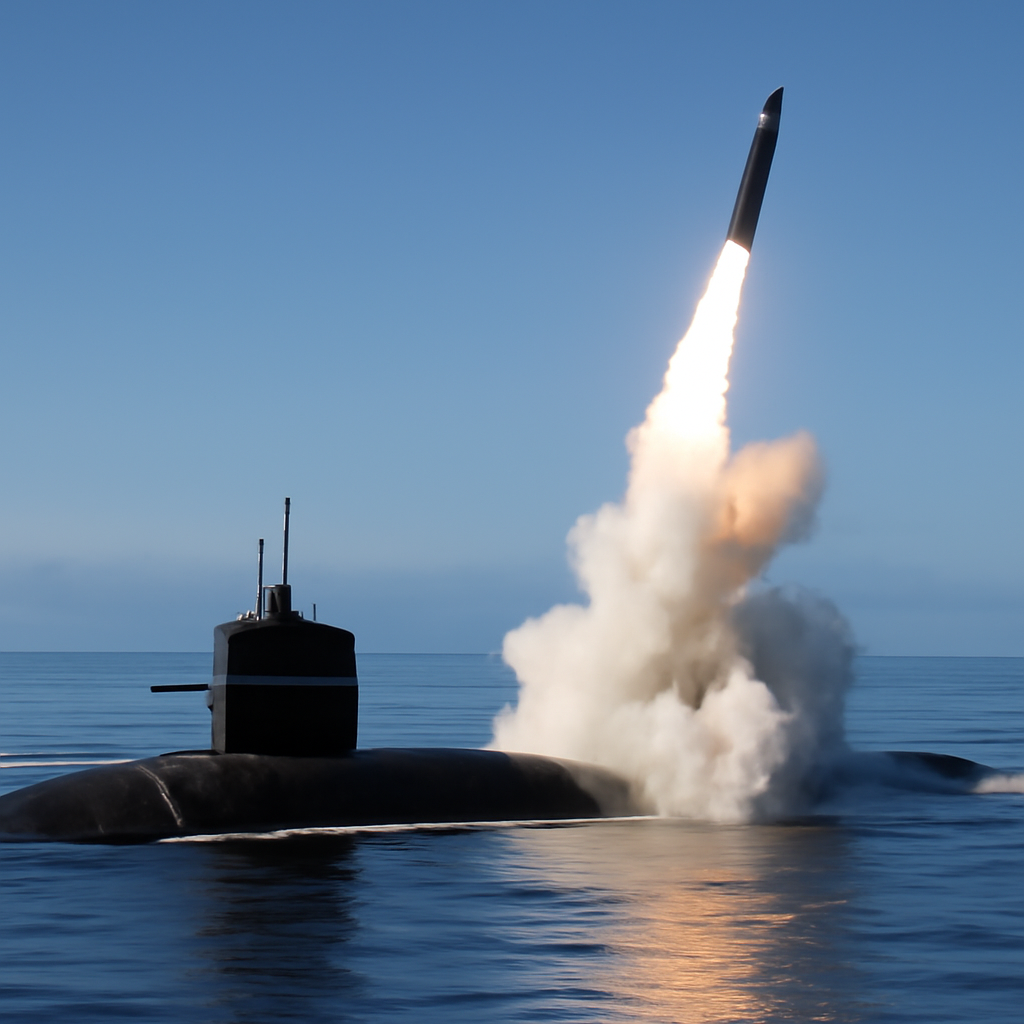
China's People's Liberation Army Navy successfully tested a submarine-launched ballistic missile in the Pacific Ocean on July 6, with the missile accurately landing in a predetermined sea area. The drill was part of routine annual military training, with relevant countries notified in advance, according to the PLAN.
Ukraine's capital was left vulnerable to a devastating Russian attack due to a critical shortage of Patriot interceptor missiles, which failed to shoot down a barrage of ballistic and hypersonic missiles that killed at least 20 people. The alarming gap in Ukraine's air defenses has raised urgent concerns about the country's ability to protect its citizens.
Canada is set to supercharge its underwater fleet with a dozen cutting-edge German-made Type 212CD submarines, tripling the Royal Canadian Navy's current capabilities in a $12 billion deal that's a major win for ThyssenKrupp Marine Systems. This game-changing investment will replace the Navy's aging Victoria-class boats with a more advanced, Arctic-focused fleet.
Democratic governments are taking a proactive approach to securing their critical mineral supplies, with Australia's recent announcement of a Critical Minerals Strategic Reserve being the latest example. This move is part of a growing trend to build resilience and reduce reliance on vulnerable supply chains dominated by a single country.
Witness the awe-inspiring display of North Korea's military might as the Kang Kon frigate unleashes a barrage of 12 strategic cruise missiles and a dizzying array of heavy machine guns. Kim Jong Un personally oversaw the impressive multi-system sea trial, showcasing the vessel's cutting-edge capabilities.