Tag: supply chain
1744 articles
China's Military AI Logistics Expose New Vulnerabilities in War
China's military is betting big on artificial intelligence to supercharge its logistics, but this bold move may backfire in the chaos of war, creating vulnerable chokepoints that could leave its operations crippled. Mike Tyson's famous words - "everybody has a plan until they get punched in the face" - are particularly apt for Beijing's high-stakes gamble.
Ukraine's Patriot Missile Production Hinges on Complex Supply Chain
In a surprise move, President Trump offered Ukraine a license to produce Patriot missile interceptors, a deal that could bolster the country's defenses, with the US also pledging to provide additional interceptors from its existing stockpile. The unexpected agreement was reached during a meeting between Trump and Ukrainian President Zelensky at the NATO Summit in Ankara, Turkey.
Venus Aerospace Secures $91 Million for Rocket Engine Production Scale-Up
Venus Aerospace is poised to supercharge its rocket engine production with a whopping $91 million in new funding, led by Mercury Fund and backed by Lockheed Martin Ventures. This major investment will help the Houston startup scale up to meet soaring demand from commercial and government clients.
AssuranceAmerica Breach Exposes 6.9 Million Driver Records
On March 17, 2026, AssuranceAmerica detected a security breach that put 6.9 million driver records at risk, allegedly caused by a malicious attack on one of its employees on March 16, 2026. The company has begun notifying affected individuals about the breach.
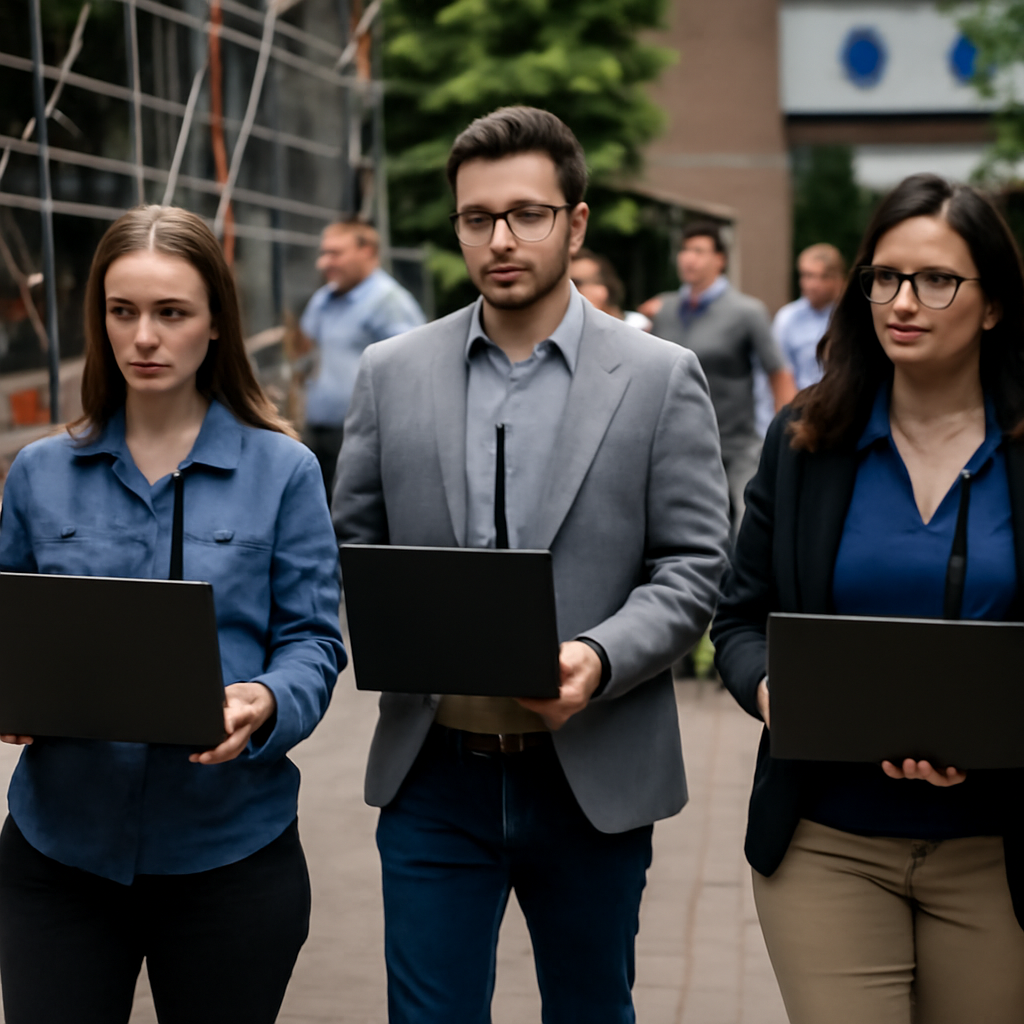
Red Teamer Exploits Trust to Steal Priceless Trophy
Imagine walking onto a secure campus with equipment in plain sight and a convincing story, and having employees roll out the red carpet - literally. A professional red teamer and his colleagues did just that, effortlessly gaining access to a Fortune 500 company's high-security site by exploiting one simple vulnerability: trust.
AI Coding Assistants Exposed to Symlink Flaw
Researchers uncovered a major vulnerability, dubbed GhostApproval, that affects six popular AI coding assistants, allowing attackers to manipulate the code and write malicious data into sensitive files. This flaw uses a clever trick involving deceptively named files and symbolic links to catch AI assistants off guard.
Chinese Spies Exploit Roundcube Flaw to Breach University Servers
A recent series of university server breaches, attributed to a group called UNK_MassTraction, has exposed vulnerabilities in North American higher-education institutions, with potentially dozens more affected. The breach, linked to a flaw in Roundcube, is believed to be an ongoing campaign.
Paris Peace Forum Launches Global Hub to Track AI Cyber Threats
The Paris Peace Forum is tackling the growing threat of AI-driven cyber attacks by launching INTAiC, a groundbreaking global hub that unites experts from two previously separate spheres: network defense and AI security. By bridging this gap, INTAiC aims to provide a unified front against the evolving risks to global internet infrastructure.
Hackers Exploit Roundcube Flaw to Target Academic Researchers
A new wave of cyber attacks linked to China is targeting academic researchers in the US and Canada, specifically those in physics, engineering, and national security-related fields, by exploiting a vulnerability in Roundcube webmail servers. The campaign, tracked as 'UNK_MassTraction', has been ongoing since May and has already hit several universities.
Phishing Campaign Targets Microsoft 365 Users with Voice-Based Entra Passkey Scam
Beware of scammers impersonating Microsoft 365, tricking users into enrolling a fake Entra passkey by mimicking the real enrollment portal and leveraging voice calls to urge action. This sneaky phishing campaign has been targeting multiple sectors since April, putting unsuspecting users at risk.
Anthropic's Claude Code Exposes Security Risk, China Alleges
A Chinese cybersecurity group has raised a red flag about a potential backdoor security risk in Anthropic's Claude Code, warning that certain versions can secretly send sensitive user data to remote servers without consent. This alarming claim puts users' identity and location information at risk.
Accenture Breach Exposes Source Code, Heightens Supply Chain Risk
Accenture's recent data breach, where 35GB of sensitive data including source code was stolen, shines a spotlight on the hidden risks of working with major consulting and services firms. As a trusted partner to businesses and governments worldwide, Accenture's breach heightens concerns about supply chain vulnerabilities.
AI Coding Agents Expose Unix-Era Security Flaw
A clever trick that exploits a long-standing Unix security flaw, dubbed GhostApproval, can bypass human approvals in AI coding assistants, rendering consent meaningless. By manipulating a harmless-looking project file, attackers can secretly alter sensitive system settings.
Turkish Defence Firms Penetrate NATO Markets Amid European Rearmament Push
Turkish defence firms are making a major breakthrough into NATO markets, with record exports of over $10 billion in 2025, and sales to Europe and the US nearly quadrupling to $5.6 billion. Turkish companies are now supplying top NATO nations like Poland, Spain, Portugal, and Romania with cutting-edge military hardware.
China Warns of Claude Code Backdoor Risks, Urges Developers to Uninstall
China's National Vulnerability Database has issued a high-priority alert, warning developers to immediately uninstall certain versions of Claude Code due to a potential backdoor risk that could compromise sensitive data. Upgrade to the latest secure version to safeguard your information.
Australia Exposed to Uyghur Forced Labour Imports
Australia's imports from China have raised red flags, with a staggering $6.95 billion worth of goods from high-risk sectors linked to Uyghur forced labour flooding the market in 2024. This exposes the country to a redirected risk of inadvertently supporting human rights abuses through its supply chains.
GitHub Verified Commits Can Be Rewritten Without Breaking Signatures
A recent study revealed a surprising vulnerability in GitHub's verified commits, showing that signed commits can be rewritten without breaking their digital signatures. This means that tampered code can still be labeled as Verified, posing a significant risk to code security.
Ubiquiti Discloses Max-Severity UniFi OS Vulnerability
Ubiquiti has urgently patched a critical vulnerability in its UniFi OS, warning customers of a maximum-severity flaw that could allow malicious actors to inject commands on host devices - and it's crucial to upgrade to version 3.4.20 or later to stay safe.
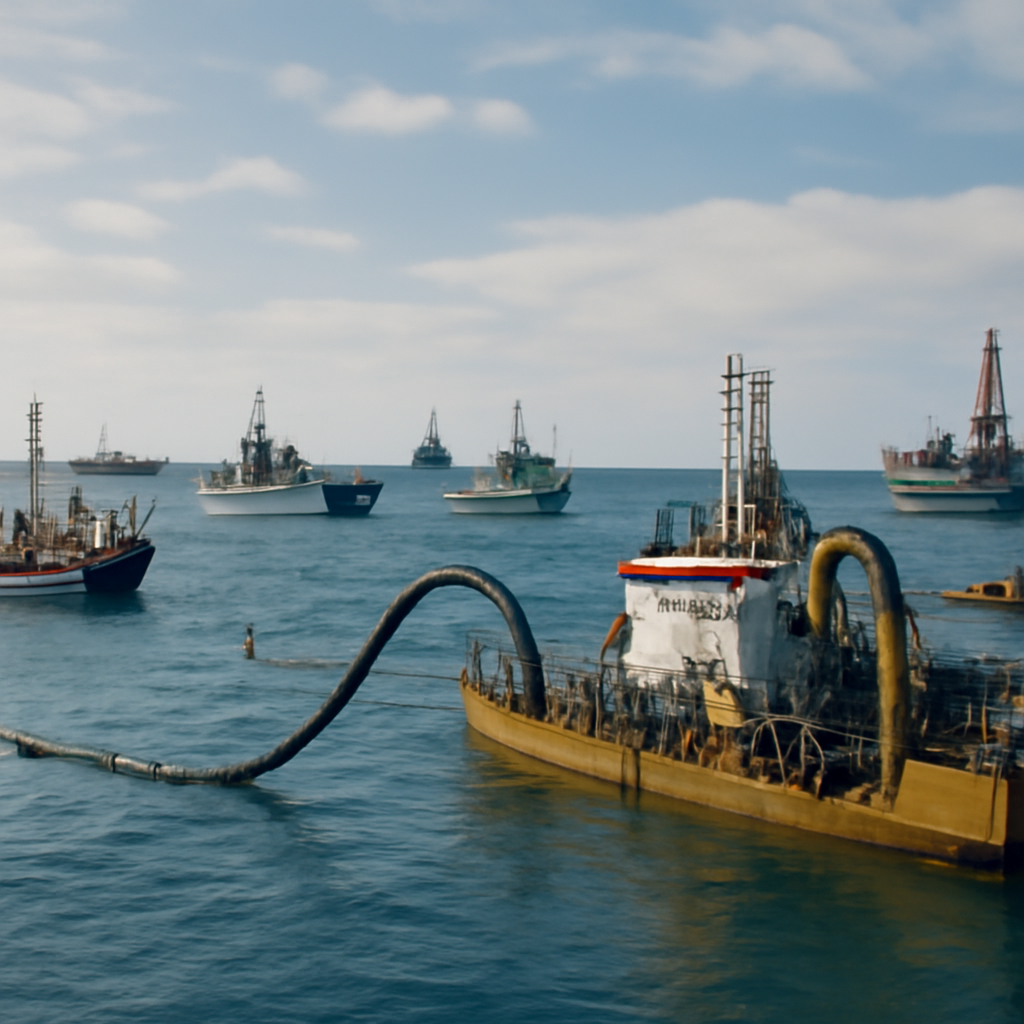
Pacific Seabed Becomes Contested Zone in Regional Power Struggle
The Pacific seabed, once a vast and empty space, has become a hotly contested zone as a growing number of nations and interests converge on its valuable resources, transforming the way power and risk are distributed in the region. This emerging crowded landscape is sparking new tensions, as mining, military operations, and other activities increasingly overlap and collide.
Malicious Activity on Industrial Systems Declines to 3-Year Low
Malicious activity on industrial systems has hit a 3-year low, with only 19.6% of ICS computers encountering malicious objects in Q1 2026 - a significant drop of 1.4 times from Q2 2023. However, beneath the calm surface, localized spikes of threats persist, warranting close attention.
Microsoft Telemetry Fingers Scattered Spider Suspect in US Crackdown
Microsoft's sharp-eyed telemetry has helped track down a suspect linked to the notorious Scattered Spider group, a prolific gang that allegedly raked in over $100 million in ransom payments by infiltrating more than 100 US company networks.
GitHub AI Agent Exposes Private Repos to Malicious Prompts
A shocking vulnerability in GitHub's AI-powered Agentic Workflows has been discovered, allowing attackers to expose private repositories with just a cleverly crafted issue and some plain English instructions - no coding skills or credentials required. This flaw lets hackers fetch and publicly share sensitive files, putting organizations at risk.
Google Dialogflow Flaw Lets Rogue Agents Hijack Chatbots
A security flaw in Google Dialogflow, dubbed "Rogue Agent," allowed hackers to hijack chatbots, but thankfully, a fix was rolled out after Varonis reported the issue through Google's Vulnerability Reward Program. The flaw was cleverly exploited through custom Code Blocks in Dialogflow CX, highlighting the importance of robust security measures in chatbot development.
GitHub Agentic Workflows Exposed to Data Leak Threat via Public Issues
GitHub's Agentic Workflows are vulnerable to a data leak threat, as researchers have demonstrated a clever technique called GitLost that tricks AI agents into spilling private content from secure repositories into public comments. All it takes is a simple public issue to launch the attack, with no stolen credentials or special access required.