Tag: supply chain
1744 articles
Lidl Data Breach Exposes Customer Info Across Europe
Lidl has warned customers in Belgium and the Netherlands that a data breach exposed their personal info, after unidentified individuals briefly accessed a file containing customer data stored with a third-party IT provider. The breach affected online customers in Germany, Belgium, and the Netherlands, but Lidl stresses that its online shop system itself was not compromised.
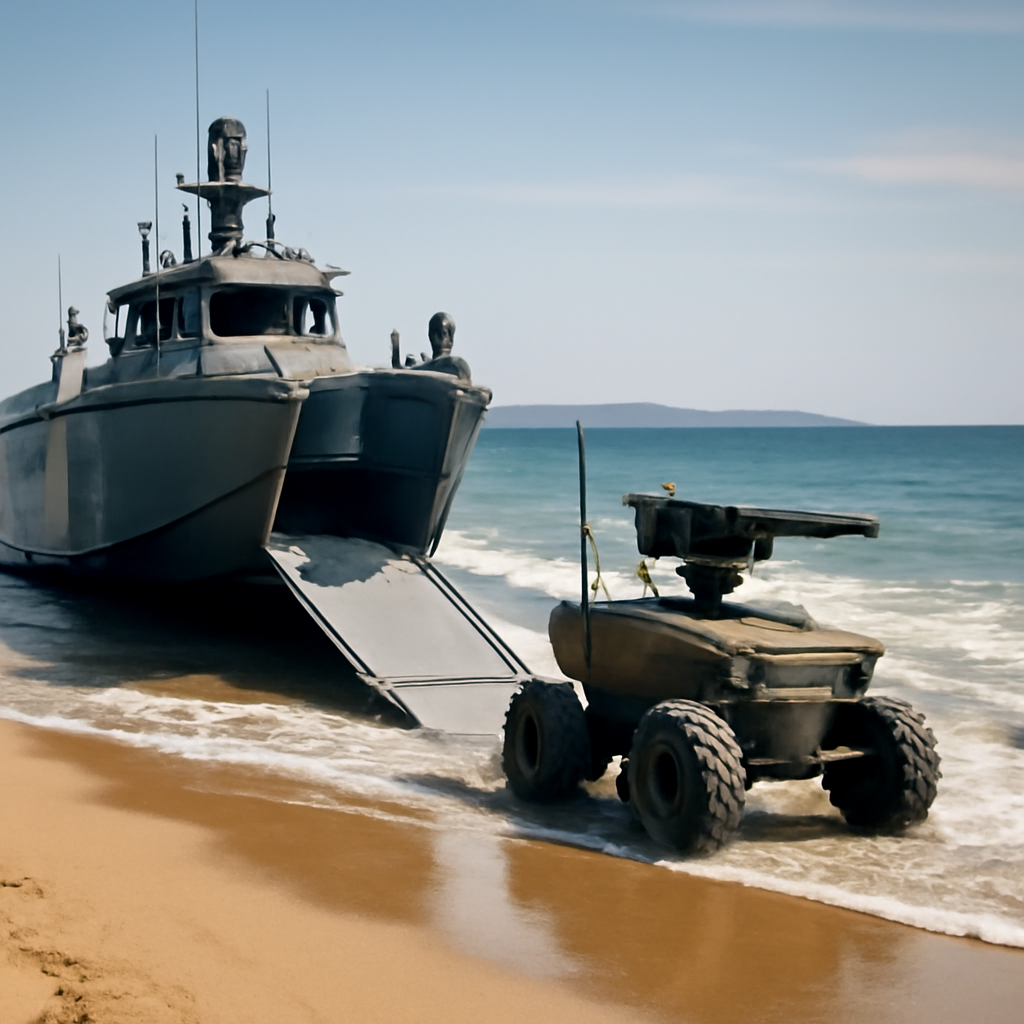
Ukraine Deploys Armed Robot Behind Russian Lines via Drone Boat
In a groundbreaking operation, Ukraine's 123rd Separate Territorial Defense Brigade has successfully deployed an armed robot behind Russian lines using a drone boat, marking a new era in modern warfare. The daring mission was captured on video, showing the robot, armed with a 7.62mm machine gun, engaging a target on the occupied Kinburn Spit.
Jscrambler npm Package Infected with Infostealer Malware
A malicious version of the Jscrambler npm package was published, infecting nearly 1,500 downloads with infostealer malware within a two-hour window before being removed and replaced with a safe version. The incident was quickly contained, but users who downloaded the compromised package between releases 8.14 and 8.20 may be at risk.
Citrix Bleed 2 Exploit Fuels Ransomware Attacks
Ransomware attacks are on the rise, fueled by a new exploit that has already made a significant impact, and now a major software company has ordered its customers to take critical systems offline due to a credible security threat. Progress has urged customers to shut down vulnerable Windows servers to prevent potential breaches.
Chinese and Indian Spies Target Pakistani Police Systems
Suspected Chinese and Indian spies launched a targeted attack on Pakistani police systems, specifically focusing on the Balochistan Police, between February 2024 and April 2026. The intrusion campaigns compromised sensitive data, including biometric records, criminal case files, and national identity information.
Lidl Online Shop Breach Exposes Customer Data After Service Provider Hack
Lidl's online shop was hit by a data breach after a service provider was hacked, exposing customer information - but fortunately, the online shop's system itself remained secure. The company has notified affected customers and taken steps to address the issue.
Infostealer Infection Enables Argentine FA Breach
A single compromised computer with high-level access likely gave hackers the keys to the Argentine Football Association's database and internal email system, thanks to an infostealer infection that went undetected for months. The breach, traced back to September 8, 2025, highlights the devastating impact of a simple infection on a high-privilege machine.
Russian Hackers Target Routers Globally, Warn Cybersecurity Agencies
A brazen plot by Russian hackers to disrupt global networks was thwarted, but not before cybersecurity agencies warned of a potentially catastrophic attack that could have left 500,000 citizens shivering in the dark. The hackers, linked to Russia's Federal Security Service, targeted vulnerable routers worldwide using simple and easily exploitable passwords.
Compromised jscrambler NPM Package Drops Rust Infostealer
A malicious version of the jscrambler NPM package, 8.14.0, was published on July 11, 2026, and could silently infect your system with a Rust-based infostealer just by installing it, no extra steps required. Merely running the install command was enough to trigger the payload on vulnerable systems.
U-Boot Flaws Expose Devices to Code Execution, Crashes
Six newly discovered flaws in U-Boot, a widely used bootloader, leave devices from home routers to data-center servers vulnerable to code execution and crashes, posing a significant risk to everything that loads after it. These vulnerabilities can be exploited before the operating system even starts, undermining the entire security chain.
GitHub Compromise Injects Malicious npm Packages with Wallet-Key-Stealing Code
A malicious actor hijacked a trusted GitHub account and used it to inject wallet-key-stealing code into 18 npm packages, including Injective Labs' SDK, by exploiting the project's pipeline. This sneaky move allowed the attacker to spread the backdoor through a series of seemingly legitimate updates.
AI Agents Expose Identity Security Gap
The alarming truth is that security systems, designed with people in mind, are failing to protect against AI agents - and the consequences are stark. A single compromised machine identity can become a gateway to a vast array of sensitive information, as a recent breach involving an OAuth token and hundreds of organizations painfully illustrates.
Hackers Exploit Microsoft Entra Passkey Enrollment in Voice Phishing Attacks
Hackers are using voice phishing attacks to trick Microsoft 365 users into enrolling a new Entra passkey, targeting multiple sectors including food and beverage, technology, and healthcare. They're registering domains with the word "passkey" to convincingly pose as legitimate Microsoft representatives.
Ex-Con Ransomware Negotiator Sentenced for BlackCat Attacks
A former ransomware negotiator, Angelo Martino, has been sentenced to 70 months in prison for his role in a string of BlackCat ransomware attacks that targeted multiple victims between 2023 and 2025. Martino's guilty plea brings to justice a key player in the notorious ALPHV ransomware gang.
Australia Urged to Cultivate Domestic Critical Minerals Workforce
Australia's mining sector is facing a critical shortage of skilled workers, with a 63% skills gap in 2022, and recent university closures are exacerbating the problem, threatening to leave valuable mines and processing plants idle. The country lags far behind China, which churns out 3,000 mining engineering graduates annually from 45 programs.
Australia's Strategic Focus Shifts to Endurance Over Efficiency in Infrastructure Investment
Imagine a 2,700 km corridor that connects Darwin to Port Augusta, but it's more than just a highway - it's a complex system that supports defence, freight, and community needs across northern Australia. This critical infrastructure, known as the Stuart corridor, is a lifeline that weaves together highways, railways, fuel storage, telecommunications, and industrial supply chains.
OpenMandriva Linux Project Hit by Sabotage Attempt
Davide Beatrici, a leading developer of the Mumble app, has denied allegations of sabotage against the OpenMandriva Linux Project, claiming his actions were deliberate but not malicious. He admitted to deleting key repositories and pushing a package, but insists his moves were targeted, not hurtful.
npm Package Infects Developers with Cryptocurrency Wallet Stealer
A malicious npm package, downloaded a staggering 50,000 times weekly, was briefly infected with code that stole cryptocurrency wallet private keys and sensitive seed phrases, putting countless developers at risk. The attack was launched after a contributor's GitHub account was compromised, allowing the hackers to spread the poisoned code across multiple projects.
Turkey's TEI Advances Domestic Turbofan to Break Ukraine Engine Chokepoint
Turkey's TEI is making significant strides in developing its domestic turbofan engine, with plans to deliver the TF6000 to Baykar and Turkish Aerospace Industries by early 2027 for pre-integration testing. This milestone marks a crucial step towards breaking Ukraine's engine chokepoint and advancing Turkey's aerospace capabilities.
GitHub Accounts Used to Map Corporate Orgs in Stealthy Campaigns
Cyber attackers are using sneaky tactics, leveraging old or compromised GitHub accounts, to secretly map out corporate organizations and steal sensitive data. They're exploiting loopholes with automated tools and stolen tokens to quietly gather intel from GitHub APIs.
GitHub npm Tightens Security With Disabled Install Scripts
GitHub's latest npm update takes a giant leap in security by disabling install scripts by default, reducing supply-chain risks and giving developers more control. To adapt, plan to switch to trusted publishing or staged publishing with human approval for automated publishing.
Clearinghouses Race to Remediate Pre-Disclosure Vulnerabilities
Chainguard's Athena clearinghouse has been quietly remediating vulnerabilities for months, converting findings into fixes at an incredible pace, with a one-day SLA on actively exploited vulnerabilities and over 100,000 issues resolved so far. This swift action comes as the threat landscape accelerates, with the mean time to exploit now estimated at just -7 days.
AI Coding Assistants Expose Flaw in Approval Process
Researchers have uncovered a shocking flaw, dubbed GhostApproval, that affects six major AI coding assistants, allowing malicious code to bypass approval prompts and wreak havoc on a developer's machine. This vulnerability can be exploited through a clever use of symbolic links, posing a significant risk to developers who rely on these tools.
Beijing Intensifies Campaign to Isolate Taiwan
Beijing's campaign to isolate Taiwan has taken a more sinister turn, with everyday obstruction and procedural meddling making it increasingly costly for Taipei to engage with the world. From botched visas to high-profile exclusions, China's tactics are raising the stakes and making Taiwan's isolation a harsh reality.