Tag: supply chain
1740 articles
Cisco Discloses Active Exploitation of ISE Flaw
Cisco warns that a critical API vulnerability, CVE-2026-76460, is under active exploitation, allowing attackers to bypass security and gain unauthorized access to devices with a simple crafted request. This maximum-severity flaw scores a perfect 10.0 on the CVSS scale, making it a high-risk threat that demands immediate attention.
Cisco Discloses Actively Exploited Zero-Day in Identity Services Engine
Cisco has sounded the alarm on a critical zero-day flaw in its Identity Services Engine that's being actively exploited by attackers, allowing them to bypass authentication and gain unauthorized access. To stay safe, customers are urged to upgrade to a patched version ASAP.
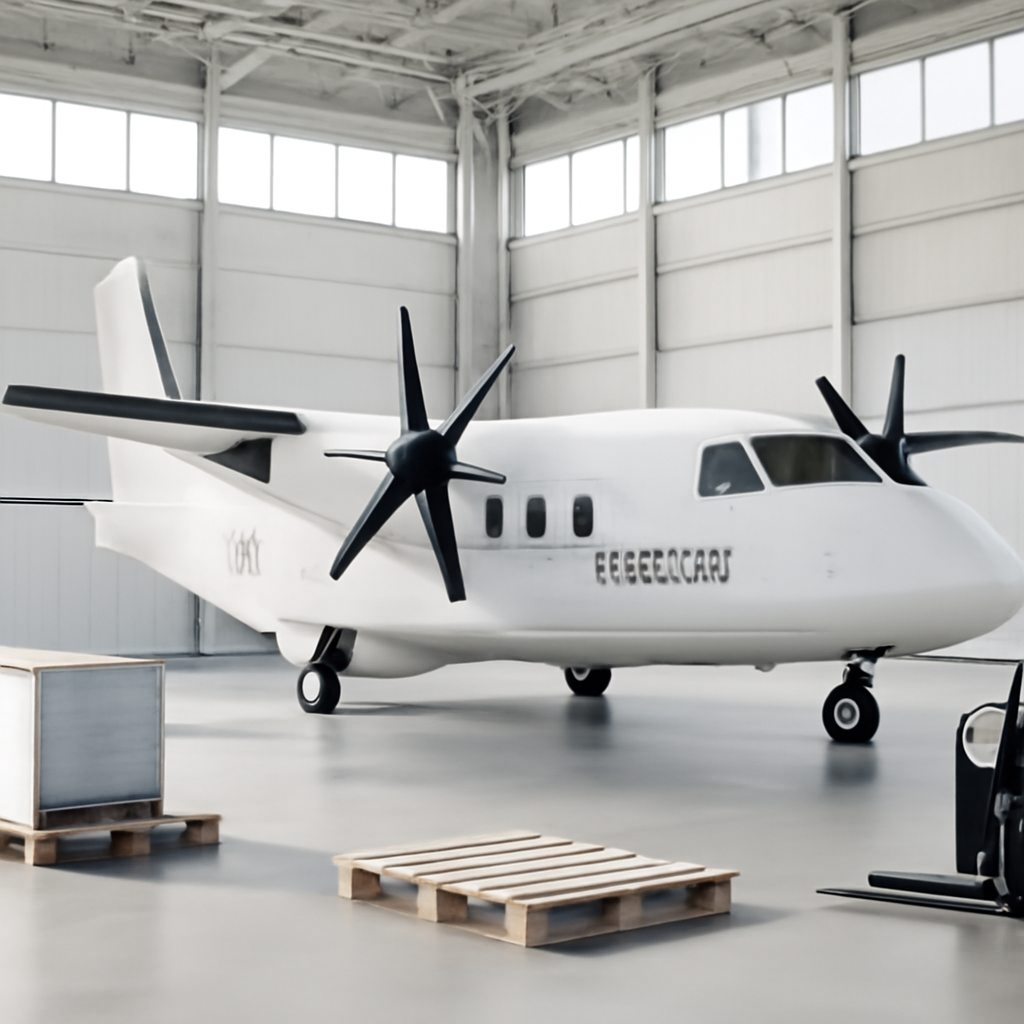
Textron Unveils SkyCourier UX for Uncrewed Logistics
Imagine a logistics solution that can rapidly deliver critical supplies to any location - from the Arctic to the Amazon - and now, thanks to Textron and Merlin Labs, that vision is a reality with the unveiling of the uncrewed SkyCourier UX. This game-changing aircraft leverages a proven twin-turboprop design to accelerate from concept to combat logistics.
Australia's Iron Ore Exports Face Looming Value Decline
Australia's iron ore export earnings are expected to plummet by 34% by 2030-31, despite a mere 2% decline in export volume, raising the question: can shipment volumes alone preserve income and jobs? The answer lies in a strategic shift in policy.
Australia's Research Sector Divided Over Security Reforms
As Australia's research sector navigates new national security reforms, a pressing question emerges: can freedom and vigilance coexist? The country's top universities are already feeling the impact, with recent terminations of high-profile partnerships sparking a heated debate.
Industrial Base Accelerates to Meet Air Force, Space Force Demands
The Air Force and Space Force are turning to the industrial base to turbocharge their capabilities, and the message is clear: they need more, and they need it fast. Ursa Major CEO Chris Spagnoletti shares his insights on the demands military leaders are placing on the industrial base.
Pentagon Procurement Chief Warns of Industrial Base Strains
The Pentagon's top procurement officer, Air Force Gen. Dale R. White, is sounding the alarm on strains in the US defense industrial base, warning that capacity concerns are widespread and affecting multiple platforms. These worries aren't limited to specific programs like the F-35 or F/A-XX, but are a broader issue that demands attention.
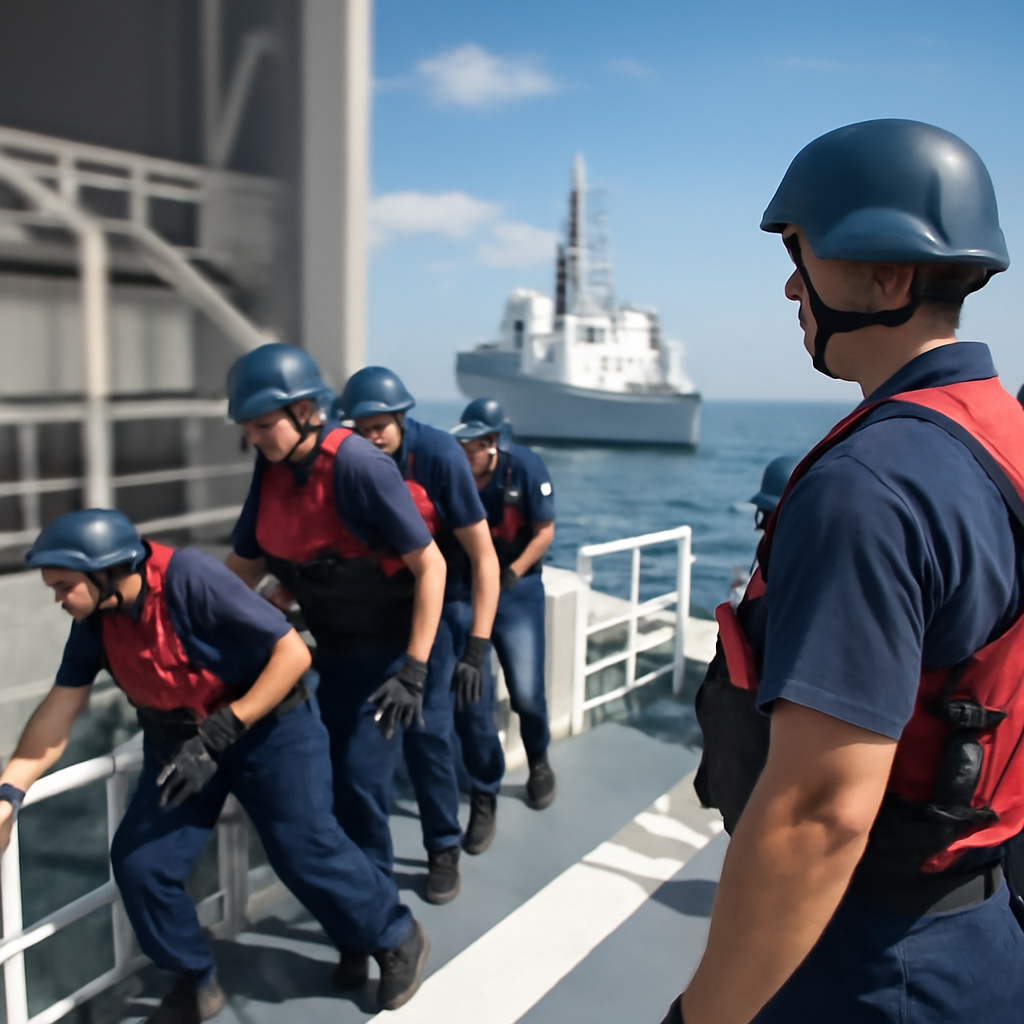
US Coast Guard, FBI Intercept Foreign Ships to Investigate Cyberattacks
In a proactive move to safeguard the nation's maritime security, the US Coast Guard and FBI teamed up to board two foreign commercial tankers in the Gulf of Mexico, investigating suspected cyberattacks that could have put crew safety and environmental stability at risk. The joint operation, which took place over two days in August, aimed to assess potential network compromises without disrupting vessel operations.
Browser Extensions Expose AI Assistants to Takeover Risk
Researchers found that AI assistants in popular browser extensions are vulnerable to takeover risks due to a common architecture that splits the assistant into a browser-based "body" and a server-based "brain". This setup can be exploited with just two ordinary permissions, leaving users exposed.
Russian Enterprises Targeted by Backdoor, Ransomware Attacks from Three Threat Groups
Russian enterprises are under attack by three threat groups, with hackers exploiting compromised credentials to breach corporate VPNs and deploy powerful malware like GhostContainer, a modular backdoor that gives attackers complete control over Microsoft Exchange Servers. This sneaky malware can run arbitrary code, manipulate files, and hide in plain sight, making it a formidable foe for even the most secure systems.
Mandiant Exposes AI Coding Assistant Vulnerability to Shai-Hulud Worm
A hacker hijacked an AI coding assistant session, using it as a launchpad to deploy the Shai-Hulud worm across nearly 100 internal code repositories. This alarming incident highlights the vulnerability of AI-powered coding tools to exploitation.
N0va Phishkit Targets Businesses with Legitimate Authentication Flows
Meet N0va, a sneaky phishkit that's duping businesses across North America and Europe by masquerading as trusted services and exploiting genuine authentication flows. Its clever attack chain can swiftly turn a single phishing click into persistent access to corporate resources.
Acronis Plugin Vulnerability Exploited in Targeted Attacks
A high-severity vulnerability in Acronis' Backup plugin has been exploited in targeted attacks, allowing attackers to escalate privileges on Linux deployments - and a patch is available in update 1.9.3 HF3. Users are urged to install it immediately to avoid potential security breaches.
WSO2 API Manager Flaw Sees Active Exploitation Attempts
A critical flaw in WSO2 API Manager, tracked as CVE-2026-5430, is under active exploitation, allowing hackers to bypass JWT authentication and gain unauthorized access with a CVSS score of 9.8 out of 10.0, potentially leading to account takeover and compromise of administrative accounts.
Anduril Warns of Delay in CCA Drone Production Without FY27 Budget
Anduril's VP for strategy execution, Erin Simpson, warns that without a FY27 budget, production of the FQ-44 Fury drone will be delayed, despite the company's significant investments in a new production facility and long-lead items. Even with a head start, Anduril needs procurement dollars to move forward with full-rate production.
Apple Discloses Record 260 Vulnerabilities in Massive Patch Cycle
Apple just dropped a massive patch cycle, tackling a record-breaking 260+ vulnerabilities across its operating systems, browsers, and software products - the largest update of its kind in the company's history. This critical update includes fixes for 122 security issues in iOS 27 and 204 in macOS 27 Golden Gate.
Compromised Plugin Backdoors 1,500 WordPress Sites
A malicious update to the WordPress plugin Admin Menu Editor Pro infected around 1,500 sites with a backdoor, after hackers compromised the plugin's update server and uploaded a trojanized version. The attackers even created a hidden user account and installed a web shell on affected sites.
Pratt Licenses Hermeus to Produce F100 Fighter Jet Engine
Pratt & Whitney is teaming up with aircraft startup Hermeus to produce the F100-PW-229 turbofan, a powerful engine that has been propelling some F-15 and F-16 fighter jets since 1992. This marks Pratt's first-ever license agreement of its kind with a fellow American company, aiming to strengthen the defense industrial base.
Cisco Discloses Actively Exploited Zero-Day in Email Gateways
A critical zero-day vulnerability, CVE-2026-76461, is under active exploitation, allowing hackers to remotely execute commands as root on Cisco Secure Email Gateway appliances with just a simple email. This gaping security hole gives attackers total control of the gateway, putting your email security at risk.
Fraudulent Hires Evade Detection, Gain Network Access Before Exposure
Imagine getting hired, passing background checks, and receiving your official login credentials - all without being who you claim to be. Once inside, malicious hires can wreak havoc for days, with the average fraudulent employee enjoying 5.73 days of unrestricted access to sensitive corporate networks.
Cisco Email Gateways Exploited by Malicious Emails
A single malicious email can wreak havoc on your Cisco Secure Email Gateway, thanks to a critical vulnerability (CVE-2026-76461) that allows hackers to gain root access with a 9.8 CVSS score - and patching is the only fix.
Mass-Scanning Campaign Exploits Vite Flaw to Harvest Cloud Credentials
A high-severity flaw in Vite, tracked as CVE-2026-39364, has been exploited in a mass-scanning campaign, allowing attackers to bypass security restrictions and harvest cloud credentials. By manipulating query parameters, unauthenticated attackers can leak sensitive files that were meant to be blocked.
Ransomware gangs exploit VMware flaw
Ransomware gangs are actively exploiting a critical VMware flaw, CVE-2026-59310, that was patched just two weeks ago, putting organizations at risk of devastating attacks. The US Cybersecurity and Infrastructure Security Agency has warned of the vulnerability, which allows unauthenticated attackers to execute arbitrary code.
Microsoft Fixes RDS, Hyper-V Issues with Emergency Patch
Microsoft's massive September Patch Tuesday update, which bundled a record 974 CVEs, caused widespread disruptions to core services, including RDS and Hyper-V, just days after its release. The company has now issued an emergency patch to fix these issues, restoring stability to affected systems.