Tag: supply chain
1740 articles
CISA Warns of Active Exploitation of Linux Kernel Flaws
Hackers are actively exploiting three Linux kernel vulnerabilities, prompting the US Cybersecurity and Infrastructure Security Agency (CISA) to escalate them to the highest federal priority, requiring immediate security updates and forensic analysis. The alarming part? One of these flaws, CVE-2025-39964, had been lurking in the Linux kernel for a staggering 14 years.
Microsoft Resolves Excel Copy-Paste Issue After Security Updates
Microsoft has fixed a frustrating issue in Excel where copying and pasting data would fail silently, leaving users none the wiser - until now, that is! The problem, which emerged after September's security updates, affected various versions of Excel, including 2016, 2019, 2021, and 2024, as well as Excel Online.
Attackers Exploit npm Trusted Publishing in GHAPPIER Supply Chain Campaign
Malicious actors have cleverly exploited npm's trusted publishing feature to unleash a supply-chain attack, using a hijacked maintainer account to distribute a sneaky loader called GHAPPIER. They got away with it by hiding behind a valid provenance attestation, highlighting a loophole in the system.
Jade Sleet Targets Indian IT Provider with FLATROOF and ROOFDECK Backdoors
North Korean-aligned threat actor Jade Sleet has launched a targeted attack on an Indian IT provider, using FLATROOF and ROOFDECK backdoors to gain long-term access to high-value targets by exploiting developer workflows and supply-chain tooling. The attack, detected as early as March 18, 2026, is part of a persistent campaign that highlights the group's evolving tactics.
Australia Urges Substitutes for Critical Minerals
As new US defence procurement rules take effect in 2027, Australia is pushing to reduce its reliance on critical minerals from uncertain foreign sources by exploring substitutes that can perform the same function. By finding alternative materials, Australia can build a more resilient supply chain - and fast.
Malicious npm packages exploit runtime evasion tactics
Meet the sneaky npm package that impersonated a popular library, racking up 2 million weekly downloads before revealing its true malicious intent. This cleverly disguised package, indexed-btree, hid its payload in plain sight, masquerading as a legitimate tool until it was too late.
North Korean Hackers Infect 30,000 Devices in Global Campaign
North Korean hackers have pulled off a massive global cyberattack, infecting 30,000 devices in over 100 countries and making off with millions in cryptocurrency. The financially motivated gang, known as WaterPlum, has been siphoning funds and account credentials from over 7,000 cryptocurrency wallets since December 2025.
TanStack npm Attack Exposes 170 Private GitHub Repositories
A shocking npm attack on TanStack exposed a massive 170 private GitHub repositories after a malicious actor exploited a stolen OAuth token from a former employee's account. The breach was linked to a supply-chain compromise of TanStack's npm packages, tracked as CVE-2026-45321, which allowed attackers to steal sensitive credentials.
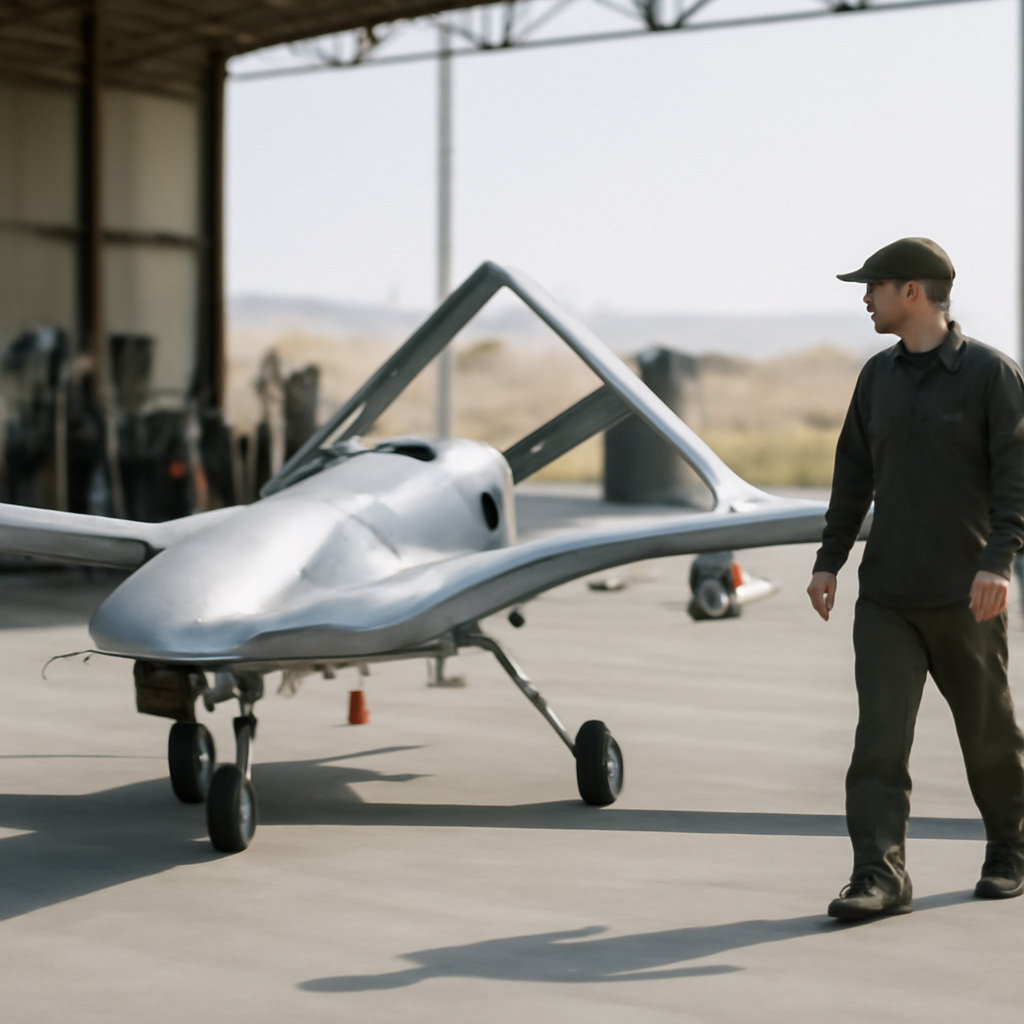
Central Asia Turns to Local Drone Development to Curb Foreign Security Dependency
Central Asian countries are ditching foreign security solutions and turning to local drone development to break free from dependency on external suppliers. Kyrgyzstan's recent procurement spree on Turkish drones, however, only serves to highlight the risks of new foreign entanglements.
North Korea Exploits Job Seekers to Infect 30,000 Devices
North Korean hackers have compromised over 30,000 devices by posing as recruiters, targeting unsuspecting job seekers with a clever ruse that steals sensitive information and cryptocurrency. By exploiting stolen IDs, these cybercriminals can impersonate victims and generate foreign currency, ultimately funding the regime.
Transparent Tribe Exploits GitHub for Rust Backdoor Deployment
Meet RUSTYSHADE, a sneaky Rust-based backdoor that's being used by Transparent Tribe to target government and defense organizations in India and Afghanistan, leveraging private GitHub repositories for covert communication. This latest tactic is part of a broader campaign, dubbed Operation RapidRust, aimed at infiltrating sensitive targets.
Malware Campaign Targets LastPass Users with Rapuncel Infostealer
Beware of a sneaky malware campaign targeting LastPass users with the Rapuncel Infostealer - hackers are using fake GitHub repositories and search engine tricks to steal your info. Victims who search for popular software like LastPass Authenticator may unknowingly download the malware.
Flaw in AI Coding Agents Exposes Users to Plugin Swaps
A newly discovered flaw, dubbed Plugin4Shell, allows hackers to swap out a plugin installed by an AI coding agent with malicious code, putting users at risk of having their files read, credentials stolen, and accounts compromised. This vulnerability was found in all four major AI coding agents, and the affected vendors have been notified.
Browser Alerts Expose Rogue Scripts in Thousands of Sites
Thousands of websites, repositories, and documentation pages are unwittingly exposing users to rogue scripts, thanks to a long-abandoned content delivery network domain that was re-registered by a malicious actor. This simple domain hack has opened the door to a massive security vulnerability.
npm Packages Deliver WeaselBiscuit Stealer to Harvest Chrome Data
Meet WeaselBiscuit, a sneaky new malware that's small but packs a punch, stealing Chrome data by masquerading as harmless npm packages. This stripped-down stealer is designed to evade detection, and it's being spread through 13 infected npm packages.
Ransomware Attacks Surge in Manufacturing Sector
Ransomware attacks on manufacturing organizations are surging, with a staggering 22% of all victims coming from this sector over the past year, making it the most targeted industry for the fifth year in a row. This alarming trend shows a steady rise in attacks since 2022, with a significant spike in early 2026.
Northrop, Lockheed Pursue Munitions Deals Amid Budget Uncertainty
Northrop Grumman is seizing the opportunity to collaborate with new partners and showcase its cutting-edge munitions products, aiming to secure a larger share of the market. The company is in active discussions with major contractors on around 10 agreements covering eight key weapons systems.
Iran-Linked Malware Exploits Telegram for Password Theft
Meet HEAVYGRAM, a sneaky Telegram backdoor linked to Iran that's packed with espionage capabilities, from snapping screenshots to siphoning off sensitive data, and controlled remotely by its masters. This malicious tool has been quietly lurking in the shadows since September 2023, leaving a trail of compromised systems in its wake.
Docker Flaw Lets Guest Code Read, Modify macOS Host Files
A newly discovered Docker flaw on macOS could allow malicious code in a virtual machine to break free from its sandbox and read or modify sensitive host files, potentially leading to code execution on the host. This vulnerability, tracked as CVE-2026-77179, leverages a weakness in the virtio-fs host server to gain unauthorized access.
AI Agents Expose New Attack Vectors
A shocking 230 out of 243 unauthenticated LocalAI instances were found to be vulnerable to exploitation, highlighting a disturbing trend: our increasing reliance on convenient tools is creating new avenues for old security mistakes. This alarming vulnerability was recently exploited in a large-scale campaign, compromising high-value targets, including infrastructure linked to the Thai military.
Check Point Flaw Lets Unauthenticated Users Execute Code as Root
A critical flaw in Check Point's Security Management and Log Servers, rated 9.8 out of 10, allows unauthenticated users to execute code as root via a simple login request with a very long username. Fortunately, there's no evidence that this vulnerability has been exploited in the wild - yet.
AI Coding Agents Expose Zero-Click Flaw
A newly discovered vulnerability, dubbed Plugin4Shell, allows attackers to execute remote code with just a single click - or none at all - giving them carte blanche access to sensitive data and assets. This zero-click flaw in AI coding agents highlights the urgent need for updated security measures to prevent devastating supply-chain attacks.
Pentagon Accelerates AIM-260 Missile Production Amid China Threat
The Pentagon is ramping up production of the AIM-260 missile to stay ahead of China's growing threat, with a new framework agreement with Lockheed Martin aimed at ensuring a stable and efficient supply chain. This move is part of a broader effort to accelerate development of cutting-edge air dominance weapons.
Brevo Cloudflare API Key Compromise Injects Malicious ClickFix Scripts
Attackers compromised a Cloudflare API key with full account permissions, allowing them to inject malicious scripts into website responses by creating a rogue Cloudflare Worker that cleverly evaded standard security checks. By modifying content at the CDN edge and removing key security headers, the hackers kept origin servers and files untouched, making the tampering difficult to detect.