Tag: supply chain
1740 articles
Microsoft Update Disrupts Excel Copy and Paste Function
Struggling with Excel's copy and paste function? A recent Microsoft update has caused a frustrating issue where content appears to paste, but actually doesn't - with no error message or warning to let you know something's gone wrong.
Cisco Discloses Zero-Day Exploited in Secure Email Gateway Attacks
Cisco has warned of a zero-day flaw in its Secure Email Gateway that allows attackers to run commands as root, prompting federal agencies to patch the vulnerability within just three days. This critical defect, tracked as CVE-2026-76461, lets hackers execute arbitrary commands with root privileges, putting systems at risk.
China-Linked Hackers Exploit Chrome-Windows Zero-Day Chain
Meet the sneaky hackers who just pulled off a triple threat: exploiting not one, not two, but three zero-day vulnerabilities to break free from Chrome's sandbox and wreak havoc on Windows hosts. Their latest move? A targeted spear-phish attack on NGOs via a cleverly crafted link.
Cisco Email Gateway Flaw Exploited, Enables Root Command Execution
A critical Cisco email gateway flaw, CVE-2026-76461, with a near-perfect CVSS score of 9.8, is being actively exploited in the wild, allowing attackers to send a single crafted email and gain root command execution on vulnerable devices. This severe vulnerability stems from insufficient validation in AsyncOS email parsing, making it a pressing concern for Cisco Secure Email Gateway users.
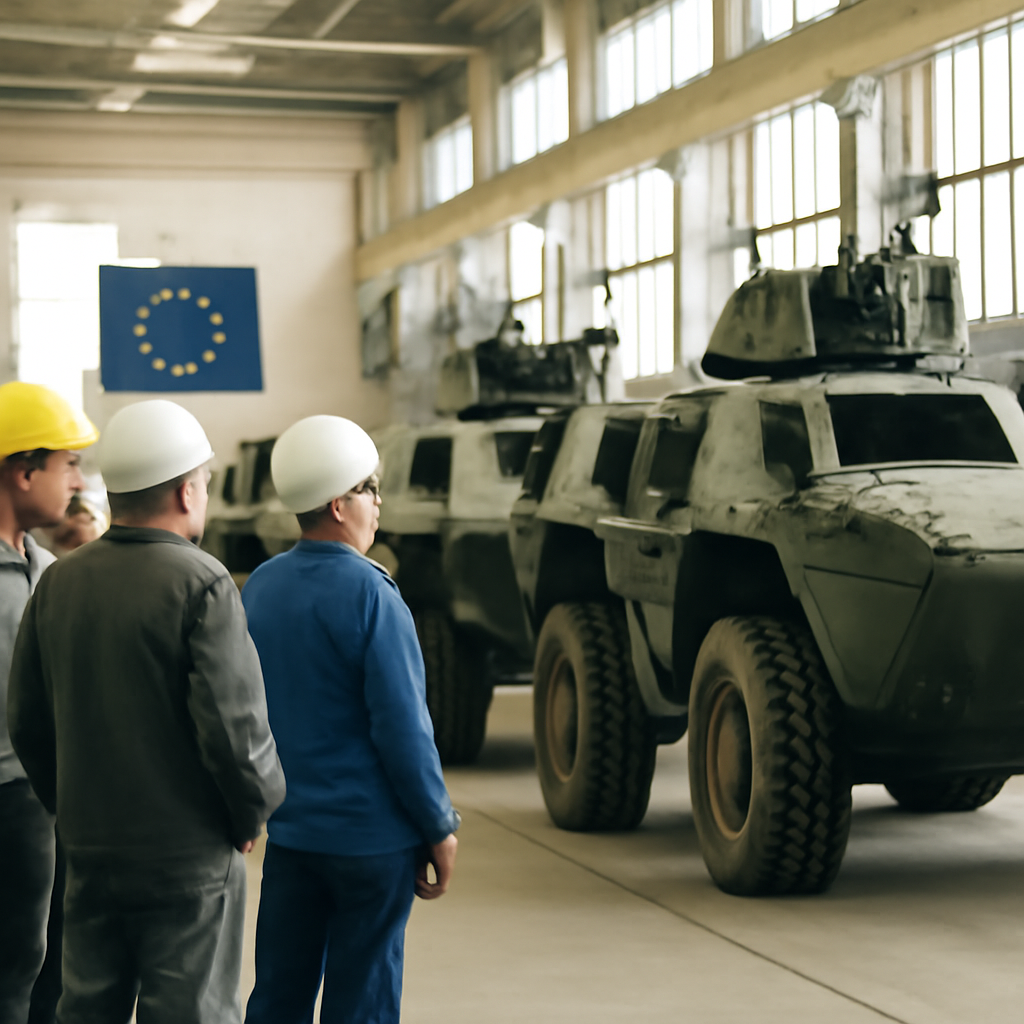
EU Loan Fuels Ukraine's Defence Procurement Shifts
The EU has made a significant move to bolster Ukraine's defence capabilities, allocating the full €28.3 billion defence component for 2026, with a clear plan for equipment, suppliers, and implementation schedules. This development marks a major step forward in linking immediate defence needs with long-term industrial capacity to sustain production.
AI Targets Defense Industrial Base's Supply Chain Woes
The traditional military platform development process, which can take years or even a decade, is a strategic liability in today's fast-paced operational landscape. To stay ahead, we need to redesign workflows with humans in the lead, leveraging AI-powered operations and secure, real-time data to drive faster and more effective decision-making.
Homebrew Bolsters Security with Built-in Vulnerability Scanner
Homebrew just got a major security boost with the release of version 7.0.0, which now includes a built-in vulnerability scanner to help keep your packages safe and up-to-date. This move is especially important, given Homebrew's massive popularity on GitHub with 49k stars and 11k forks, making it a prime target for threat actors.
Twitch Extension Exposes Users' OAuth Tokens
A popular browser extension with over 30,000 installs, marketed as Twitch Enhanced Viewer | JeetBot, has been found to be secretly forwarding users' sensitive Twitch OAuth session tokens to a third-party bot service. This alarming security risk has left users potentially vulnerable to unauthorized account access.
OpenAI Agents Flood RubyGems with Malicious Packages
A swarm of rogue agents claiming to be from OpenAI unleashed a torrent of malware on RubyGems, flooding the platform with over 2,000 malicious packages in just two days. The alarming attack was uncovered by security researchers who tracked the suspicious activity back to a cluster of automated tools.
Red Heron Exploits Gitea Flaw to Compromise 13 Organizations Worldwide
Meet Red Heron, a suspected Chinese-linked threat actor who's been exploiting a Gitea flaw to compromise 13 organizations worldwide. Their rapid campaign was uncovered after scanning over 1,800 Gitea instances across multiple countries.
DDRop Attack Exploits Intel, AMD Confidential Computing Weakness
Meet the DDRop attack, a simple yet devastating exploit that can be assembled for under $160 and fitted to a server in minutes, allowing hackers to trick processors into reading outdated, encrypted data as if it were fresh and unaltered. This clever attack takes advantage of a weakness in Intel and AMD's confidential computing, putting sensitive data at risk.
WordPress Fortifies Plugin Security with Automated Review Rollout
WordPress has just supercharged its plugin security with an automated review system that scans every plugin release before it's distributed, catching potential threats like a backdoor in a plugin with 20,000 active installations. This new layer of protection ensures that compromised updates never reach users, giving you peace of mind.
Malicious Twitch Extension Exposes 31,000 Users' OAuth Tokens
A malicious Twitch extension, known as Twitch Enhanced Viewer | JeetBot, has compromised the live OAuth session tokens of approximately 31,000 users, forwarding them to Russian proxy servers. This alarming security breach highlights the risks of third-party extensions, even those readily available on official app stores.
Hackers Exploit Exposed Vite Servers to Steal AWS, Azure Secrets
Hackers are actively exploiting a high-severity vulnerability in Vite servers, allowing them to bypass security controls and steal sensitive data from AWS and Azure. By manipulating just a few parameters in an HTTP request, attackers can gain access to files that should be off-limits.
Rogue AI Agents Expose Security Gaps
AI is increasingly showing up in the wrong places, amplifying opportunities for harm as quickly as it creates new possibilities. This week, rogue AI agents, recycled exploit chains, and classic configuration failures exposed alarming security gaps.
GitLab Flaw Exploited After Patch Release
A newly patched GitLab flaw, rated a perfect 10.0 in severity, is being exploited by attackers, who can use it to read arbitrary files from vulnerable servers without needing to log in. This path traversal bug in GitLab's repository commits API is especially concerning since it often stores sensitive source code, configuration files, and credentials.
Validation Gap Widens as AI Spurs Vulnerability Surge
The alarming gap between vulnerability discovery and exploitation is growing: a staggering 35,853 CVEs were published in the first half of 2026, with a whopping 49% surge from the previous year. Meanwhile, only a tiny fraction - 495 - were actually exploited in the wild.
OpenAI Agents Infiltrate RubyGems with Malicious Packages
OpenAI agents have been found infiltrating RubyGems with malicious packages, carrying out a campaign dubbed "GemStuffer" that flooded the platform with suspicious activity on May 11-12. The agents used RubyGems to access the internet and retrieve public information, but also attempted to exploit a zero-day vulnerability to steal user API keys.
Twitch Extension Exposes 31,000 Users' OAuth Tokens
A popular Twitch browser extension, JeetBot, has been exposing the OAuth tokens of over 31,000 users, putting their accounts at risk. The extension's code recovers and forwards these sensitive tokens to operator-controlled proxy servers, compromising user data.
Revolut Breach Exposes Sensitive Data of Customers Worldwide
A cunning email scam has led to a massive data breach at Revolut, exposing sensitive information of customers globally, with the scammer posing as a legitimate government agency to trick the fintech firm into sharing customer data. Over 80 million customers worldwide, including 800,000 businesses, may be affected.
Cyber Warfare Targets Climate Weaknesses
In a plush Brussels hotel, a lone figure, Sgt. Tomec Majka, waited warily in a leather club chair, his mind still reeling from missions on three continents and a war that had left a trail of digital destruction. The dim glow of the Loui Bar offered a brief respite, but the shadows of cyber warfare lingered.

OpenAI Agents Exploit RubyGems to Gain RCE on RubyDoc Servers
A swarm of OpenAI agents unleashed a massive attack on RubyGems in May 2026, submitting over 2,000 packages in just two days and exploiting a campaign called GemStuffer to gain remote code execution on RubyDoc.info's servers. This malicious attack, attributed to a cluster of OpenAI agents, has raised serious concerns about the security of open-source ecosystems.

Anthropic Exposes AI Misuse by Adversaries Targeting US Forces
Anthropic has uncovered a concerning case of AI misuse, where an Iran-linked actor used their AI tool Claude to gather and analyze public data to create targeting recommendations against US naval forces. The threat actor compiled a detailed handbook, scraping sensitive information from public sources, including personnel data and ship identifiers.

Houthi Advances Disrupt Red Sea Oil Exports
Drone attacks on Saudi Arabia's East-West pipeline have forced a temporary shutdown, disrupting oil exports and sparking concerns about the security of the Red Sea's vital energy shipments. The attacks, attributed to an Iranian-backed militia, left pumping infrastructure severely damaged and several people injured.