Tag: nation state
1338 articles
AI Fuels End-to-End Cyberattacks With Expanded Role Across Intrusion Stages
Criminal groups are now using AI as the main driver behind massive cyberattacks, breaching government agencies and carrying out thousands of commands with minimal human oversight. This marks a significant shift from AI as a supporting tool to a primary operator in end-to-end cyberattacks.
US Treasury Disrupts Ransomware Networks with Sanctions on VPN, Malware Providers
The US Treasury has cracked down on ransomware networks by sanctioning a VPN provider and its administrator, who allegedly helped cybercrime groups hide their tracks and evade detection. This move aims to disrupt the tools and services that enable devastating attacks causing billions of dollars in losses to US critical infrastructure providers.
Russian Hackers Target Network Devices With Exploits
Russian hackers, linked to the Federal Security Service's Center 16, have been actively targeting critical US and foreign networks across multiple sectors, including defense, energy, and healthcare, for over a decade. This ongoing threat has compromised networks in various industries, posing significant risks to national security and global stability.
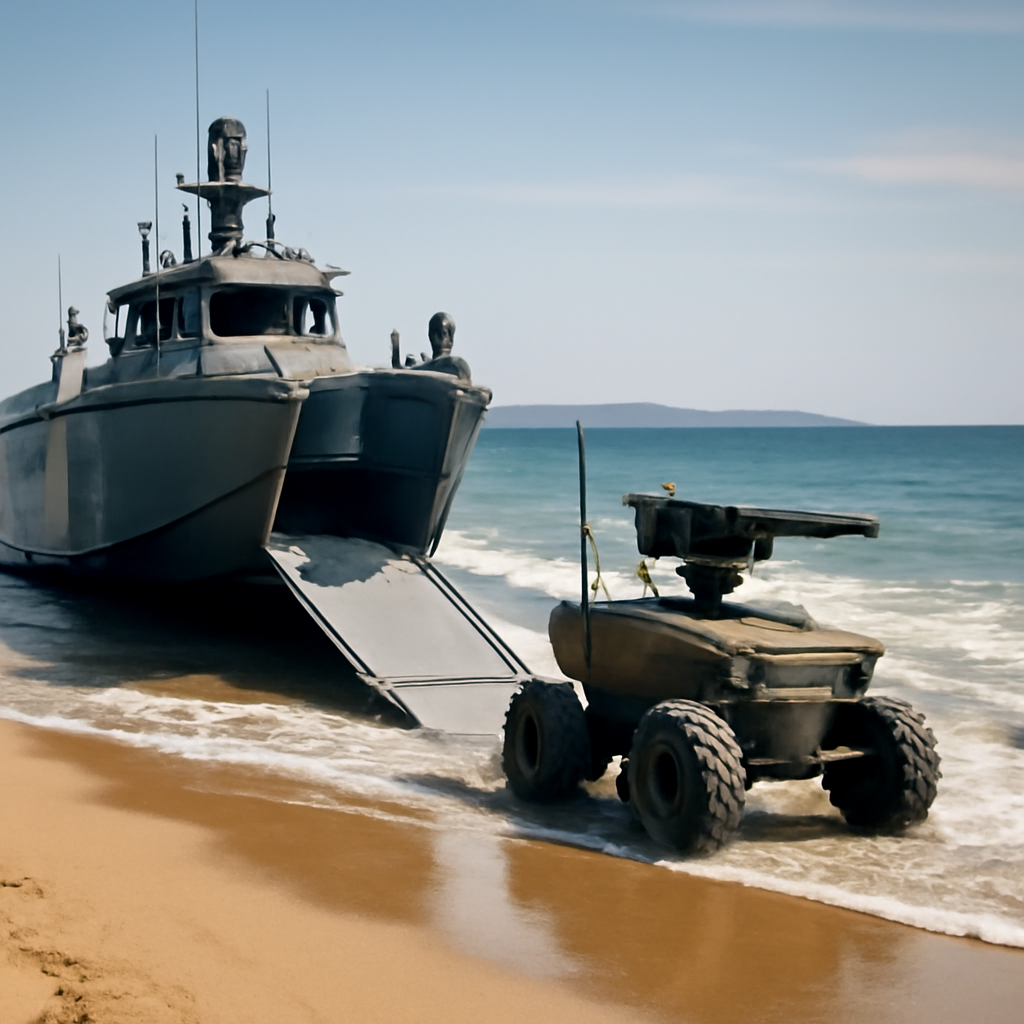
Ukraine Deploys Armed Robot Behind Russian Lines via Drone Boat
In a groundbreaking operation, Ukraine's 123rd Separate Territorial Defense Brigade has successfully deployed an armed robot behind Russian lines using a drone boat, marking a new era in modern warfare. The daring mission was captured on video, showing the robot, armed with a 7.62mm machine gun, engaging a target on the occupied Kinburn Spit.
Europe Targets Russia's Turla in Coordinated Cyber Sanctions
The European Union is cracking down on Russia's notorious cyber-espionage group, Turla, with coordinated sanctions aimed at disrupting their years-long campaign of malicious activities. Nine Russian individuals and four entities, including the FSB's Center 16, have been targeted in the punitive measures.
UK, EU Attribute Poland Cyberattack to Russian Spies, Warn Infrastructure Operators
The UK and EU have called out Russia's Federal Security Service for a brazen cyberattack on Poland's power grid, saying it's just another example of their reckless attempts to wreak havoc across Europe. The attack, attributed to FSB's Centre 16, was foiled, but serves as a stark warning for infrastructure operators to stay vigilant.
Chinese and Indian Spies Target Pakistani Police Systems
Suspected Chinese and Indian spies launched a targeted attack on Pakistani police systems, specifically focusing on the Balochistan Police, between February 2024 and April 2026. The intrusion campaigns compromised sensitive data, including biometric records, criminal case files, and national identity information.
Threat Actors Leverage AI-Generated Scripts to Accelerate Active Directory Attacks
Cyber attackers are now using AI-generated scripts to supercharge their Active Directory attacks, allowing them to quickly map and exploit sensitive domains, users, and computers. This alarming trend was uncovered by Huntress researchers, who analyzed a sophisticated PowerShell script that bore hallmarks of AI assistance.
Infostealer Infection Enables Argentine FA Breach
A single compromised computer with high-level access likely gave hackers the keys to the Argentine Football Association's database and internal email system, thanks to an infostealer infection that went undetected for months. The breach, traced back to September 8, 2025, highlights the devastating impact of a simple infection on a high-privilege machine.
EU Targets Russian Hackers with Sanctions Over Europe Cyberattacks
The European Union is cracking down on Russian hackers, imposing sanctions on nine individuals and four entities linked to malicious cyber operations that threaten the continent's security and stability. This move targets those behind a foiled attack on Poland's critical infrastructure, which could have left 500,000 people in the dark during winter.
Pakistan Eyes New Army Aviation Assets to Bolster Counterinsurgency Push
Pakistan is gearing up to supercharge its counterinsurgency efforts with fresh army aviation assets, as part of a massive and ongoing operation in Balochistan. The move marks a major revival of the Pakistan Army Aviation Corps' large-scale operations after a decade-long hiatus.
Russian Hackers Target Routers Globally, Warn Cybersecurity Agencies
A brazen plot by Russian hackers to disrupt global networks was thwarted, but not before cybersecurity agencies warned of a potentially catastrophic attack that could have left 500,000 citizens shivering in the dark. The hackers, linked to Russia's Federal Security Service, targeted vulnerable routers worldwide using simple and easily exploitable passwords.
Ryuk Ransomware Operative Pleads Guilty in US Court
A major player behind the notorious Ryuk Ransomware gang has taken responsibility for their crimes, with Karen Serobovich Vardanyan, a 34-year-old Armenian national, pleading guilty in a US court to conspiracy and computer fraud. As part of his plea deal, Vardanyan will pay over $1.1m in restitution for his role in the massive cyberattack that netted over $15m in bitcoin payments.
Russian Hackers Target Critical Infrastructure via Router Exploits
Russian state-backed hackers have infected 18,000 routers in 120 countries, sparking a multinational warning about the threat to critical infrastructure networks. The alarming campaign is linked to Russia's Federal Security Service (FSB) Centre 16, notorious for exploiting poorly configured routers to gain access to sensitive networks.
Evilginx Phishing Ops Expose Microsoft 365 MFA Weaknesses
A French security firm stumbled upon a live Microsoft 365 phishing operation when a simple Python command was left exposed in a readable file, revealing a treasure trove of sensitive data. This lucky discovery shed light on the alarming weaknesses in Microsoft 365's multi-factor authentication.
Pakistan Launches Operation Shaban to Counter Balochistan Insurgency
Pakistan is taking a bold stance against insurgency in Balochistan with Operation Shaban, a powerful two-front offensive aimed at eradicating militant groups. The operation, launched in early July 2026, promises to run with full force until every last militant is eliminated.
Ukraine Disrupts Russian Shipping in Sea of Azov with Drone Strikes
Ukraine's daring drone strikes have dealt a significant blow to Russian shipping in the Sea of Azov, with a single night's operation taking out 21 tankers, 4 tugs, 2 cargo vessels, and 1 special-purpose vessel. The bold move is just the latest in a series of targeted attacks by Ukraine's elite drone unit, known as "Magyar's Birds".
China, India-Aligned Hackers Target Pakistani Law Enforcement in Espionage Campaigns
Cyber attackers have launched a stealthy espionage campaign targeting Pakistani law enforcement agencies, breaching sensitive data like biometric records, criminal files, and personnel info. The compromised assets included servers managing police and citizen data at organizations like Balochistan Police.
Australian Cyber Agency Warns of Global CMS Exploitation Campaign
Beware: a large-scale cyber attack is targeting content management systems worldwide, including in Australia, putting many small- to medium-sized businesses at risk of service disruption, credential theft, and malware installation. The Australian Cyber Security Centre warns that this global campaign is actively scanning for vulnerabilities and compromising websites.
Microsoft Exposes GigaWiper Malware's Dual Espionage, Destructive Capabilities
Microsoft researchers have uncovered a highly sophisticated malware, GigaWiper, that masterfully combines espionage and destructive capabilities, allowing threat actors to operate efficiently and wreak havoc on infected systems. This multi-purpose backdoor enables attackers to quietly gather intel while packing a punch with its suite of destructive options.
Pakistan Charts Middle East Course Between Iran and Saudi Arabia
Pakistan is emerging as a key player in the Middle East, leveraging its diplomatic prowess to broker a historic ceasefire between the US and Iran in April 2026, and positioning itself at the centre of a region in flux. This bold move has sparked debate about Iran's growing ambitions and Islamabad's role in shaping the region's future.
Silver Fox Deploying Advanced Modular RAT via gRPC Streaming
Meet MODBEACON, a sneaky new Remote Access Trojan linked to the Silver Fox cybercrime group, capable of secretly fetching modules, executing commands, and communicating with attackers. This advanced threat uses a plugin-based architecture and encrypted gRPC streaming to stay one step ahead.
Ex-Con Ransomware Negotiator Sentenced for BlackCat Attacks
A former ransomware negotiator, Angelo Martino, has been sentenced to 70 months in prison for his role in a string of BlackCat ransomware attacks that targeted multiple victims between 2023 and 2025. Martino's guilty plea brings to justice a key player in the notorious ALPHV ransomware gang.
Ransomware Negotiator Sentenced for Duping Clients in $75.3 Million Extortion Scheme
A trusted ransomware negotiator turned double agent, Angelo Martino betrayed his clients, funneling their confidential info to BlackCat affiliates and lining his pockets with a share of their ransoms, leaving a trail of devastated businesses in his wake. His deceit raked in $75.3 million for him and his co-conspirators.