Tag: nation state
1338 articles
OpenMandriva Linux Project Hit by Sabotage Attempt
Davide Beatrici, a leading developer of the Mumble app, has denied allegations of sabotage against the OpenMandriva Linux Project, claiming his actions were deliberate but not malicious. He admitted to deleting key repositories and pushing a package, but insists his moves were targeted, not hurtful.
ASELSAN Builds Sovereign Military 5G Core with GÖKBAĞI Satellite Network
ASELSAN is revolutionizing military communications with GÖKBAĞI, a game-changing system that combines a low-Earth orbit satellite network with a dedicated military 5G core for secure, high-capacity, and resilient connectivity. This cutting-edge architecture enables uninterrupted communication on the move, even in electronic warfare conditions.
Microsoft Exposes GigaWiper Backdoor's Triple Threat
Microsoft has uncovered a highly destructive backdoor, dubbed GigaWiper, which poses a triple threat to Windows systems, allowing attackers to silently spy and destroy machines in three different ways. This multi-purpose threat doesn't just crash systems - it gives attackers the power to choose how and when to render a machine irrecoverable.
AI-Generated Malware Targets Active Directory Environments
Criminals are now leveraging AI to create malicious software, as seen in a recent case where an attacker used an AI-assisted PowerShell script to infiltrate an Active Directory environment. This emerging threat, dubbed "vibe coding," allows attackers to generate software by simply prompting a large language model in plain language.
China's Military AI Logistics Expose New Vulnerabilities in War
China's military is betting big on artificial intelligence to supercharge its logistics, but this bold move may backfire in the chaos of war, creating vulnerable chokepoints that could leave its operations crippled. Mike Tyson's famous words - "everybody has a plan until they get punched in the face" - are particularly apt for Beijing's high-stakes gamble.
Red Teamer Exploits Trust to Steal Priceless Trophy
Imagine walking onto a secure campus with equipment in plain sight and a convincing story, and having employees roll out the red carpet - literally. A professional red teamer and his colleagues did just that, effortlessly gaining access to a Fortune 500 company's high-security site by exploiting one simple vulnerability: trust.
Chinese Spies Exploit Roundcube Flaw to Breach University Servers
A recent series of university server breaches, attributed to a group called UNK_MassTraction, has exposed vulnerabilities in North American higher-education institutions, with potentially dozens more affected. The breach, linked to a flaw in Roundcube, is believed to be an ongoing campaign.
Paris Peace Forum Launches Global Hub to Track AI Cyber Threats
The Paris Peace Forum is tackling the growing threat of AI-driven cyber attacks by launching INTAiC, a groundbreaking global hub that unites experts from two previously separate spheres: network defense and AI security. By bridging this gap, INTAiC aims to provide a unified front against the evolving risks to global internet infrastructure.
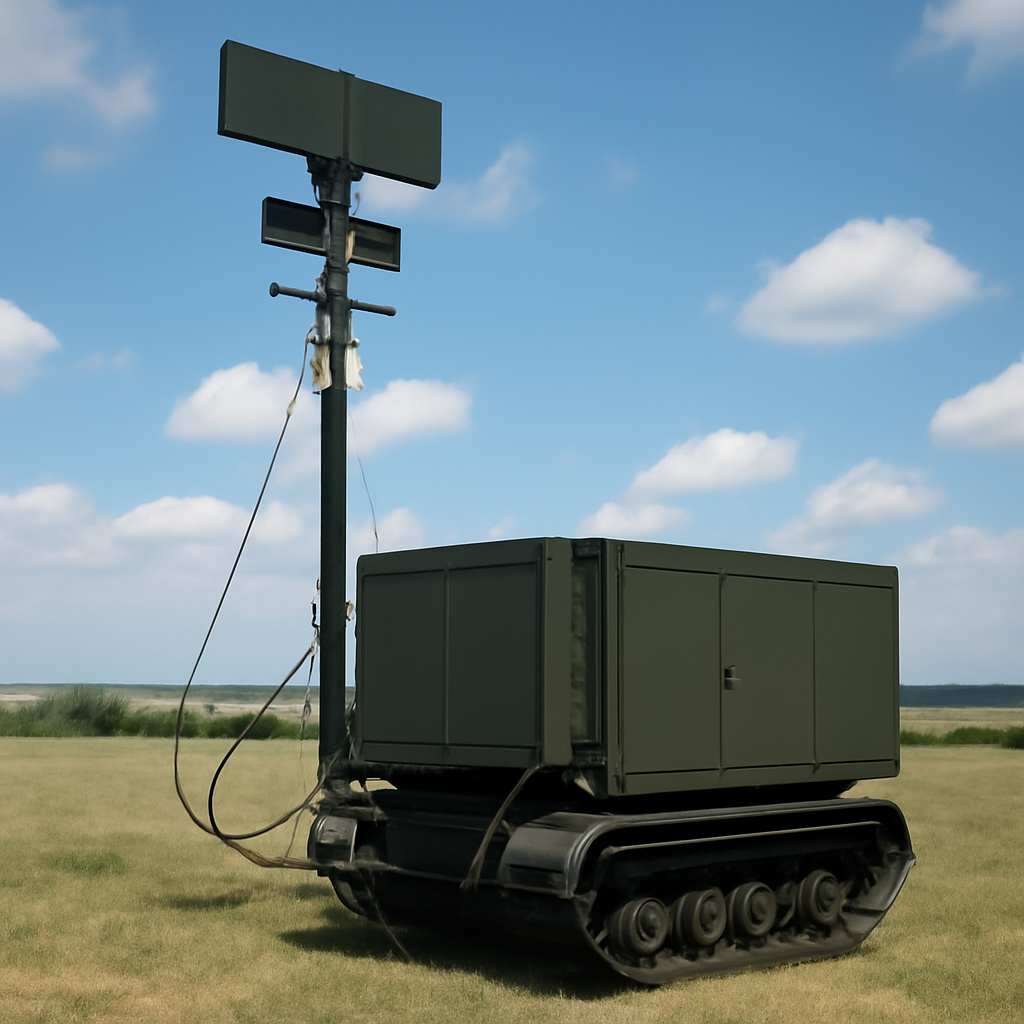
Ukraine's Lima Exposes Russia's Vulnerability to Cyber-Electronic Warfare
Meet Lima, a game-changing electronic warfare system that's helping Ukraine defend against Russia's aerial attacks - with an impressive track record of diverting over 60 high-tech Kinzhal missiles away from protected sites. Developed by Cascade Systems, Lima has proven to be a powerful countermeasure, with more than 400 units deployed to date.
Hackers Exploit Roundcube Flaw to Target Academic Researchers
A new wave of cyber attacks linked to China is targeting academic researchers in the US and Canada, specifically those in physics, engineering, and national security-related fields, by exploiting a vulnerability in Roundcube webmail servers. The campaign, tracked as 'UNK_MassTraction', has been ongoing since May and has already hit several universities.
Phishing Campaign Targets Microsoft 365 Users with Voice-Based Entra Passkey Scam
Beware of scammers impersonating Microsoft 365, tricking users into enrolling a fake Entra passkey by mimicking the real enrollment portal and leveraging voice calls to urge action. This sneaky phishing campaign has been targeting multiple sectors since April, putting unsuspecting users at risk.
China-Linked APT Bolsters Proxy Network with Custom Malware Arsenal
Meet UAT-7810, a China-linked advanced persistent threat that's rapidly expanding its proxy network with custom malware, allowing other attackers to hide their tracks and route traffic through compromised devices. This sophisticated operation, known as LapDogs, has been providing infrastructure for malicious activities for years.
China Warns of Claude Code Backdoor Risks, Urges Developers to Uninstall
China's National Vulnerability Database has issued a high-priority alert, warning developers to immediately uninstall certain versions of Claude Code due to a potential backdoor risk that could compromise sensitive data. Upgrade to the latest secure version to safeguard your information.
China-Linked APT Expands ORB Network with LONGLEASH Malware
Meet UAT-7810, a Chinese threat actor with a mission to build and expand Operational Relay Box (ORB) networks, which can be hijacked by other malicious groups to launch targeted attacks on high-value targets. Their latest move involves deploying the LONGLEASH malware to supercharge their ORB network.
UK Unveils AI-Powered Cyber Shield to Bolster National Defense
The UK's National Cyber Security Centre warns that attackers are using AI to supercharge their cyber offensives, speeding up vulnerability discovery and reconnaissance to alarming levels. In response, the UK has unveiled an AI-powered Cyber Shield to bolster its national defense and stay ahead of the threats.
Spain Seizes Suspect Tied to Russian Hacktivist Group
In a major cybercrime crackdown, Spanish authorities have arrested a suspect linked to a notorious pro-Russian hacktivist group, following a nearly year-long investigation sparked by a tip from the FBI. This breakthrough is a testament to global law enforcement collaboration, with the FBI vowing to continue disrupting cybercriminals worldwide.
Microsoft Telemetry Fingers Scattered Spider Suspect in US Crackdown
Microsoft's sharp-eyed telemetry has helped track down a suspect linked to the notorious Scattered Spider group, a prolific gang that allegedly raked in over $100 million in ransom payments by infiltrating more than 100 US company networks.
China-Aligned Hackers Exploit Roundcube Servers at US, Canada Universities
China-aligned hackers are targeting universities in the US and Canada, exploiting vulnerable Roundcube webmail servers to gain access to sensitive physics and engineering departments with potential national security links. This latest campaign highlights the ongoing threat of email-based attacks and the need for robust server security.
Spain foils pro-Russian hacktivist's escape plan
Spain's National Police have thwarted a daring escape plan by a suspected pro-Russian hacktivist, exposing his secret communications with terrorist groups and freezing his cryptocurrency assets. The suspect, allegedly part of the notorious CyberArmy of Russia Reborn and Z-Pentest groups, was caught after a months-long investigation sparked by a tip from the FBI.
Watling Exposes Shifts in Global Power Rules
The global rules of power have changed, and recent strategic failures reveal a harsh truth: it's not technology that's the problem, but flawed decision-making. From intelligence missteps to misguided priorities, the consequences can be catastrophic, as seen in the US's unprepared response to Iran's retaliation.
US Army Websites Targeted in 404 Hijacking Campaign
The US Army has confirmed that two of its websites, oil.army.mil and ai2c.army.mil, were recently hijacked in a 404 error page defacement campaign, displaying politically charged messages that denigrated high-profile figures and promoted a separatist cause. The incident was discovered by independent researcher Ronald Lovelace and reported to US Army officials.
Xi Jinping Reshapes China's Military Leadership Amid Purge Fallout
In a significant move, China's military leadership has been reshaped with the promotion of two lieutenant generals to full general, amid a backdrop of sweeping purges that have rocked the People's Liberation Army. On July 3, Zhang Shuguang and Wang Gang were elevated to their new roles, marking a major shift in the PLA's top ranks.
China-Aligned Hackers Exploit Roundcube Flaws to Infiltrate Universities
China-aligned hackers have launched a sneaky attack on universities, exploiting two flaws in the popular Roundcube webmail client to steal credentials and gain persistent access. At least a few dozen universities are believed to be affected, with Proofpoint researchers confirming fewer than 10 intrusions so far.
FBI Traces Scattered Spider Hacker via Persistent Windows Device ID
In a brazen ransom email, the attackers boldly declared, "IMPORTANT: WE STOLE THE DATA, CONTACT UMMEDIATELY," leaving no doubt about their malicious intentions. The hackers infiltrated the retailer's network through a clever help-desk ploy, tricking staff into resetting passwords and gaining control of critical accounts.