Tag: legacy systems
84 articles
US Army Grapples with Integrating Anduril's NGC2 Tech into Legacy Comms
The US Army's first attempt to integrate Anduril's Next Generation Command and Control tools into its legacy communications system was a learning experience, with Brig. Gen. Shane Taylor describing it as "not seamless" after a test during Lightning Surge 5 in Hawaii. The trial, which used Anduril's Lattice platform with the 25th Infantry Division, marked a key step in the Army's effort to modernize its command-and-control architecture.
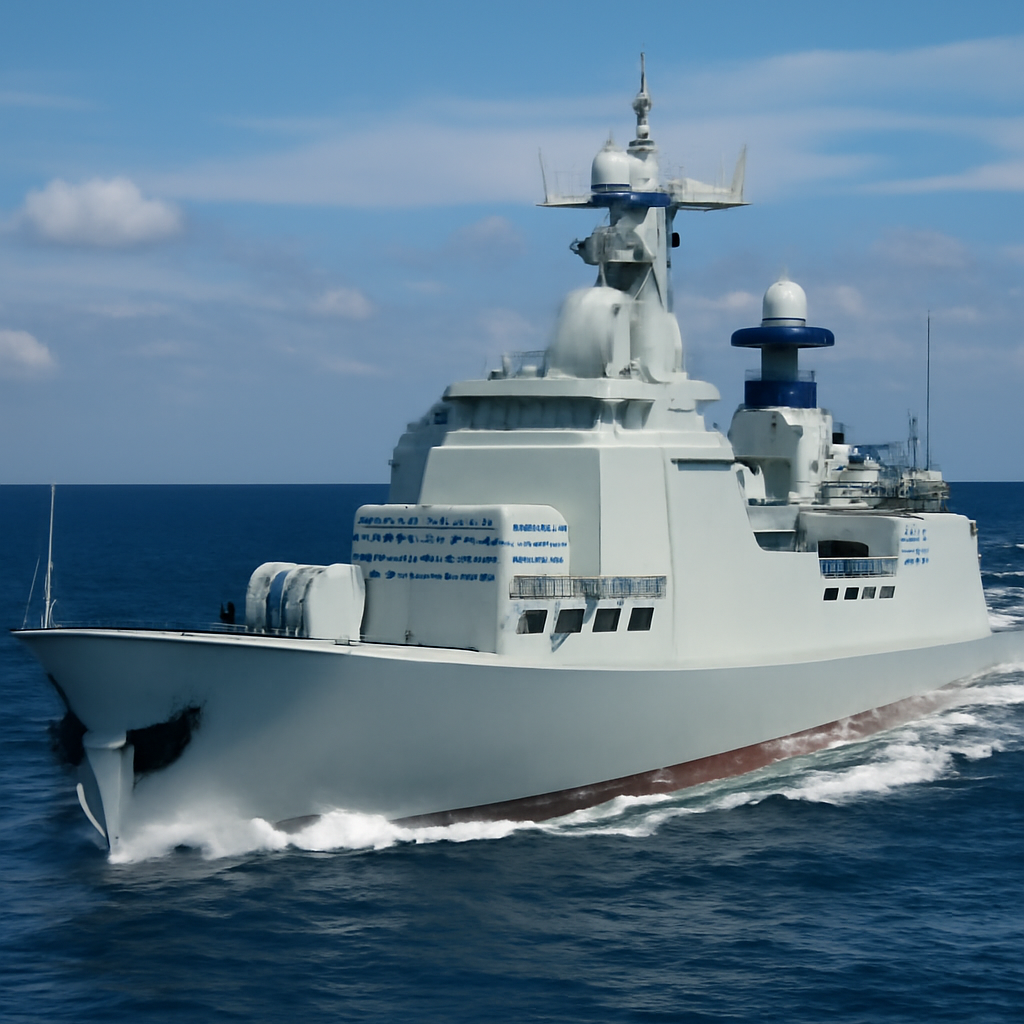
China's PLAN Upgrades, Decommissions Legacy Submarines
China is breathing new life into its naval fleet, and a recent photo of the Type 051C destroyer Shenyang at sea reveals some exciting upgrades that are leaving its legacy submarines in the dust. The Shenyang's makeover ditches its outdated S-300 system for four sleek HQ-10 short-range air-defense launchers.
Federal AI Initiatives Hinge on Universal Connectivity
As federal AI initiatives continue to multiply, a pressing challenge emerges: connecting the vast amounts of data scattered across legacy systems, cloud platforms, and SaaS applications to fuel more accurate and cost-effective AI decision-making. Universal connectivity is the linchpin that can unlock the true potential of AI in the federal space.
Bromcom Breach Exposes Email Addresses in Legacy Sign-on System
Bromcom's legacy single sign-on system has been breached, exposing email addresses and limited information of affected users. The incident, tied to a superseded registration functionality, has prompted the UK school software provider to withdraw the vulnerable component.
Bromcom Breach Exposes Email Addresses in Legacy Sign-on Flaw
A major security flaw in Bromcom's legacy single sign-on system has led to a significant data breach, exposing email addresses of users across the UK's education sector. The incident, identified on September 6, affected a legacy registration mechanism still in use despite being superseded.
NASA Revives Blackbird Legacy for High-Speed Flight Tests
Imagine being able to launch a 5-tonne vehicle at an incredible Mach 3 - a feat only achieved by the legendary Blackbird, and one that's got NASA eager to revive its high-speed legacy. This half-century-old capability is still turning heads, and for good reason.
NSA's Legacy Uncovered in Cray Supercomputer Design
The NSA's legacy lives on in the design of Cray supercomputers, with innovations from the older Harvest system influencing the development of the lightning-fast Cray-1. Although Harvest itself didn't dominate the scene, its ideas persisted as secret perks built into Cray hardware for years to come.
Microsoft Phases Out WMIC Tool Amid Cybercrime Exploits
Microsoft has pulled the plug on the Windows Management Instrumentation Command-line (WMIC) tool, removing it from Windows 11 versions 24H2 and 25H2, and phasing it out from future updates. This move marks the end of an era for a utility that's been a favorite among cybercriminals.
Wyden Urges Feds to Phase Out Insecure Public-Facing VPNs
Senator Ron Wyden is calling on federal agencies to ditch outdated, vulnerable VPNs and upgrade to modern, secure remote-access technology to protect against devastating cyberattacks. In a letter to top officials, he urged a coordinated effort to safeguard government employees' remote access and prevent further breaches.
Abbott Labs Probes Two Cyber Incidents Amid Extortion Claims
Abbott Laboratories is investigating a cyber incident that involved unauthorized access to a limited number of internal systems within its Cancer Diagnostics business, and has activated incident response procedures to address the issue. The company confirms that its operations remain unaffected and that the affected systems are separate from its other businesses and systems.
DHS Breach Exposes Flaws in Cyber Detection Process
A recent cyber incident at the Department of Homeland Security went undetected for weeks, despite raising red flags in not one, but two separate assessments that were initially dismissed as harmless. The breach, which occurred on the Homeland Security Information Network (HSIN), highlights alarming flaws in the cyber detection process.
Microsoft to Phase Out OWA Light in Exchange Server Update
Microsoft is bidding farewell to OWA Light, shifting its focus to the full Outlook on the web experience, which promises a more seamless and modern way to access your inbox. By August 2026, the tech giant will retire OWA Light, streamlining its engineering efforts and enhancing the overall user experience.
Historic Unix OS KSOS Exposed in Public Archives
Get ready to explore a piece of computing history: the source code for KSOS, a highly secure Unix operating system backed by the US Department of Defense, is now freely available in the archives of The Unix Heritage Society. This remarkable release offers a glimpse into the development of secure operating systems in the 1970s and 80s.
DHS Probes Breach of Homeland Security Information Network
The Department of Homeland Security is investigating a recent cyber breach targeting a legacy information sharing environment used by its Homeland Security Information Network. This platform is a critical tool for sharing sensitive information among partners to protect communities and respond to incidents.

US Army Deploys Jailbroken Systems to Middle East in Interoperability Push
The US Army has kicked off Operation Jailbreak, a 30-day sprint to revolutionize how its systems communicate, by deploying jailbroken systems to the Middle East. This bold move aims to break down software barriers, enabling seamless data sharing between legacy and new equipment.
Federal Agencies Face AI Infrastructure Hurdles
As federal agencies increasingly integrate AI into their facilities, they're facing a major hurdle: outdated legacy systems that require a fresh, open systems approach to support the technology. This critical upgrade is essential to unlock AI's full potential and drive vital service delivery improvements.
Microsoft to Discontinue Legacy TLS Versions in Exchange Online by July 2026
Microsoft is putting the brakes on outdated security protocols, announcing that it'll start blocking legacy TLS 1.0 and 1.1 connections to Exchange Online in July 2026 - so it's time to upgrade and stay secure! This move marks the end of an era for older clients that still rely on these outdated protocols.
Microsoft Offers Lifeline for Laggard Exchange, Skype Customers
Microsoft is throwing a lifeline to organizations still relying on outdated Exchange Server and Skype for Business Server, offering extended security updates for a fee to help bridge the gap to newer products. This move acknowledges that some businesses need more time to migrate, providing a temporary safety net for those lagging behind.

Aligning IT: Exclusive Best Practices for Federal Health
Facing the challenge of modernizing mission‑critical systems without disrupting care? This guide shares exclusive federal health IT best practices—from phased cloud stewardship to zero‑trust identity and automation—to help agencies secure, scale, and sustain 24/7 services.
UK government seeks Must-Have Affordable CTO
Could one Affordable CTO on a £100k salary really untangle a £23bn government tech estate without shaking public trust? David Knott’s exit forces ministers to choose: hire a modestly paid fixer to stabilise ageing, costly systems or invest more now to rebuild brittle, monopolised infrastructure.

Cyberattack Hits EU Airports: Exclusive Critical Alert
A ransomware infection has rippled through EU airports, knocking out check‑in kiosks and flight displays and forcing travelers into long queues while teams scramble to isolate systems—was this criminal extortion, a state‑level probe, or a preventable collapse of ageing IT and lax supplier controls? Our exclusive alert explains what happened, who noticed first, and how authorities are racing to restore operations.

Oracle E-Business Suite Risky: Must-Have Breach Guide
Google’s Threat Analysis Group says the Clop ransomware gang accessed a large volume of data from Oracle E-Business Suite — a wake-up call for any org that hasn’t checked who holds the keys to its crown jewels. Now’s the time to hunt for shadow EBS instances, tighten access, and patch or segment vulnerable systems before attackers turn stolen data into extortion.

AIOps for Government: Must-Have Best-Practice Guide
Government agencies can unlock new value from costly legacy systems by layering AIOps—AI-driven monitoring and predictive maintenance—that boosts resiliency, cuts downtime, and stretches IT dollars without risky rip-and-replace projects. Done right, AIOps becomes a secure, incremental bridge to modernization that protects services, reduces firefighting, and preserves public trust.
mission success: Must-Have Infrastructure for Best Defense
When mission needs outpace aging IT and cloud, cyber, and AI demands collide, infrastructure becomes the strategic foundation for federal success—enabling agility, security, and trustworthy AI. Cloud Exchange 2025 made clear: treating infrastructure as a mission enabler, not a cost center, is the only way agencies can modernize, defend assets, and deliver better services.