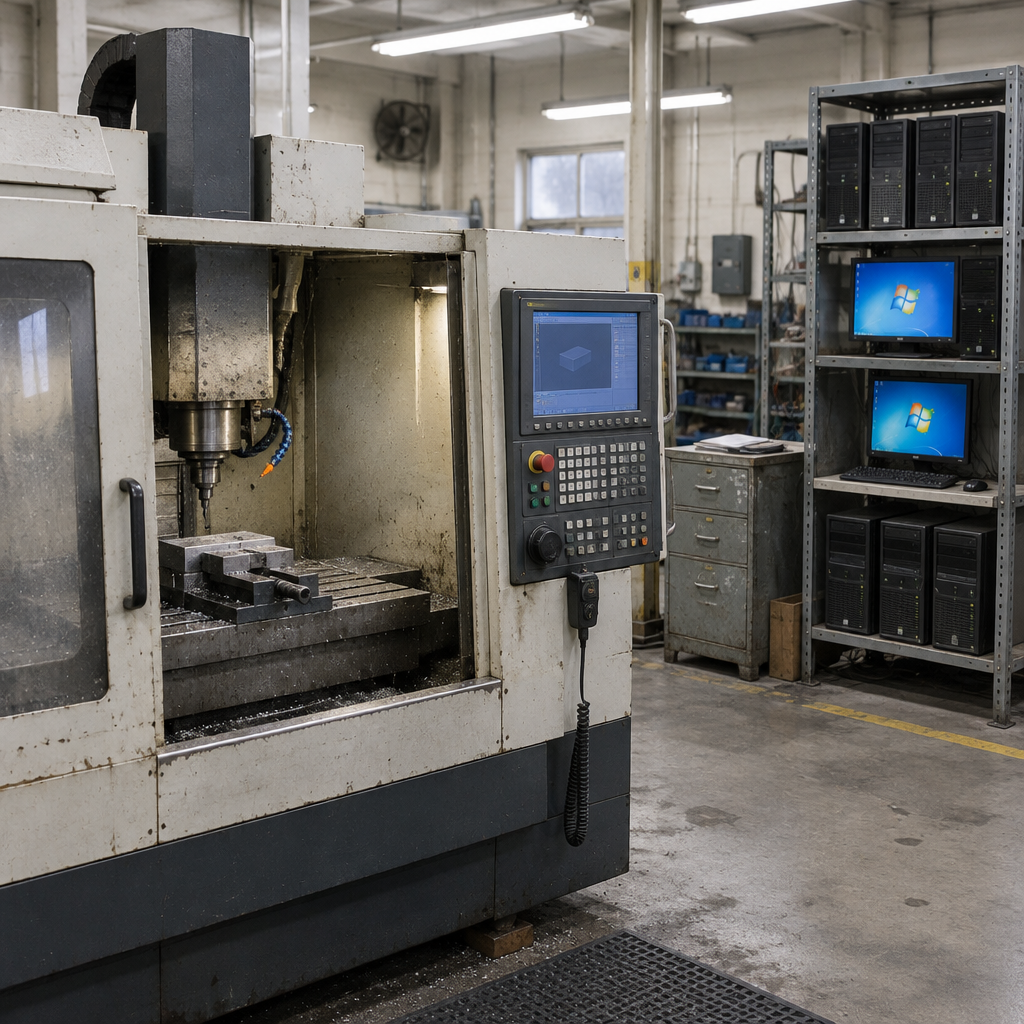
"So I've been looking through these and most of them had been disconnected from the domain, so it's the right move," said Dahvid Schloss, the leading red teamer and pen tester of Suzu Labs, describing why an initial scan of a factory network turned up few obvious entry points.
The factory visit and an auditer's brief
Schloss traveled to a factory at the client's request to verify that adjustments made after a breach six months earlier had closed the holes. He found multiple Windows 7 servers attached to CNC milling machines — legacy systems still in place “even though Windows 10 was by then Microsoft's supported desktop OS.” Most of those machines were not on the domain, which limited lateral attack options during the assessment.
EternalBlue, LSASS and the one vulnerable server
Because most servers were disconnected from the domain, Schloss initially passed on running EternalBlue. But one server hooked to milling equipment was connected to the network and on the domain, and it was vulnerable to EternalBlue. Schloss said he dumped LSASS (the Windows Local Security Authority Subsystem Service) from that device and found credentials harvested via WDigest. The dump included a pair of credentials, one of which "looked like an admin account."

This site is the portfolio.
OSINTSights runs on Cloudflare Workers, D1, R2, and Vectorize, with an AI pipeline on Hetzner ARM. Nubivance designed, built, and operates it. We do the same for clients.
See what we buildThe leet insult that turned out to be a domain admin password
On inspection the password string read “heyhackergof***yourself,” presented in leet speak (noted in the report as [l337 5p34k]). Schloss initially assumed the odd phrasing was a prank left to bait intruders and set the credential aside for a week. During a briefing he asked the IT team who had configured the account; staff looked toward the senior manager of IT and Schloss recalled the manager's expression: “oh shit, like what?” The team confirmed the password string was the actual administrator password.
When Schloss returned on Monday and tried the username and password combination, it gave him "complete control of the entire network." With domain admin rights he was then able to access other stored passwords on the network — many of which, the assessor found, were similarly insulting phrases aimed at potential hackers.
Patching and legacy OSes: the proximate cause
Schloss framed the technical lesson bluntly: it was the outdated machine that let him in, not the strange password. The report emphasizes that the vulnerable entry point was the legacy Windows 7 server attached to industrial equipment, not the strength of a single credential. As the write-up notes, “hackergof***yourself” in leet speak isn't a terrible password from an entropy perspective — it was merely embarrassing once exposed — but the real failure was allowing an insecure legacy OS to remain connected and unpatched on a domain.
What this means for technologists, affected enterprises, and procurement leaders
- Technologists and security teams: Pay attention to domain membership and device patching. Even well-chosen passwords can be undermined by an unpatched, legacy OS on the domain; tools that dump LSASS and exploit EternalBlue remain practical on unpatched Windows 7 systems.
- Affected enterprises and operations owners: Industrial control environments using proprietary or legacy software must weigh the operational risk of running unsupported OSes on domain-connected machines. Segmentation, patching plans for devices that cannot be upgraded, and separate authentication practices for machines attached to operational technology should be reviewed.
- Procurement leaders: When buying software or hardware that depends on legacy platforms, insist on supplier plans for secure support or compensated migration paths — a workaround of insulting credentials does not mitigate the network-level risk posed by unpatched systems.
The episode is plain in its arithmetic: a post-breach security theater — leaving insulting but strong-looking passwords in place to vent frustration — did not close the real vector. A single connected Windows 7 server vulnerable to EternalBlue and yielding LSASS dumps granted the assessor domain administrator rights and access to a trove of other credentials. The client's anger at a previous intruder produced memorable passwords; the unpatched, legacy machine produced a full takeover.
Read the original account at The Register: https://www.theregister.com/security/2026/10/29/admin-dropped-the-f-bomb-in-a-password-to-show-hackers-who-was-really-1337/