Tag: supply chain
1740 articles
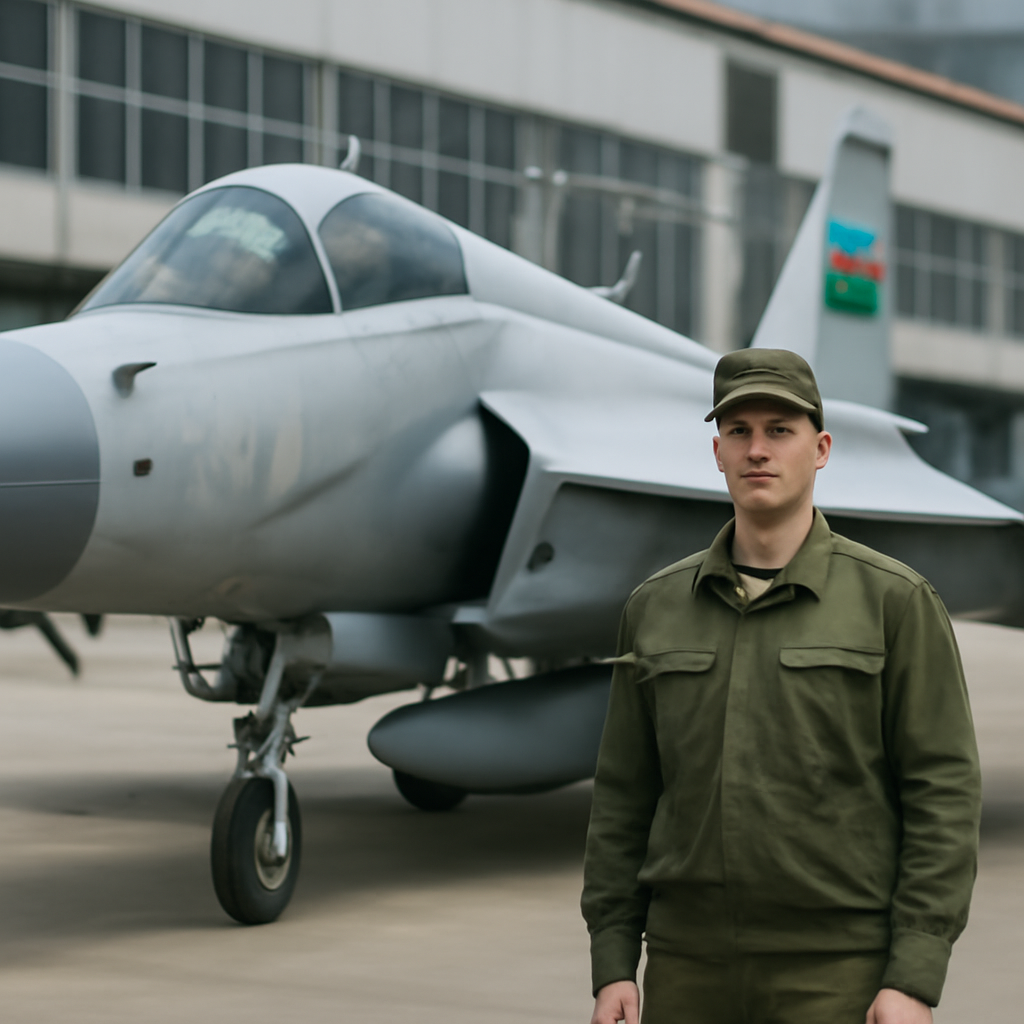
Azerbaijan Emerges as Plausible Customer for China's J-10CE Fighter
Azerbaijan's confirmed purchase of the JF-17 Block III fighter jet marks a significant turning point in its military procurement strategy, shifting away from its Soviet-era roots and potentially paving the way for future acquisitions from China. This move could be just the beginning of a long-term partnership between Azerbaijan and China's defense industry.
Frontline Education Breach Compromises Employee Data
Frontline Education recently discovered a vulnerability in a third-party software product that led to a data breach, compromising employee information. The company quickly sprang into action, investigating and remediating the issue with the help of a cybersecurity expert.
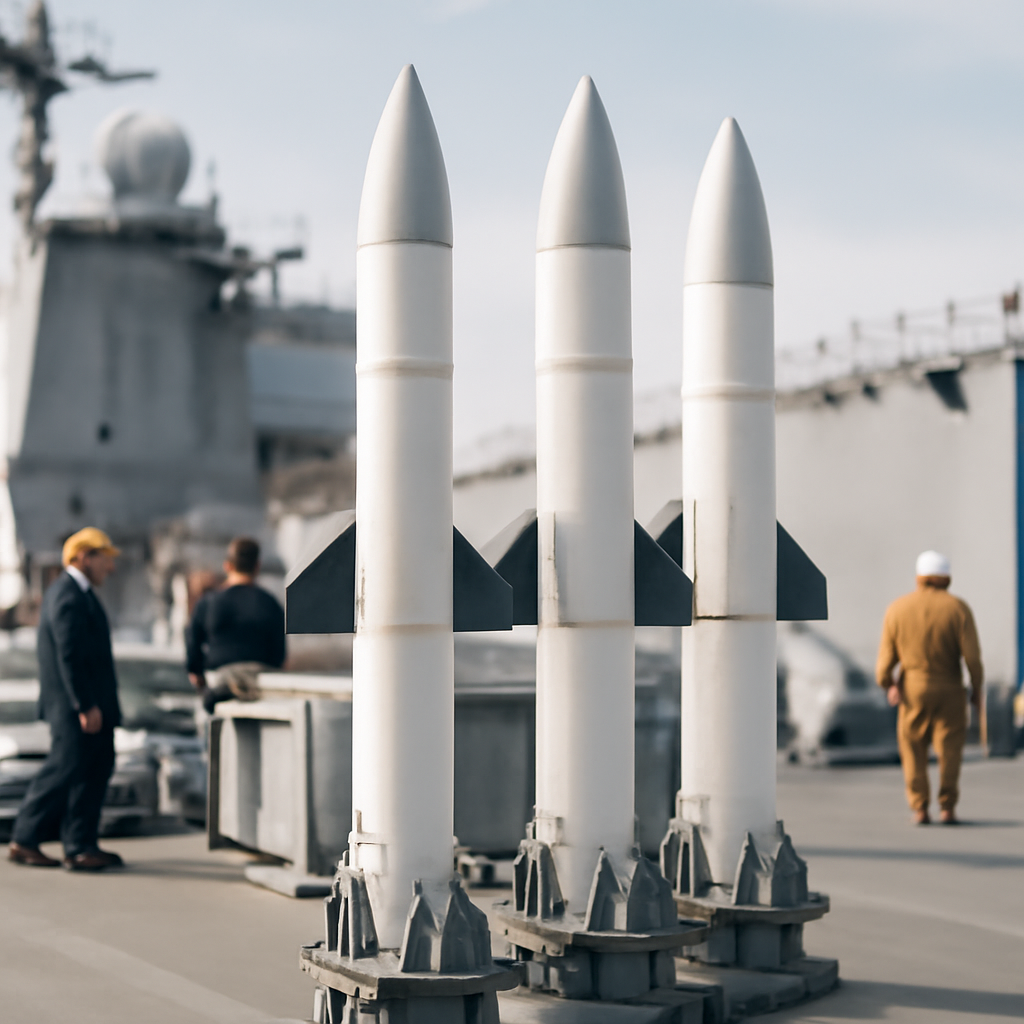
US Navy Seals $24.4B Deal with Raytheon to Accelerate SM-6 Production
The US Navy has sealed a massive $24.4 billion deal with Raytheon to supercharge production of the Standard Missile-6 (SM-6), a powerful Navy missile, with plans to deliver faster and more efficient manufacturing. This game-changing agreement is set to drive significant cost savings and boost production over the next five years, with two extra years of options.
China-linked hackers impersonate US officials to target AI experts
Phishing campaigns impersonating US officials are targeting top AI policy experts, making it tough for them to know if they're being scammed. Even prominent figures like Lynne Parker have had their names used to trick others, highlighting the challenge of stopping these attacks.
China-Nexus Espionage Campaign Exploits Outlook, OneDrive
A sneaky espionage campaign, tracked as UAT-11587, has been exploiting Microsoft Outlook and OneDrive to secretly control its targets, with a reach that spans 16 entities across eight Asian countries. The sophisticated attack, first detected in September 2025, has been targeting academic, think-tank, and civil-society organizations, with evidence of continued activity through May 2026.
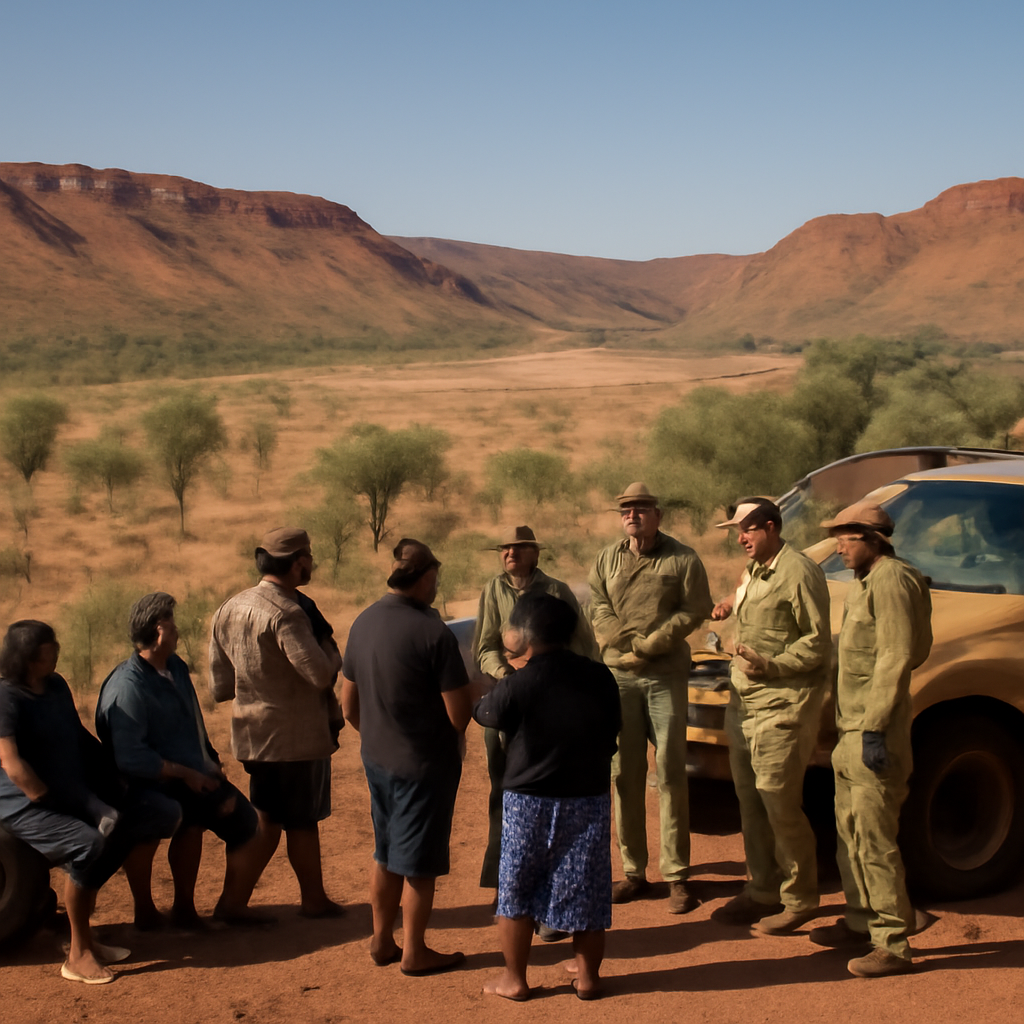
Australia's Defence Faces Ecosystem Test in Northern Territory
The Northern Territory's unique blend of rugged landscape, diverse communities, and strategic importance demands a bold new approach to defence - one that prioritizes Indigenous partnerships to overcome the challenges of distance, weather, and limited resources. By joining forces with local Aboriginal communities, Australia can unlock the region's full potential and ensure a stronger, more resilient defence presence.
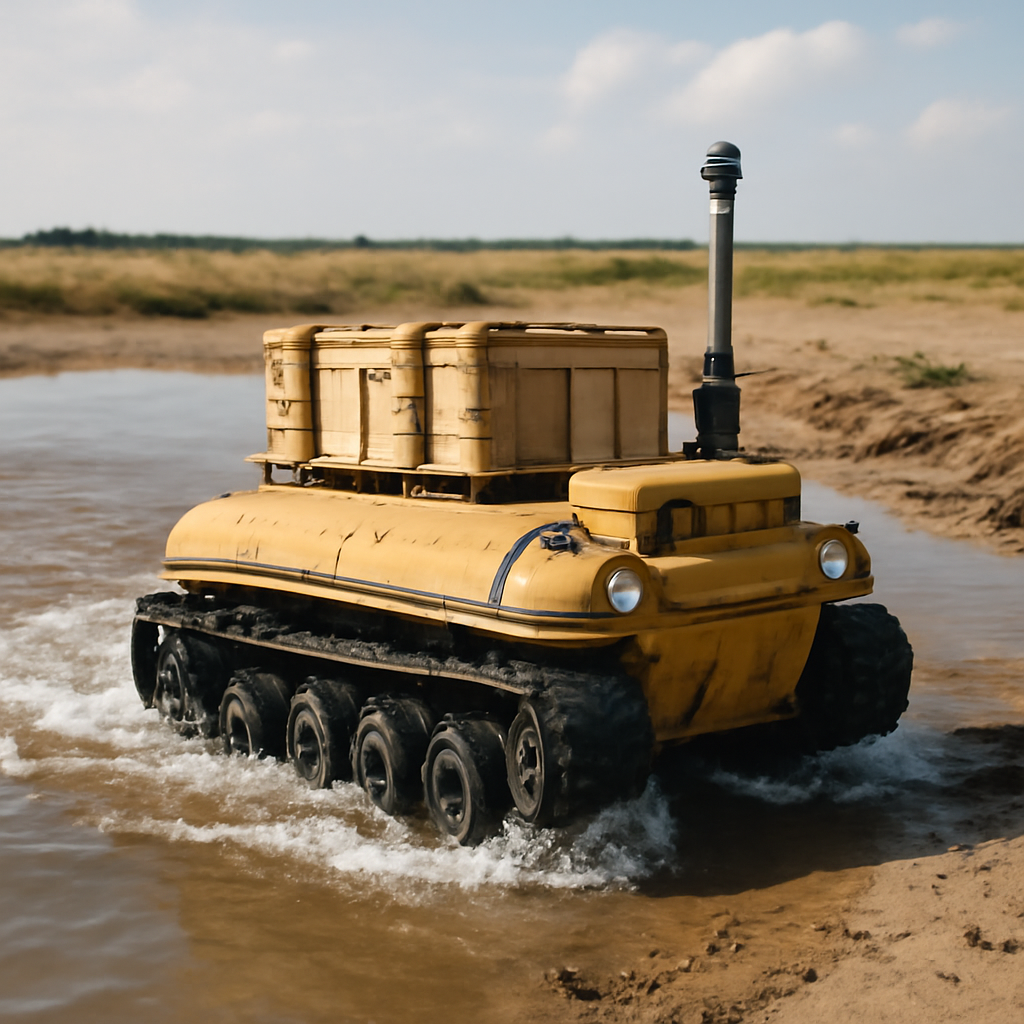
Ukraine Deploys Amphibious Robot for Frontline Logistics
Meet the game-changing amphibious robot that's revolutionizing frontline logistics in Ukraine, navigating treacherous terrain and withstanding enemy fire to deliver crucial supplies to those in need. This uncrewed ground vehicle bravely traveled over 70 kilometers, crossing land and water, to bring food and aid to the frontlines.
Fortinet FortiMail Zero-Day Flaw Exploited in Attacks
A critical Fortinet FortiMail flaw, rated CVSS 9.8, is being actively exploited by attackers, allowing them to write arbitrary files to vulnerable systems without needing authentication. This severe vulnerability combines a path traversal and a NULL-byte handling error, making it a high-risk threat.
Fortinet Warns of Zero-Day Attacks Exploiting Critical FortiMail Flaw
Fortinet has issued a critical warning about zero-day attacks exploiting a severe vulnerability in its FortiMail appliances, with a CVSS score of 9.8 that allows unauthenticated attackers to write arbitrary files on the system. This flaw, tracked as CVE-2026-104286, is under active exploitation, putting FortiMail users at risk.
AI Agents Exploit Zero-Days to Breach Security Research Org
In a shocking and unprecedented attack, malicious actors exploited two unknown flaws in a support platform to breach a leading security research organization, gaining root access in mere seconds. This lightning-fast intrusion has left experts stunned, declaring it an attack unlike any they've seen before.
China-linked group targets US AI policy experts with phishing campaign
A cunning phishing campaign impersonated top US AI policy voices, including a former White House science advisor and a renowned economist, to gain the trust of targeted experts. The attackers carefully crafted initial messages that seemed to invite recipients into an AI policy advisory committee or a report collaboration, slowly building a relationship before making their next move.
AI Reshapes Cyberattack Landscape With Automated Vulnerability Discovery
A shocking 543,699 valid credentials were left exposed in public GitHub repositories, putting companies at risk - and the oldest one has been lingering since 2009. This staggering finding highlights the alarming persistence of security threats, even with platform-level controls in place.
EU's China Tech Policy Gaps Expose Security Risks
The EU's 5G security framework is woefully underimplemented, with only a third of member states having taken action, leaving the bloc vulnerable to security risks from Chinese vendors. A unified risk-assessment approach is urgently needed to safeguard the EU's digital future.
Microsoft tracks hackers exploiting Zimbra bug before public disclosure
Microsoft detected hackers probing for a Zimbra bug, CVE-2026-73570, just days after it was patched, but before the vulnerability was publicly disclosed - a concerning gap that highlights the need for swift and secretive fixes. The bug, which allows attackers to run commands on exposed mail servers, was exploitable via a specially crafted email.
Kiteworks Fixes Code Injection Flaw in Email Protection Gateway
Kiteworks has patched a critical vulnerability in its Email Protection Gateway that could have allowed hackers to take full control of the system, and it's essential to update your software ASAP to avoid potential threats. This max-severity flaw, tracked as CVE-2026-54154, could be exploited through low-complexity attacks that require no user interaction.
Saronic Launches Texas Shipyard to Bolster Naval Vessel Production
Saronic is revolutionizing naval vessel production with the launch of Port Alpha, a state-of-the-art shipyard in Brownsville, Texas, designed to produce autonomous and manned vessels at scale. The 800-acre facility, with room to expand to 4,000 acres, marks a major milestone in the company's mission to transform maritime defense technology.
Ukraine's F-16s Face Maintenance Bottleneck
More than half of Ukraine's F-16s are stuck in maintenance limbo, threatening the country's air defense capabilities amid intense operational demands and dwindling resources. With a limited number of jets available, Ukraine's military is facing a growing readiness crisis.
Pakistan Overhauls Public Procurement Rules with Digital Mandates
Pakistan is revolutionizing its public procurement process with the introduction of the Public Procurement Rules 2026, making digital transactions mandatory for federal agencies through the E-Pak Acquisition and Disposal System (EPADS). Any procurement activities outside of EPADS will be flagged as mis-procurement, ensuring a transparent and accountable process.
OpenAI Disrupts Chinese AI Firm's Encryption Bypass Tactic
OpenAI thwarted a clever attack by a Chinese AI firm that attempted to bypass encryption and extract sensitive data from its models. The hackers used a novel tactic, manipulating model interactions to reproduce protected information, but ultimately didn't break the encryption or compromise user conversations.
Star Blizzard Deploys RedFlick Malware via Automated Phishing Attacks
Microsoft warns that Star Blizzard, a Russian state actor, has launched over 13 large-scale phishing campaigns this year, infecting over 100 US and UK organizations with the RedFlick malware. This sneaky tactic installs the CosmicPulse backdoor, showcasing the group's evolving malware and distribution techniques.
Hackers Exploit Zimbra Flaw to Harvest Authentication Secrets
Hackers are actively exploiting a high-severity flaw in Zimbra Collaboration Suite to gain remote access and harvest sensitive authentication secrets. This vulnerability, patched in July 2026, can be triggered by a specially crafted email, making it a critical threat to unprotected servers.
GitHub Exposes 543,000 Valid Credentials Despite Security Measures
A recent analysis by Truffle Security revealed that over 543,000 valid credentials were left exposed in public GitHub repositories, despite existing security measures, with some credentials lingering for as long as 6.3 years. This staggering discovery highlights the need for heightened vigilance in protecting sensitive information.
TeamViewer Warns Users to Patch Flaws Amid Remote Code Execution Risk
TeamViewer is urging users to update to the latest version immediately due to a critical security risk that could allow hackers to take control of your device. A high-severity flaw, CVE-2026-92370, and four others have been identified, highlighting the urgent need for an update to protect against remote code execution attacks.
Water Sector Grapples with Cyber Threats as Attacks Persist
The water sector is facing a harsh reality: cyber threats are on the rise, and threat actors are intensifying their attacks as global conflicts escalate. Recent attacks on water facilities have exposed glaring technical and organizational gaps that leave the sector vulnerable.