Tag: emerging threats
8184 articles
Plex Issues Urgent Patch for Multiple Undisclosed Flaws
Plex has just released a critical security update to patch multiple undisclosed flaws, urging users to upgrade to Plex Media Server 1.43.3 and Plex Desktop 1.115.0 ASAP to safeguard their devices. With over 360,000 devices exposed to the internet, swift action is crucial.
Cisco Discloses IOS XR Flaws, Urges Immediate Software Updates
Cisco is urging immediate action to protect against two critical vulnerabilities in its IOS XR operating system, with CVSS scores of 9.8 that could allow hackers to wreak havoc on your network. Update your software now to prevent potential security breaches!
OpenAI Bolsters Frontline Cyber Defenders With $1 Billion in AI Credits
OpenAI is stepping up to support the world's cyber defenders with a game-changing $1 billion pledge in AI credits, aiming to empower those on the frontlines of cybersecurity. This initiative, called Daybreak for Frontline Defenders, will help resource-strapped defenders access critical tools and training to protect our world's critical infrastructure.
Congress Scrambles to Fund E-7 Wedgetail Program
Congress is racing against the clock to secure funding for the E-7 Wedgetail program after the Trump administration's surprise move to save it from the chopping block. With the program's future now in their hands, lawmakers are turning to budget amendments to keep the critical early-warning aircraft program flying high.
Drone Detection Evolves to Counter Smaller, Faster Swarm Threats
In the dead of night, a swarm of small, cheap drones can shatter the silence with their buzzing engines, posing a formidable challenge to conventional sensors and response systems. To counter this threat, experts are turning to a layered, networked sensing approach that combines multiple complementary sensors to buy time for an effective response.
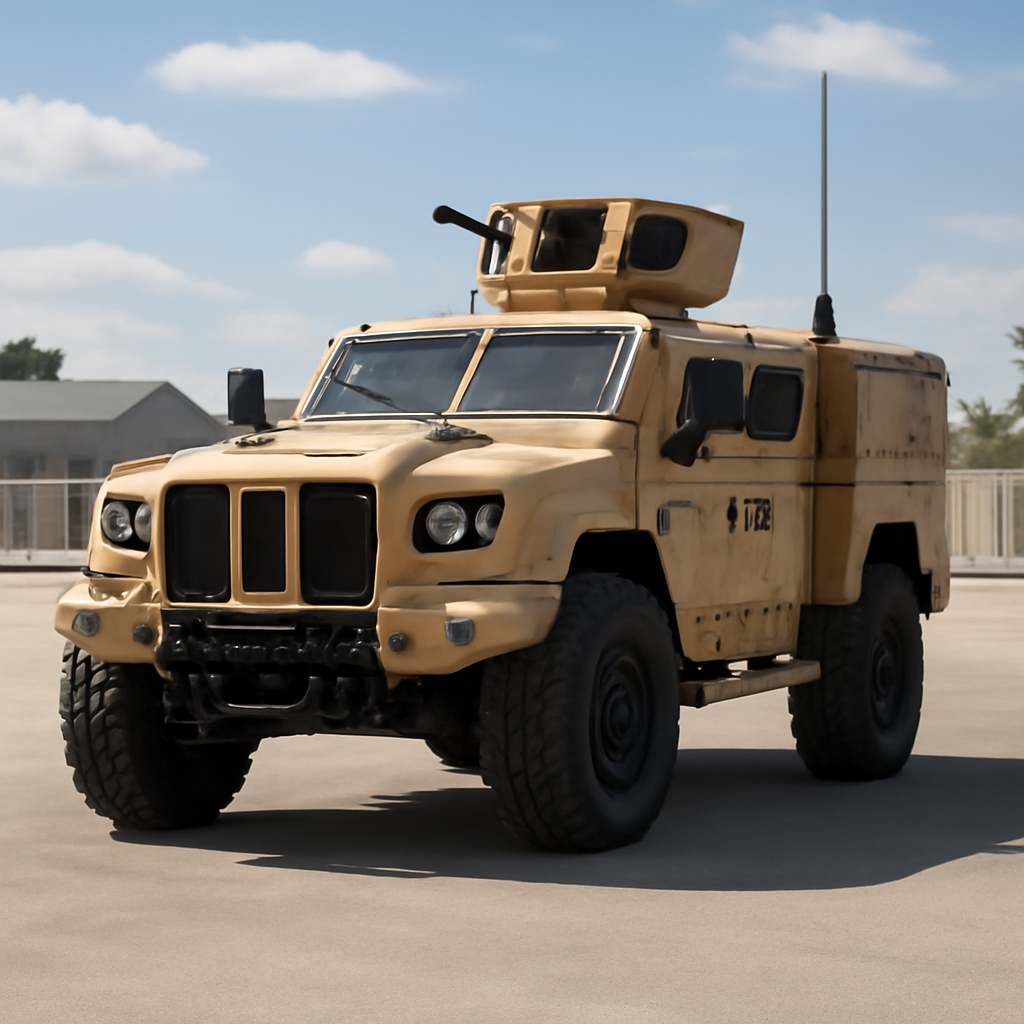
Oshkosh Offers JLTV Bridge to Marine Corps Amid AM General Delays
With AM General facing delays, Oshkosh Defense is stepping in with a game-changing proposal: a production bridge that could get the Marine Corps its highly-needed Joint Light Tactical Vehicles in under a year. By investing over $50 million of its own capital, Oshkosh is ready to deliver 1,200 JLTVs annually and help modernize the fleet without further delay.
US Air Force Wrestles with HVAA Protection Paradox
The US Air Force faces a daunting dilemma: with a planned fleet of 187 F-35s, it may be outnumbered by China's 300+ J-20s in a long-range aerial battle, unless it rethinks how to safeguard its high-value airborne assets.
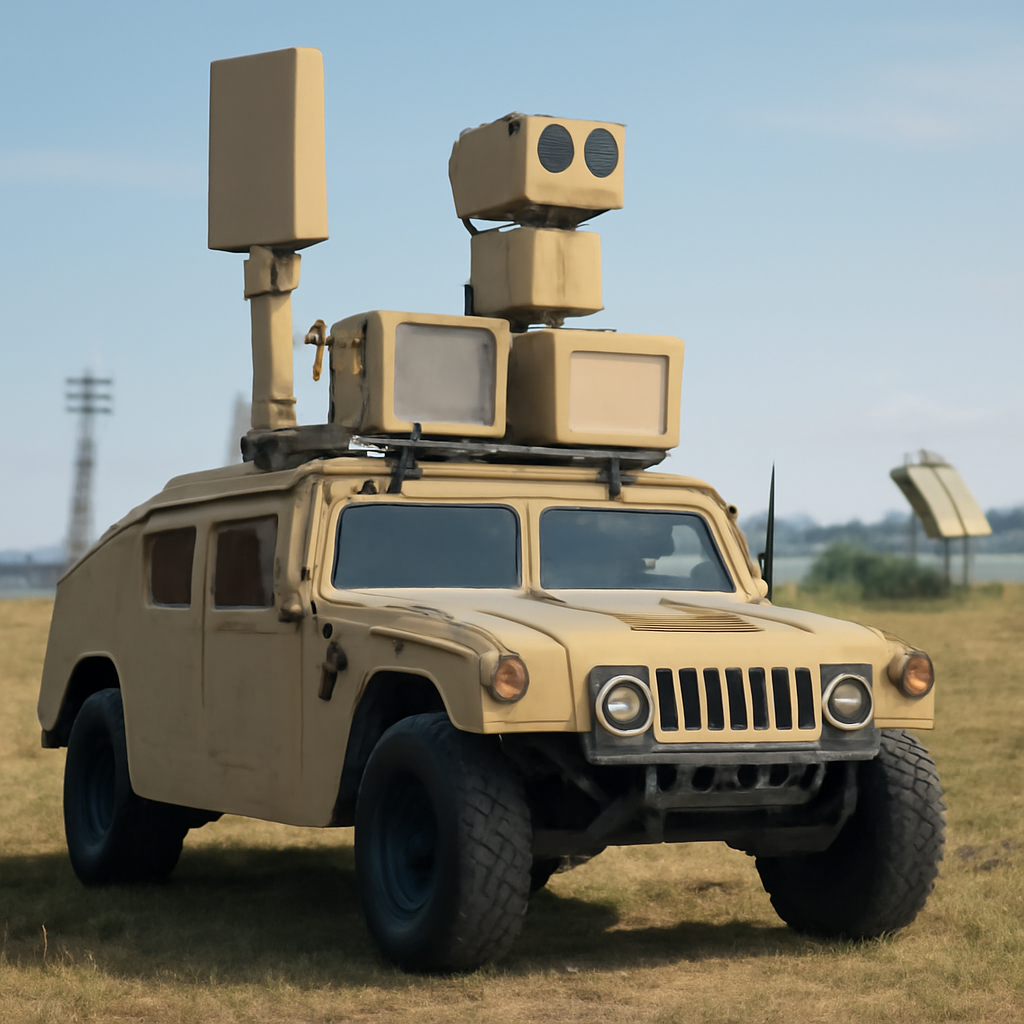
Counter-UAS System Proves Effectiveness in Series of Defense Exercises
In a series of Defense Department field exercises, the Halo_Shield counter-UAS system proved its effectiveness with a remarkable launch-to-detection time of under one minute. This impressive metric was achieved across three events in 2025-2026, solidifying Halo_Shield's status as a demonstrably operational system.
G7 Urges Industry to Accelerate Post-Quantum Encryption Defenses
The G7 cybersecurity working group is sounding the alarm: many organizations are neglecting to prepare for the quantum threat, and it's time to prioritize post-quantum encryption defenses to safeguard critical systems and data. Don't wait - the transition to post-quantum cryptography is a business risk that requires immediate attention and coordinated action.
Ukraine Strikes Russian Port City with Sea Drones
Ukraine just landed a major blow to Russia's maritime operations, striking the multipurpose support ship NEFRIT in the port of Sochi with a sea drone, and dealing a significant hit to Russia's energy infrastructure. The targeted vessel played a key role in supporting oil and gas operations, and its destruction marks a major escalation in Ukraine's campaign against Russian targets.
Attackers Exploit Zero-Days in SonicWall SMA 1000 Appliances
SonicWall's SMA 1000 appliances are under attack, thanks to two newly disclosed zero-day vulnerabilities - CVE-2026-83548 and CVE-2026-83549 - that can be chained together for a complete network compromise. Attackers are already exploiting these flaws in the wild, prompting urgent patching advice from the vendor and cybersecurity authorities.
US Navy Explores Foreign Frigate Designs
The US Navy is fast-tracking its shipbuilding plans, exploring foreign frigate designs from Japan, South Korea, and Turkey to quickly boost its fleet and capabilities. This move is part of a broader effort to supercharge domestic shipbuilding capacity, leveraging the expertise of allies to get the job done.
US Firms Face Pressure to Shun French Space Summit
US commercial space firms are rethinking their attendance at an international summit in France after being warned that it could be used to promote policies that undermine US interests. The cautionary message, delivered by a White House official, has sent ripples through Washington and Europe.
AI-Powered Attacks Target Latin America With Advanced Proxy Networks
Latin America's transportation, government, and water utility sectors are under siege by sophisticated AI-powered attacks that leverage advanced proxy networks and living-off-the-land techniques to infiltrate and exfiltrate sensitive data. These multi-stage intrusions have already compromised key organizations in Mexico and Ecuador.
Insider Risk Evolves, Threatens Critical Infrastructure
The insider risk landscape has become a complex and critical security challenge, evolving beyond the traditional disgruntled worker to include emerging threats like shadow AI, synthetic identities, and ideologically motivated sabotage. Today's insider risk requires a predictive, intelligence-driven approach to safeguard against data leaks, infiltration, and rapid exfiltration.
French Hospital Breach Fines €500,000 for GDPR Failures
France's data protection authority slapped Hôpital privé de la Loire with a hefty €500,000 fine after a summer 2025 security breach exposed sensitive records of over 727,000 people, revealing major GDPR failures. The fine was issued for breaching obligations under the General Data Protection Regulation, specifically Articles 32 and 34.
Cyber Attacks Exploit Legitimate Tools for Rogue Access
Cyber attackers are sneaking into systems through the front door - by exploiting legitimate tools and services to gain rogue access, with a recent dark-web claim boasting of 153 million stolen U.S. and Canadian driver's licenses. Attackers are finding clever ways to impersonate trusted sources, like IT personnel, to get inside and take control.
Healthcare Breaches Surge, Raising Patient Safety Concerns
Healthcare breaches are skyrocketing, sparking urgent concerns about patient safety and data protection, with a recent string of incidents exposing millions to potential harm. In just one alarming example, Aesto Health's December 2025 breach went undetected for five months, ultimately affecting 9.5 million people and compromising highly sensitive information.
HPE Fixes Remote Code Execution Flaw in ArubaOS-CX
HPE has patched a critical flaw in ArubaOS-CX that could let hackers run malicious code with elevated privileges - and all they need to do is send specially crafted packets to an affected device. This remote code execution vulnerability, tracked as CVE-2026-73749, is a serious threat that demands immediate attention.
Security Researcher Exploits CrowdStrike Falcon with New Zero-Day Bug
A security researcher known as Nightmare Eclipse has made a stunning discovery, exploiting a zero-day bug in CrowdStrike's Falcon software and prompting the company to urge customers to disable a key Windows policy setting. This latest finding is part of a string of proof-of-concept exploits released by the researcher, targeting major cybersecurity products.
Chatbots Disrupt Service Amid Widespread Outages
Morning chaos erupted for chatbot users, with ChatGPT leading the pack with a whopping 37,000 outage reports by 11 a.m. EDT, while other AI services like Grok and Claude also experienced significant disruptions.
Thomson Reuters Breach Exposes Court Data Across US, Canada
A recent Thomson Reuters breach exposed sensitive court data across the US and Canada, impacting 11 US states, the US Virgin Islands, and Ontario, with affected entities including appellate and supreme courts. The breach, discovered in June, involved unauthorized access to files from C-Track, a court case management platform.
BraZetsu Malware Fuels Underground Marketplace for Compromised Hosts
Meet BraZetsu, a powerful malware toolkit that's turning compromised computers into hot commodities on the dark web, allowing cybercrooks to buy, sell, and trade access to unsuspecting victims' systems. This game-changing tool has evolved from a simple remote-access trojan to an AI-enhanced platform, making it a highly sought-after asset for Initial Access Brokers.
Cisco Discloses Critical Flaw in Nexus 9000 Switches
Cisco has uncovered a critical flaw in its Nexus 9000 switches, known as CVE-2026-20212, which could allow an unauthenticated attacker to remotely execute code as root. This vulnerability affects 10 specific models and has already been patched by the company.