Tag: emerging threats
8404 articles

PLA Unveils Upgraded Bangalore Torpedo
Meet the GBP113A, a game-changing upgrade to the century-old Bangalore torpedo, now with a rigid-flexible combination design that lets it curve, snake, and blast its way into previously hard-to-reach areas. This innovative device delivers the same powerful punch as its predecessor, but with added maneuverability and flexibility.

SaaS Providers Face Trust Crisis After Canvas Breach
A massive breach of the Canvas learning management system has left 275 million users reeling, compromising student records and disrupting learning at over 8,800 institutions worldwide. The shocking incident has sparked a trust crisis for SaaS providers, raising urgent questions about security and data protection.
Anthropic Readies Restricted AI Model for Public Rollout
Anthropic is on the cusp of unveiling its game-changing Mythos model, a frontier AI that's poised to revolutionize code reasoning and autonomy with capabilities that far surpass its predecessors. This powerful tool could redefine the cyber landscape, giving a significant edge to those who harness its potential.

Australia's Defence Strategy Lags in Information War Arena
Australia is losing ground in a different kind of battle – one of perception and understanding – where adversaries are manipulating what people believe to be true, eroding public trust and turning domestic audiences into a vulnerability in times of crisis. By shaping perceptions through information, our nation risks being left behind in the information war arena.

Linux Flaws Expose Critical Infrastructure to Root Command Execution
GitHub confirmed that a compromised employee device, infected by a poisoned Nx Console VS Code extension, led to the theft of around 3,800 internal repositories, sparking swift action to contain the breach and protect sensitive data. The incident highlights the vulnerability of even the most secure systems to supply chain attacks.
FBI Warns of Kali365 Phishing Service Targeting Microsoft 365 Accounts
Beware of Kali365, a sneaky phishing service that's hijacking Microsoft 365 accounts by exploiting a legitimate authentication flow - and it's happening fast, with the platform emerging as recently as April 2026. This clever trick uses a short code to trick victims into handing over control of their accounts.

Agentic AI Tames Network Detection's Alert Firehose
Imagine sifting through 847 network anomalies daily - that's like trying to find a needle in a haystack! With agentic AI triage, that overwhelming number is dramatically reduced to just 4 prioritized detections, complete with the evidence and suggested actions analysts need to take swift and effective action.

Ghost CMS Flaw Exploited to Hijack Over 700 Sites in ClickFix Attacks
Over 700 websites were hijacked in a massive campaign that exploited a critical Ghost CMS vulnerability, turning legitimate pages into gateways for Windows malware. This alarming attack was made possible by CVE-2026-26980, an SQL injection flaw with a near-perfect CVSS score of 9.4.

Lazarus Group Deploys Memory-Only RAT in Financial Sector Attacks
The notorious Lazarus Group has unleashed a sneaky new attack tool, a memory-only Remote Access Trojan (RAT), targeting the financial sector with cunning precision. This stealthy malware, known as RemotePE, is just the latest weapon in the group's arsenal, and it's being used to infiltrate and manipulate its victims.

FBI Warns of Kali365 Phishing Kit's OAuth Token Heist
The FBI has sounded the alarm on Kali365, a phishing-as-a-service platform that's making it easy for even novice hackers to steal Microsoft 365 login credentials and bypass security measures like multifactor authentication. This subscription-based service, mainly spread through Telegram, provides attackers with AI-generated phishing lures, campaign templates, and real-time tracking tools to target individuals and organizations.

Fraudsters Target F1 Fans with Fake Streams, Counterfeit Merch Scams
When it comes to motorsports, speed is a double-edged sword - while the action is fast-paced and thrilling, it also creates opportunities for scammers to strike, as noted by Bogdan Botezatu, senior director of threat research at Bitdefender. Cybercriminals are now targeting F1 fans with fake streams and counterfeit merch scams, making it essential for fans to stay vigilant.

TrapDoor Attack Spreads Credential-Stealing Malware Across Software Ecosystems
A massive supply chain attack, dubbed TrapDoor, has been spreading credential-stealing malware across three major language ecosystems, infecting over 34 malicious packages and 384 versions. The coordinated campaign began on May 22, 2026, and continues to target developers with cleverly named packages related to cryptocurrency, DeFi, Solana, and AI.
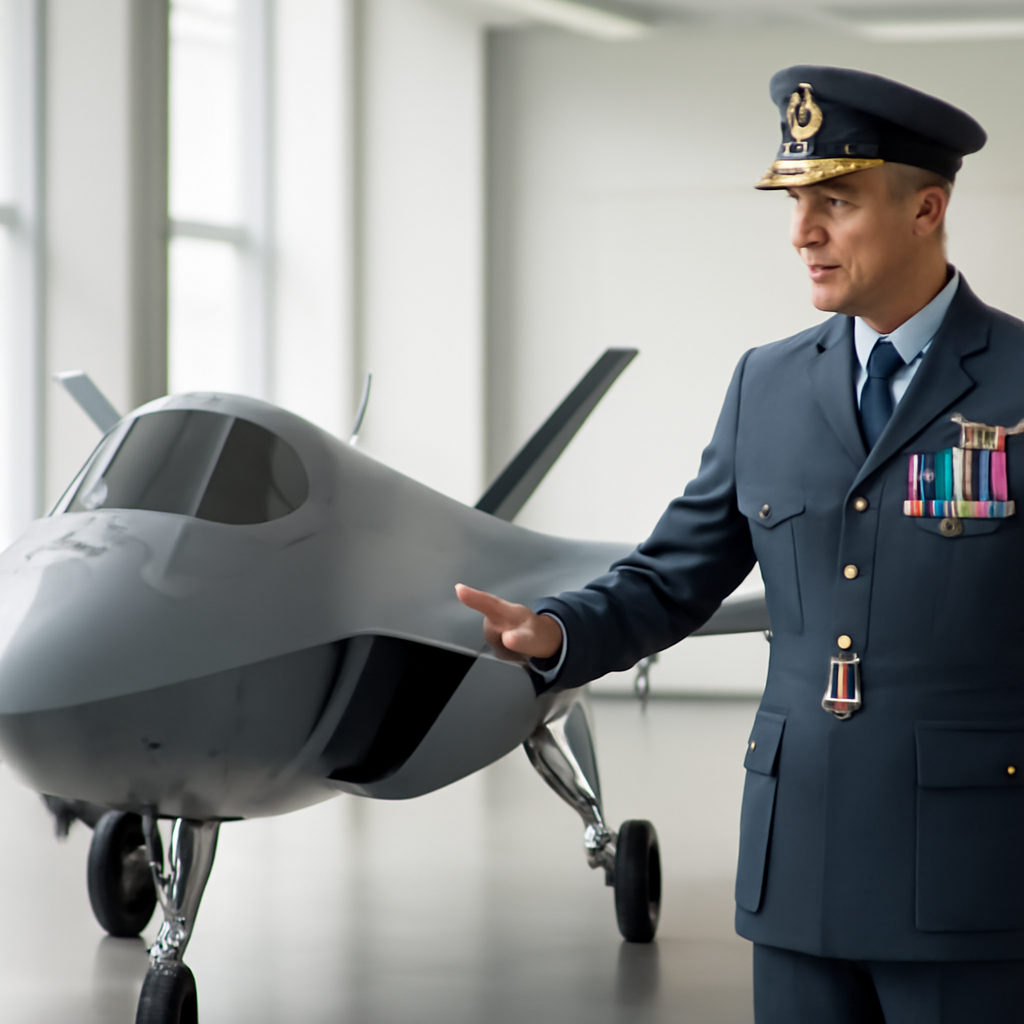
Pakistan Air Force Explores Bayraktar Kizilelma for Autonomous Combat Architecture
A dramatic photo of Pakistan's top air chief standing beside a cutting-edge stealth drone, fresh from a successful test firing a long-range missile, marks a significant turning point in the country's military capabilities. This powerful image signals a major leap forward in Pakistan's pursuit of autonomous combat technology.
Mandiant Exposes KnowledgeDeliver Vulnerability via ViewState Deserialization
A critical vulnerability, CVE-2026-5426, was discovered in KnowledgeDeliver installations, allowing unauthenticated remote code execution across multiple customer sites due to identical ASP.NET machineKey values. This widespread flaw was caused by a standardized web.config with hardcoded keys, used across deployments, leaving sites vulnerable to attack.

US Navy to Test Aircraft Carrier as Floating Nuclear Power Plant
This summer, the US Navy will pioneer a groundbreaking experiment, using an aircraft carrier as a floating nuclear power plant to energize Norfolk Naval Base. The innovative test aims to demonstrate the Navy's ability to deliver reliable, mission-critical power to its installations.
US Military Grapples with Pacific Theater's Logistics Challenge
The harsh reality of the Pacific Theater's logistics challenge was summed up by Gen. Xavier Brunson: if our supply lines stretch 5,000 miles, we can't win. The daunting distances are stark: Hawaii is 3,000 miles from the US West Coast, and the critical first island chain is 1,500 miles from Guam, leaving a vast, sparsely supported ocean.

Chinese PhaaS Ecosystem Evolves, Threatens Global Financial Security
The game has changed in the world of phishing: attackers are now using Phishing as a Service (PhaaS) to intercept one-time passcodes and tokenize payment cards, giving them direct control over victims' financial accounts. This sinister shift threatens global financial security, allowing attackers to tap into accounts in real-time.
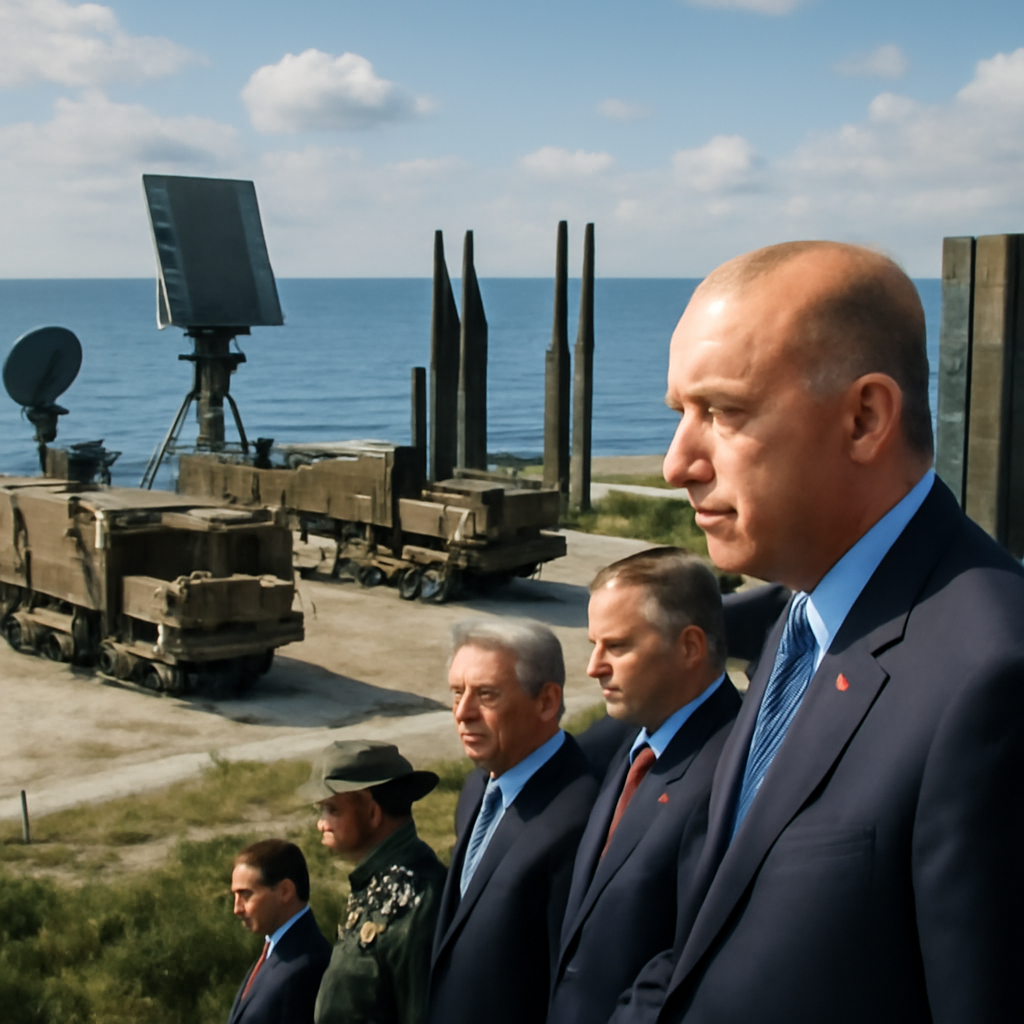
Turkey Unveils Integrated Steel Dome Air Defence Architecture
Witnessing a major milestone in air defence technology, President Recep Tayyip Erdoğan and defence leaders from 50 nations gathered to unveil Türkiye's revolutionary Steel Dome architecture in action. For the first time, the multi-layered air and missile defence system was showcased in a live-fire demonstration, leaving a lasting impression on its international audience.

US Special Ops Forces Seek AI Edge in Remote Warfare
US Special Ops Forces are leveraging AI to gain a strategic edge in remote warfare, with a focus on harnessing generative AI for tactical operations and resource allocation. They're now pushing to deploy AI capabilities to the tactical edge, enabling faster decision-making in disconnected environments.

AI-Discovered Bugs Expose Linux Security Trend
Linux is facing a surge in security vulnerabilities, with two high-risk kernel-level flaws uncovered just days apart - a trend that's expected to continue, potentially forcing companies to reboot servers on a weekly basis. These recently publicized issues, including Dirty Frag, Copy Fail, and Fragnesia, are linked by a common weakness in the page cache, a core kernel abstraction.
Ghost CMS SQL flaw fuels large-scale ClickFix attacks
Over 700 domains were hit in a massive cyberattack that exploited a critical vulnerability in Ghost CMS, putting sensitive data at risk. The flaw, tracked as CVE-2026-26980, allowed hackers to tap into site databases and steal admin API keys.

Pakistan Wrestles with JF-17's Industrial Future
As Pakistan's JF-17 Thunder aircraft proves its mettle in combat, a new question takes center stage: will this successful jet remain just a procurement prize or become the cornerstone of a thriving domestic aerospace industry? With over 170 JF-17s produced and export interest soaring, the country's defence planners must decide how to take the reins of this high-flying program.
GitHub Tags Exploited to Deploy Credential-Stealing Malware
Malicious actors have manipulated hundreds of GitHub tags to spread credential-stealing malware through popular Laravel Lang localization packages, putting countless users at risk. By rewriting historical tags, attackers tricked Composer installations into downloading the malicious payload.

GitHub-Hosted Malware Targets PHP Packages in Coordinated Supply Chain Attack
Malicious code was injected into eight PHP packages on Packagist, triggering a Linux binary download from GitHub Releases via JavaScript lifecycle hooks in package.json postinstall scripts. The attack was swiftly contained, with the malicious versions removed from Packagist.