Tag: emerging threats
8404 articles

Fiber Network Anchors US Homeland Defense Initiative
In today's complex threat landscape, the US faces a multitude of adversaries with malicious intentions, making traditional defense strategies obsolete. Lumen's Golden Dome initiative aims to revolutionize homeland defense with a cutting-edge, data-driven approach that enables rapid decision-making and decisive action.

South Korea Accelerates Nuclear-Powered Submarine Development Plan
South Korea is set to make waves with its ambitious plan to launch its first nuclear-powered submarine in the mid-2030s, with the goal of having it enter operational service later that decade. The development roadmap, unveiled by Defense Minister Ahn Gyu-back, marks a major milestone in the country's naval modernization efforts.

Anthropic's AI Model Uncovers 10,000 Software Vulnerabilities
Anthropic's AI model has made a groundbreaking discovery, uncovering over 10,000 high- or critical-severity software vulnerabilities in just a month of testing. This game-changing technology is shifting the focus from detection to fixing these bugs, highlighting the need for increased human capacity to triage, report, and deploy patches.

Texas Tech University Bolsters Critical Infrastructure Security with New Research Site
Texas Tech University is taking a giant leap in safeguarding America's critical infrastructure with the launch of a cutting-edge research site, solidifying its role as a leader in national security. The new facility at the Reese National Security Complex will supercharge innovation and collaboration to tackle vulnerabilities and protect the nation's backbone.

Chinese Phishing Services Shift to Live Credential Interception Tactics
Cyber attackers are now using live administration panels to interact with victims in real-time, capturing one-time passcodes and instantly bypassing multifactor authentication protections. This new tactic allows them to neutralize security measures and steal sensitive information more effectively.

Lithuania's National Register Breached, 600,000 Entries Exposed
A massive data breach has hit Lithuania's national registers, exposing over 600,000 sensitive entries, including records of legal entities and real estate holdings. The breach has prompted swift action from authorities, who have restricted access and blocked suspected accounts to mitigate the damage.
BTMOB Android RAT Exploits No-Code Tools in Global Phishing Campaigns
A single malicious download can put an entire company's sensitive data at risk, so it's crucial for corporate security teams to educate employees on the dangers of rogue apps.
Microsoft Defender Automatically Isolates Hacked Endpoints
Microsoft Defender for Endpoint just got a major boost with its new automatic isolation feature, which swiftly isolates compromised devices to prevent attackers from wreaking havoc on your organization. This cutting-edge capability is part of Microsoft's automatic attack disruption feature, designed to contain threats and give security teams more time to respond.

Microsoft Fixes SharePoint Flaw That Exposes Servers to Remote Code Execution
Microsoft just patched a high-severity flaw in SharePoint that could let hackers execute malicious code remotely - and it's crucial you update your servers ASAP to stay safe. The vulnerability, tracked as CVE-2026-45659, has a CVSS score of 8.8, making it a prime target for attackers.

Experts Dispute Farage's Russian Hack Claim
Nigel Farage's claim that Russian spies hacked his phone and leaked a £5 million gift from a close associate has sparked controversy, with experts demanding evidence to back up the explosive allegation. Ciaran Martin hit back, saying Farage has produced no evidence to support his aggressive intervention claim.
MFA Prompt Bombing Exposes Weakness in Two-Factor Security
A shocking 2.8GB of data was stolen from Cisco after a clever attacker tricked an employee into approving a push-based MFA prompt, highlighting a disturbing vulnerability in two-factor security. This brazen hack, linked to the Yanluowang ransomware group, shows how attackers can exploit the very security measures meant to protect us.

India's CERT-In Mandates Swift Patching for Exposed Flaws
CERT-In is urging organizations to act fast to contain cyber threats, setting a tight 12-hour deadline to patch known vulnerabilities in critical, internet-facing systems. This swift response aims to combat the accelerating threat of AI-driven cyber-attacks.

Iranian Hackers Deploy AI-Backed MiniFast Backdoor via Phishing and SEO Poisoning
Iranian hackers have escalated their cyber attacks, leveraging AI-powered tools to craft malware and targeting key sectors like aviation, defense, and telecommunications across the US, Europe, and the Middle East. Their sophisticated tactics, including phishing and SEO poisoning, have allowed them to spy on organizations with alarming speed and efficiency.

Iran-Linked Hackers Target US Aviation with Sophisticated Phishing and SEO Poisoning
Meet Nimbus Manticore, an Iran-linked hacking group that's back with a vengeance, using clever phishing and SEO poisoning tactics to target the US aviation industry in a series of sophisticated attacks. Their latest campaign, which ran from February to April 2026, marked a significant expansion into aviation, defense, and telecommunications.

CISA Mandates Patching of Exploited Drupal Vulnerability
The US Cybersecurity and Infrastructure Security Agency has issued a directive requiring federal agencies to patch a critical Drupal vulnerability, known as CVE-2026-9082, by May 27 to prevent devastating SQL injection attacks. This highly critical flaw allows hackers to exploit PostgreSQL-powered Drupal sites and gain unauthorized access to sensitive information.

Microsoft Warns of Domain Controller Lookup Failures on Windows Server 2016
If you've installed the KB5087537 update on your Windows Server 2016 system, be aware that domain controller lookup may fail if your server hostname is exactly 15 characters long. This issue affects only those with 15-character hostnames, so check yours to see if you're impacted.

7-Eleven Data Breach Compromises 185,000 People's Personal Info
A recent 7-Eleven data breach has put the personal info of 185,000 people at risk, exposing sensitive details like names, addresses, birthdays, and phone numbers. The breach, which occurred on April 8, 2026, is still shrouded in mystery, with 7-Eleven only confirming that certain systems storing franchisee documents were compromised.
KnowledgeDeliver LMS Flaw Exploited to Deploy Malware
A security flaw in the KnowledgeDeliver LMS, known as CVE-2026-5426, was exploited by a threat actor to inject malicious code and infect users visiting the site. This vulnerability was caused by a predictable secret in the system's web.config file, allowing attackers to execute remote code.
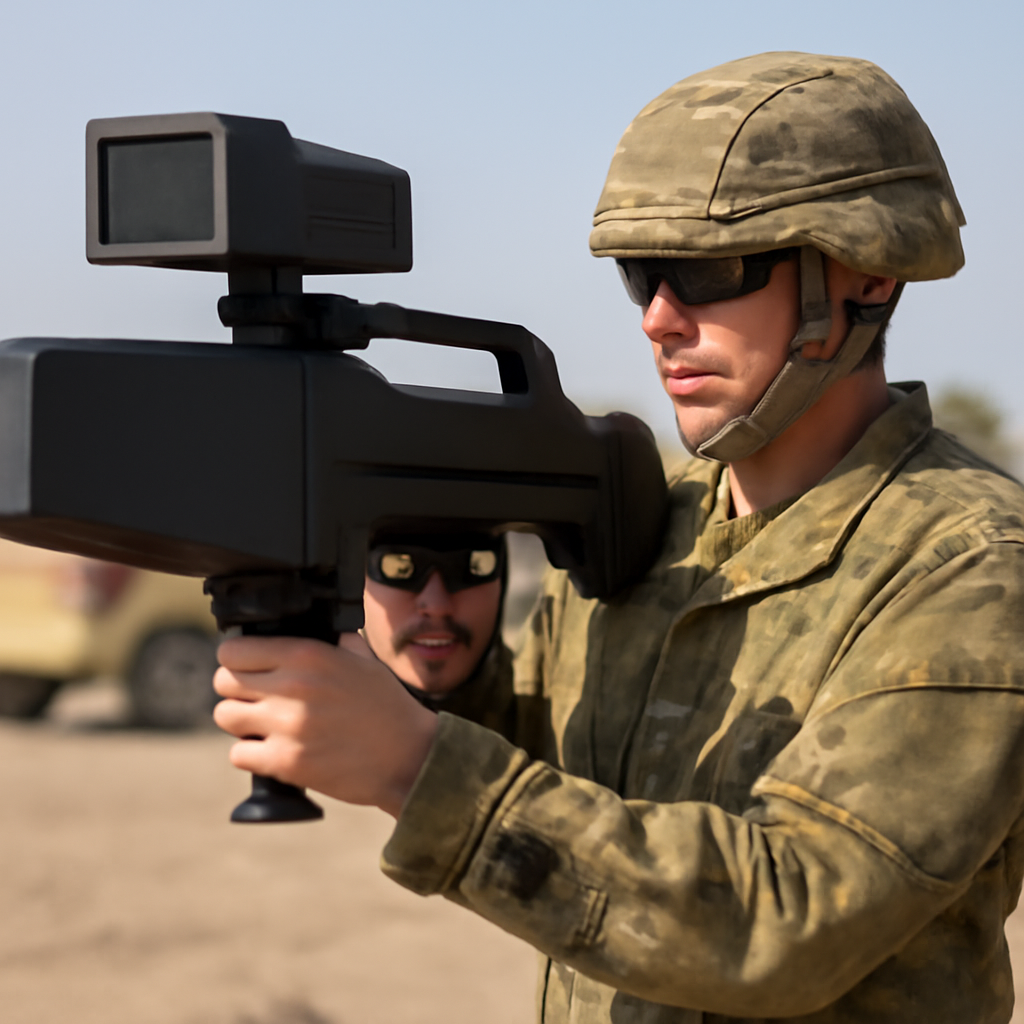
Pentagon Taps Perennial Autonomy for $500M Counter-Drone Contract
The Pentagon has taken a major stand against the growing threat of drones, awarding a $500 million contract to Perennial Autonomy for cutting-edge, AI-powered counter-drone systems. This game-changing deal is part of the US military's broader Drone Dominance initiative to stay ahead of the curve in modern warfare.

USAF Deploys Upgraded ULTRA Surveillance Drones to Middle East
The US Air Force has taken a major leap forward with its ULTRA Surveillance Drones, successfully completing a 60-hour flight at 25,000 feet and 100 knots - now, a turbocharged variant is set for operational testing in the Middle East. This next phase will see the drone put through its paces in a real-world setting within US Central Command's area of responsibility.

China's 'Bohai Sea Monster' Emerges with Apparent Combat Capabilities
Newly surfaced images of China's mysterious Bohai Sea Monster reveal a surprising detail: four turboprop engines, each driving a three-bladed propeller, hinting at a more complex role and extended range than initially thought. This game-changing feature has analysts reevaluating the capabilities of this enigmatic craft.

Europe's Drone Defense Gap Exposes Critical Infrastructure Risks
Europe's critical infrastructure is left vulnerable due to a lack of clear governance and rules of engagement, despite having the technology to defend against drone threats. The absence of ownership and jurisdictional clarity hinders the deployment of drone defense systems where they're needed most.

Dutch Authorities Disrupt Russian Cyber Operations, Seize 800 Servers
In a major blow to Russian cybercrime, Dutch authorities seized over 800 servers and arrested two individuals in a daring raid that cracked down on illicit online operations. The suspects, a 57-year-old Amsterdam resident and a 39-year-old from The Hague, were charged with violating sanctions law by aiding EU-sanctioned entities.

Damaged KC-135 Tanker Spotted at RAF Mildenhall Amid Post-War Repairs
A KC-135 tanker, bearing scars of a intense battle, has been spotted at RAF Mildenhall, its damaged airframe a testament to the high stakes of war, with makeshift repairs and a missing refueling boom telling a story of their own. Aviation photographer Andrew McKelvey captured striking images of the battered jet, revealing a patchwork of temporary fixes and shrapnel damage.