Tag: emerging threats
8355 articles
Ransomware Attacks Surge Across Europe
Ransomware attacks are surging across Europe, with a staggering 55.1% year-over-year increase in just the first four months of 2026, averaging 171 incidents per month. Five key countries - Germany, the UK, France, Italy, and Spain - are bearing the brunt, accounting for 70% of all recorded attacks.
macOS Flaw Enables Users to Disable EDR, MDM Tools
A security flaw in macOS has been discovered that allows users to quietly disable crucial enterprise security tools, including EDR and MDM, without needing administrator privileges. This gap in endpoint security models could leave businesses vulnerable to attacks.
Gaslight Malware Exposes AI-Assisted Analysis Limits
Meet Gaslight, a sneaky new macOS malware that uses fake system-failure messages to trick AI-powered analysis tools into doubting themselves. Created by North Korea-aligned threat actors, this Rust-based implant is a clever and concerning threat to cybersecurity.
Mistic Backdoor Targets Multiple Sectors in KongTuke's Financially Motivated Attacks
Meet Mistic, a sneaky backdoor that's leaving a trail of financial chaos across multiple sectors, thanks to its ability to run quietly in memory with no digital fingerprints left behind. Its arsenal includes a range of remote-access capabilities, from file uploads and downloads to code execution, all designed to keep attackers in the driver's seat for the long haul.
UK School's Lax Network Security Exposes Sensitive Data
A 17-year-old student gained unrestricted access to a UK school's network, discovering sensitive leadership documents and being able to reset passwords, delete accounts, and even wipe the entire network. The alarming vulnerability was uncovered when the student connected their laptop to the school's Active Directory domain, which surprisingly required no administrator authentication.
US Seeks $67 Billion Defense Boost in $87.6 Billion Supplemental Request
The White House is seeking a massive $87.6 billion supplemental spending boost, with a whopping $67.1 billion dedicated to defense costs related to the war in Iran, in a bid to further secure the region and counter the regime's growing threats. This dramatic increase in defense spending comes on the heels of a major operation that successfully deterred a nuclear-armed Iran and crippled its regional influence.
ASIO Chief Warns of Interconnected Security Threats
ASIO Chief Mike Burgess has issued a stark warning: Australia faces a complex web of security threats that must be tackled simultaneously. He delivered this message to a packed room in Canberra, emphasizing the need for vigilance in the face of multiple, overlapping dangers.
Lockheed Secures $35 Billion THAAD Production Boost
Lockheed Martin is set to supercharge production of its Terminal High Altitude Area Defense (THAAD) interceptors with a whopping $35 billion contract, quadrupling output over the next seven years. This game-changing deal is a major win for the company and a significant boost to America's defense capabilities.
General Atomics Upgrades Ground Stations for MQ-9B Drone Compatibility
General Atomics is upgrading its Block 30 ground control stations to ensure seamless compatibility with its latest MQ-9B SkyGuardian and SeaGuardian drones, addressing a key concern for current MQ-9A operators. The company will fund the upgrade research and development and plans to begin flight testing by the end of the year.
Australia's Security Threats Converge as AI Compresses Risk Timeline
When Australia's critical infrastructure is disrupted, it will be a shock, but not a surprise - and with AI supercharging threats, that disruption may come sooner than we think. The warning signs are clear: AI is rapidly expanding the offensive toolkit, making threats more immediate, concurrent, and devastating.
Cisco SD-WAN Zero-Day Exploited for Root Access
A shocking new discovery reveals that a Cisco SD-WAN zero-day vulnerability, CVE-2026-20245, was exploited for root access at least two months before its public disclosure. This highly critical flaw, with a CVSS score of 7.8, allows attackers to execute arbitrary commands with elevated privileges.
Pentagon Unveils Quantum Strategy to Fortify Cryptography Defenses
The Pentagon is bolstering its defenses with a new quantum strategy, aimed at safeguarding its systems for decades to come, Chief Information Officer Kirsten Davies announced. This forward-thinking plan will help mitigate the risks of emerging quantum capabilities and modernize defense networks.
Hackers Exploit Cisco Zero-Day for High-Level Access at Telecom Provider
In a chilling cyberattack, hackers exploited a previously unknown Cisco zero-day vulnerability to gain unrestricted access to a major telecom provider's system, creating a rogue admin account with full control. The breach, detected in March, was carried out in two waves, allowing the attackers to infiltrate the provider's SD-WAN Manager devices.
ASIO Disrupts Nation-State Cyber Sabotage Targeting Australian Infrastructure
ASIO director general Mike Burgess revealed that nation-state hackers had infiltrated a critical Australian infrastructure provider's network, gaining login credentials to sabotage it at will. The alarming breach was thwarted thanks to ASIO's swift action and dedicated response.
Cisco Vulnerabilities Targeted in String of Exploits
Hackers are actively exploiting a recently patched Cisco vulnerability, CVE-2026-20230, using a clever chain of attacks that can grant them root privileges on compromised devices. This alarming exploit activity was uncovered by threat-intel company Defused, highlighting the urgent need for robust security measures.
DraftKings hacker sentenced to 18 months for $600,000 cyberattack
Meet Nathan Austad, a 21-year-old from Minnesota who pleaded guilty to masterminding a massive $600,000 cyberattack on DraftKings, compromising nearly 60,000 customer accounts with a clever alias and a crew of co-conspirators. He'll be serving 18 months for his role in the hack, which exploited weak passwords and left thousands of customers vulnerable.
Mandiant Exposes Cisco SD-WAN Zero-Day Attacks' Root Access Methods
Cisco's SD-WAN system was exploited in active attacks using a high-severity flaw, allowing hackers to create a rogue root account and take full control of targeted devices. This vulnerability, tracked as CVE-2026-20245, was triggered through a simple tenant-upload feature in the command-line interface.
Malicious Edge Extension Exploits Native Messaging for Malware Deployment
Beware of malicious Edge extensions that can deploy malware through native messaging, with attackers using social engineering tactics on Microsoft Teams to trick victims into installing fake updates. Once infected, victims are presented with a fake Outlook update page offering three options to deploy the Edgecution malware.
UK Industry Partners Miniaturize DragonFire Laser for Type 45 Destroyer Debut
The UK's naval industry is making strides in laser technology, with QinetiQ, MBDA, and Leonardo teaming up to miniaturize the powerful DragonFire laser system for its debut on a Type 45 destroyer by 2027. This innovative partnership is shrinking the hardware to make the high-energy laser more feasible for naval deployment.
Threats Expose Gaps in US Air-and-Missile-Defense Industrial Base
The US air-and-missile-defense system is struggling to keep up with today's threats, revealing gaps in real time, because its industrial base was designed for a bygone era. It's clear that we need a new approach, with more innovators and fresh ways to design, build, and deploy critical technologies like munitions and hypersonics.
MQ-28 Ghost Bat Drone Deploys in Major Pacific Combat Exercise
The MQ-28 Ghost Bat drone made its debut in a major Pacific combat exercise, demonstrating its cutting-edge capabilities as a force multiplier that can fly alongside crewed fighters and extend their reach. This milestone marks a significant step forward in human-machine teaming and showcases the US commitment to a free and open Indo-Pacific.
US Space Superiority at Risk as Acquisition Pace Lags
The battle for space superiority is heating up, with experts warning that the US is falling behind - and it's not just about being first, it's about control of the ultimate high ground that dictates success in every other domain, from air and sea to cyberspace. As one general put it, space operations are now vital to every military move, and the question is - can the US keep up?
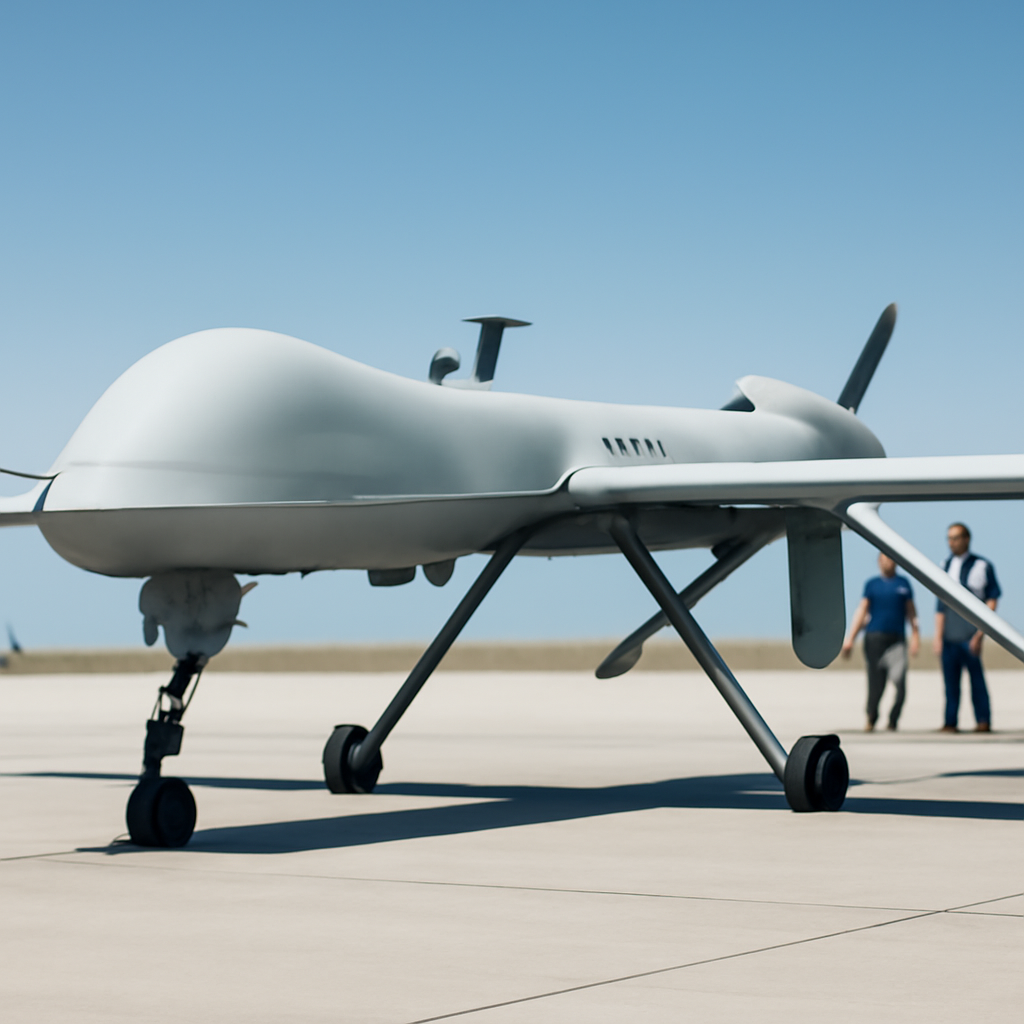
US Navy Still Flies MQ-1 Predators in Secret Test Role
The US Navy is secretly testing a fleet of 20 MQ-1 Predators, acquired from the Air Force in 2019 and rebranded as NMQ-1Bs, despite the aircraft's official retirement in 2018. These drones are being used for mysterious testing purposes at the Naval Air Warfare Center Weapons Division.
Governments Struggle to Secure Open-Source Software
The alarming reality is that years of underinvestment in open-source software security are catching up with us, with a new supply chain compromise emerging almost every week. A recent scan by Project Glasswing found over 6,000 high-risk vulnerabilities in popular open-source projects, but only a tiny fraction have been patched.