Tag: emerging threats
8355 articles
SharkLoader Targets Global Entities with Cobalt Strike Deployment
Kaspersky researchers have uncovered a sophisticated campaign, dubbed StrikeShark, where hackers exploited vulnerabilities like ProxyLogon to deploy SharkLoader malware and gain access to high-stakes targets worldwide. The attackers used multiple publicly disclosed flaws to compromise internet-facing services, hitting diplomatic entities, software vendors, and more.
Microsoft Disrupts Dual Cybercrime Tools in Novel Court Takedown
In a groundbreaking move, Microsoft led a global effort to dismantle two notorious cybercrime tools, Amadey and StealC, used by hackers to infect over 140,000 computers worldwide in just one week. This bold takedown marks a significant win in the fight against cybercrime.
Sen. Warren Probes Raytheon Exec's Ethics on Space Acquisition Nomination
Sen. Elizabeth Warren is pressing a Raytheon executive to promise strict ethics if he's confirmed to the Air Force's top space procurement office, citing concerns about impartiality due to his past ties to the defense contractor. She wants him to commit to a four-year recusal from matters involving his former employer.
CISA Warns of Active Exploitation of Lantronix EDS5000 Flaw
A critical code-injection flaw, CVE-2025-67038, has been discovered in Lantronix EDS5000 Series devices, allowing attackers to inject arbitrary OS commands with root privileges due to a lack of input sanitization in the HTTP RPC module. This vulnerability has a CVSS score of 9.8, indicating a high severity level.
Oman, IMO Unveil Evacuation Plan for Stranded Strait of Hormuz Ships
Oman and the International Maritime Organization (IMO) have teamed up to launch a safe evacuation plan for ships stranded in the Strait of Hormuz, a vital waterway for global trade. A temporary maritime corridor has been established, allowing vessels to transit safely with IMO coordination.
Malware Developers Embed Deceptive Text to Evade AI Analysis
Malware developers are getting sneaky, hiding their spyware behind a façade of disturbing text about nuclear and biological weapons to throw AI analysis off their trail. By embedding this decoy content, they're making it harder for automated systems to detect their malicious code.
Microsoft AI Disrupts Malware Operations in Novel Racketeering Suit
Microsoft is shaking up the fight against malware by harnessing the power of AI to disrupt cybercrime operations, as seen in a groundbreaking racketeering case that treats two separate malware operations as a single, unified threat. By combining AI analysis with a novel application of the Racketeer Influenced and Corrupt Organizations Act (RICO), Microsoft's Digital Crimes Unit is pioneering a new approach to tackling malicious software.
Law Enforcement Disrupts Amadey Malware Network, Recovers 27M Stolen Credentials
In a major cybercrime crackdown, international law enforcement agencies and private sector partners joined forces to dismantle the Amadey malware network, recovering a staggering 27 million stolen login credentials. This huge blow to cybercriminals was delivered between June 15-19, 2026, as part of Operation Endgame.
Europol Operation Disrupts StealC and Amadey Infostealers
In a major win for cybersecurity, a coordinated international effort has dismantled the operations of two notorious malware families, StealC and Amadey, freezing a whopping €41m in crypto assets of criminal origin. This significant disruption was made possible through the collaboration of Europol, Germany's Federal Criminal Police Office, J-CAT, and Eurojust.
Researchers Expose AI Browser Vulnerability to Credential Theft
Imagine a simple game trick that could convince AI-powered browsers to hand over your login credentials - a vulnerability researchers have now exposed, leaving users at risk. By creating a malicious web page that changes an AI agent's sense of reality, hackers can bypass safety guardrails and gain access to sensitive information.
Microsoft-Led Operation Disrupts Amadey, StealC Malware Networks
In a major win for cybersecurity, a Microsoft-led operation has successfully disrupted the networks behind Amadey and StealC malware, significantly increasing friction for cybercriminals and making it harder for attacks to succeed. This collaborative effort between law enforcement and private sector partners marks a crucial step forward in the fight against cybercrime.
CISA Warns of Actively Exploited Ubiquiti Flaws
The US Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning that hackers are actively exploiting security flaws in Ubiquiti UniFi OS devices, posing a significant threat to system security. Federal agencies have just three days to apply crucial updates or recommended fixes to avoid potential breaches.
Cordyceps Flaws Compromise 300+ GitHub Repositories
A newly discovered flaw, dubbed Cordyceps, has left over 300 GitHub repositories vulnerable to exploitation by unauthenticated users, allowing for code execution, credential theft, and supply-chain compromise. This critical weakness can be easily exploited, putting countless open-source projects at risk.
North Korea-linked Backdoor Exploits AI Triage Tools
When building AI triage tools, it's crucial to treat sample contents as potentially hostile input, not instructions, to prevent malicious manipulation. Experts warn that failing to do so can allow attackers to sneak hostile content into your model.
Social Engineering Attacks Target Service Desks
Service desks have become a prime target for cyber attackers, who often find it easier to manipulate staff into divulging sensitive information than to crack the technology itself. In a string of recent incidents, hackers have successfully impersonated employees to gain access to internal systems, as seen in the 2025 UK attacks on major retailers like Marks & Spencer, Co-op, and Harrods.
AI-Powered Adversaries Compress Cyberattack Timeline
In early 2026, the emergence of advanced agentic AI models marked a chilling new era in cyber threats, enabling attackers to compress the time between discovery and weaponization to mere minutes. This means that the window for detecting and responding to breaches may soon be shorter than the time it takes to finish a cup of coffee.
MuddyWater Exploits Ransomware Disguise for Cyber Espionage
The line between ransomware attacks and nation-state espionage is rapidly blurring, as cyber groups like MuddyWater now disguise their operations as financially motivated ransomware attacks to further their strategic objectives. MuddyWater, linked to Iran's Ministry of Intelligence and Security, has been caught posing as the Chaos ransomware group in a deliberate campaign.
Mistic Backdoor Enables Long-Term Access in Ransomware Attacks
Cyber attackers have deployed a sneaky backdoor called Mistic, allowing them to maintain long-term access to infected systems during ransomware attacks, all while staying remarkably under the radar. This stealthy threat uses clever tactics like running payloads in memory and mimicking legitimate Microsoft security tools to evade detection.
US Seizes Huione Cloud Account Tied to $31 Billion Cyber Scam Laundering
The US Department of Justice has seized a cloud account linked to a staggering $31 billion cyber scam laundering operation, disrupting a vast online marketplace for fraud and money laundering. This massive crackdown targeted HuiOne Group, a Cambodia-based company accused of helping scammers launder billions through its subsidiaries.
AI Enables Faster, Cheaper Cyber-Attacks
Cyber attacks just got a whole lot faster, cheaper, and sneakier thanks to AI, which is now a key player in the cybercrime world, enabling attackers to launch more sophisticated and elusive threats. ReliaQuest reports that AI is revolutionizing the attack workflow, making it easier for attackers to scale, customize, and slip past traditional defenses.
UK Museums Exposed to Rising Cybersecurity Threats
The UK's cultural treasures are under threat from rising cybersecurity risks, with a recent report criticizing the Department for Culture, Media and Sport for being reactive rather than proactive in protecting national galleries and museums. This vulnerable stance puts priceless artifacts and historical exhibits at risk of being compromised.
Cisco Unified CM Flaw Exploited in Active Attacks
Hackers are actively exploiting a high-severity flaw in Cisco Unified CM, tracked as CVE-2026-20230, which allows them to send malicious HTTP requests and potentially take control of affected devices. This vulnerability, with a CVSS score of 8.6, could enable attackers to write files to the underlying operating system and escalate their privileges.
US-UK Nuclear Pact Bolsters Mutual Deterrence
The US-UK nuclear partnership is a two-way street, with Washington gaining tangible technical, operational, and strategic advantages from the collaboration, just as London has benefited from US support for over 65 years. This mutual deterrence pact serves US interests just as much as British ones, experts argue.
Iranian Drone Swarm Poses Questions After F-15E Downing
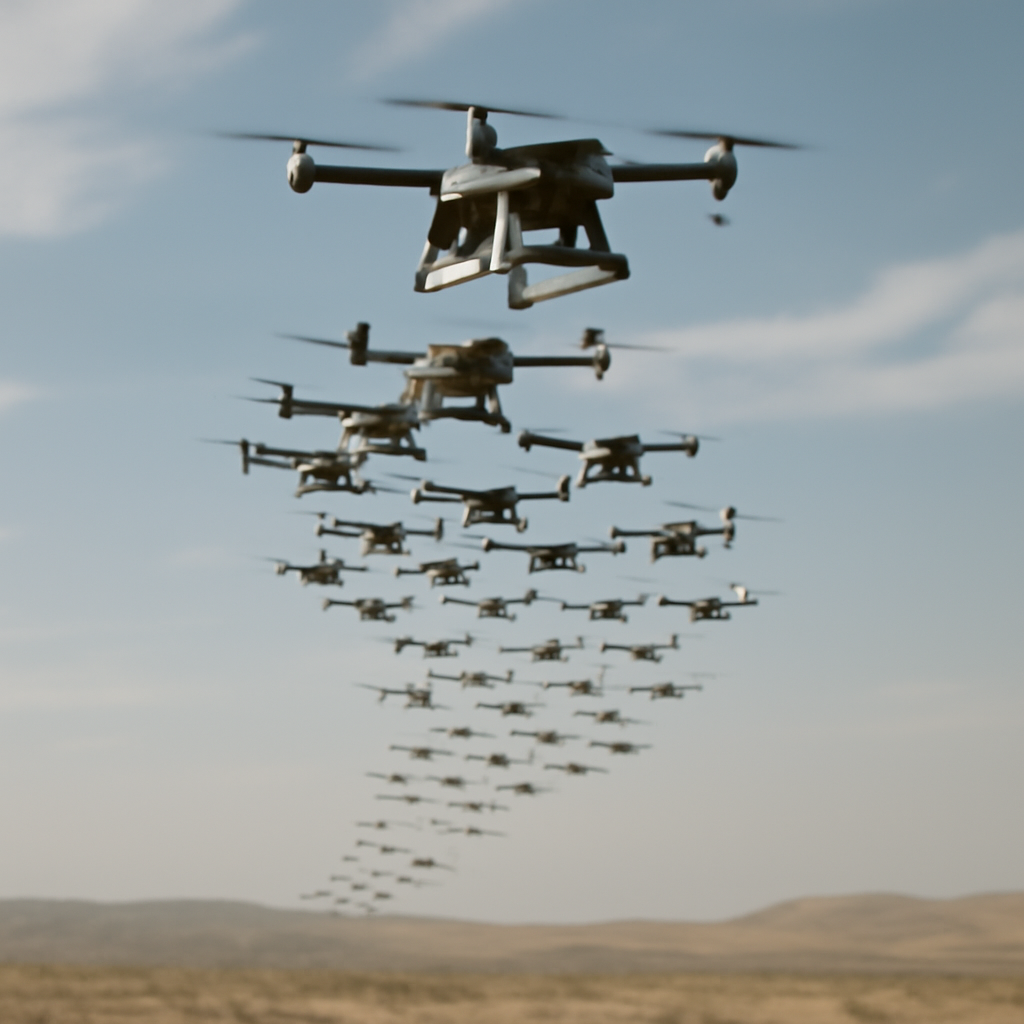
An F-15E pilot described a chilling scene before ejecting from his downed jet: a swarm of Iranian drones moving in unison, resembling a jellyfish with smaller drones clustered beneath larger ones like legs. This unprecedented encounter has raised more questions than answers.