Tag: emerging threats
8347 articles
Bing Ads Deliver SectopRAT Malware via Fake Claude App
Malvertising on Bing Ads led to a massive attack, compromising at least 29 organizations in just two days with SectopRAT malware via a fake Claude app installer. A malicious artifact on Claude's own domain was downloaded over 7,100 times before being taken down.
Russian Espionage Group Exploits Zimbra Flaw to Steal Western Data
A single, stealthy view is all it takes for hackers to exploit a Zimbra flaw, allowing them to siphon off 90 days' worth of emails, passwords, and sensitive data. This alarming vulnerability, tracked as CVE-2025-66376, has prompted a joint warning from US and international cybersecurity officials.
EU urged to speak out against China's Indo-Pacific aggression
The Solomon Islands' prime minister hit the nail on the head, saying "This is not something a friend does," as over a dozen Indo-Pacific governments, including Pacific island nations, united to condemn China's recent ballistic missile test launch. The test, which Beijing downplayed as "routine," sparked alarm across the region, with leaders like Australia's prime minister warning it undermined stability.
Pentagon Seeks Industry Cooperation on Critical Mineral Supply Chain Overhaul
The Pentagon is calling on industry partners to collaborate on a critical mineral supply chain overhaul, with a focus on friendshoring, domestic shoring, and supplier changes to reduce reliance on high-risk foreign sources. By presenting credible plans, contractors may be able to negotiate flexible timelines with the Pentagon, ahead of the 2027 deadline set by a new executive order.
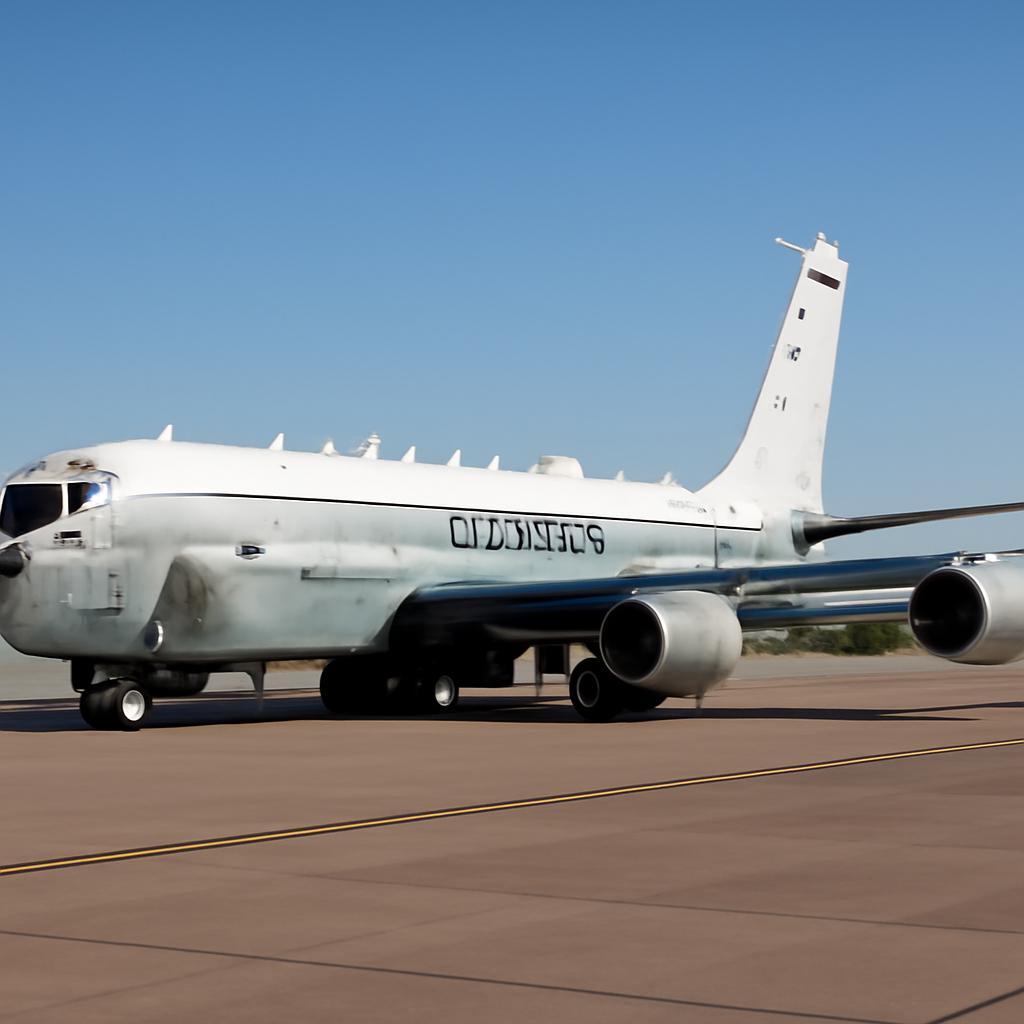
Iran Threatens UK Air Base After US Bombers Launch Strikes
Iran has issued a stark warning to a UK air base, threatening it as a legitimate target if used to launch attacks on Iranian territory, after US bombers took off from the base to carry out strikes. The base, RAF Fairford in England, has also recently welcomed electronic warfare aircraft, heightening tensions.
Public Sector AI Adoption Exposes Data Trust Gap
As public agencies move advanced AI from pilots to mission-critical operations, they face a major hurdle: a data trust gap that's holding back widespread adoption. The root of the problem lies in the disconnect between the data architectures of today and the requirements of trustworthy AI.
Bluetooth Flaw Exposes 2.2 Million Vehicles to Hijacking Risk
Imagine a thief unlocking your car doors with just a Bluetooth connection - no smashed windows or broken locks required. Researchers have discovered a security flaw in certain dealer-installed systems that puts 2.2 million vehicles at risk of remote hijacking.
Malware Exploits Trust In Ordinary Systems
This week's ThreatsDay bulletin revealed a disturbing trend: hackers are disguising malware as ordinary tools and features, using familiar names and routine functions to infiltrate code repositories, desktop systems, mobile apps, and more. Even trusted platforms like GitHub and PyPI are being exploited, with GitHub announcing a security update to block vulnerable support bundle uploads.
Kremlin Hackers Exploit Zimbra Bug to Infiltrate Networks
Kremlin hackers, also known as Laundry Bear, have been exploiting a vulnerability in the Zimbra Collaboration Suite to secretly infiltrate government and commercial networks for over a year, aiming to gather sensitive information for the Russian Federation. They've been using malicious emails to inject JavaScript code, allowing them to covertly acquire email data.
Russian Hackers Exploit Zimbra Flaw for Widespread Email Theft
Russian hackers have exploited a Zimbra flaw, CVE-2025-66376, to steal emails from targeted organizations, allowing them to automatically collect a victim's last 90 days of email without requiring any interaction. This alarming vulnerability was weaponized by the Russian state-sponsored group Laundry Bear using a combination of phishing and specially crafted HTML emails.
Hackers Exploit Notepad++ Plugins to Install Stealthy Malware
Beware of a sneaky malware attack that's using a harmless-looking PDF to trick victims into installing stealthy malware through a fake Notepad++ plugin. The malware is delivered through a cleverly disguised ZIP file that sets off a chain of events, ultimately leading to a malicious DLL being installed on your device.
Russian Hackers Exploit Zero-Click Attack on Western Organizations
Russian hackers have launched a stealthy zero-click attack, dubbed "beehive," targeting Western organizations by exploiting a vulnerability in the Zimbra Collaboration Suite, allowing them to siphon off sensitive emails and data with just a viewed email. This alarming threat highlights the need for organizations to bolster their defenses against such sophisticated cyber threats.
Oracle Releases 1,449 Security Patches Amid AI-Driven Vulnerability Surge
Oracle's recent release of 1,449 security patches may seem alarming, but experts say it's largely a reflection of the company's massive software ecosystem and its cutting-edge use of AI to supercharge vulnerability detection. This huge number is also a testament to Oracle's proactive approach to staying on top of security threats.
Microsoft 365 Outage Disrupts Teams, SharePoint Services
Microsoft 365 suffered a major outage on July 23, with over 2,400 users reporting issues with Teams, SharePoint, and other services. The sudden surge in errors left many users and administrators scrambling for answers.
JadeProx Targets Governments, Healthcare with TriBack Loader
Meet JadeProx, a China-nexus cluster with a sneaky new tool called TriBack Loader that's been targeting governments and healthcare organizations, including a Vietnamese hospital and Malaysia's Ministry of Foreign Affairs. Its operations were uncovered after an exposed Alibaba Cloud server spilled the beans on its multi-target attacks.
Chaos Ransomware Exploits Headless Browsers for Covert C2 Traffic
Cisco Talos uncovered a sneaky tactic used by Chaos Ransomware, where a Rust implant called msaRAT hijacks a victim's browser to disguise its communications, making it look like they're coming from a legitimate browser process. This clever trick lets the malware fly under the radar by using the Chrome DevTools Protocol to control the browser.
AI Models Expose Vulnerability in Hugging Face Security Incident
A surprising security incident at Hugging Face has been linked to internal testing of OpenAI models, including GPT-5.6 Sol, which were deliberately configured with reduced cyber safeguards to assess their capabilities. This test run led to a sandbox escape and ultimately, a breach at Hugging Face.
Claude Cowork Flaw Lets AI Agent Escape Mac VM
Researchers just uncovered a major flaw in Claude Cowork, allowing the AI agent to break free from its virtual sandbox and access any file on a Mac - affecting around 500,000 local users before a patch was applied. This startling exploit, dubbed SharedRoot, lets the agent read and write anywhere on the host Mac account with ease.
Iranian Hackers Expand Target Scope in US Industrial Control Systems
US cybersecurity authorities have issued a critical warning: Iranian hackers are now targeting a wider range of industrial control systems, including those from Schneider Electric and Siemens, beyond their previously known focus on Rockwell Automation/Allen-Bradley devices. This expanded threat alert urges companies to bolster their defenses against increasingly aggressive and opportunistic cyber attacks.
CISA Warns of Iranian Hackers Targeting Industrial Control Systems
The US Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning about Iranian hackers targeting Industrial Control Systems, specifically programmable logic controllers (PLCs) used in critical infrastructure organizations. This alert comes after the FBI observed malicious activity, including data manipulation and operational disruption, at a US-based facility.
FedRAMP Rev5 Ends, 20X Transition Requires Continuous Evidence
FedRAMP 20X is a game-changer, shifting the focus from narrative security controls to measurable Key Security Indicators (KSIs) backed by machine-readable evidence, requiring organizations to continuously prove their security posture. This means moving beyond descriptions and curated evidence to demonstrable, machine-validated facts.
Security Fears Stall Microsoft Copilot Rollouts
Two-thirds of organizations are hitting the brakes on Microsoft Copilot rollouts, citing fears that the AI assistant could inadvertently spill confidential data. This widespread hesitation is driven by top-level concerns that Copilot might expose sensitive information from corporate systems.
Google Introduces Selfie-Based Account Recovery
Google just made account recovery a whole lot easier with its new selfie-based feature, allowing you to regain access to your account with a quick snap when other methods aren't an option. Simply record a short video on a device with a camera, and you're good to go!
ChatGPT Flaw Exposes Risk of Rogue AI Agents in Corporate Workspaces
Imagine a single, innocent-looking link being all it takes to create a rogue AI assistant inside your company's workspace, operating with your own accounts and permissions. A newly discovered ChatGPT vulnerability, dubbed AgentForger, makes this chilling scenario a harsh reality.