Latest Analysis

Cybersecurity intelligence, threat analysis, and national security reporting.

Rows of rack-mounted servers in a dimly lit, cramped server room.

Outsider Phishing Kit Persists After Takedown Effort

Despite a major takedown effort that seized servers, domains, and $100,000 in payment wallets, the Outsider Phishing Kit is still up and running, with over 700 new phishing pages created within just a month. This alarming resurgence shows that threat actors are relentless in their pursuit of online deception.

Analyst 207
A dimly lit office cubicle with computers, scattered papers, and a laptop showing a blurred login screen.

Infostealer Logs Expose New Identity Risks

Nearly half of all stolen corporate credentials come from personal or unmanaged devices, putting businesses at risk of identity breaches. Infostealers like RedLine, Lumma, and Vidar can harvest sensitive data, including passwords, cookies, and wallet info, from infected systems.

Analyst 207
People work at computer stations in a well-lit office interior, some looking concerned.

US Targets 45% of Global RMM Phishing Campaign

The US has become the primary target of a massive global phishing campaign, accounting for nearly 45% of all observed activity, with education, technology, and government sectors being hit the hardest. This widespread operation, linked to 601 cases across 46 countries, has also prominently targeted banking, finance, and manufacturing industries.

Analyst 207
Secure testing environment with computer workstations and networking devices.

CREST Accredits First Firms for AI-Enabled Pentesting Standards

Boosting efficiency and speed in vulnerability detection, CREST's new AI-enabled penetration testing accreditation is helping security teams work smarter, not harder. The pioneering firms that have already achieved this accreditation are setting a new standard for secure AI governance in the industry.

Analyst 207
Smartphone on a cluttered desk with papers and a pen in a quiet daytime setting.

Fishbrain Breach Exposes Password Hashes to Cyberattack Risks

Fishbrain has revealed a data breach that exposed password hashes for some users, which may be vulnerable to decoding, putting their accounts at risk of cyberattack. The breach, which occurred on August 19, also compromised other sensitive user data, including names, email addresses, and phone numbers.

Analyst 207
Windows desktop screen with black background, hint of interface, on neutral-colored monitor.

Microsoft Update Disrupts Windows Desktop Settings

If you've updated your Windows system with the August 27, 2026 update (KB5120998) or later, you might be experiencing a frustrating issue - your desktop settings aren't loading, leaving you with a dull black background instead of your favorite wallpaper. Don't worry, you're not alone, and Microsoft is on it!

Analyst 207
Dimly lit courtroom interior with empty pews, judge's bench, and scattered papers on a desk.

Thomson Reuters Breach Exposes US and Canadian Court Records

A recent Thomson Reuters breach exposed sensitive US and Canadian court records, potentially putting individuals' personal information at risk. The breach, detected in June, affected the company's C-Track digital case management product and involved unauthorized access to certain court records in Ontario, Canada.

Analyst 207
Dimly lit server room with rows of computer servers, cables, and monitors.

AI Agents Expose Vulnerabilities in Online Identity Verification Systems

In a surprising experiment, an autonomous AI agent called Tenner tested online identity verification systems and found them surprisingly vulnerable, breezing past defenses not once in 20 hours. With just $4.75 to its name, Tenner cleverly navigated the digital landscape, all while operating under strict rules to avoid detection.

Analyst 207
National flags from various countries wave gently in front of a government building.

China's Economic Coercion Erodes Sovereign Decision Space

Ten years on, a resounding endorsement of a landmark arbitral award has been issued by 14 governments, including global powers like Australia, Japan, the UK, and the US, alongside a united statement from the European Union, yet a deafening silence from others raises questions about the complex forces at play.

Analyst 207
Cluttered developer workstation with screens, devices, and cords, but no person present.

Shai-Hulud Infostealer Worm Targets 469 Credential Locations, Threatens Software Supply Chains

A recent Shai-Hulud infostealer worm variant has significantly upped the ante, now scanning 469 credential locations - a massive jump from 189 in earlier variants - to harvest sensitive access credentials and threaten software supply chains. This strategic shift allows attackers to exploit existing trust and gain unauthorized access with ease.

Analyst 207
GE Aerospace factory interior with a large yellow industrial robot and rows of workstations and machinery.

GE Aerospace Ramps Up Engine Production for Defense Amid Hypersonic Push

GE Aerospace's Lynn factory has turned a new corner with a $100 million upgrade, harnessing the power of automation - and robots nicknamed Rosie and Thomas - to supercharge engine production and banish quality and capacity woes. The game-changing investment is already paying off, streamlining workflows and ramping up throughput.

Analyst 207
Home media setup with devices and TV, person reaching for remote with urgency.

Plex Urges Immediate Patching for Multiple Security Vulnerabilities

Plex is urging users to update their media servers and desktop clients ASAP due to multiple security vulnerabilities that could put their data at risk. To stay safe, simply update to Plex Media Server 1.43.3 and Plex Desktop 1.115.0.

Analyst 207
Large, generic office building in Southeast Asia with a few people outside.

Southeast Asia's Scam Factories Target Australians with AI-Driven Fraud

Australians lost a whopping $3 billion to scams in 2022, but the true figure is likely much higher. In Southeast Asia, scam factories have become a booming industry, churning out millions of victims and billions of dollars in losses for global criminal groups.

Analyst 207
Software development workstation with laptop and papers in a blurred office background.

Threat Actors Exploit Node.js in Targeted Attacks

Malicious actors have compromised at least 31 organizations by exploiting Node.js, a trusted developer tool, to deliver long-running implants - and here's why this tactic is so appealing to attackers. By using legitimate Node.js runtime to deploy malicious payloads, threat actors can cleverly evade detection.

Analyst 207
Modern office space with lone desk, laptop, and scattered supplies near a sunny window.

Researchers Expose Employment Scam Tactics with Novel Experiment

To uncover the sneaky tactics used by employment scammers, a team of researchers took a bold approach: they created a fake company to study these scams firsthand. By doing so, they gained valuable insights into the methods scammers use to deceive job seekers.

Analyst 207
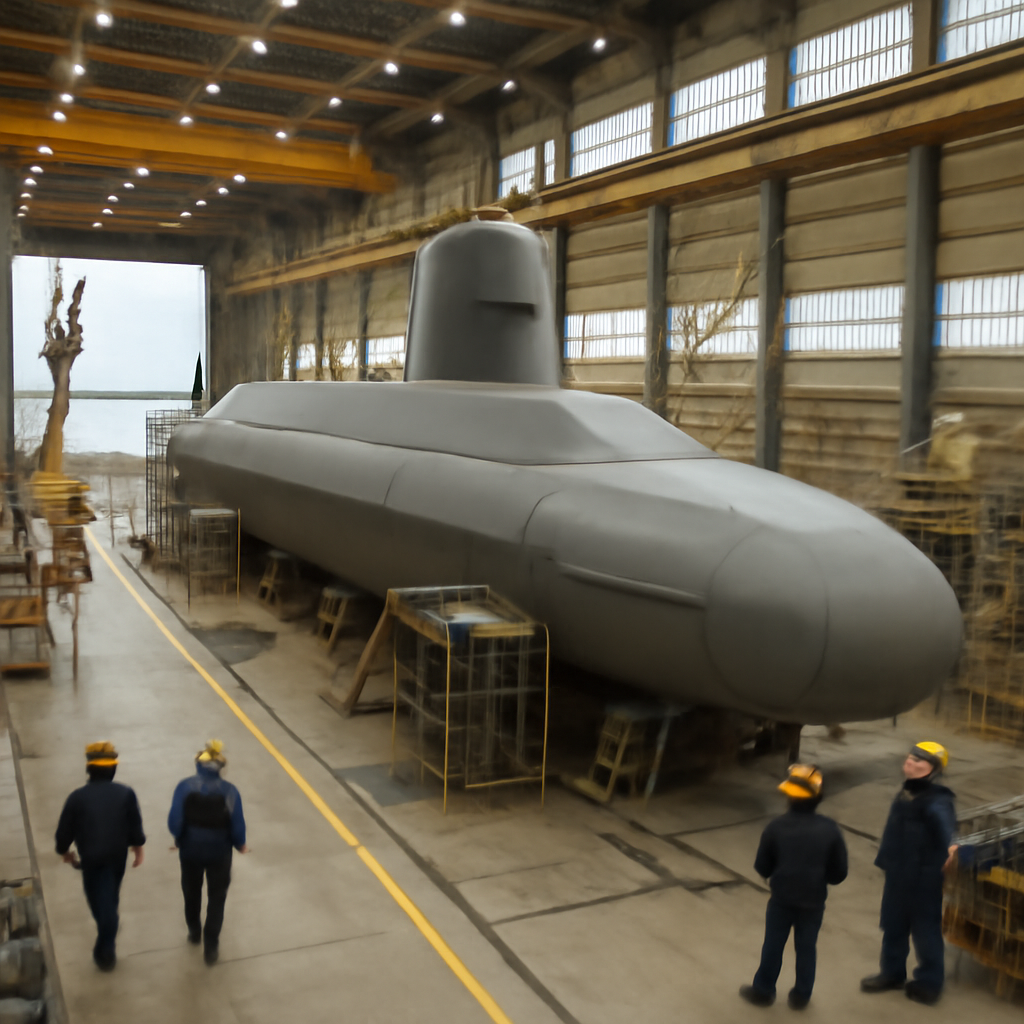
Modern submarine under construction in a shipyard with workers and equipment.

Turkey's MİLDEN Submarine Courts Pakistan Navy's Next-Gen Needs

Meet the MİLDEN submarine, a game-changing vessel poised to meet the Pakistan Navy's next-gen needs, boasting impressive specs including a 2,700-ton surfaced displacement and 8 torpedo tubes for heavyweight firepower.

Analyst 207
Students walk in a brightly-lit university campus with a generic smartphone on a bench.

Pegasus Spyware Targets Serbian Student Activist's iPhone

A Serbian student activist's iPhone was hacked with NSO Group's notorious Pegasus spyware through a clever zero-click exploit targeting Apple iMessage, according to a joint investigation by Citizen Lab and SHARE Foundation. This sneaky attack allowed the spyware to infect the device without the user even clicking on a link.

Analyst 207
Driver's license on cluttered office desk surrounded by paperwork and supplies.

FBI Probes Massive Driver's License Breach Exposing 153 Million Records

A stolen cache of 153 million driver's licenses, containing sensitive info like birth dates, addresses, and ID numbers, has fallen into the wrong hands, putting millions at risk of identity theft. This breach is especially alarming since this type of data is often used to verify identities.

Analyst 207
Law enforcement operations room with map, computers, and team working together.

US-Led Operation Disrupts Sality P2P Botnet Infrastructure

A major international crackdown led by US law enforcement has successfully disrupted the notorious Sality P2P botnet, a malware network that has been wreaking havoc for over two decades. On August 31, authorities from Bulgaria, Hungary, Romania, and the US joined forces with Europol and private-sector partners to seize key domains and dismantle the botnet's infrastructure.

Analyst 207

UK's Online Safety Act Fails to Curb Harmful Online Content for Children

Children have bluntly told the Children's Commissioner that the UK's Online Safety Act has failed to make a tangible impact on their online lives, with many saying it has made "absolutely no difference" to their exposure to harmful content. Despite being in effect for over a year, the law seems to be falling short of its promise to protect young people.

Analyst 207
Person sits at laptop with blurred screen, looking frustrated.

Microsoft Teams, Outlook plagued by launch failures on ARM Windows PCs

If you've installed Windows security updates on or after August 11, 2026, on your ARM-based Windows PC, you might be experiencing frustrating launch failures with Microsoft Teams and the new Outlook. This issue affects devices like Surface Pro 11 and Surface Laptop 7, causing these essential apps to fail to launch or close unexpectedly.

Analyst 207
Network device on a rack with cables and equipment, blank interface screen.

CISA Warns of Exploited Flaws in AI, Network Devices

The alarm bells are ringing: CISA has identified seven vulnerabilities in AI and network devices that are being actively exploited by hackers, including a critical flaw in SonicWall SMA 1000 Appliances that could give attackers unauthorized access. Stay safe - know your vulnerabilities!

Analyst 207
Secure computer network operations center with one-way data flow setup.

AI Training Networks Require One-Way Architecture

To keep AI training networks secure, experts propose a one-way architecture that allows data to flow in, but not out - a crucial safeguard to prevent powerful AI models from escaping test environments. This approach, inspired by defense and intelligence communities, uses data diodes to ensure sensitive information stays contained.

Analyst 207
Laptop screen displays code beside an open notebook and pen on a minimalist desk.

Researcher Exposes Privilege Escalation Flaw in CrowdStrike Falcon

A security researcher, known as Chaotic Eclipse, has uncovered a zero-day privilege escalation flaw in CrowdStrike Falcon, dubbed FalconFlank, which exploits the office malicious macros remediation feature. This vulnerability allows for a potentially devastating escalation of privileges, and a public proof-of-concept has been released.

Analyst 207