[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
Threat actors have upgraded their game, leveraging AI frameworks to supercharge credential theft and drastically cut the time between initial compromise and large-scale attacks. Gone are the days of simple, one-off AI prompts - now, attackers are orchestrating entire attacks with sophisticated multi-agent frameworks.
A critical vulnerability in FreeIPA, tracked as CVE-2026-76578, allows an unauthenticated client to create admin credentials by exploiting a chain of defects that lets them create a Kerberos identity and join the administrators group. This flaw, with a preliminary CVSS score of 9.8, was fixed in FreeIPA version 4.13.4.
Meet the sneaky THost9 Android RAT that's exploiting exposed ADB services to spread its reach - and it can scan a massive 65,025-host range with ease.
Meet BengalSEO, a notorious group that's been secretly manipulating Bing search results with sneaky Black Hat SEO tactics since at least 2015, luring victims into malware and tech-support scams. They're masters of creating fake support pages that look legit, but actually serve as traps.
Adobe just patched a critical zero-day flaw, CVE-2026-75650, that's been exploited to deploy a Rust backdoor, known as StyleSmuggler, targeting Adobe Commerce merchants - and it's crucial you update ASAP to avoid arbitrary code execution. This severe vulnerability has a CVSS score of 10.0, so don't wait to secure your site.
Security researchers just uncovered a massive phishing operation targeting Microsoft 365 credentials, with a staggering 5,137 compromised records and 3,331 unique victim IPs exposed. The researchers even gained admin access to the operation's control panel, revealing a vast network of 42 VPS nodes used to carry out the attacks.
A data breach at Trezor has just gotten much worse, with 81,000 customers now confirmed to be affected, having their personal details including names, emails, and addresses exposed. This significant increase from the initial report puts even more users at risk of phishing scams and other malicious activities.
The UK is set to supercharge its space capabilities with a whopping £7.8 billion investment, boosting satellite launches, threat detection, and everyday services while creating skilled jobs and driving growth. This bold move is expected to unlock a new era of opportunities in space, benefiting industries and citizens alike.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Grindr is shelling out $35 million to settle a UK lawsuit that claimed the company shared users' personal info, including their HIV status, with third parties without their consent. The settlement, which doesn't admit any wrongdoing, resolves a class-action suit filed on behalf of over 10,000 users.
A staggering 220 million traveler records, including passenger and crew information, were left vulnerable due to a misconfigured system linked to a Vietnamese organization. This massive data leak, discovered by Kinryū Labs, exposed sensitive information spanning nearly a decade.
A new partnership between Aurelius Capital, the state of Lower Saxony, and Volkswagen AG is set to transform the former VW site in Osnabrück into a cutting-edge defense hub, securing the location's future and creating a center of excellence for security and defense solutions. This bold move is a strategic win for the region, with Minister-President Olaf Lies hailing it as a genuine future perspective for the site.
Imagine a future that's already here, but only in glimpses - and discover how science fiction can help policymakers and analysts better prepare for what's to come. By challenging traditional predictive methods, science fiction offers a powerful tool to widen our aperture and anticipate the uneven arrival of future challenges.
The Royal Australian Air Force faces a pressing challenge: how to produce more combat-ready pilots without breaking the bank with costly frontline fighter jets that run A$60,000 per flight hour. Could turboprops offer a smart solution to boost pilot training capacity?
Sweden is supercharging its rocket artillery capabilities with a $732 million deal for Lockheed Martin's HIMARS system, which brings game-changing long-range precision firepower to the battlefield. The contract includes over ten launchers and a substantial stockpile of ammunition, with deliveries set to start in 2027.
Meet PEEP, a sneaky post-exploitation toolkit that disguises itself as a harmless bookmarks extension in Chrome and Edge, allowing hackers to execute commands on compromised devices. It requires prior admin access to install, cleverly bypassing security checks to forge a sense of legitimacy.
A newly discovered zero-day vulnerability, dubbed "StyleSmuggler," is being exploited in the wild to install a stealthy Linux backdoor on over 160,000 Magento and Adobe Commerce sites, including 14,000 of the top 1 million sites. This alarming attack has already hit a target running the latest security updates, leaving many sites vulnerable.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
Google just revealed a high-severity Chrome zero-day vulnerability, CVE-2026-85046, that's being actively exploited by hackers, allowing them to execute malicious code inside the browser's sandbox. This type confusion bug in Chrome's V8 engine was reported by researcher Salvatore Gulizia on August 4, 2026.
Beware of fake IT calls that can trick you into giving away your Microsoft 365 login credentials - scammers are using a clever vishing scheme to steal account details and hold them for ransom. It starts with a convincing phone call from someone claiming to be from IT, directing you to a fake authentication page.
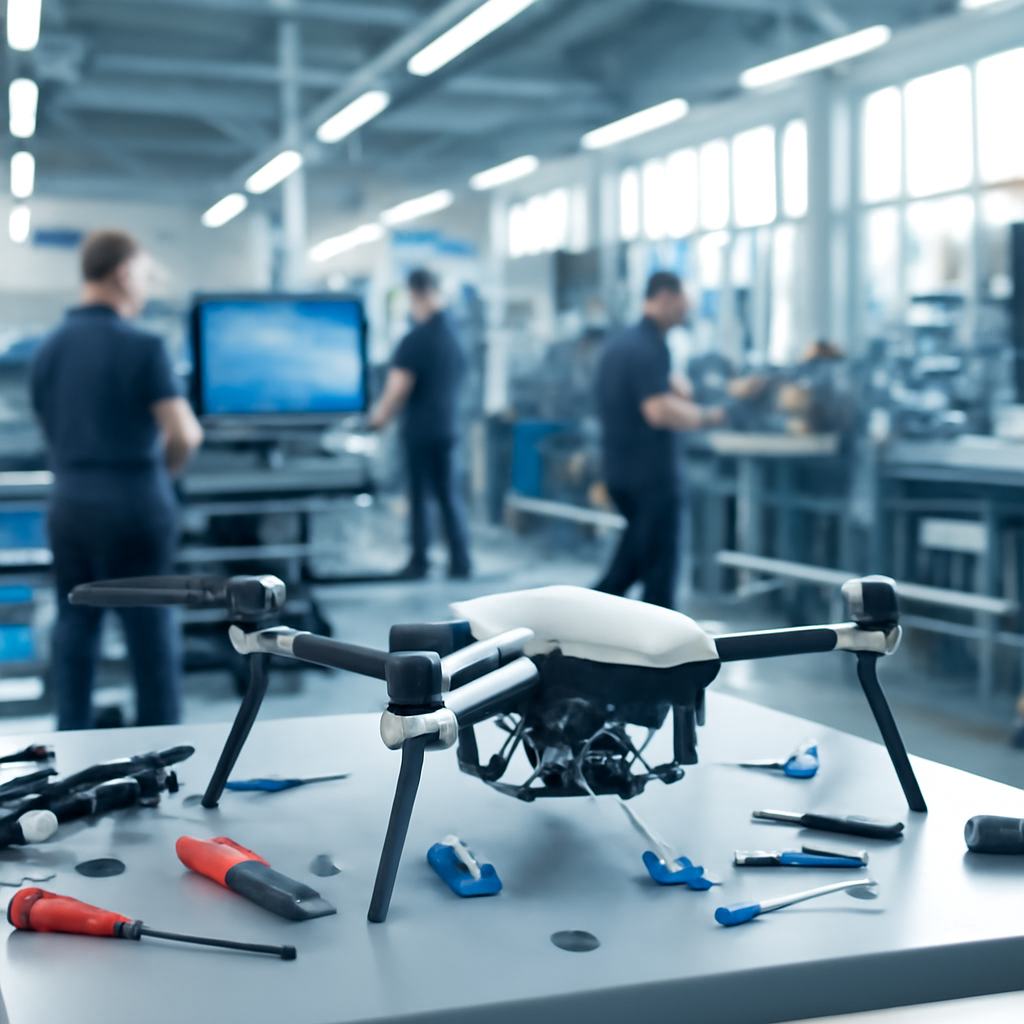
Pakistan's Heavy Industries Taxila (HIT) has just unveiled a cutting-edge drone production facility, marking a major milestone in the country's military tech advancements. The state-of-the-art Unmanned Aerial Systems Factory is set to churn out a range of innovative drones, from surveillance models to loitering munitions.
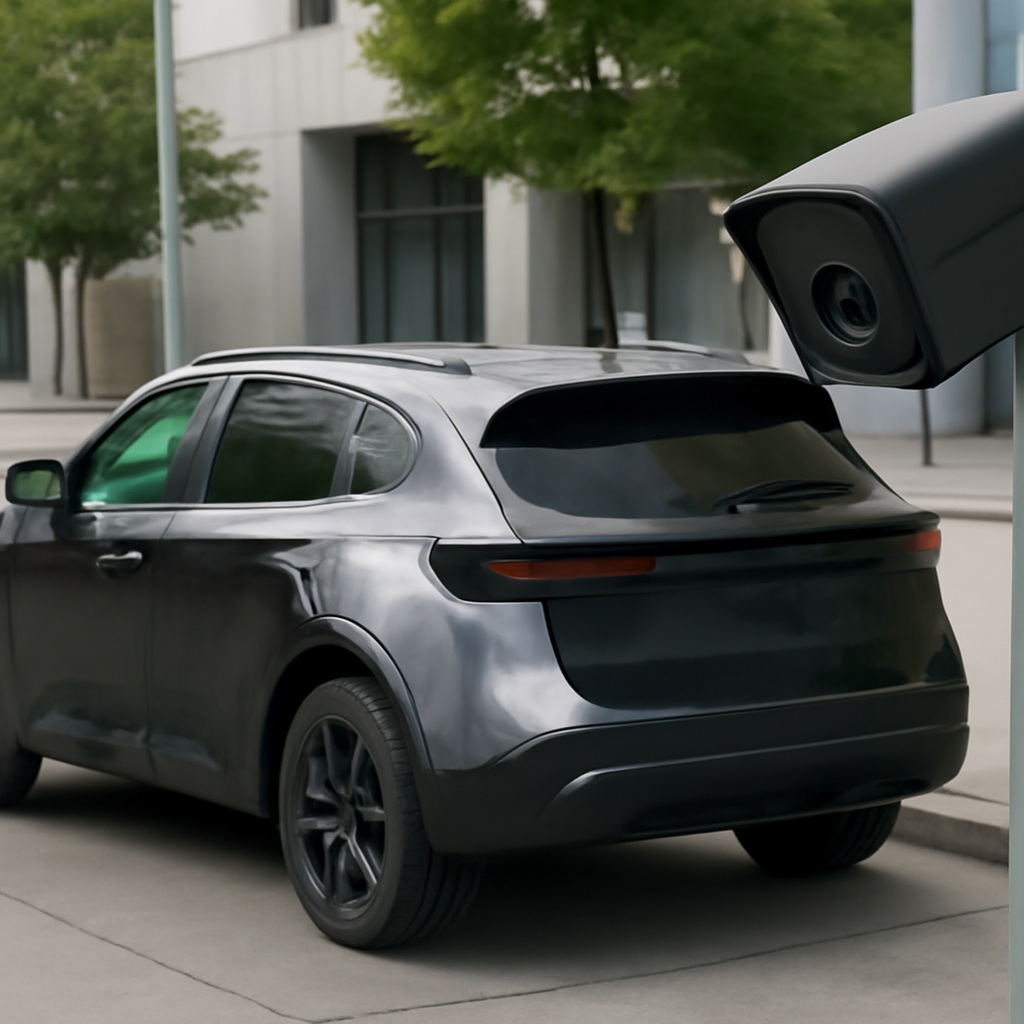
A recent test has raised eyebrows, showing that a specially designed camouflage can evade detection by Flock cameras and Axon body cameras, sparking questions about the effectiveness of other surveillance technologies. Will upgrades to these systems be enough to catch visually altered vehicles, or will new methods be needed to stay one step ahead?
As the UN General Assembly convenes, a pressing question looms: will institutions like the UN assert their authority to interpret their own rules, or will external forces dictate the terms? The fate of Taiwan's status hangs in the balance, tied to the interpretation of Resolution 2758.
BigBear 2.0, a sneaky phishing-as-a-service operation, has compromised 258 companies by bypassing multi-factor authentication (MFA) for Microsoft 365 users worldwide, swiping 5,137 credential records in the process. This cunning attack used an adversary-in-the-middle approach to intercept passwords, MFA tokens, and session cookies, allowing hackers to hijack authenticated sessions with ease.
Stay vigilant, especially on holidays like Labor Day - even company staff aren't immune to unexpected messages, as Nightwing's CEO recently proved when a message meant for employees somehow made its way to The Register. This incident serves as a reminder to always be cautious when receiving unsolicited messages.
Employees are increasingly turning to AI tools outside of company-approved systems, a phenomenon known as "shadow AI," which poses significant security risks. A staggering 71% of UK employees have already admitted to using unauthorized AI tools at work.