[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
Researchers at Check Point found that a sneaky instruction in a ChatGPT conversation can secretly siphon off sensitive data from connected Gmail accounts, sending it to an attacker's hidden channel without raising any red flags. This covert hack can even exfiltrate chat history and files, putting users' private info at risk.
Poland and Canada are taking their defense partnership to the next level with a new pact that cements their commitment to joint exercises, military training, and stronger ties. The agreement was sealed by Poland's Minister of National Defence, Władysław Kosiniak-Kamysz, and his Canadian counterpart, David J. McGuinty, ahead of a major defense trade show.
Security has taken center stage in the world of videoconferencing, with 31% of businesses now prioritizing it over price and quality when selecting collaboration products. Top security concerns include cyberattacks, device compliance, and risky employee behavior.
Australia and Japan are forging a powerful model for middle-power cooperation, leveraging their combined economic, political, and security strengths to drive institution-building in the Indo-Pacific region. By championing principles like the rule of law, open markets, and freedom from coercion, these two leading democracies are setting a compelling example for others to follow.
Meet the Kessel Run team, the US Air Force's elite unit tasked with delivering cutting-edge operational air power to protect and defend the nation. Led by Col. Richard Lopez, this innovative team is revolutionizing the way the Air Force approaches modernization with a bold, modern approach.
Big news: CISA is cutting back on free cybersecurity resources for critical infrastructure operators, leaving many in the security community scrambling to adapt. Recently touted as a go-to solution, these now-retired tools included Cyber Resilience Reviews and Ransomware Readiness Assessments.
In a surprise move, hackers claiming to be "whitehats" returned a whopping 3,400 bitcoin, valued at $265 million, to the Liquid Federation, leaving $47 million still in dispute. The mysterious intruders made their move on September 7, sending the funds back after a daring heist that stole nearly 4,000 bitcoin from the Liquid Network.
If you've installed the August 2026 Windows security update on your Windows Server 2016 system, you might be experiencing recurring application errors due to a compatibility issue with the CompatTelRunner.exe process. This error can occur when the Compatibility Appraiser diagnostic service is enabled, causing frustrating Application Error events with Event ID 1000.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment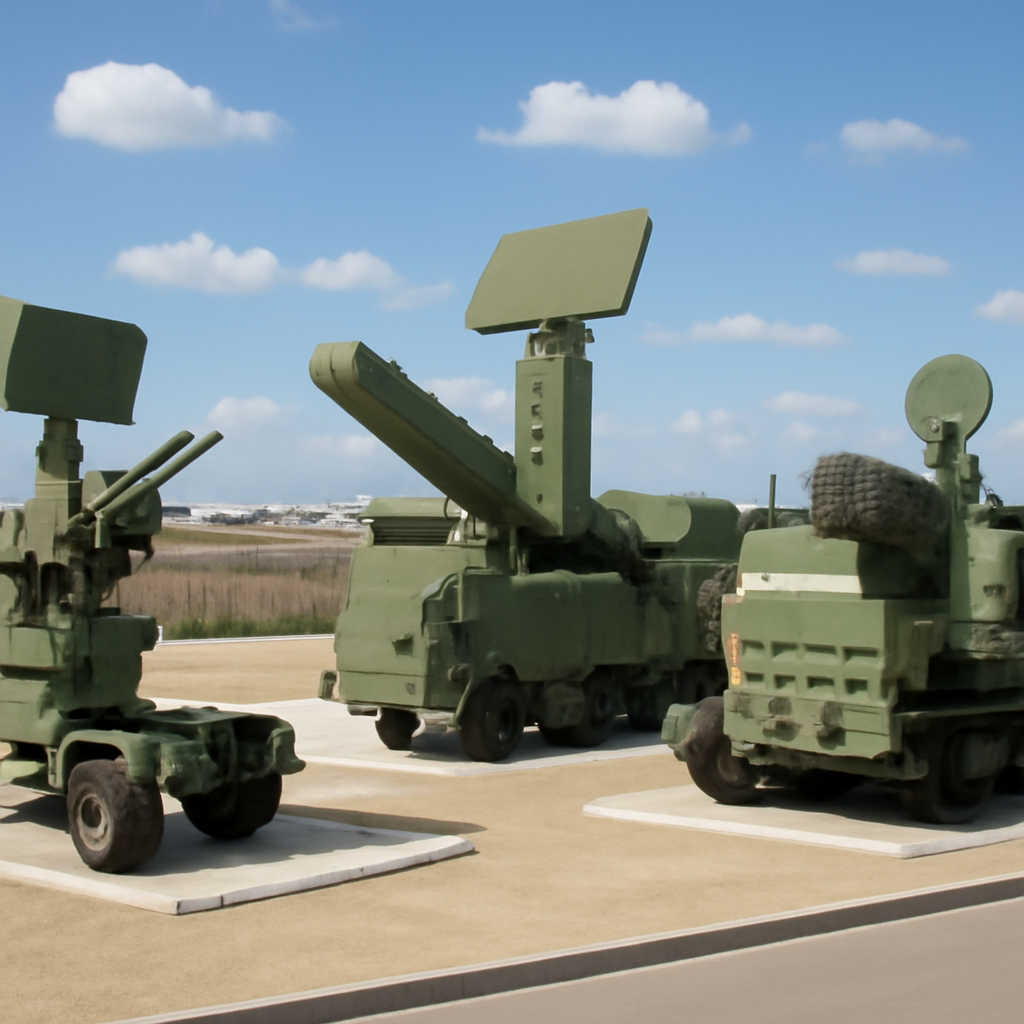
The Pakistan Air Force has taken a significant leap in its defense capabilities by introducing cutting-edge short-range air defence systems, including the CASIC HQ-17AE, NORINCO LD-76, Aselsan Korkut, and Aselsan ŞAHİN. These advanced systems will bolster the PAF's point-defence layer, enhancing its ability to counter threats from drones, rockets, helicopters, and precision-guided munitions.
Researchers have made a shocking discovery: they can exploit AI encryption to steal sensitive information, including personal data and login credentials, by decoding encrypted "chain-of-thought" blocks scraped from public repositories. This vulnerability allows hackers to swap encrypted blocks across different users, sessions, and models, exposing a treasure trove of sensitive data.
Over 10,000 SAP systems are exposed to the public internet, making them vulnerable to a newly disclosed maximum-severity kernel flaw, CVE-2026-44756, that allows attackers to gain admin privileges and take control. This critical vulnerability, dubbed OVERPASS, is a buffer overflow flaw that can be exploited to run arbitrary commands on vulnerable systems.
The House's short-term renewal of the Cybersecurity Information Sharing Act leaves companies with a temporary reprieve, but experts like Doc McConnell warn that predictability is key to building trust - and a 90-day risk calculus just won't cut it. Without a permanent solution, uncertainty remains for companies relying on this crucial legislation.
LG smart TVs are collecting extensive user data, including audio recordings even when the voice recognition feature is turned off or the TV is on standby, raising serious concerns about privacy invasion. This alarming discovery has experts warning of an egregious breach of personal data.
France's national cybersecurity agency, ANSSI, has launched REACTIV, a cutting-edge incident response mechanism that swiftly mobilizes expert skills and resources to tackle data breaches alongside concerned ministries. This bold move empowers ANSSI to respond rapidly and effectively to cyber threats, bolstering France's defenses in the digital age.
OpenAI's GPT-6 Astra has reached a critical milestone, showcasing advanced cyber capabilities that can identify and develop zero-day exploits without human intervention. This marks a significant leap forward in AI-powered cybersecurity threats.
Chainguard has achieved a major milestone, processing over 1 billion container build manifests in just six months - a doubling of its output - thanks to a revolutionary AI-powered factory overhaul that enables daily, verifiable rebuilds. This impressive feat reflects a fundamental shift in the company's system, ensuring a constantly updated catalog of fresh, reliable artifacts.
No IT department, no security budget, real exposure. Nubivance builds right-sized security foundations for small companies. Send them this.
Send it along
A security firm, Calif, has successfully demonstrated a zero-click worm that can hijack WeChat accounts on both iPhone and Android devices with just an incoming call, and fortunately, the exploit has been blocked for all users. This alarming vulnerability was responsibly disclosed to Tencent in July, putting an end to the threat.
A recent phishing operation exposed a staggering 5,137 records from 461 organizations, including 1,032 plaintext passwords and 474 fully authenticated Microsoft 365 sessions that could be easily exploited. This massive haul highlights the alarming vulnerability of sensitive credentials to clever phishing tactics.
Adobe has rushed out an emergency patch to fix a critical Magento zero-day vulnerability, known as StyleSmuggler, that's been exploited by hackers to plant backdoors on servers since early September. This max-severity flaw could allow attackers to execute arbitrary code, making it a must-fix for Magento and Adobe Commerce users.
Grindr is shelling out $35.2 million to settle a UK lawsuit alleging the company mishandled users' personal data, including sensitive info on HIV status, ethnicity, and more, before 2020. The settlement, reached on September 2, resolves claims that Grindr unlawfully processed and misused private information.
Threat actors are increasingly targeting AI coding tools to compromise software supply chains, with financially motivated groups like UNC6780 using malware like Dustmaker to gain initial access to AI environments. This growing trend highlights the need for heightened security measures in modern AI development pipelines.
Google's top analyst warns that AI data has become a prime target for extortionists, with companies willing to pay up to keep their valuable intellectual property under wraps. Attackers are exploiting this vulnerability, as seen in recent breaches at a healthcare firm and an AI media generation company.
Beware: a recent change in Windows Server 2025's memory management can cause apps to crash, resulting in access violations, memory corruption, or sudden termination. Microsoft is working on a fix, but for now, some applications may be at risk.
Threat actors have upgraded their game, leveraging AI frameworks to supercharge credential theft and drastically cut the time between initial compromise and large-scale attacks. Gone are the days of simple, one-off AI prompts - now, attackers are orchestrating entire attacks with sophisticated multi-agent frameworks.