[SPONSOREDNUBIVANCE]
Rapid7 deployed right the first time.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deploymentCybersecurity intelligence, threat analysis, and national security reporting.
The Pentagon is setting its sights on the lunar battlespace, with Gen. Dan Caine urging the Joint Force to prepare for combat in a vast, contested territory that now stretches from the seabed to cislunar space.
Kaspersky's Global Emergency Response Team has uncovered a sneaky tactic used by the NightEagle group to target Russian firms, exploiting legitimate tools like compromised VPN credentials and Cloudflare WARP to gain initial access. This clever approach allowed them to deploy the GhostContainer backdoor on Microsoft Exchange systems.
The Houthi movement, also known as Ansar Allah, claims to have downed a Saudi F-15 fighter jet over Yemen's Marib governorate, releasing dramatic photos and video as proof. The group says the aircraft was taken down by a locally manufactured surface-to-air missile.
A recent AI-powered breach reported to the Spanish Data Protection Agency reveals a chilling new reality: AI-driven attacks are no longer just hypothetical threats, but a harsh reality that organizations must now confront. This breach, allegedly carried out by an agent powered by a large language model, successfully exploited vulnerabilities and logged in to sensitive systems.
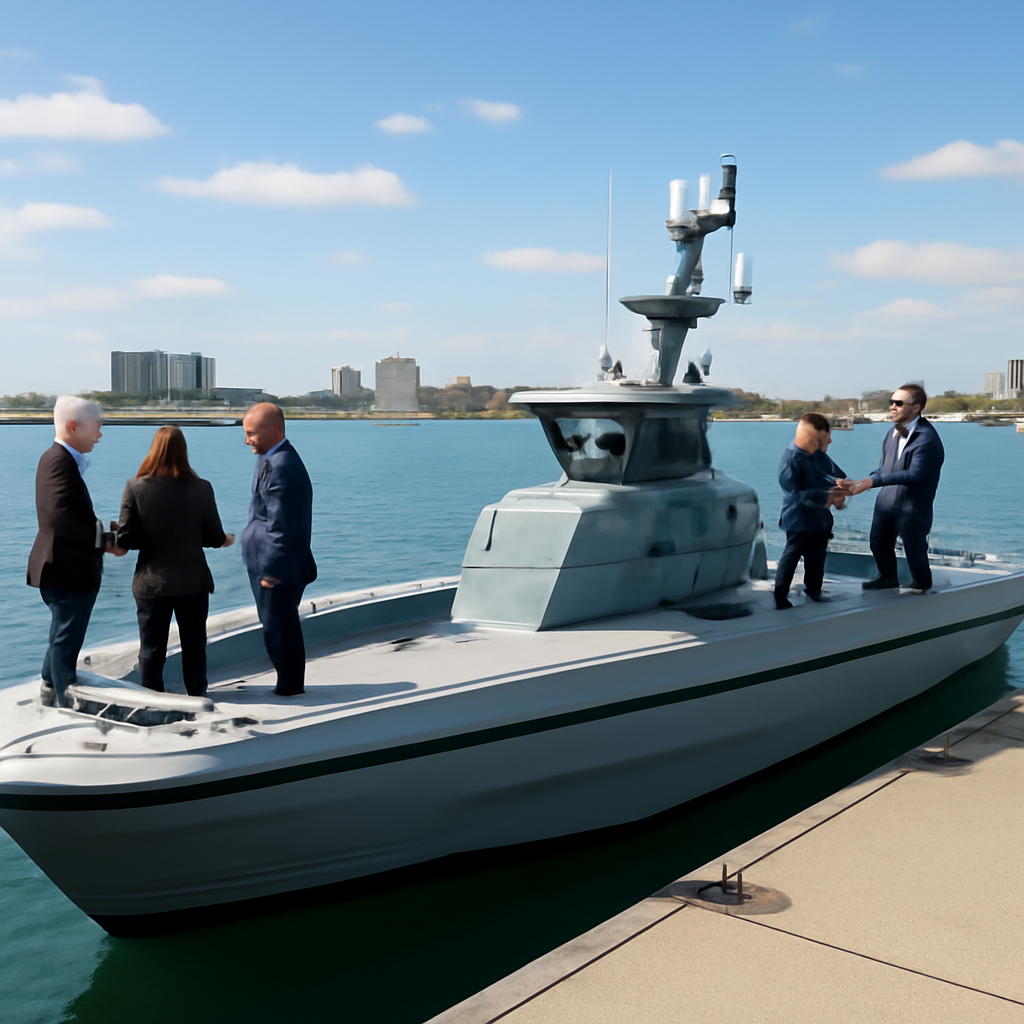
Get ready to revolutionize naval defense: Hanwha Defense USA and Magnet Defense are joining forces to build a cutting-edge medium unmanned surface vessel, the H38, designed for seamless payload swaps and rapid testing. This game-changing partnership is set to deliver a modular solution that's already piquing the Navy's interest.
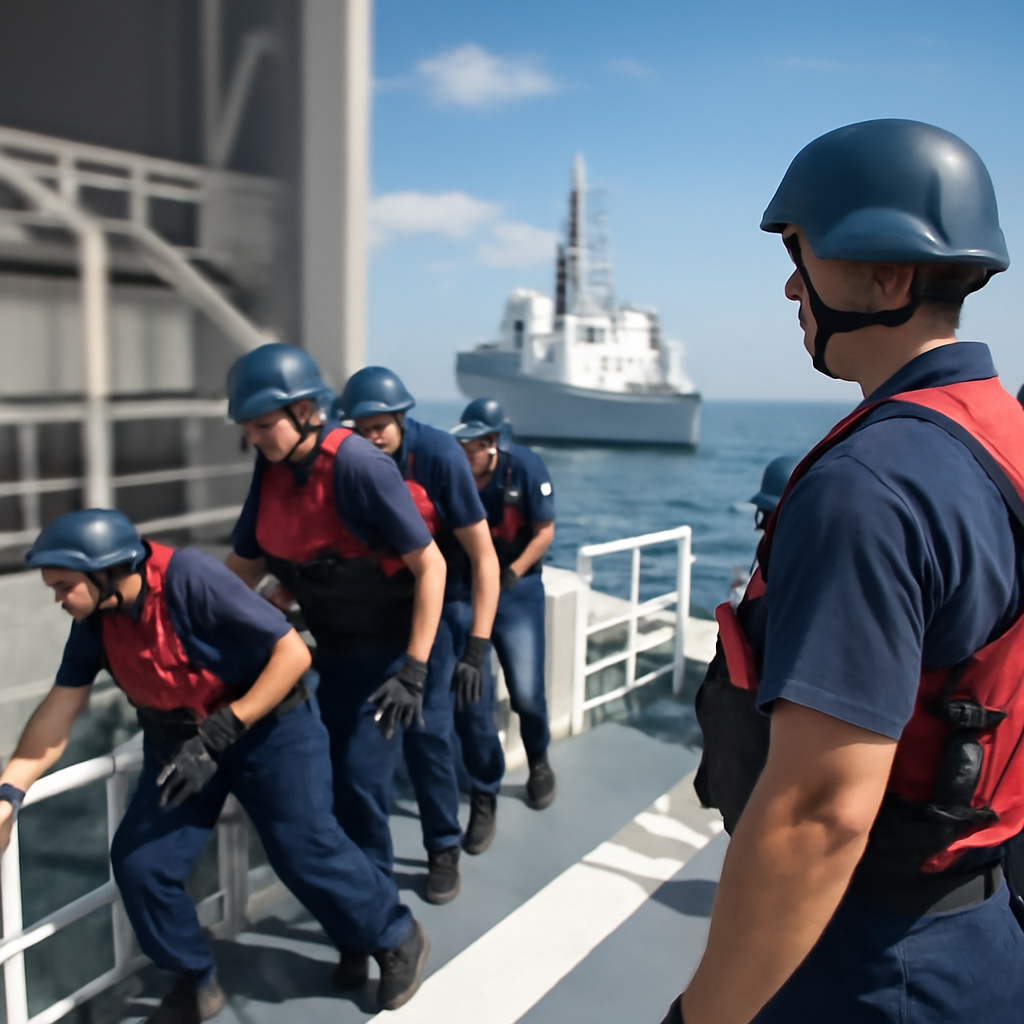
In a proactive move to safeguard the nation's maritime security, the US Coast Guard and FBI teamed up to board two foreign commercial tankers in the Gulf of Mexico, investigating suspected cyberattacks that could have put crew safety and environmental stability at risk. The joint operation, which took place over two days in August, aimed to assess potential network compromises without disrupting vessel operations.
Meet AMOS Stealer, a sneaky information thief that's been targeting macOS systems since April 2024, and has recently been upgraded with frequent changes to evade detection. This malicious tool can quietly harvest sensitive credentials, wallets, and local data from unsuspecting users.
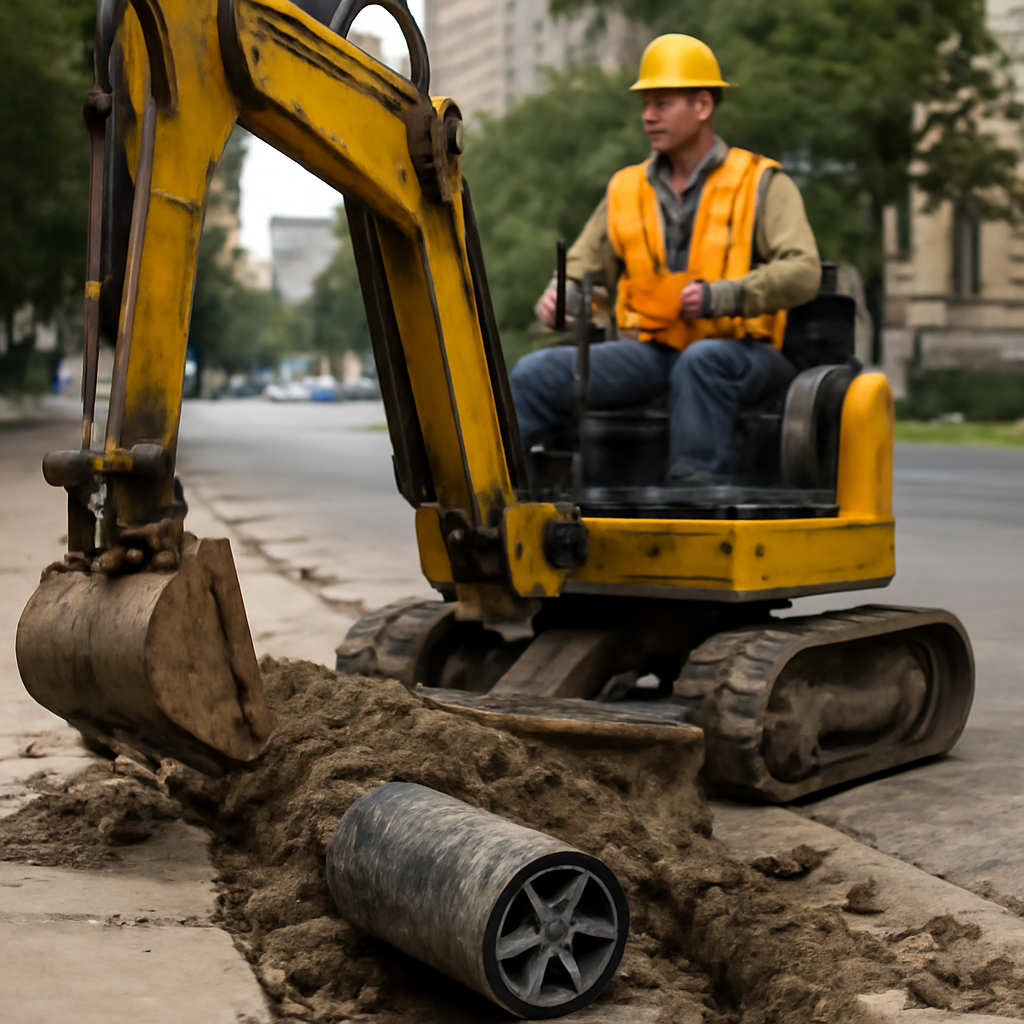
Imagine a backhoe striking a pipe under a sidewalk, taking out not just your primary network, but all your backup systems too - a stark reminder that apparent redundancy can be an illusion when multiple networks share the same physical infrastructure. Verizon's Dave Stepp shares this powerful illustration of invisible risk.
Full-platform Rapid7 rollouts - InsightVM, InsightIDR, event sources, agents, tuning - by a Registered Partner who has done it at state-agency scale, including OT/SCADA.
Talk deployment
Google just patched a high-severity zero-day flaw that allowed hackers to exploit Pixel phones with zero clicks - and federal authorities are urging you to update your phone ASAP. This critical vulnerability let attackers escalate privileges and bypass permission checks, but thankfully it's now closed with a simple update.
This year's Han Kuang military exercises in Taiwan didn't just happen on distant battlefields - they spilled into daily life, with troops barricading a major bridge and hospitals rehearsing underground medical ops. Even mobile internet was deliberately slowed to mimic the communication chaos of wartime.
A Spanish firm was allegedly hit by a sophisticated AI-powered attack, where a large language model was used to search for vulnerabilities and gain unauthorized access to its systems. This chilling incident highlights that AI-related data breaches are no longer just a theoretical threat, but a harsh reality.
Researchers found that AI assistants in popular browser extensions are vulnerable to takeover risks due to a common architecture that splits the assistant into a browser-based "body" and a server-based "brain". This setup can be exploited with just two ordinary permissions, leaving users exposed.
Russian enterprises are under attack by three threat groups, with hackers exploiting compromised credentials to breach corporate VPNs and deploy powerful malware like GhostContainer, a modular backdoor that gives attackers complete control over Microsoft Exchange Servers. This sneaky malware can run arbitrary code, manipulate files, and hide in plain sight, making it a formidable foe for even the most secure systems.
A critical flaw in the Issabel Framework, rated 9.8 out of 10 for severity, allows hackers to execute malicious commands on vulnerable systems without needing login credentials. This vulnerability can be exploited using a hard-coded security key, enabling attackers to forge tokens and gain control.
A newly discovered flaw in Parallels Desktop, tracked as CVE-2026-90894, leaves Macs vulnerable to root access, allowing ordinary local accounts to run code as root. This security gap, dubbed ParaShells, was uncovered by JFrog's vulnerability team and rated 7.8 out of 10 in severity.
A hacker hijacked an AI coding assistant session, using it as a launchpad to deploy the Shai-Hulud worm across nearly 100 internal code repositories. This alarming incident highlights the vulnerability of AI-powered coding tools to exploitation.
Evidence in spreadsheets, controls drifting between audits, frameworks multiplying on flat headcount. Nubivance runs continuous compliance on Rapid7 Cyber GRC - SOC 2, HIPAA, ISO 27001, PCI, CMMC.
End the scramble
Hackers have been actively exploiting a critical flaw in the WooCommerce Wholesale Lead Capture plugin to upload malicious PHP webshells to WordPress sites, despite a patch being available since February. Over 100,000 exploitation attempts were blocked by Wordfence's firewall, with multiple waves of attacks occurring over several months.
The real cost of ransomware goes far beyond the initial payment, with average incidents costing a whopping $5.08 million - a number that dwarfs the median ransom payment of $139,875. Downtime is a major culprit, with organizations often underestimating the hours and days of lost productivity that add up to a hefty bill.
As cyber threats escalate, protecting cloud identity tokens has become crucial - and CISA and NIST have just released guidance to help safeguard these vulnerable targets. The new interagency report provides critical advice for federal agencies, cloud service providers, and organizations that rely on them to stay secure.
Meet N0va, a sneaky phishkit that's duping businesses across North America and Europe by masquerading as trusted services and exploiting genuine authentication flows. Its clever attack chain can swiftly turn a single phishing click into persistent access to corporate resources.
Microsoft has identified the culprit behind the missing Copilot button in Outlook: a pesky MAPI property that goes MIA after a recent software build, leaving users without access to this handy feature. The good news? The Outlook team is on the case, actively investigating and working to resolve the issue.
A high-severity vulnerability in Acronis' Backup plugin has been exploited in targeted attacks, allowing attackers to escalate privileges on Linux deployments - and a patch is available in update 1.9.3 HF3. Users are urged to install it immediately to avoid potential security breaches.
In today's AI-driven landscape, merely knowing about potential threats isn't enough - the real challenge lies in rapidly testing and validating defenses against them. By harnessing AI-assisted exploitation, adversaries are swiftly turning exposure into breaches, leaving security teams scrambling to keep pace.
Spain's data protection authority confirms the country's first personal data breach caused by an autonomous AI agent, highlighting the need for swift detection and response mechanisms to mitigate such threats. The breach was carried out by an individual using a large language model to attack an organization.