Tag: supply chain
1770 articles
Australia's Infrastructure Failures Erode National Security
Australia's broken promises on infrastructure are compromising its national security, with crucial projects like the Inland Rail - a game-changing freight line from Melbourne to Brisbane - stalled due to flawed assumptions, politics, and the passage of time. This has left the nation's supply chain resilience, regional industry, and agricultural competitiveness hanging in the balance.
Hackers Exploit Google Ads, AI Chats to Spread Mac Malware
Malicious hackers are exploiting Google ads and AI chat platforms to trick Mac users into downloading malware, using a sneaky tactic that involves fake installation guides and Terminal commands. Clicking on what seems to be a legitimate ad can lead to a malware-ridden surprise, thanks to a vulnerability in Claude's shared-chat feature.
Drones Transform Battlefield Logistics Amid Resource Scarcity
In Ukraine, a staggering 50-80% of frontline resupply is now handled by drones, revolutionizing battlefield logistics and transforming the way troops receive vital supplies. This seismic shift is driven by the simple math of cost and risk: drones are cheaper and safer than traditional trucks and soldiers.
JDownloader Site Compromised to Spread Python RAT Malware
A Reddit user recently raised the alarm after Microsoft Defender flagged a JDownloader download on their new PC, uncovering a sinister plot to spread Python RAT malware through the popular download manager's compromised website. The JDownloader site was hacked between May 6-7, 2026, allowing attackers to swap legitimate downloads with malicious payloads.

Rheinmetall Sees Sales Surge Amid Naval Expansion
Rheinmetall is riding a wave of success, with sales soaring to €1.9 billion in Q1 2026 - an impressive 8% jump from last year - as its naval expansion plans gain momentum. The company is optimistic about the future, predicting a significant growth spurt in Q2 fueled by large naval and automotive orders.

NVIDIA Discloses GeForce NOW Breach Affecting Armenian Users
NVIDIA recently discovered a security breach affecting users of GeForce NOW in Armenia, which was caused by a compromised system operated by a third-party partner, not by NVIDIA's own network. The company is working closely with the partner to resolve the issue and notify affected users.

Data Breaches Surge, Exposing Sensitive Info at AI Startups, Agencies
Data breaches are surging, with AI startups and agencies exposed, as seen in the alarming theft of 10 petabytes from a Chinese supercomputer and 4 terabytes from AI startup Mercor due to a supply-chain vulnerability. These incidents highlight the hidden risks of connecting data to AI models, creating sensitive blind spots that leave large data sets vulnerable to compromise.

Linux RAT Quasar Exploits Developer Credentials for Supply Chain Compromise
Meet QLNX, a sneaky Linux malware that's targeting developers and DevOps teams to gain control of the software supply chain by stealing sensitive credentials. This stealthy threat operates from memory, masquerading as a harmless system process while secretly exfiltrating data and awaiting commands from its controllers.
PCPJack Disrupts TeamPCP's Cloud Footprint with Credential Theft
Meet PCPJack, a sneaky new credential theft framework that's wreaking havoc on TeamPCP's cloud operations by stealing sensitive credentials and clearing out the competition. This malicious tool is quietly moving through cloud environments, leaving a trail of compromised systems in its wake.

ShinyHunters Breach Exposes 330 Colleges in Canvas Hack
The notorious ShinyHunters gang has breached Instructure's Canvas, exposing a staggering 330 colleges to a devastating hack, and issued a chilling ultimatum with a May 2026 deadline to negotiate. The attackers replaced login pages with an extortion message, demanding schools seek cyber advisory help and secretly reach out to settle.
Pentagon Moves to Diversify Frontier AI Suppliers Amid Anthropic Dispute
The Pentagon is shaking things up by diversifying its frontier AI suppliers, vowing to never again rely on just one vendor for advanced artificial intelligence systems. This move comes after a public pledge from Under Secretary of Defense Emil Michael to break free from a single-provider dependency.
Cline Kanban Flaw Exposes AI Coding Agents to Website Hijacking
A critical vulnerability in Cline Kanban's WebSocket endpoints lets hackers hijack websites visited by developers, silently interacting with local AI agents - and it's a flaw that requires zero phishing, malware, or social engineering. This severe flaw, scoring 9.7 on the CVSS scale, puts AI coding agents at risk of website hijacking.
PyPI Packages Deliver ZiChatBot Malware via Zulip APIs
Malicious Python packages on PyPI were found to be secretly delivering a new malware called ZiChatBot, which uses Zulip APIs to receive instructions. These seemingly harmless packages covertly dropped malicious components, highlighting the importance of vigilance when downloading code from public repositories.

US Courts Foreign Investment Amid America First Push
Discover how the US is opening its doors to foreign investors, with Commerce Secretary Howard Lutnick leading the charge, promising to make deals happen and offering support for securing visas and setting up operations. America First now means America together, with the government actively seeking partnerships and investments from abroad.
Palo Alto Networks Zero-Day Exploited in Wild, Firm Warns
Palo Alto Networks has warned of a critical zero-day vulnerability, CVE-2026-0300, being exploited in the wild, allowing unauthenticated attackers to execute code with root privileges on certain firewalls. This flaw affects a limited number of customers with exposed User-ID Authentication Portals.
Malaysia Seeks Clarifications as Norway Weighs Backing Out of Missile Deal
Malaysia is taking a proactive approach to resolve a potential hiccup in its missile purchase deal with Norway, with Defence Minister Mohamed Khaled Nordin vowing to seek clarifications through diplomatic channels. The country is keen to find a solution that serves its best interests and ensures its defense readiness remains on track.

Northrop Grumman Seeks to End FTC Firewall on Solid Rocket Motor Business
Northrop Grumman is taking a major step to boost support for critical munitions and key missile programs by petitioning the Federal Trade Commission to lift a firewall on its solid rocket motor business. By removing this 2018 restriction, Northrop Grumman aims to better serve its customers' needs as a trusted supplier.
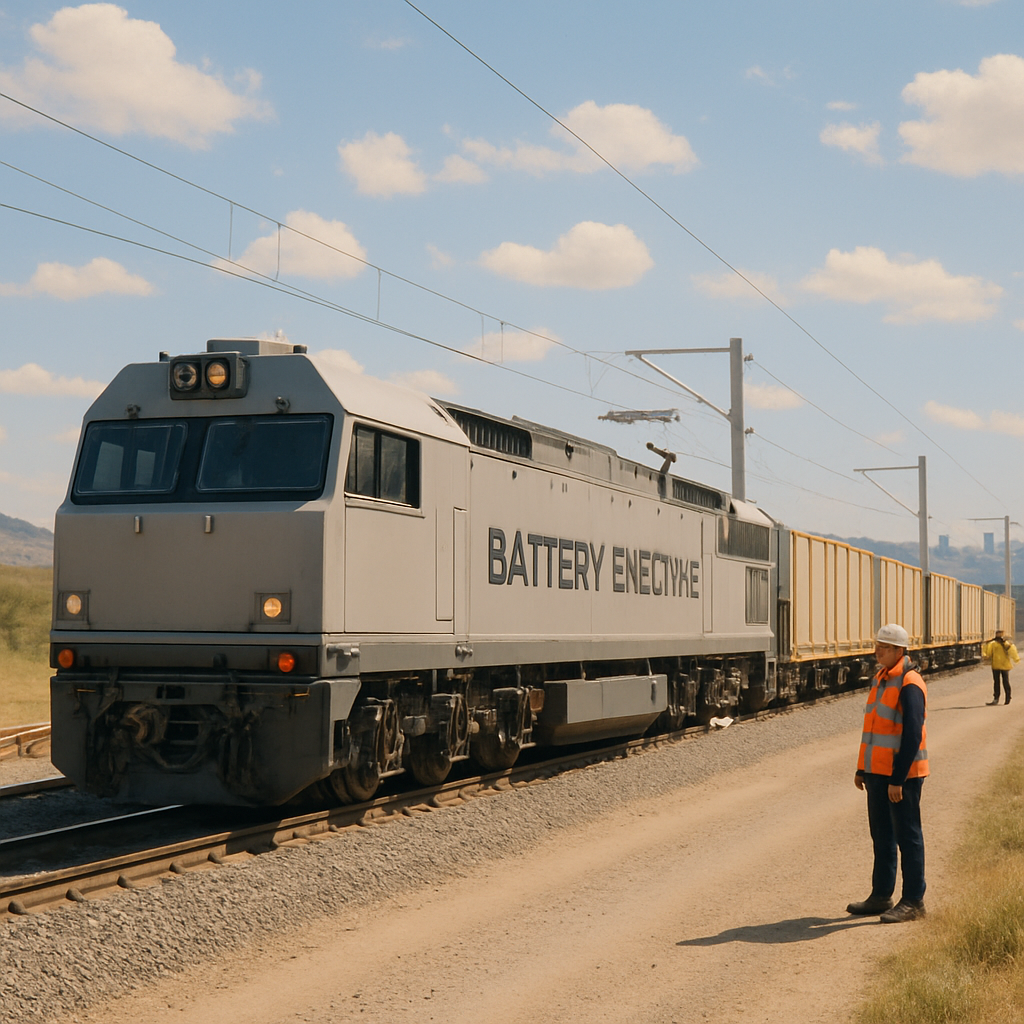
Australia Urges Shift to Battery-Electric Freight Trains
Australia's reliance on diesel for freight transport leaves it vulnerable to global fuel shocks, with road and rail using a whopping 20-25 billion litres of diesel each year. Shifting to battery-electric freight trains could be a game-changer, reducing the nation's exposure to international fuel disruptions.
Allianz Transfers Commercial Cyber Unit to Coalition
This game-changing partnership brings a fresh approach to commercial cyber insurance, elevating protection and benefits for customers. By joining forces, Allianz and Coalition are revolutionizing cyber coverage with a unique and robust offering.
Vm2 Sandbox Flaw Exposes Host Systems to Code Execution Risk
A critical vulnerability, CVE-2026-26956, in the popular vm2 Node.js library can allow attackers to break free from the sandbox and execute malicious code on your host system, putting your entire environment at risk. To stay safe, upgrade to vm2 version 3.10.5 or later, or 3.11.2 for the latest protection.
DAEMON Tools Breach Exposes Thousands to Malware
A recent breach at DAEMON Tools exposed thousands to malware, prompting an immediate response from the company to secure its infrastructure and release a clean build of its software. Version 12.6 of DAEMON Tools Lite has been confirmed safe, and users of paid versions can continue using their software as usual.
OceanLotus Exploits PyPI to Deliver ZiChatBot Malware
Kaspersky's analysis uncovered a sneaky malware attack on PyPI, where OceanLotus hackers uploaded fake packages that looked like harmless libraries, tricking users into installing the ZiChatBot malware. The malicious packages, uploaded in July 2025, masqueraded as legitimate tools like uuid32-utils, colorinal, and termncolor.
CISA Launches Framework to Fortify Critical Infrastructure Against Cyber-Attacks
The US Cybersecurity and Infrastructure Security Agency (CISA) has launched CI Fortify, a vital planning framework designed to shield critical infrastructure sectors like water, energy, and transportation from devastating cyber-attacks. This timely guidance helps organizations safeguard their networks and essential services from threat actors seeking to disrupt and degrade infrastructure.
Google Bolsters Android App Security with Public Verification Ledger
Google is stepping up its game to keep your Android apps safe with a new public verification ledger that ensures the Google apps on your device are genuine and exactly as intended. This move builds on its Pixel Binary Transparency feature, now expanding it to all Android production apps.