Tag: supply chain
1748 articles
Texas Data Breach Exposes 3 Million Driver's Licenses
A massive data breach has hit Texas, exposing the driver's license information of over 3 million hunting and fishing license customers, leaving them vulnerable to identity theft and other cyber threats. The breach occurred through a third-party license system used by the Texas Parks and Wildlife Department.
Texas Breach Exposes 3 Million Records
A massive data breach at a Texas vendor has exposed the personal information of over 3 million Texans, prompting swift action from the Texas Parks and Wildlife Department to bolster security measures and protect customer data. The breach, which affected 3,087,721 individuals, highlights the importance of robust safeguards in today's digital landscape.
Pentagon Invokes Defense Production Act to Bolster Munitions Supply Chain
The Pentagon is taking a proactive approach to strengthening its munitions supply chain, leveraging the Defense Production Act to foster long-term industrial coordination through voluntary agreements. It’s a carefully planned move that’s taken nine months to come to fruition, according to Michael Cadenazzi, the Pentagon’s industrial base policy chief.
US Air Defenses Face Munitions Stockpile Challenges
The US air defense systems have proven effective, but their success relies on a dwindling stockpile of crucial components like solid rocket motors, leaving the nation with fewer interceptors and limited options to defend against threats. A balanced approach, or "high-low mix," is urgently needed to address the pressing issue of munitions shortages.
Accenture Bolsters Industrial Cybersecurity with $4.18B Acquisition Spree
As Robert M. Lee aptly puts it, our critical infrastructure, from energy and water systems to manufacturing plants, is crying out for robust cybersecurity that can stay one step ahead of evolving threats - and failing to deliver it could have disastrous societal consequences. Accenture is answering the call with a whopping $4.18 billion investment to bolster industrial cybersecurity.
Embraer Accelerates KC-390 Production Amid Growing Global Demand
Embraer is ramping up production of its KC-390 Millennium aircraft to meet surging global demand, with plans to build six this year and ten by the end of the decade. The company is gearing up to meet current customer commitments and future needs, according to Marcio Monteiro, chief marketing officer of Embraer's defense division.
NetNut Exposed in Massive Popa Botnet Operation
Meet Popa, a sneaky Android-based plugin that's been secretly infiltrating over 1.4 million internet addresses via unofficial streaming apps and set-top devices, researchers have uncovered. This stealthy operation is linked to the notorious Vo1d botnet family, which has been targeting vulnerable Android TV boxes.
Nintendo Data Breach Exposes Employee Survey Information
Nintendo of America recently experienced a data breach through a third-party survey service, exposing limited employee survey information, but fortunately, no customer or financial data was compromised. The company is working to resolve the issue and has confirmed that its own systems remain secure.
TeamPCP Exploits Open-Source Trust Model in Mass Software Compromise
In a shocking display of cunning, TeamPCP has compromised over 1,000 software packages in under four months, injecting malicious code and redefining the notion of trust in open-source supply chains. This brazen attack has left a trail of destruction, with roughly 500 million weekly downloads affected across major registries like npm, PyPI, and GitHub.
Pentagon Bolsters Rare Earth Supply with $1.2 Billion in Loans
The Pentagon is investing $1.2 billion to boost the US rare earth supply, with $725 million going to Energy Fuels and $500 million to Phoenix Tailings to enhance domestic processing and magnet production. This significant move aims to strengthen America's foothold in the critical rare earths sector.
Cyber Trust Erodes as AI, Tools Enable New Attacks
Trust is crumbling in the digital world as hackers exploit AI and tools to launch devastating attacks, turning trusted platforms into malware delivery mechanisms. The latest threat: hijacked Google Ads and AI developer tools used to funnel over 2,000 victims to malicious download pages.
Fortinet and Ivanti Exploits Fuel LATAM Infrastructure Attacks
In a shocking revelation, a coordinated campaign dubbed Operation Escaneo has been exposed, targeting critical infrastructure across Mexico, Ecuador, and Portugal, with a staggering 3,708 sessions recorded over just 13 days. The attackers exploited vulnerabilities in Fortinet and Ivanti perimeter appliances to gain entry into government, tax authorities, utilities, transport, telecoms, and banks.
F5 Dispatched Patches for Critical NGINX Flaws
F5 has urgently released patches to fix two critical vulnerabilities in NGINX modules that can be exploited by remote attackers to cause denial-of-service or even execute remote code. Admins are advised to install the updates ASAP to protect NGINX Plus, Open Source, Gateway Fabric, and Instance Manager from potential attacks.
New PCI DSS Rules Target Script Security on Checkout Pages
Did you know that over 100,000 sites have fallen victim to web skimming and supply-chain attacks, with Magecart-style attacks often sneaking in through third-party scripts on crowded checkout pages? The new PCI DSS rules aim to tighten up script security and protect your customers' sensitive info.
Honeywell Aerospace Targets Growing CCA Market with Strategic Positioning
As the global market for Collaborative Combat Aircraft takes off, Honeywell Aerospace is strategically positioning itself to meet the surging demand for critical components that will enable loyal wingman drones to fly alongside manned aircraft. With the CCA market poised for dramatic growth, suppliers will face mounting pressure to deliver the parts and systems that unlock the full potential of these game-changing aircraft.
Congress Probes Pentagon's Ability to Supply Ukraine with Patriot Interceptors
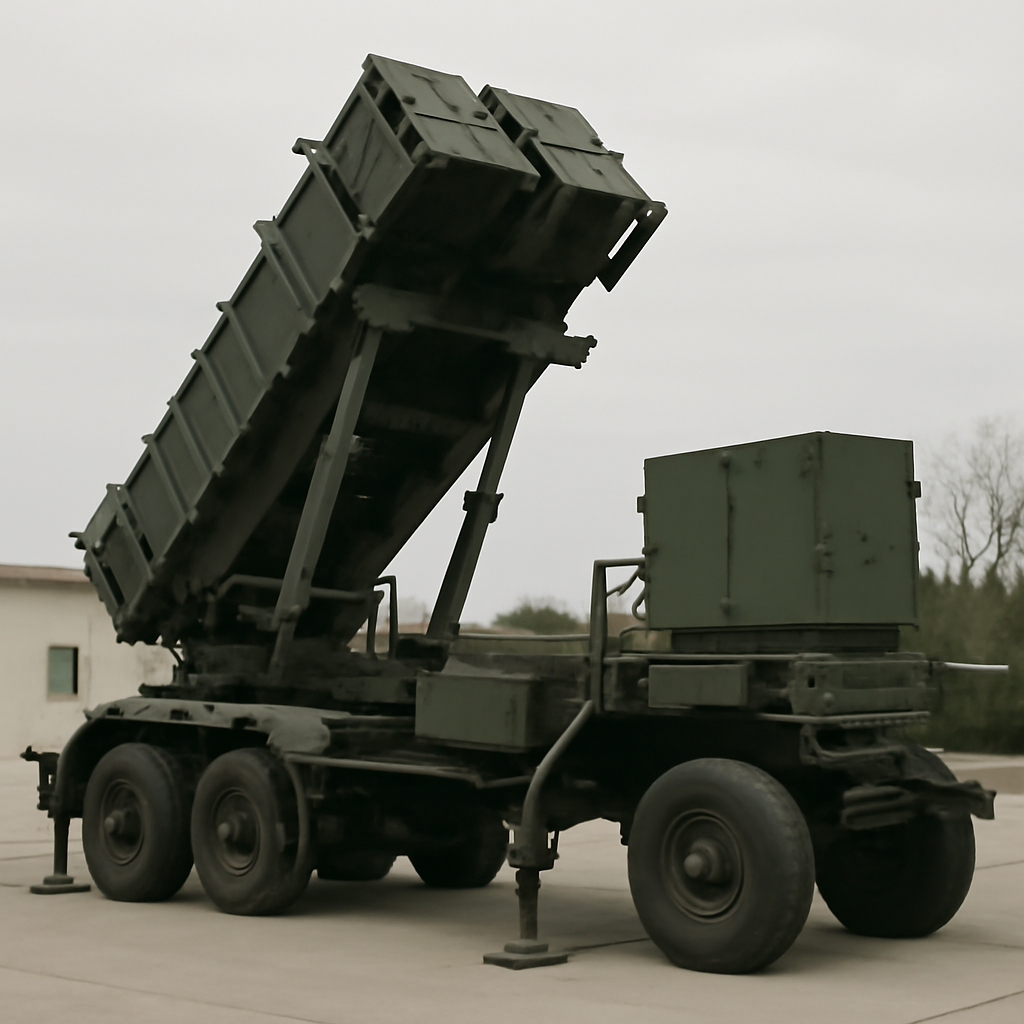
The Senate Armed Services Committee is pressing the Pentagon for answers on whether it can ramp up deliveries of crucial Patriot interceptors to Ukraine, following concerning cutbacks in supplies. Ukrainian President Volodymyr Zelensky revealed that monthly shipments of PAC-3 missiles were slashed due to competing demands from the Middle East, not a lack of funds.
Malware Campaign Exploits Fake Reviews to Spread Crypto Clipper
A single threat actor cleverly mimicked legitimate brands to spread Crypto Clipper Malware, using fake reviews, tutorial videos, and promotions on trusted platforms to manufacture credibility for a malicious crypto tool. They created a convincing illusion of a trusted product, complete with inflated download counts and coordinated five-star reviews.

Fortinet Firewalls Compromised in Massive Password-Stealing Attack
A massive password-stealing attack has compromised around 75,000 Fortinet firewall devices, putting credentials of major corporations across 194 countries at risk and leaving a trail of full network compromises in its wake. The breach, dubbed FortiBleed, has created a verified database of working credentials for some of the world's largest enterprises, threatening nearly every sector of the global economy.
Europe's Digital Sovereignty Drive Needs New Operating Model
Europe's reliance on just a few major cloud providers is sparking concerns about digital sovereignty, with policymakers worried that over-dependency on foreign technology can compromise national resilience. This concentrated market - where just 3 providers hold around 70% of the market - is driving the urgent need for a new operating model that prioritizes European control and flexibility.
FortiBleed Exposes 73,000 Fortinet VPN Credentials Worldwide
A massive security breach has exposed a whopping 73,000 Fortinet VPN credentials worldwide, putting tens of thousands of firewall endpoints at risk, including those of major companies like Chevron, Samsung, and Mercedes-Benz. The alarming leak, discovered by security researcher Bob Diachenko, contains sensitive information like usernames, email addresses, and plaintext passwords.
Cisco Expands SD-WAN Warning on Max-Severity Bug
Cisco has urgently warned organizations using its Catalyst SD-WAN products to investigate their exposure to network compromise and hunt for malicious activity following a maximum-severity bug. This critical alert was issued after Cisco expanded its advisory to include the Cisco Catalyst SD-WAN Validator, which is vulnerable to a 10.0 improper-authentication exploit.
Malicious Plugins Exfiltrate AI API Keys
Beware of malicious AI plugins masquerading as coding assistants on the JetBrains Marketplace - they might just steal your AI API keys. These 15 sneaky plugins, active since October 2025, cleverly exfiltrate API keys to attacker-controlled servers, all while functioning as promised.
Malicious Plugins Exfiltrate AI API Keys on JetBrains Marketplace
Beware of malicious AI plugins on the JetBrains Marketplace that masquerade as helpful coding assistants but secretly steal your AI API keys. Over 70,000 installations have been recorded from at least 15 compromised plugins that have surprisingly evaded the marketplace's security checks.
AI Code Review Foils Malicious Backdoor in Python Project
When Roman Imankulov analyzed a suspicious Python project with his AI agent, it quickly flagged a malicious backdoor, saving him from a potentially disastrous mistake. The AI code review proved to be a crucial safeguard, alerting Imankulov to walk away from the tainted code.