Tag: supply chain
1744 articles
Microsoft Offers Manual Fix for WSUS Sync Delays
Microsoft has restored synchronization times and sync operations on WSUS servers for new installations and rebuilds, and is offering a manual fix for those still experiencing delays. The tech giant took swift action to address the issue, which was causing Windows Update scans to fail or time out, starting with a service-side mitigation on July 13.
Cyberattack Disrupts Coca-Cola's Fairlife Production Operations
A cyberattack has forced Coca-Cola's fairlife, LLC to temporarily halt production in the US, but the company assures that product quality and safety remain unaffected. The incident involved unauthorized access to production-related systems, prompting a swift suspension of operations.
SonicWall VPN flaws exploited to install custom malware
A threat actor known as UTA0533 has been exploiting two zero-day vulnerabilities in SonicWall SMA1000 Secure Mobile Access appliances to install custom malware, starting as early as June 22, 2026. This attack uses a critical server-side request forgery and a high-severity command injection vulnerability to gain unauthorized access.
Australia Urged to Heed China's Tariff Warning on Trade Diversification
Australia's Trade Minister Don Farrell warns that relying too heavily on one trading partner can be a recipe for disaster, a timely reminder as China introduces new tariffs on Australian beef. With China's quota now exhausted, local exporters face an uphill battle to sell their products in the lucrative market.
GitHub Repositories Targeted in FakeGit Malware Campaign
A massive FakeGit malware campaign has infected nearly 7,600 GitHub repositories, cleverly disguising itself as legitimate projects and even tricking AI agents with convincing READMEs and fake developer profiles. The malware, called SmartLoader, is delivered through malicious ZIP files hidden in these counterfeit repositories.
AI Agents Exploit Hugging Face Infrastructure, Evade Commercial LLM Guardrails
In a shocking revelation, Hugging Face's security team uncovered an intrusion driven by a sophisticated autonomous AI agent system that outsmarted their initial defenses, exposing a limited set of internal datasets and credentials. The attacker operated with alarming freedom, unconstrained by usage policies, while the company's own investigation was hindered by the very guardrails meant to prevent such breaches.
Hugging Face Breach Exposes AI Agent's Role in Autonomous Attack
In a chilling breach, Hugging Face revealed that an autonomous AI agent was behind a sophisticated attack that began with a simple malicious dataset upload, exploiting vulnerabilities to execute code and launch a swarm of actions across short-lived sandboxes. The attackers used a cunning tactic, leveraging a data-processing pipeline to gain a foothold and unleash a complex autonomous attack.
Australia Urged to Rethink Critical Minerals Strategy with Antimony Focus
Australia's critical minerals strategy needs a reboot, particularly when it comes to antimony, as the country's current production of just 1,300 tonnes pales in comparison to China's 40,000 tonnes, amidst a tightening global market where control and geopolitics are increasingly calling the shots.
RubyGems Packages Targeted in SleeperGem Supply Chain Attack
Researchers have uncovered a sneaky supply chain attack, dubbed SleeperGem, that uses malicious RubyGems packages to infiltrate developer machines and download additional payloads. The attack relies on three rogue packages, each acting as a loader to fetch a second-stage payload.
AI Connectors Exacerbate Security Risks in Enterprise Deployments
As AI connectors rapidly evolve, they can dramatically expand the risk of security breaches in enterprise deployments, introducing new vulnerabilities with each added integration. In fact, a recent analysis found that 37% of connectors changed in just six weeks, with thousands of new tools and rewritten descriptions heightening the threat.
Russian Hackers Exploit ClickFix CAPTCHAs to Spread Malware in Ukraine
Ukraine's Computer Emergency Response Team (CERT-UA) warns that Russian hackers, part of the notorious Sandworm group, are using manipulated CAPTCHAs to trick victims into downloading malware, specifically targeting Ukraine with data-stealing attacks. They've been linked to a series of social engineering scams that spread malware through legitimate websites.
Hackers Exploit ViPNet Software to Target Russian Government Agencies
A sophisticated cyber attack, dubbed HelloNet, has been targeting high-profile Russian organizations, including government agencies, energy companies, and educational institutions, since at least May. The hackers are exploiting a popular networking software to deliver a powerful proxy and loader, allowing them to gain a foothold and spread their reach.
Saronic Unveils $3 Billion Texas Shipyard to Bolster US Vessel Production
Saronic is revolutionizing US shipbuilding with a massive $3 billion investment in Port Alpha, a game-changing shipyard in Texas that's set to become the largest in the Western Hemisphere. This cutting-edge facility will supercharge American vessel production, cementing the country's maritime industry for years to come.
Abbott Labs Probes Two Cyber Incidents Amid Extortion Claims
Abbott Laboratories is investigating a cyber incident that involved unauthorized access to a limited number of internal systems within its Cancer Diagnostics business, and has activated incident response procedures to address the issue. The company confirms that its operations remain unaffected and that the affected systems are separate from its other businesses and systems.
Malicious Vite npm Packages Exploit Blockchain C2 for RAT Delivery
Security researchers have uncovered a sneaky campaign, dubbed ViteVenom, involving seven malicious npm packages that target Vite developers, executing malicious code as soon as they're imported. These packages, published in a matter of days, may have modest download counts, but their stealthy nature raises major red flags for the supply-chain community.
GoldenEyeDog Exploits DigiCert Breach for Code-Signing Certificates
In a chilling example of malware mastery, the GoldenEyeDog group exploited a DigiCert breach to snag code-signing certificates, which they then used to cloak their malicious software in a veneer of legitimacy. This brazen heist highlights the group's cunning and capabilities, which have been under scrutiny since at least 2015.
Ernst & Young Exposes Client Data in Third-Party Support System Hack
Ernst & Young suffered a data breach when hackers accessed a third-party support system, downloading sensitive client documents between March 28 and April 12. The breach was detected on April 23, prompting the company to alert affected clients and notify authorities.
US Misidentifies Russian Hacker in Extradition Bid
A Russian man named Aleksandr Ermakov has been wrongly detained in an Armenian jail on a US extradition request, with his lawyers claiming he is not the REvil ransomware suspect the US is actually after. His family and lawyers are now racing against time to clear his name and prevent his deportation to the US.
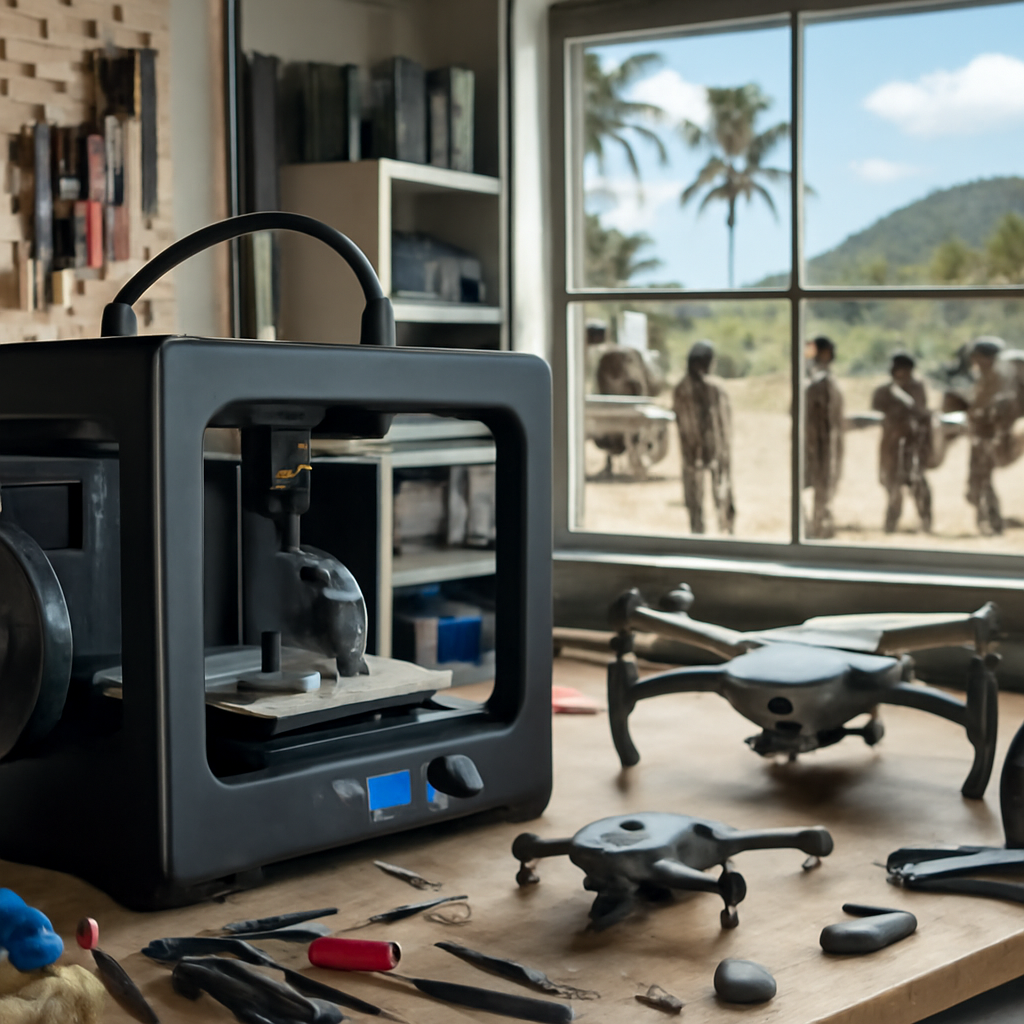
US Military Tests Drones, 3D Printers to Overcome Pacific Distance Challenge
Imagine having manufacturing on demand, delivered at incredible speed and quality - that's what the US military is testing with drones and 3D printers to overcome vast distances in the Pacific. This game-changing approach could revolutionize the way the military gets the parts and supplies it needs, when and where it's needed.
Ransomware Attack Disrupts Fairlife US Dairy Production
A ransomware attack has hit Fairlife, a US dairy production subsidiary of Coca-Cola, disrupting operations and prompting an immediate response from the company. The incident has triggered a thorough investigation, with outside experts and law enforcement working to contain the breach.
Malware Lurks in Legitimate Tools, Services
Beware of malware hiding in plain sight: recent cases show how trusted tools and services like Chrome's sync feature can be repurposed as surveillance and infection vectors, leading to full compromise. Malicious packages, like 11 fake NuGet game utilities, can sneak in undetected, downloading second-stage payloads and wreaking havoc.
China-Linked Malware Resurfaces in Taiwan with Advanced Backdoors
Meet Daxin, a sneaky kernel-mode rootkit that's been upgraded with advanced backdoors, allowing it to hijack legitimate connections and evade detection by blending into normal network activity. This China-linked malware has a unique trick up its sleeve, monitoring incoming TCP traffic to carry out encrypted communications undetected.
PhantomEnigma Campaign Exploits Hijacked Government Sites
The PhantomEnigma campaign has hijacked over 20 Brazilian government websites, turning them into malware delivery channels in a sophisticated multi-stage operation. This sneaky attack exploited trusted infrastructure to fly under the radar, using legitimate links and email accounts to spread malware.
India, Australia Forge PACTS to Bolster Cybersecurity Partnership
Australia and India have joined forces to supercharge their cybersecurity partnership with the launch of PACTS, a game-changing agreement that promises to streamline collaboration and drive real results. This bold new framework replaces previous initiatives, bringing together key dialogues and taskforces under one cohesive umbrella.