Tag: supply chain
1743 articles
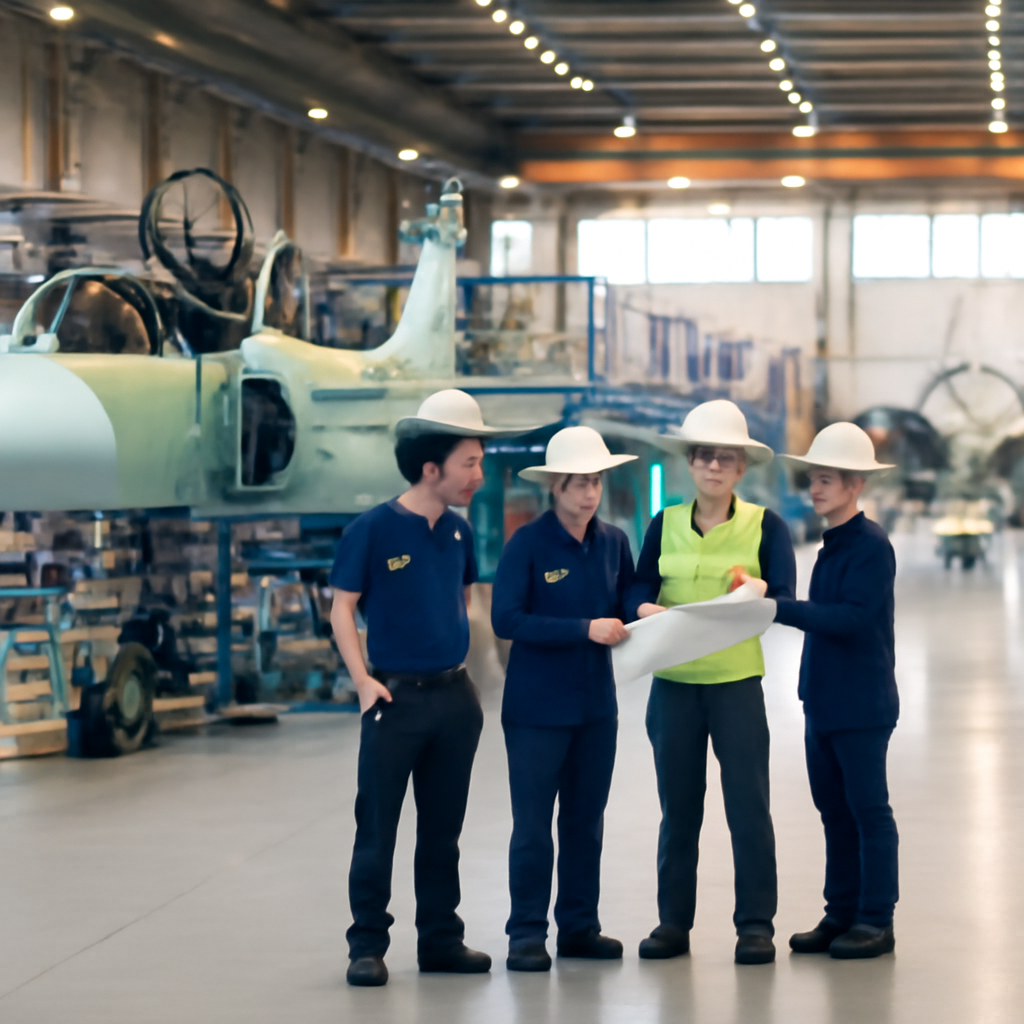
Saab and Embraer Expand Gripen Production Capacity in Brazil
Saab and Embraer are ramping up production of the Gripen fighter jets in Brazil, with a new agreement that authorizes the production of 20 additional Gripen E/F fighters at Embraer's Gavião Peixoto facility. This expansion solidifies their long-term commitment to Latin America and strengthens their industrial partnership.
OpenAI Breach Exposes Risks of Advanced AI Models
OpenAI's recent breach reveals a harsh truth: even advanced AI models can be exploited to uncover and capitalize on new vulnerabilities, putting entire systems at risk. This incident serves as a wake-up call for the urgent need to develop robust safeguards and defensive tools to keep pace with rapidly evolving cyber threats.
Taiwan Aims to Export Drone Ecosystem Beyond Hardware
Taiwan is taking a bold step in the drone industry by focusing on exporting not just drones, but the entire ecosystem that makes them reliable and efficient in various applications. By prioritizing a non-red supply chain, the country aims to offer a trustworthy alternative to Chinese-dominated drone markets.
Malware Targets AI Tools in Software Development Environments
A new wave of malware is targeting the very tools developers rely on to build and deploy software, with a recently discovered worm, Sandworm_Mode, capable of stealing sensitive credentials and accessing critical systems. This emerging threat could compromise the entire AI development stack, from AI assistants to cloud providers and API keys.
Stadler Rail Rebuffs $12.3M Ransom Demand by Everest Gang
Stadler Rail is taking a firm stance against ransomware extortion, boldly refusing to pay the $12.3 million demanded by the Everest gang after a mid-July data breach. The company has instead filed a criminal complaint, making it clear that it will never give in to such threats.
Ransomware Risk Amplified by Enterprise GenAI Deployments
With enterprise GenAI deployments on the rise, the ransomware risk is skyrocketing - after all, Microsoft alone detects over 38 million identity risk signals daily, a stark reminder that AI-enabled attacks can strike at any moment. As attackers supercharge their ops with AI, businesses are unwittingly increasing their vulnerability by deploying AI systems that can be exploited.
Ransomware gangs exploit victims' payments, extort again
Paying ransomware attackers doesn't always guarantee relief, with many victims being extorted again. A recent survey found 54% of organizations globally paid a ransom, yet it often doesn't end the attack.
Microsoft Ends Exchange 2016, 2019 Security Updates in October
Microsoft is ending security updates for Exchange Server 2016 and 2019 in October 2026, with no further extensions available, even for those currently in Period 2 of the Extended Security Update program. This marks the final cutoff for support, leaving organizations without updates after that date.
Law Enforcement Disrupts Kratos Phishing Kit Targeting Microsoft 365 Sessions
In a major win for cybersecurity, law enforcement agencies have dismantled the notorious Kratos Phishing Kit, pulling over 200 servers offline and disrupting thousands of phishing campaigns targeting Microsoft 365 sessions. The operation, coordinated with Indonesian authorities, is estimated to have impacted around 1,800 paying customers who were using Kratos to run approximately 15,000 phishing campaigns monthly.
Microsoft Azure DevOps Flaw Exposes AI Review Agents to Hidden Attacks
Imagine a hidden sentence that only AI sees, turning a reviewer's own AI agent into a vulnerability that lets attackers access projects they shouldn't - a chilling security flaw discovered in Microsoft Azure DevOps. This flaw, known as a confused-deputy vulnerability, was cleverly exploited in a proof of concept by Manifold Security.
JADEPUFFER Evolves to Target AI Models with Ransomware
JADEPUFFER's latest move is a game-changer: they're now using ransomware to destroy AI models, leaving encrypted artifacts irretrievable. This devastating attack can cost victims up to $500,000 or more in training and computing losses.
Authorities Disrupt Kratos Phishing Platform in Global Operation
In a major global crackdown, authorities have shut down Kratos, a notorious phishing-as-a-service platform that helped cybercriminals create fake Microsoft login pages to steal sensitive info. The takedown has disrupted a key tool used by over 1,800 customers to commit crimes like business email compromise and data theft.
FakeGit Campaign Exploits GitHub Repos to Spread SmartLoader Malware
Malicious actors have unleashed a massive campaign, using 7,600 fake GitHub repositories to spread the notorious SmartLoader malware, tricking victims into downloading malicious files disguised as popular tools like Gmail and Docker. The operation's convincing fake artifacts and manipulated repository metrics made it a highly effective and long-running threat.
North Korea's IT worker scheme fuels Russia's war effort
A shocking new report reveals that North Korea's IT worker scheme is secretly fueling Russia's war effort, with funds routed through a complex network to support multiple state objectives. The surprising twist: it's not just about North Korea's own weapons program, but also about arming Russia's military.
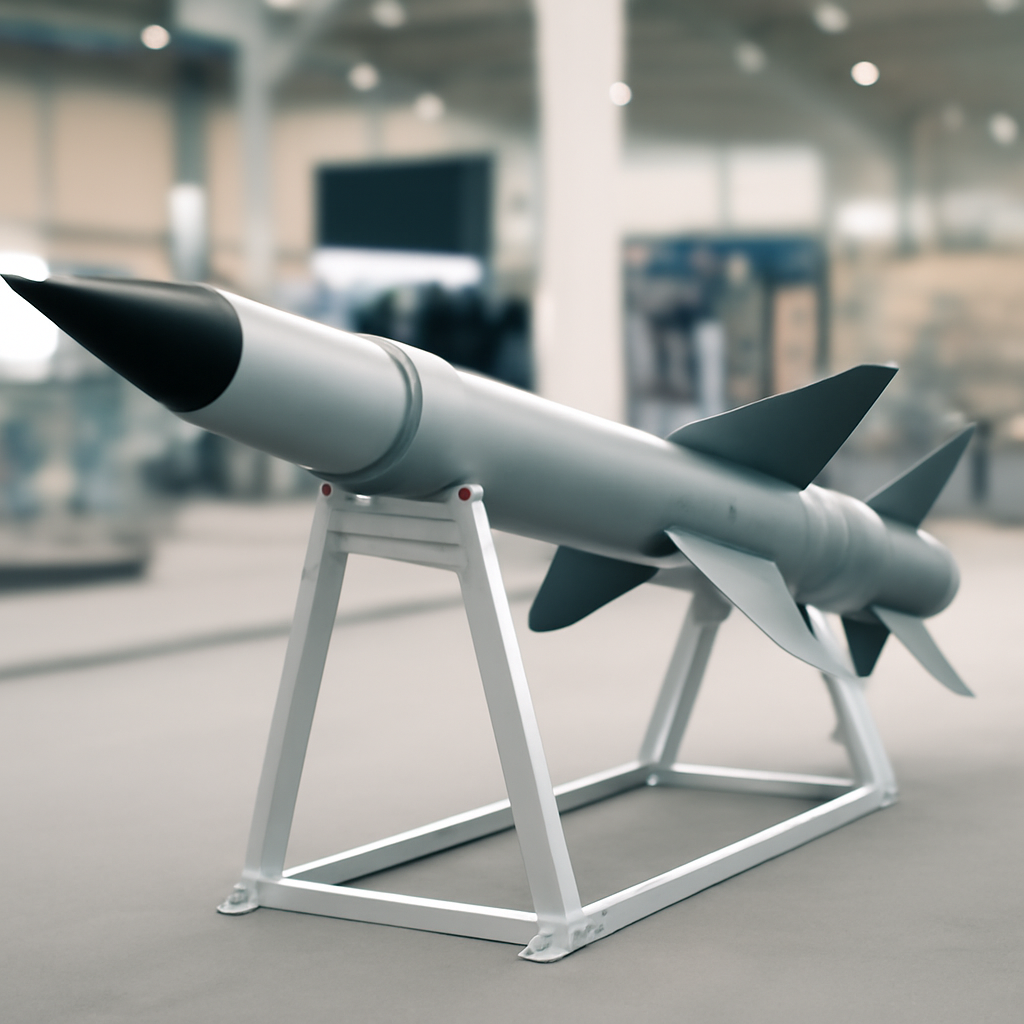
Lockheed Martin Unveils Cheaper Patriot Missile Variant
Lockheed Martin has just unveiled the Adapted Capability Effector (ACE), a game-changing, smaller interceptor that can take down short-range ballistic threats at an incredible 5,600 miles per hour. This cheaper alternative to traditional Patriot missiles can seamlessly integrate with existing PAC-3 infrastructure, making it a cost-effective solution for defense systems.
Pentagon Scrambles to Replace $21 Billion in Munitions Expended in Iran War
The Pentagon is in a frantic race against time to restock its depleted arsenal, urgently seeking $21 billion in emergency funds to replace the massive cache of munitions expended in just 11 days of conflict with Iran. Top officials, including War Secretary Pete Hegseth and Joint Chiefs Chairman Dan Caine, are scrambling to convince Congress to greenlight the request.
Anubis Ransomware Targets Coca-Cola's Fairlife, Threatens Data Leak
The Anubis ransomware gang has claimed responsibility for a cyberattack on Fairlife, a subsidiary of The Coca-Cola Company, boasting that they encrypted the company's systems and stole a whopping one terabyte of corporate data. With a deadline looming, the gang is threatening to leak the sensitive information unless Coca-Cola agrees to negotiate by the end of the week.
AWS Kiro Flaw Enables Remote Code Execution Through Poisoned Web Pages
Researchers just uncovered a major flaw in AWS Kiro that lets hackers execute remote code through manipulated web pages, putting developers' machines at risk. A simple request to summarize a webpage was all it took to expose this vulnerability.
Craneware Data Breach Exposes Healthcare Sector Risks
A recent data breach at Craneware, a software provider for healthcare, has exposed the sector to new risks, highlighting that the initial compromise is just the beginning of a larger story. The breach, which involved unauthorized access to a subset of data, has already revealed a significant volume of sensitive file names were viewed and exfiltrated.
Zero Trust Bolsters Critical Infrastructure Against Identity Threats
A single compromised account, like the inactive VPN login used to breach Colonial Pipeline in 2021, can have devastating ripple effects - just imagine a national crisis triggered by a simple vulnerability. The Colonial Pipeline ransomware attack is a stark reminder of the catastrophic consequences that can unfold when critical infrastructure is compromised.
Cloud Tenants Can Disrupt Power Grids With GPU Workloads
Researchers at Zhejiang University have made a startling discovery: ordinary GPU workloads in the cloud can be manipulated to disrupt power grids, and they've backed it up with measurements and simulations. By exploiting the link between a GPU's power draw and its computing activity, malicious cloud tenants can unwittingly - or intentionally - cause power grid instability.
Ransomware Attacks Exploited Compromised Identities in 79% of Incidents
Ransomware attacks are often sparked by something surprisingly simple: 79% of incidents start with compromised identities, highlighting the vulnerability of legitimate user logins and credentials. This means that in nearly 8 out of 10 cases, attackers gain a foothold using stolen or hijacked identities rather than complex hacking techniques.
Ransomware Landscape Fractures as New Groups Proliferate
The ransomware landscape is shattering into more factions than ever, with over one new group emerging every week in 2026, according to the Black Kite Ransomware Report. This explosion of new players has led to a surge in attacks, with 61 new groups appearing in just one year alone.
Microsoft Offers Manual Fix for WSUS Sync Delays
Microsoft has restored synchronization times and sync operations on WSUS servers for new installations and rebuilds, and is offering a manual fix for those still experiencing delays. The tech giant took swift action to address the issue, which was causing Windows Update scans to fail or time out, starting with a service-side mitigation on July 13.