Tag: supply chain
1740 articles
Global Missile Defences Erode as US Stockpiles Dwindle
The US is running perilously low on missile defenses, with depleted stockpiles of crucial Patriot and Thaad missiles threatening to leave the country vulnerable in the face of prolonged conflict. With as few as 70 Thaad rounds and 870 Patriot rounds remaining, lawmakers are sounding the alarm.
Feds Warn of AI-Generated Code Threat to Critical Infrastructure Controllers
The feds have issued a dire warning: AI-generated code is being used to actively threaten critical infrastructure controllers, putting industries like water, energy, and manufacturing at risk. This is a very real and present danger, not just a hypothetical threat.
Ransomware Affiliate Exploits Trust with Fake Recovery Service
A new scam is targeting ransomware victims, with a fake recovery service called Ransom Busters offering to provide decryption keys and delete stolen data for a hefty fee of $20,000 to $60,000. The impostors are preying on people's trust, contacting them via email and claiming to have access to sensitive information.
Clop Exploits PTC Zero-Day in Large-Scale Data Theft Spree
Clop's latest large-scale data theft spree exploited a critical PTC zero-day vulnerability, CVE-2026-12569, affecting supply chain systems used by manufacturers, retailers, and industries like aerospace and automotive. This attack continues Clop's trend of targeting SaaS logistics companies with zero-days to carry out mass-exploitation campaigns.
India, Japan Pursue Defense Tech Cooperation With Eye on China-Free Supply Chain
Japanese Defense Minister Koizumi Shinjiro is pushing for a game-changing partnership with India: building a China-free supply chain for defense equipment to bolster resilience and break free from Beijing's grip. By joining forces, India and Japan can create a robust defense production capacity that serves as a powerful deterrent.
TikTok Reversal Sparks Mobile Security Concerns
TikTok's recent U.S. entity shift has done little to alleviate mobile security concerns, as its privacy policy still raises red flags about invasive data collection and usage. Expert Matt Stern warns that the app's practices remain a threat to user data.
US Charges 17 Iranians in $3.4 Billion Intellectual Property Theft Scheme
The US Department of Justice has charged 17 Iranians with masterminding a massive, state-sponsored scheme to steal $3.4 billion worth of intellectual property from American universities, businesses, and government institutions. This brazen hacking operation allegedly involved a hacking-for-hire company called Mabna Institute.
Azure Exfiltration Campaign Exposes 3.6 Million Records
A shocking data breach has hit major players like McDonald's and Gap Inc., with a hacker claiming to have made off with a staggering 3.6 million Azure account records, including 1.7 million sensitive employee records from McDonald's alone. The breach exposes names, emails, addresses, and more, serving as a stark reminder that traditional security perimeters just aren't enough.
Linux Foundation's Akrites to Launch Vulnerability Platform in September
Get ready for a game-changer in vulnerability management: Akrites, launched by the Linux Foundation, is set to unveil a groundbreaking platform in September that streamlines AI-enabled vulnerability reports to open-source maintainers, ensuring swift fixes for the entire ecosystem. By doing so, it will revolutionize the way we tackle security incidents and vulnerability disclosure.
Hackers Exploit Dahua Devices via Credential Attacks and Auth Bypasses
Over 14,530 Dahua devices were compromised in a massive cyberattack, dubbed Operation CameraSwarm, which used credential attacks and authentication bypasses to gain control of cameras and other devices. The attackers hit hard in Ukraine and Russia, infiltrating devices via exposed credentials, flaws, and peer-to-peer relay tech.
Hackers Exploit 2,000 WordPress Sites in StopAndProtect Malware Campaign
This sneaky malware campaign, known as StopAndProtect, has already hacked nearly 2,000 WordPress sites, using a powerful toolkit that encrypts files, steals sensitive documents, and even lets attackers chat with their victims in real-time. The damage is widespread, with over 6,000 unique IP addresses affected worldwide.
Medusa Ransomware Targets Over 500 Infrastructure Orgs, Expands Tactics
Medusa ransomware has hit a staggering 500+ critical infrastructure organizations, with healthcare being a prime target, as reported in a recent FBI advisory. The attacks are happening at an alarming rate, with exploitation windows as short as 24 hours or even less.
Clop Ransomware Operation Exploits Windchill Flaw with Custom Web Shell
The Clop ransomware operation has exploited a critical flaw in PTC Windchill and FlexPLM servers, deploying a custom web shell that allows for easy credential theft and massive data exfiltration. This sneaky move gives attackers a direct path to sensitive data, with no extra tools needed.
Medusa Ransomware Targets Over 500 US Critical Infrastructure Orgs
The Medusa ransomware gang has struck a staggering 500+ US critical infrastructure organizations across multiple sectors, including healthcare, defense, and finance, since June 2021. This alarming surge in attacks has prompted a joint warning from top US agencies, highlighting the urgent need for heightened cybersecurity measures.
US Military Tests 3D Printing in War Games to Bolster Pacific Supply Lines
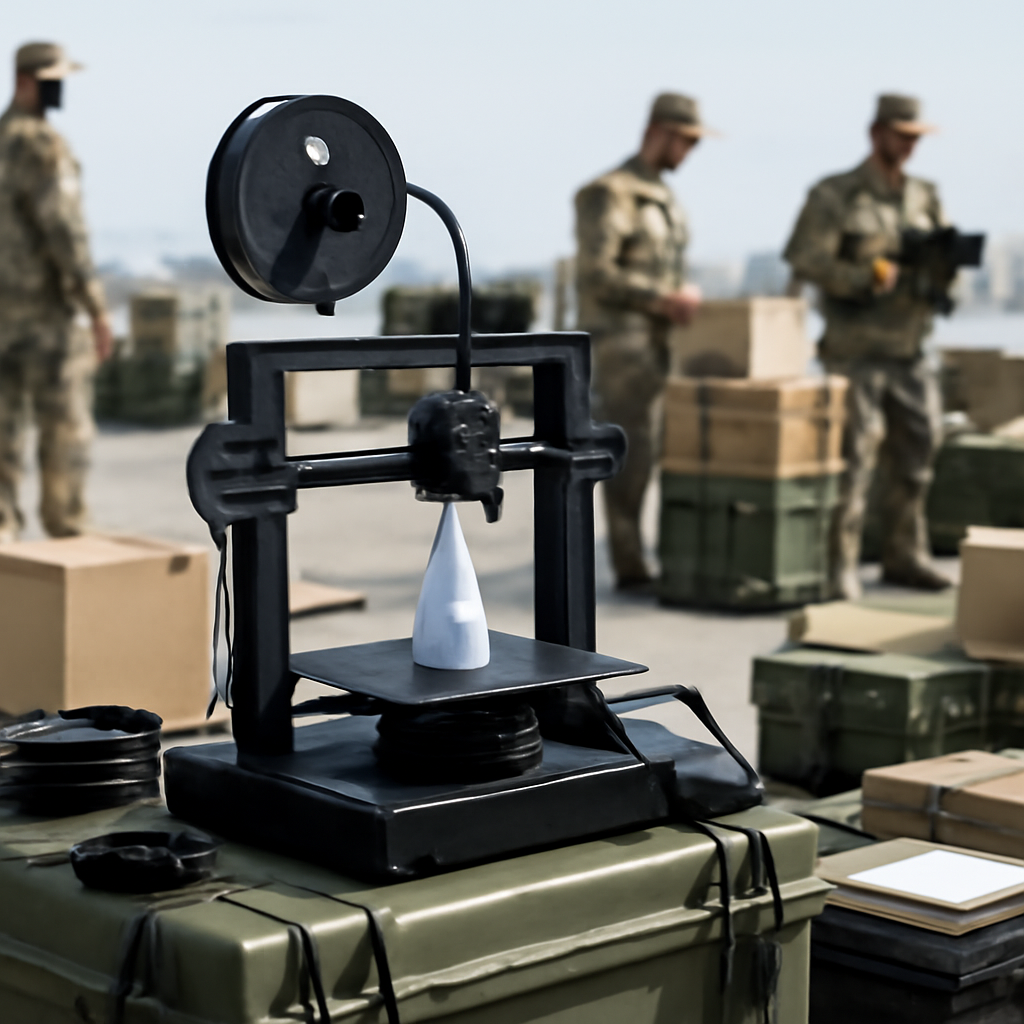
In a high-intensity conflict in the Indo-Pacific, the US military could struggle to meet its repair and resupply needs - a challenge that 3D printing may help alleviate. The Navy recently tested an experimental 3D printing network during the Rim of the Pacific wargames to see if on-demand production could ease logistics in a potential Pacific conflict.
Medusa Ransomware Expands Reach with New Tactics, Hundreds More Victims
The Medusa ransomware gang is on the loose, exploiting unpatched software to target hundreds of victims across various sectors, with the Healthcare and Public Health industry being a frequent hit. Now, US agencies have issued an updated warning, detailing the group's latest tactics and partnerships.
India Expands Air Defense with Helicopter-Based Drone Interdiction Tactics
India is taking its air defense to new heights with cutting-edge helicopter-based drone interdiction tactics, recently putting its skills to the test in a week-long exercise at the Pokhran firing range in Rajasthan. The country is set to bolster its defense capabilities with 156 additional helicopter units by 2032.
Clop Ransomware Gang Crafts Custom Web Shell for Windchill Attacks
The Clop ransomware gang has taken its attacks to the next level by crafting a custom Java web shell that specifically targets PTC Windchill and FlexPLM servers, allowing them to harvest sensitive data with ease. This tailored tool is a significant evolution of their mass-exploitation tactics, making it a major concern for businesses using these applications.
Supply Chain Hack Exposes Pokémon Center Customer Data
A recent supply chain hack exposed sensitive customer data at the Pokémon Center, but fortunately, the breach occurred through a third-party logistics partner, CEVA, and not directly through the retailer's own systems. The incident, triggered by CEVA's notification on July 30, compromised customer order details for Pokémon Center's UK and German shipments.
CISA Mandates Swift Fix for Exploited Ray RCE Flaw
A critical bug in the Ray framework, scoring 9.4 under CVSS v4, can be exploited for remote code execution with a simple visit to a malicious web page or hostile ad in Firefox or Safari. This vulnerability can be triggered when an attacker crafts requests that appear browser-originated, allowing for a potentially disastrous security breach.
NASA Ground Software Flaw Exposes Unauthenticated Command Functions
A critical flaw in NASA's open-source ground software, AIT-GUI, has been discovered, exposing it to unauthenticated command functions - and it's a big one, with a 9.4 CVSS rating. The vulnerability affects versions up to 2.5.1, but a fix is available in version 2.5.2.
Microsoft Copilot Exposes Vulnerability to Meta-Hacking
Researchers at Varonis Threat Labs uncovered a vulnerability in Microsoft Copilot, cleverly manipulating it to reveal its own weaknesses and craft a working attack, which they've dubbed CoSnitch. This surprising exploit was responsibly disclosed to Microsoft, which plans to issue a patch.
Ransomware Attacks Singly Target Mid-Market Firms
Ransomware attacks are hitting mid-market firms with alarming frequency, and the threat is only escalating as AI-powered tools rapidly uncover new vulnerabilities at an overwhelming pace. Mid-market companies, with revenues between $10m and $1bn, now account for nearly three-quarters of ransomware attack victims.
Russia Bolsters Long-Range Drone Launch Network Near NATO Borders
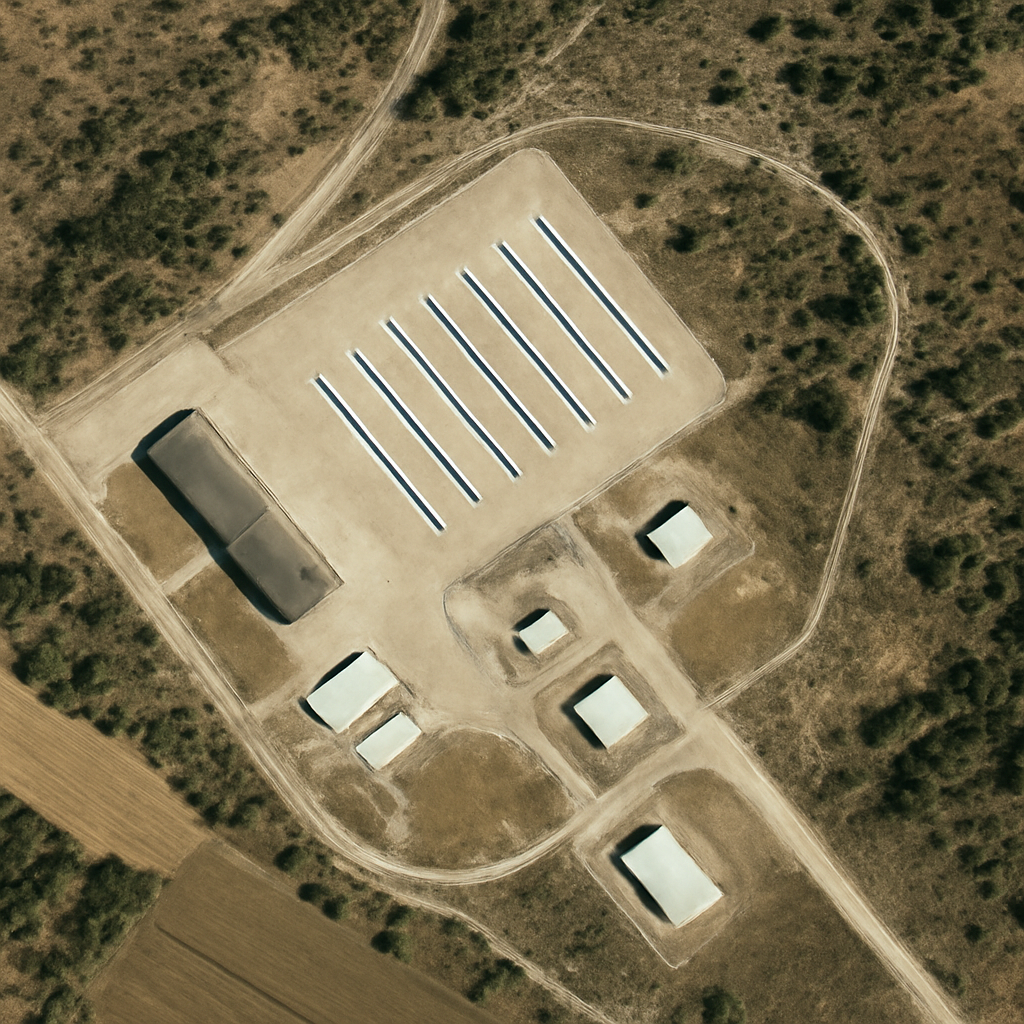
Russia is rapidly expanding its long-range drone launch network near NATO borders, with satellite images revealing at least 59 new launch rails capable of supporting advanced Geran-type drones. This alarming buildup is part of a broader effort to bolster its military capabilities, with many of these new sites already showing signs of active use in attacks on Ukraine.