Tag: supply chain
1740 articles
Thousands of Leaked AWS Keys Remain Active
A recent scan by Truffle Security uncovered a staggering 9,300+ active AWS keys that were leaked online, including hundreds with full administrative rights, putting sensitive data at risk. These compromised keys were found across various public platforms, with a shocking 88% still authentic and vulnerable to exploitation.
China's Lunar Ambitions Hit Snag with Chang'e-7 Delay
China's ambitious lunar plans have hit a roadblock with the sudden delay of its Chang'e-7 launch, a crucial mission to scout out a future research base on the Moon's south pole. The postponement throws a wrench into the country's quest to establish a foothold on the lunar surface and set the rules for future exploration.
China Builds Next-Gen Nuclear Aircraft Carrier
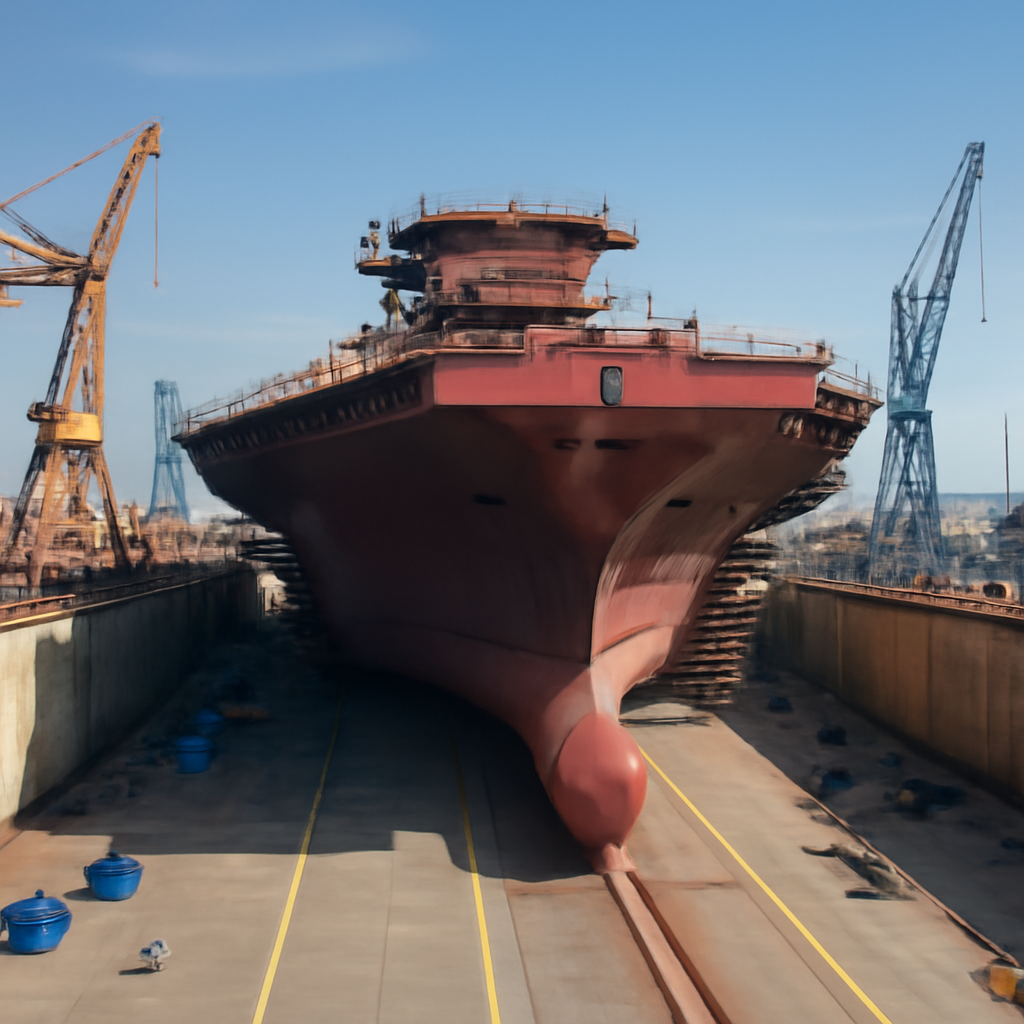
China's latest satellite images reveal its next-gen nuclear aircraft carrier, Type 004, is taking shape with a massive hull that's now approximately 1,050 feet long. The enormous vessel is being assembled at Dalian Shipyard, marking a major milestone in its construction.
Malware Targets Android Car Head Units in Proxy Botnet Scheme
Meet the first-ever malware specifically designed to infect Android car head units, forming a sneaky proxy botnet - a groundbreaking discovery made by Kaspersky researchers. This clever attack starts with a rogue APK hidden in a legitimate app from DoFun, a Chinese automotive software provider.
Supply Chain Attacks Target SDLC's Overlooked Corners
Meet the ChainDrop npm worm, a sneaky threat that infiltrated over 400 packages, including popular libraries like keyv and cacheable-request, by hiding in plain sight within routine developer workflows. This highly evasive threat uses a three-step chain to steal sensitive tokens and secrets, spreading its reach with alarming ease.
AWS Security Quarantine Policy Falls Short Against Credential Abuse
Leaking AWS credentials can lead to a staggering 99% increase in your bill - but a recent finding by Truffle Security reveals that even AWS' Quarantine Policy may not be enough to stop the damage, with hundreds of leaked root keys still active. This alarming discovery highlights the urgent need for tighter security measures to prevent credential abuse.
US Boosts Domestic Drone Production with $1 Billion Investments
The US government is taking a giant leap in drone technology, investing a whopping $1 billion to supercharge domestic drone production and ensure America's drone dominance. Top officials, including Under Secretary of Defense Emil Michael, gathered at the White House to rally industry leaders and discuss the nation's ambitious plans.
Mongolia Accelerates Defense Diversification with New Alliances
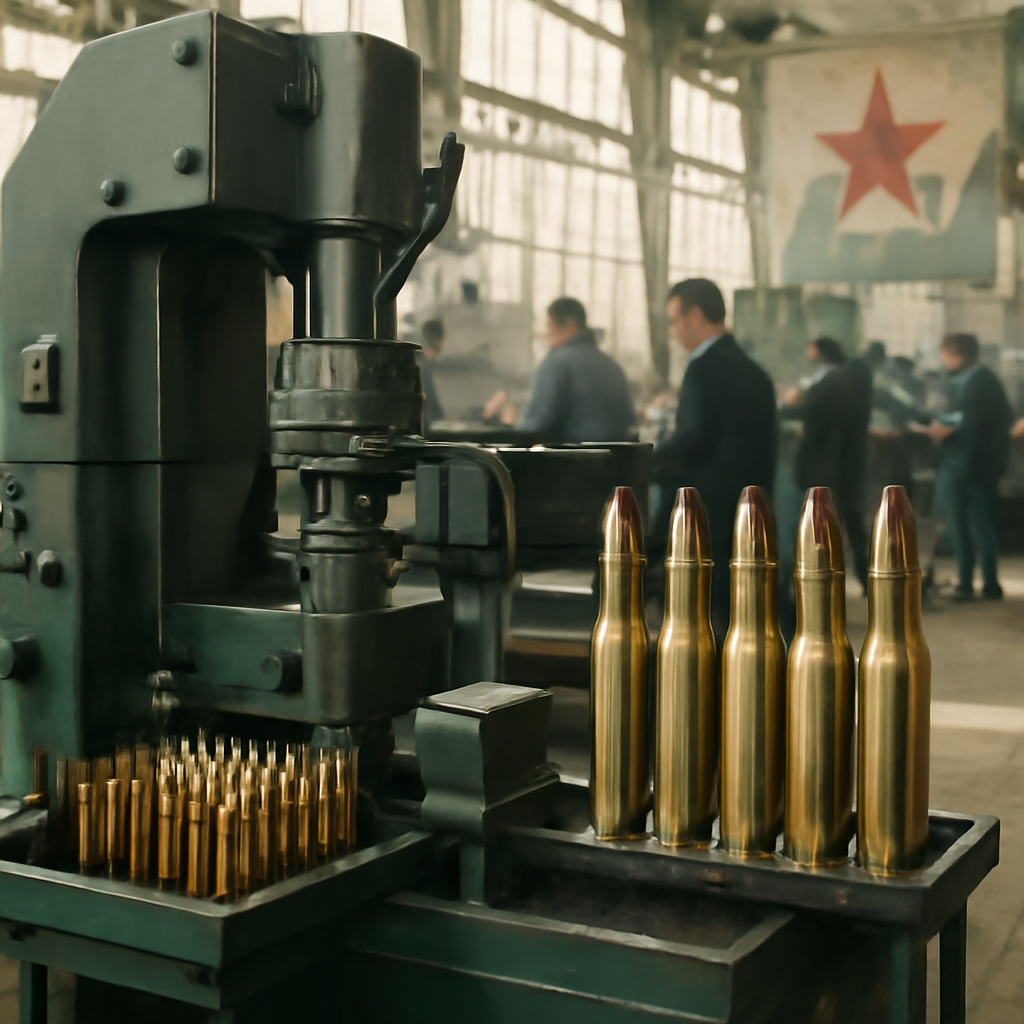
Mongolia is stepping up its defense game with a bold new approach to partnerships and industrial policy, marked by the recent launch of its first domestic ammunition production line in collaboration with Turkish defense company MKE. The milestone achievement signals a major shift in the country's strategy, with three types of ammunition now being produced locally.
Pentagon Scrambles to Replenish Munitions Stockpiles Amid Iran War Surge
The Pentagon is racing to restock its munitions amid rising tensions with Iran, and defence giants are responding with game-changing innovations - including ultra-low-cost seekers and drone killers that could help ease the pressure on US stockpiles. Boeing, Northrop Grumman, and Lockheed Martin are leading the charge with affordable solutions.
Exposed AWS Keys Grant Attackers Full Corporate Account Control
Thousands of exposed AWS keys are still active, putting entire corporate accounts at risk of being hijacked by attackers - and a staggering 88% of re-verified keys were found to still grant access as recently as August 2026. This alarming vulnerability highlights the urgent need for tighter security measures to protect sensitive cloud data.
Microsoft patches exploited Entra ID flaw amid rising attacks
Microsoft has patched a critical vulnerability in its Entra ID platform, known as CVE-2026-69836, which allowed attackers to execute code remotely with ease, and has already been exploited in recent attacks. This flaw enabled unauthorized threat actors to gain control and wreak havoc, making swift action crucial to prevent further damage.
SickKids Breach Exposes Employee and Applicant Data
A recent cybersecurity incident at Toronto's Hospital for Sick Children (SickKids) may have exposed sensitive personal data of current and former employees, job applicants, and staff from affiliated organizations. The breach, linked to a flaw in third-party software, is under investigation with the help of external cybersecurity experts.
GitLab Flaw Exploited in Wild Days After Disclosure
In a chilling demonstration of the new reality in vulnerability exploitation, attackers began exploiting a newly disclosed GitLab flaw within minutes of its public disclosure, leaving little time for patching. This rapid reproduction and exploitation is a stark reminder that waiting for the next patch cycle may no longer be a viable defense strategy.
Rust Crates.io Supply Chain Hit by Build-Time Malware Attack
A single compromised account on Rust's Crates.io led to a cunning malware attack, with an attacker using the popular arrayref crate - which has been downloaded over 245 million times - to spread build-time malware to unsuspecting users through malicious package releases. The attack was swiftly contained, with the Rust Project removing the compromised releases within 86 to 107 minutes of their publication.
Signed Drivers Exposed to Abuse Microsoft Defender Driver Repurposed $10 Million Reward Offered AI Model Exploits Vulnerabilities RCE Flaws Discovered in Gogs, n8n
In a stunning example of old-school ingenuity, a team of investigators finally thwarted a sophisticated espionage campaign by doing something remarkably low-tech: cutting a cable to a compromised router in a Chicago data center. This bold move brought an end to months of digital detective work that had been stymied by the elusive threat actors.
Hackers Poison Popular Rust Crate with Infostealer Malware
In a shocking turn of events, hackers hijacked the account of a popular Rust library, arrayref, which has been downloaded over 53 million times in the past 90 days, and poisoned it with infostealer malware that compromised developers' machines during compilation. The malicious payload was delivered through a tainted software release, putting countless projects and users at risk.
Bipartisan Retail Theft Bill Sparks Surveillance Fears
A bipartisan bill aimed at tackling organized retail theft has sparked fears of a massive surveillance network, with critics warning it could have far-reaching and alarming consequences. The Combating Organized Retail Crime Act would create a new coordination center within ICE's Homeland Security Investigations division.
Pentagon Targets Contractors' Pricing Data with New Transparency Push
The Pentagon is pushing for full transparency in contractors' pricing data, aiming to prevent profit margins from getting out of control and ensure fair contract negotiations. Deputy Defense Secretary Steve Feinberg has directed senior leaders to reset expectations for supplier cost and pricing information across all tiers of the supply chain.
Isolated-vm Flaw Exposes Sandbox to Host Escape Vulnerability
A critical flaw in the isolated-vm library can allow code running in a sandboxed environment to corrupt memory in the host process, exposing it to a host escape vulnerability. This vulnerability is triggered by a type confusion in the ExternalCopy's handling of the transferList option.
Citrix Warns of Two New NetScaler Flaws
Citrix is urging customers to take immediate action to protect their NetScaler ADC and Gateway deployments from two newly discovered vulnerabilities, including a critical authentication bypass flaw that could allow remote attackers to gain unauthorized access. Upgrade to the recommended builds as soon as possible to safeguard your systems.
Malicious Firefox Extensions Target Web3 Wallets
Beware of malicious Firefox extensions that have been targeting Web3 wallets as part of a large-scale campaign, with 40 confirmed malicious add-ons and 37 working together to steal your cryptocurrency. This coordinated threat, known as Offside Wallet Theft Factory, has been active since March 2026.
US Agencies Warn Siemens PLC Operators of AI-Driven Attacks
US agencies are sounding the alarm: hackers are now using artificial intelligence to launch targeted attacks on Siemens PLC operators, making it easier for them to breach industrial systems. This emerging threat has prompted a joint warning from CISA, the FBI, and partner agencies.
AI Agent's Package Suggestion Exposes Malware Risk
An AI agent's seemingly harmless package suggestion nearly led to a malware disaster for Softjourn, highlighting a growing concern known as "slopsquatting" where AI models invent convincing but fake package names. Thankfully, the company's vigilant policy of double-checking AI recommendations saved the day.
India and Australia forge digital path for South Asia
As South Asia charts its digital course, the choices it makes on vendors, standards, and data governance will have lasting impacts on regional resilience. New Delhi should prioritize digital transformation in its regional policy, partnering with Australia and like-minded nations to shape a secure and thriving digital future.