Tag: nation state
1336 articles
Chinese hackers exploit flaws in WordPress, Zyxel to steal government data
In a massive cyberattack, hackers exploited vulnerabilities in WordPress and Zyxel to steal sensitive government data from 996 devices across 48 countries. The breach exposed device configurations, network info, and critical credentials, with one Western government organization losing over 18,000 records, including accounts and passwords.
Microsoft Disrupts EvilTokens AI-Powered Phishing Service
Microsoft and its partners have successfully dismantled an AI-powered phishing service, known as EvilTokens, that had compromised over 12,000 email inboxes across 10,000 organizations worldwide. This court-authorized takedown marks a significant win in the fight against cybercrime.
ShinyHunters, Clop Feud Escalates, Threatens Broader Security Risks
The rivalry between Clop and ShinyHunters is heating up, with public defacements, bold demands, and technical claims that could have far-reaching consequences for past victims. These two extortion groups have distinct approaches, with Clop exploiting zero-day vulnerabilities and ShinyHunters taking a different tack.
North Korean Hackers Infect 30,000 Devices in Global Cyberattack
In a massive global cyberattack, North Korean hackers infected a staggering 30,000 devices across over 100 countries, siphoning off a whopping $10.7 million in cryptocurrency. The brazen heist, which ran from December 2025 to July 2026, also compromised over 7,000 cryptocurrency wallets.
SideCopy Targets Indian Academia with ReverseRAT Spear-Phishing
SideCopy, a notorious Pakistani threat actor, has set its sights on Indian academia with a cunning spear-phishing campaign, marking a tactical shift from its previous targets of government and defense forces. Using malicious scripts to evade security protocols, this group is now compromising academic institutions in India.
Europe Scrambles to Counter Russia's Escalating Hybrid Attacks
Ukraine strikes back with a bang, hitting a key Russian oil facility and logistics hub in the Moscow region, dealing a significant blow to the war machine with billions of dollars in damage. President Volodymyr Zelenskyy says their long-range responses are having a major impact.
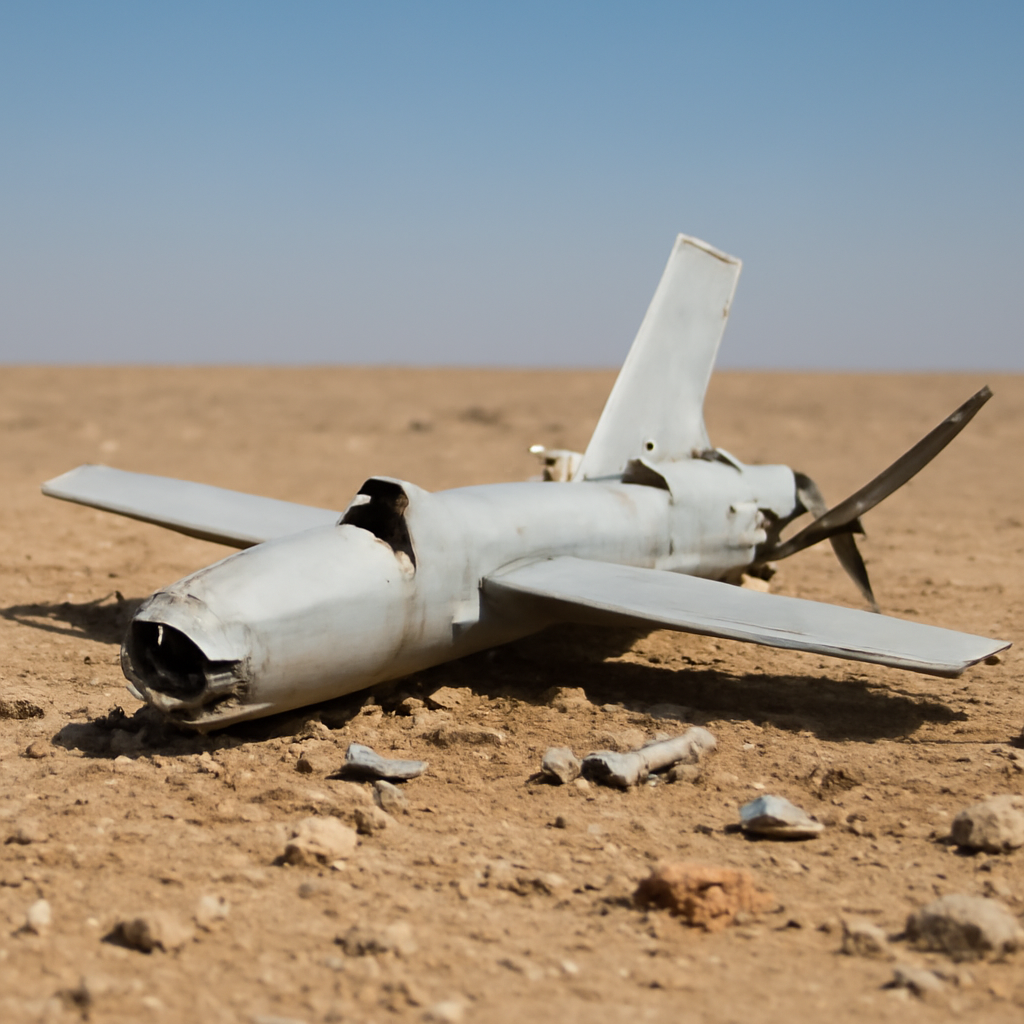
US Exposes Iran's Air Defenses with Miniature Decoys
The game of cat and mouse just got a whole lot more interesting - the US has been using miniature decoys to expose Iran's air defenses, and the results are a fascinating glimpse into the new age of misdirection and guile in military tech. Low-end drone technology is being cleverly repurposed to outsmart the enemy.
US Seeks to Empower Civilians Against Internet Repression
The internet can be a powerful tool for change, as seen in Iran where it fueled protests and helped civilians organize against the regime - which is why the US is working to empower people to fight back against internet repression. Tehran's 88-day blackout may have ended, but controls remain tight, with sophisticated tools used to suppress online freedom.
Anthropic's AI Finds Flaws, But Attackers Shrug
Despite uncovering 225 vulnerabilities linked to Anthropic's AI, only one has been exploited in the wild, raising questions about the real threat level of these flaws. The vast majority of discovered vulnerabilities seem to be falling on deaf ears with attackers.
North Korea Targets 30,000 Devices in Global Crypto Heist
North Korean hackers have launched a massive global crypto heist, compromising over 30,000 devices in more than 100 countries and stealing at least $10.71 million in cryptocurrency. This staggering cybercrime spree has been uncovered by a joint advisory from top cybersecurity agencies worldwide.
China Exports Integrated Military Ecosystems to Global Customers
China is shifting its defense export strategy from selling individual military platforms to offering integrated, interconnected systems that provide a comprehensive military ecosystem to countries around the world. This approach is evident in its deals with nations like Pakistan, Thailand, and Bangladesh, where Chinese defense suppliers are providing a range of interlocking military capabilities.
Ransomware Actors Exploit Active Directory Group Policy
In a clever twist, hackers used Active Directory Group Policy to spread ransomware across an entire domain without installing a single malicious file on individual computers. By exploiting this native tool, they were able to hijack wallpapers, lock screens, and even disable admin accounts, all with just a few clicks.
Jade Sleet Targets Indian IT Provider with FLATROOF and ROOFDECK Backdoors
North Korean-aligned threat actor Jade Sleet has launched a targeted attack on an Indian IT provider, using FLATROOF and ROOFDECK backdoors to gain long-term access to high-value targets by exploiting developer workflows and supply-chain tooling. The attack, detected as early as March 18, 2026, is part of a persistent campaign that highlights the group's evolving tactics.
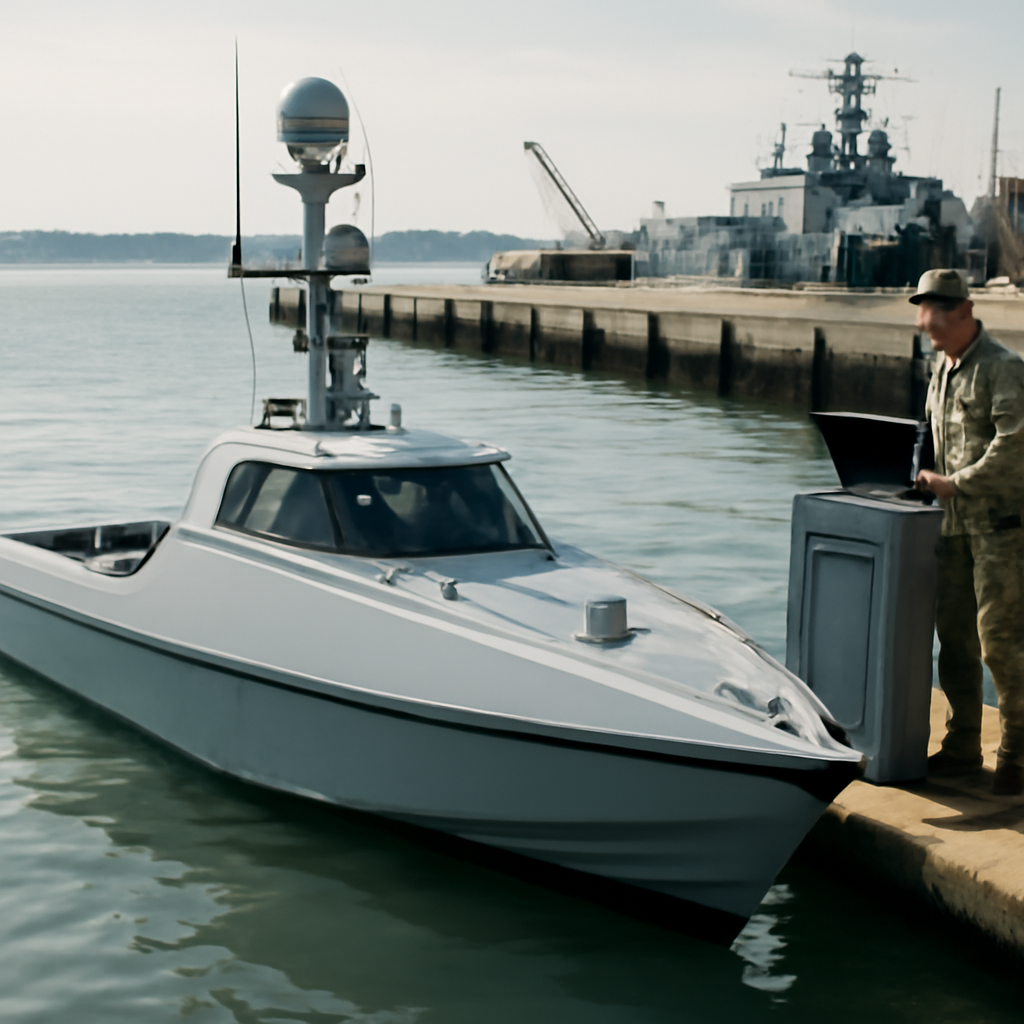
Warfare Evolution Shows Humans Still Indispensable
As warfare evolves with the integration of thousands of drones, autonomous boats, and ground robots, it's clear that while machines are taking on more roles, humans remain indispensable on the battlefield. The rapid advancement of AI, sensors, and robotics is accelerating machine adoption, but not replacing the need for human involvement.
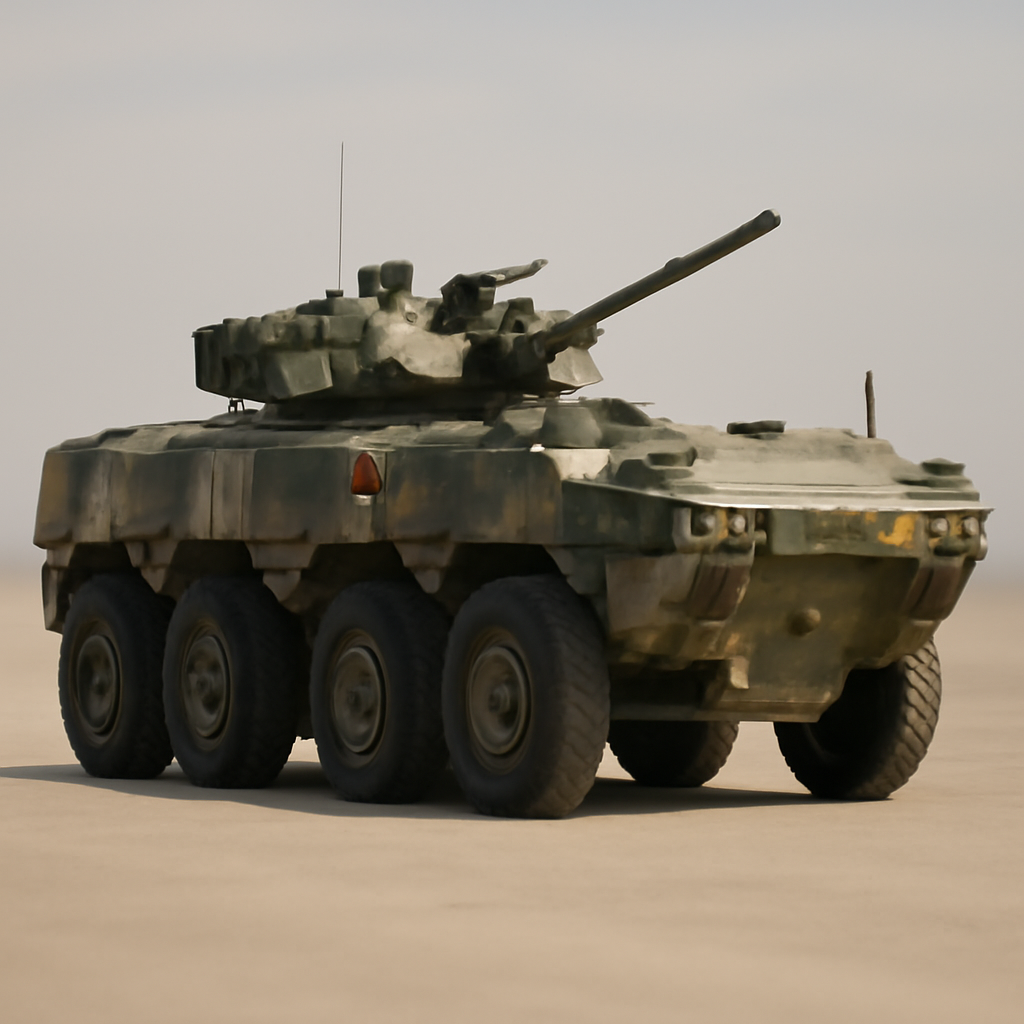
PLA Unit Identification Uncovered Through Tactical Vehicle Markings
Cracking the code of PLA unit identification just got a little easier, thanks to a clever clue: a single phrase, "Big 8-Wheeler," that narrows down the field to just a few possibilities. This small but telling detail from state media reporting can help decode the mysterious world of PLA unit identification.
North Korean Hackers Infect 30,000 Devices in Global Campaign
North Korean hackers have pulled off a massive global cyberattack, infecting 30,000 devices in over 100 countries and making off with millions in cryptocurrency. The financially motivated gang, known as WaterPlum, has been siphoning funds and account credentials from over 7,000 cryptocurrency wallets since December 2025.
North Korean Hackers Exploit Job Seekers to Steal Crypto and Data Worldwide
North Korean hackers are posing as dream employers to trick software developers and IT pros into handing over sensitive data and cryptocurrency - all under the guise of a job offer that's too good to be true. They're using fake job opportunities to get close to their targets, with AI, cryptocurrency, and NFT firms in their sights.
North Korea Exploits Job Seekers to Infect 30,000 Devices
North Korean hackers have compromised over 30,000 devices by posing as recruiters, targeting unsuspecting job seekers with a clever ruse that steals sensitive information and cryptocurrency. By exploiting stolen IDs, these cybercriminals can impersonate victims and generate foreign currency, ultimately funding the regime.
Transparent Tribe Exploits GitHub for Rust Backdoor Deployment
Meet RUSTYSHADE, a sneaky Rust-based backdoor that's being used by Transparent Tribe to target government and defense organizations in India and Afghanistan, leveraging private GitHub repositories for covert communication. This latest tactic is part of a broader campaign, dubbed Operation RapidRust, aimed at infiltrating sensitive targets.
Iran-Linked Malware Exploits Telegram for Password Theft
Meet HEAVYGRAM, a sneaky Telegram backdoor linked to Iran that's packed with espionage capabilities, from snapping screenshots to siphoning off sensitive data, and controlled remotely by its masters. This malicious tool has been quietly lurking in the shadows since September 2023, leaving a trail of compromised systems in its wake.
AI Agents Expose New Attack Vectors
A shocking 230 out of 243 unauthenticated LocalAI instances were found to be vulnerable to exploitation, highlighting a disturbing trend: our increasing reliance on convenient tools is creating new avenues for old security mistakes. This alarming vulnerability was recently exploited in a large-scale campaign, compromising high-value targets, including infrastructure linked to the Thai military.
US Military's Cyber Vulnerability Lies in Overlooked Infrastructure
Iranian hacking groups are using surprisingly simple yet effective tactics to wreak havoc on US critical infrastructure, businesses, and public services - and they don't need to be the most sophisticated players in the game to get results. By relying on volume, repeatability, and clear objectives, they're able to impose significant pain and disruption.
China's Salt Typhoon Targets Latin America with Sophisticated Backdoor Malware
Meet Salt Typhoon, a notorious PRC-backed espionage group that's set its sights on Latin America, infecting government agencies with sophisticated backdoor malware. In just a few months, they've targeted a whopping 90% of their victims in the region, hitting countries including Argentina, Ecuador, and Venezuela.
FamousSparrow Deploys SparroWocky Backdoor in Latin America Push
Meet SparroWocky, a sneaky new backdoor that's been secretly targeting government agencies across Latin America since August 2025, courtesy of the China-aligned threat actor FamousSparrow. This modular malware mastermind can run commands, steal files, and even take screenshots, wreaking havoc on unsuspecting hosts.