Tag: nation state
1337 articles
FamousSparrow Deploys SparroWocky Backdoor in Latin America Push
Meet SparroWocky, a sneaky new backdoor that's been secretly targeting government agencies across Latin America since August 2025, courtesy of the China-aligned threat actor FamousSparrow. This modular malware mastermind can run commands, steal files, and even take screenshots, wreaking havoc on unsuspecting hosts.
AI Automates Credential Theft, Threatens Identity Security
In under six hours, a single operation compromised thousands of third-party credentials, highlighting the alarming speed and efficiency of AI-powered credential theft. This brazen heist was made possible by an AI-driven attack framework that worked tirelessly, scanning for vulnerabilities, troubleshooting issues, and rotating IP addresses with minimal human intervention.
FamousSparrow Targets Latin America with SparroWocky Backdoor
Meet SparroWocky, a sneaky new backdoor that's helping the China-aligned threat actor FamousSparrow wreak havoc in Latin America. This modular C++ backdoor has been taking center stage since August 2025, replacing its predecessor SparrowDoor as the group's go-to tool.
CISA Promotes Decoys to Detect Breaches
Want to catch cyber attackers in the act? Planting decoy files, accounts, and credentials inside your network can expose machine-driven threats and help you detect breaches before they cause harm.
China-linked hackers deploy SparroWocky malware in Latin American govt espionage attacks
China-linked hackers are targeting Latin American governments with a new, sneaky malware called SparroWocky, designed to secretly collect intelligence on the region's responses to growing US pressure. The espionage campaign, tracked by ESET researchers, has hit government organizations in at least eight countries across the region.
Germany's Hybrid Threats Lesson: Underreaction Invites Sustained Coercion
Can democracies afford to sit back and let state-backed coercion, interference, and sabotage become the new normal - or will they take a stand and build the tools to detect, attribute, and respond to these threats before it's too late? Germany's recent experience with a foiled drone attack at Halle airport serves as a stark reminder that underreaction can invite sustained aggression.
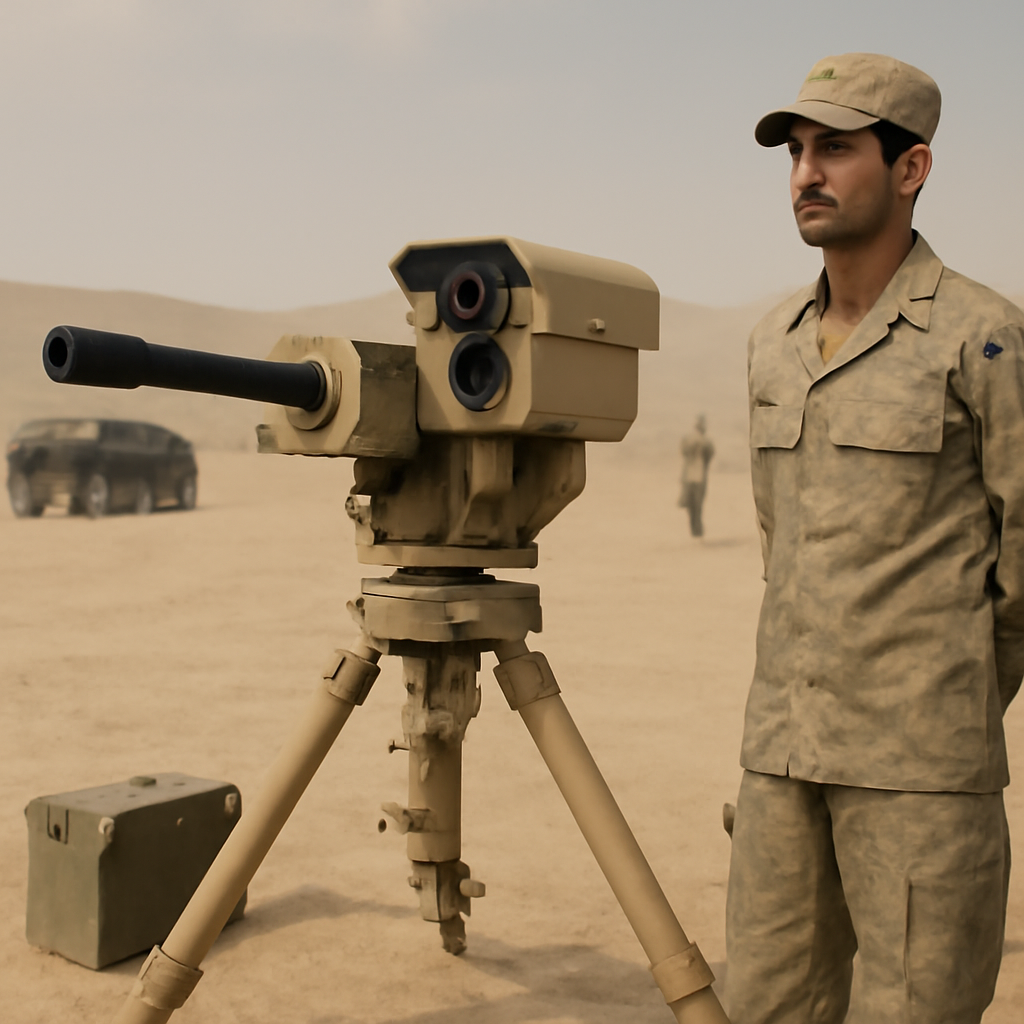
Pakistan Air Force Deploys ASELSAN ŞAHİN Counter-Drone System
Pakistan's public unveiling of ASELSAN's ŞAHİN counter-drone system marks a significant milestone in the country's defense capabilities, with the system boasting an impressive engagement range of up to 700m against mini and micro UAVs. This cutting-edge technology is set to revolutionize Pakistan's counter-drone operations.
Joint Chiefs Chairman Highlights AI's Growing Role in Combat Operations
The pace of decision-making in combat has accelerated dramatically, from weeks to days to mere seconds, and Air Force Gen. Dan Caine credits artificial intelligence for revolutionizing the speed and effectiveness of military operations. With AI, troops are now able to respond faster and smarter, as seen in recent events like the rescue of an Apache helicopter crew and the deployment of new AI-enabled tactics in Ukraine.
China's Anti-Piracy Mission Masks Maritime Military Expansion
Behind the guise of protecting global waters from piracy, China's naval forces are quietly expanding their military presence at sea. The PLA Navy's recent counterterrorism and anti-piracy drills are just the latest example of this strategic move.
Australia's Research Sector Divided Over Security Reforms
As Australia's research sector navigates new national security reforms, a pressing question emerges: can freedom and vigilance coexist? The country's top universities are already feeling the impact, with recent terminations of high-profile partnerships sparking a heated debate.
Iranian Hackers Deploy CHOSEN BRICK Malware to Spy on Global Targets
Meet CHOSEN BRICK, a sneaky Windows malware that's been used by Iranian hackers to turn everyday apps into long-term spying tools, helping the regime silence dissidents, activists, and journalists worldwide. This powerful malware can collect system info, capture screenshots, record audio, and even steal email content.
NightEagle Exploits Legitimate Tools to Target Russian Firms
Kaspersky's Global Emergency Response Team has uncovered a sneaky tactic used by the NightEagle group to target Russian firms, exploiting legitimate tools like compromised VPN credentials and Cloudflare WARP to gain initial access. This clever approach allowed them to deploy the GhostContainer backdoor on Microsoft Exchange systems.
US Coast Guard, FBI Intercept Foreign Ships to Investigate Cyberattacks
In a proactive move to safeguard the nation's maritime security, the US Coast Guard and FBI teamed up to board two foreign commercial tankers in the Gulf of Mexico, investigating suspected cyberattacks that could have put crew safety and environmental stability at risk. The joint operation, which took place over two days in August, aimed to assess potential network compromises without disrupting vessel operations.
Google Patches Zero-Day Flaw Exploited in Pixel Phone Attacks
Google just patched a high-severity zero-day flaw that allowed hackers to exploit Pixel phones with zero clicks - and federal authorities are urging you to update your phone ASAP. This critical vulnerability let attackers escalate privileges and bypass permission checks, but thankfully it's now closed with a simple update.
Taiwanese Back Military Exercises, But Understanding Lags
This year's Han Kuang military exercises in Taiwan didn't just happen on distant battlefields - they spilled into daily life, with troops barricading a major bridge and hospitals rehearsing underground medical ops. Even mobile internet was deliberately slowed to mimic the communication chaos of wartime.
Russian Enterprises Targeted by Backdoor, Ransomware Attacks from Three Threat Groups
Russian enterprises are under attack by three threat groups, with hackers exploiting compromised credentials to breach corporate VPNs and deploy powerful malware like GhostContainer, a modular backdoor that gives attackers complete control over Microsoft Exchange Servers. This sneaky malware can run arbitrary code, manipulate files, and hide in plain sight, making it a formidable foe for even the most secure systems.
Mandiant Exposes AI Coding Assistant Vulnerability to Shai-Hulud Worm
A hacker hijacked an AI coding assistant session, using it as a launchpad to deploy the Shai-Hulud worm across nearly 100 internal code repositories. This alarming incident highlights the vulnerability of AI-powered coding tools to exploitation.
Threat Intel Struggles to Close Exploitation Gap
In today's AI-driven landscape, merely knowing about potential threats isn't enough - the real challenge lies in rapidly testing and validating defenses against them. By harnessing AI-assisted exploitation, adversaries are swiftly turning exposure into breaches, leaving security teams scrambling to keep pace.
UK Warns of Iranian Spyware Campaign Targeting Dissidents
The UK's National Cyber Security Centre has warned that dissidents, activists, and journalists critical of the Iranian regime are being ruthlessly targeted by a Tehran-backed spyware campaign, which steals emails, messages, and device data to silence critics. This sinister campaign has even led to stolen info being leaked on pro-Iranian sites, putting lives at risk.
Cybersecurity Vendors Flock to UK's SE Labs Testing Program as MITRE ATT&CK Loses Momentum
As cybersecurity threats evolve at breakneck speed, SE Labs' innovative PIVOT testing program is drawing vendors in with its rigorous, adversary-driven approach to defense testing. By simulating real-world attacks, PIVOT helps vendors strengthen their defenses against the most devastating threats.
Space Force Waged Electronic Warfare Against Iran in Operation Epic Fury
The US Space Force isn't just a supporting player - it's a game-changer on the battlefield, delivering crucial space power to the fight. In a recent example, Space Force waged electronic warfare against Iran in Operation Epic Fury, providing direct support to the mission.
PLA's 69th Brigade Upgrades with Type 99B MBT
The People's Liberation Army's 69th Heavy Combined Arms Brigade has reached a major milestone in its modernization journey, now operating the advanced Type 99B MBT. This upgrade was showcased to the world during the September 2025 Victory Day parade, marking a significant leap in the brigade's capabilities.
Malware Exploits Chinese Casino Sites for Espionage
Uncover the dark side of Chinese-language casino sites: a vast network of seemingly harmless online casinos and adult sites is secretly harboring malware, facilitating espionage, and laundering money - with ties to major US cloud providers. These sites cleverly disguise themselves as legitimate entertainment hubs, using common templates and relying on the house edge to turn a profit.
Iranian Hackers Deploy Telegram-Controlled Malware to Infiltrate Dissident Networks
Iranian dissidents, journalists, and activists are in the crosshairs of Tehran's intelligence service, which is using sneaky Telegram-controlled malware to spy on and expose targets around the world, putting their personal safety and private lives at risk. This sinister campaign has prompted a joint warning from top cyber agencies in the UK, US, and Netherlands.