Tag: nation state
1342 articles
PhantomCore Exploits TrueConf Flaws to Breach Russian Networks
Researchers Daniil Grigoryan and Georgy Khandozhko revealed that PhantomCore attackers exploited a chain of three TrueConf Server vulnerabilities, including insufficient access control and file reading flaws, to breach Russian networks. This sophisticated attack highlights the importance of addressing these critical vulnerabilities to protect against potential threats.
Researchers Uncover Fast16 Malware That Preceded Stuxnet
Meet fast16.sys, a sneaky kernel driver that intercepts and modifies executable code as it's read from disk, giving its creators unprecedented control over the storage stack and filesystem. This boot-start filesystem component was a game-changer in its time, and researchers are still unraveling its secrets.
China Acquires Soviet T-72 Tanks Through Romania
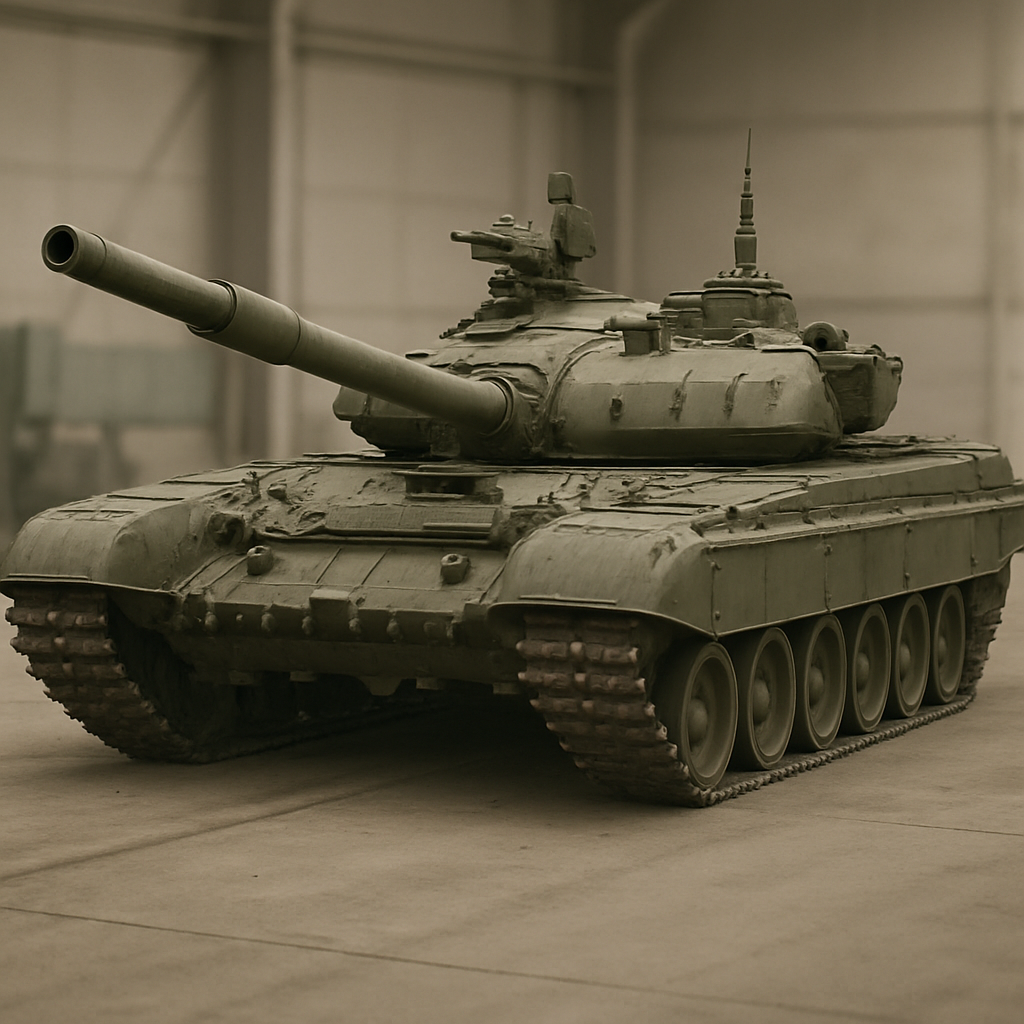
In a surprising move, China acquired Soviet T-72 tanks through Romania, with several of the 31 imported tanks quietly transferred to China for evaluation in the late 1970s. This acquisition was part of a long-running effort to understand and match Soviet tank design, sparked by the 1969 Zhenbao clash where Soviet T-62 tanks demonstrated clear technological superiority over Chinese armor.
Researchers Uncover 'fast16' Malware Targeting Engineering Software Years Before Stuxnet
Researchers have uncovered a long-forgotten malware, fast16, that was designed to sabotage engineering software, beating even the infamous Stuxnet by at least five years. This ancient cyber threat, dating back to 2005, was engineered to spread rapidly and produce inaccurate calculations across entire facilities.
US Warns of China’s Industrial-Scale AI Model Theft Campaigns
The White House has sounded the alarm on China's large-scale AI model theft campaigns, warning that stolen models, although imperfect, can still pose a significant threat. Unauthorized AI model distillation can enable foreign entities to develop knockoff versions with potentially damaging consequences.
TGR-STA-1030 Intensifies Espionage Push in Central, South America
The threat group TGR-STA-1030 is ramping up its espionage efforts in Central and South America, with sustained and widespread activity observed across multiple countries since February. This persistent campaign has recently intensified, with a heavy focus on regions within Central and South America.
Firestarter Malware Evades Cisco Firewall Updates, Persists Across Reboots
A custom backdoor called Firestarter has been discovered evading Cisco firewall updates and persisting across reboots, posing a significant threat to cybersecurity. This sophisticated malware is attributed to a threat actor linked to cyberespionage campaigns, including the notorious ArcaneDoor operation.
CISA Exposes Persistent FIRESTARTER Backdoor in Cisco Devices
CISA and NCSC have uncovered a sneaky FIRESTARTER backdoor lurking in Cisco devices, allowing hackers to regain control even after patches are applied. This persistent threat can leave devices vulnerable to re-entry, putting your entire network at risk.
US Warns of Coordinated AI Model Extraction Campaigns by Foreign Adversaries
The US government has sounded the alarm on a critical threat: foreign adversaries are launching coordinated, large-scale campaigns to steal American AI capabilities, specifically targeting the distillation of advanced US AI models into smaller, lighter-weight versions. To combat this, the White House is directing federal agencies to collaborate with the private sector to develop best practices for protection.
Netherlands Confronts Mounting National Security Threats from Russia, China
The Netherlands is facing its most severe national security threat in 80 years, with Russia and China emerging as the primary sources of pressure, according to the country's domestic intelligence service. This prolonged and multi-directional threat has been described as the gravest national security threat since World War Two.
NASA Targeted in Chinese Phishing Scheme for U.S. Defense Software
For years, unsuspecting NASA employees and collaborators were duped into sharing sensitive US defense software with a Chinese national masquerading as a colleague, in a brazen phishing scheme that went undetected for years. The scam funneled top-secret aerospace and defense tech to the imposter, violating US export control laws in the process.

Tropic Trooper Exploits SumatraPDF to Deploy AdaptixC2
Meet Tropic Trooper, a notorious cyber threat group that's been wreaking havoc since 2011, and learn how they've cleverly exploited SumatraPDF to deploy their AdaptixC2 malware. Their latest tactic involves using GitHub as a command-and-control platform to target Chinese-speaking individuals in Taiwan, as well as users in South Korea and Japan.

Researchers Uncover Pre-Stuxnet Cyber-Sabotage Malware
Meet fast16, a stealthy cyber-sabotage malware that went undetected until now, marking a new era in covert statecraft. Discovered by SentinelOne researchers, this silent threat has been hiding in plain sight since 2016.
China Builds Covert Hacker Networks with Compromised Routers
China-nexus cyber actors have dramatically changed their game, ditching solo operations for massive networks of hacked devices - and it's a threat you need to know about. A joint advisory from top cyber agencies worldwide warns of this new tactic, urging vigilance in the face of large-scale cyber attacks.

Navy Overhauls Refueling Tactics Amid Iranian Attacks
When Iranian missile and drone attacks disrupted traditional refueling operations, the US Navy was forced to rethink its logistics strategy, shifting from fixed port hubs to a more agile approach using commercially chartered tankers to fuel ships at sea. This pivot, dubbed a move from port hubs to "tanker treadmills," has been a game-changer for keeping naval vessels operational in the region.
US Military Embraces Autonomous Weapons for Future Warfare
The US military is betting big on autonomous weapons, with Joint Chiefs Chairman Gen. Dan Caine declaring they'll be a crucial part of future warfare, driving innovation in areas like drones and command-and-control systems. Gen. Caine is pushing for a cultural shift within the Pentagon to fully harness the power of AI and autonomous technology.

Surveillance campaigns exploit telecom vulnerabilities with commercial tools
Researchers have uncovered a shocking truth: telecom vulnerabilities are being exploited by covert surveillance campaigns using commercial tools, putting global telecommunications security at risk. This alarming trend allows unknown parties to track targets undetected, highlighting a pressing need for tighter regulations.

New Malware ZionSiphon Targets Water Plants, Falls Flat
A new piece of malware called ZionSiphon, reportedly targeting Israeli water facilities, has been found to be surprisingly inept, with experts describing it as broken and showing little understanding of its supposed targets. The malware's code includes strings referencing the Israeli water sector and politically charged messaging, but its overall incompetence has downplayed initial alarm.

Pentagon Rapidly Deploys 100,000 Custom AI Agents
The Pentagon has made a groundbreaking leap with its custom AI agents, deploying an astonishing 100,000+ agents in record time and racking up over 1.1 million user sessions. This explosive adoption has seen an average of 180,000 sessions per week, showcasing the military's eagerness to harness the power of AI.
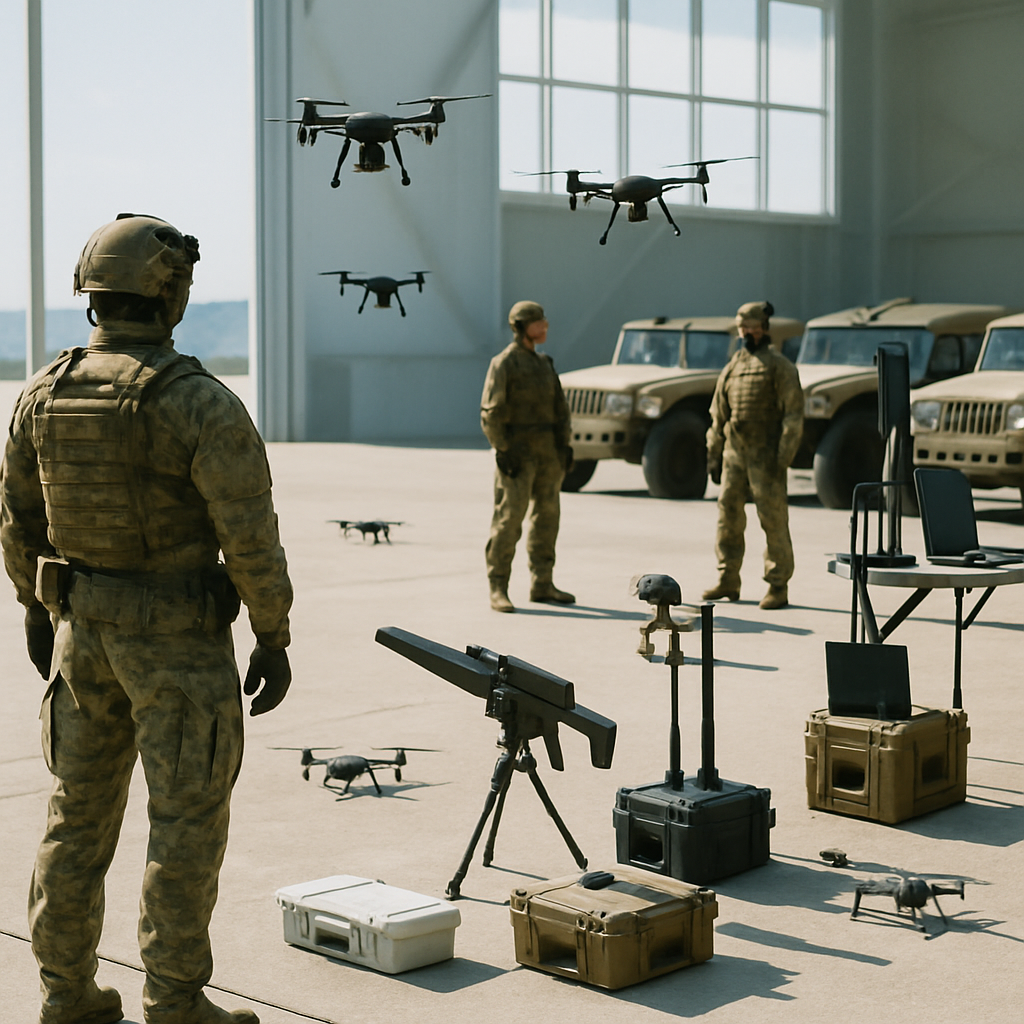
Pentagon Overhauls Counter-Drone Strategy After Ukraine-Style Exercise
The Pentagon has overhauled its counter-drone strategy after conducting a Ukraine-style exercise, dubbed Operation Clear Horizon, which simulated the "spiderweb" drone attacks used by Ukrainian forces against Russia. This hands-on test helped shape the military's priorities for countering the growing threat of drones.
US Misjudged Iran, Paving Way for Decades of Conflict
In 1977, President Jimmy Carter hailed Iran as an "island of stability" - a label that proved drastically off the mark just months later when mass demonstrations erupted, fueled by deep-seated economic and social divisions. His glowing praise of Shah Mohammad Reza Pahlavi's leadership had ominously overlooked the warning signs of a revolution brewing.

China-Linked Hackers Exploit Global Infrastructure in Covert Network Attacks
Be on high alert: China-linked hackers are secretly building global covert networks using compromised routers and devices, putting anyone who's a target at risk of devastating cyber attacks and data theft. This sinister plot, revealed by a joint advisory from 16 government agencies worldwide, has far-reaching implications for organizations and individuals alike.
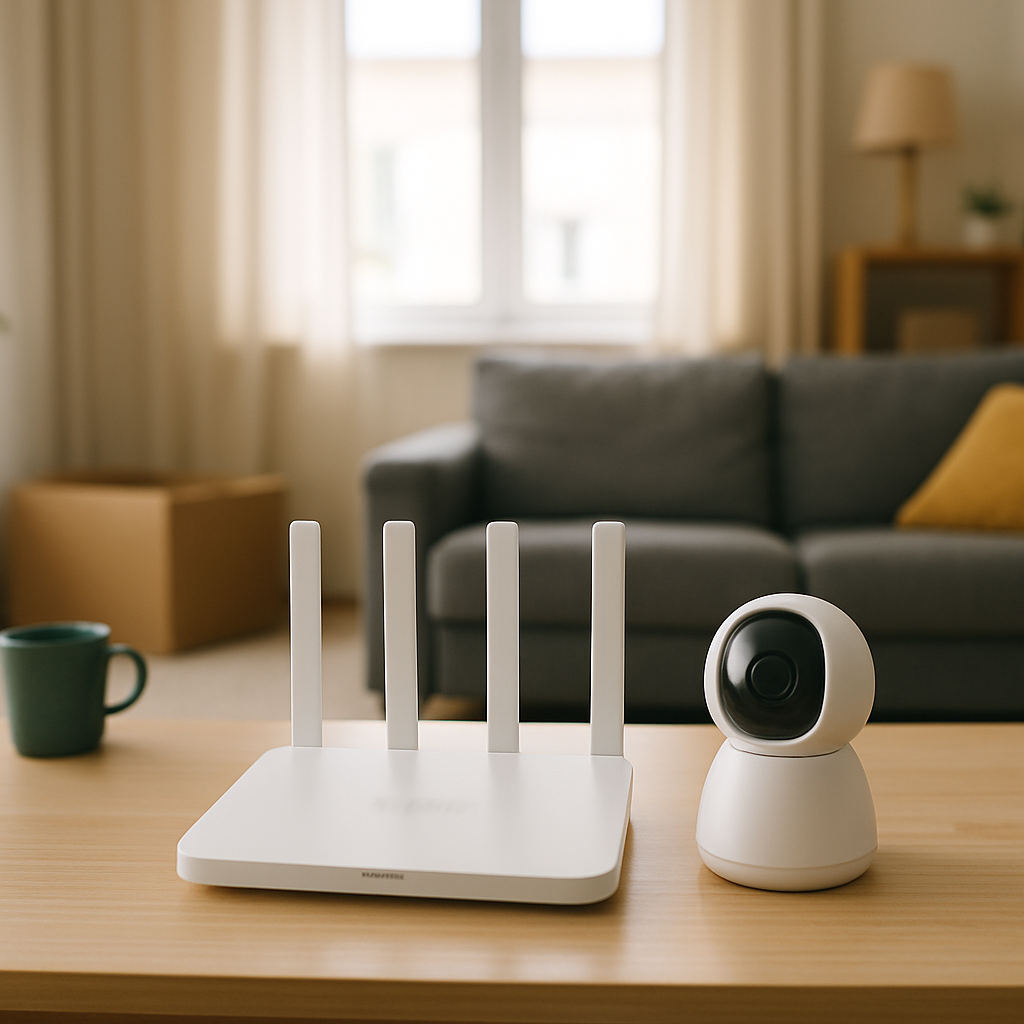
Chinese Hackers Exploit IoT Devices to Obscure Nation-State Attacks
Chinese hackers are sneaking nation-state attacks under the radar by hijacking everyday IoT devices, such as home routers and smart cameras, to hide their digital footprints. This stealthy tactic allows them to evade accountability and strike from the shadows.

Cyberattacks Exploit Known Flaws in Supply Chain, AI Tools
A recent cyberattack exploited weaknesses in a company's infrastructure, resulting in a staggering $290 million heist from KelpDAO, highlighting the vulnerability of supply chains to targeted attacks. The attackers manipulated key nodes to gain control and siphon off funds.