Tag: nation state
1342 articles
UNC6692 Exposes Custom Malware Suite via Social Engineering
In a clever social engineering ploy, UNC6692 launched a massive email campaign in late December 2025, flooding targets with messages to create a sense of urgency and distraction, before following up with a convincing Microsoft Teams message that pushed a malicious link. The attackers then cleverly disguised their malware as a legitimate "Mailbox Repair and Sync Utility" patch, hosted on an Amazon S3 page.
AI Targets Cloud Environments With Autonomous Attacks
Imagine a future where AI launches devastating cloud attacks with minimal human intervention - a threat that's no longer theoretical, but a harsh reality as demonstrated by a recent state-sponsored espionage campaign where AI executed 80-90% of the attack autonomously. Palo Alto Networks' Unit 42 has taken this threat to the next level by building a proof-of-concept AI model called Zealot that can execute end-to-end cloud attacks.
UK Warns of Chinese Hackers' Proxy Network Tactics to Evade Detection
The UK's National Cyber Security Centre has warned that Chinese hacking groups are using a sophisticated network of proxies to evade detection, with multiple covert networks constantly being updated and used by multiple threat actors. This alarming shift in tactics has prompted a coordinated warning from the NCSC-UK and nine international partners.

China-Linked APT Group Exploits Legitimate Services for Covert Ops
ESET researchers have uncovered a treasure trove of clues, analyzing 6,044 Slack messages and 3,005 Discord messages that reveal the covert operations of a China-linked APT group, dubbed GopherWhisper, which has been active since at least 2023. The recovered logs provide a rare glimpse into the group's tactics, thanks to hardcoded credentials in Go-based backdoors that gave investigators access to the group's command and control channels.
Eset Exposes Chinese Hackers' Careless Backdoor Tactics
Chinese hackers have been caught off guard by their own carelessness, leaving behind a digital trail that exposed their previously undetected backdoor tactics. Researchers uncovered over 9,000 messages revealing the attackers' testing systems and habits, leading to the identification of a Chinese nation-state actor dubbed GopherWhisper.
China-Linked GopherWhisper Targets Mongolian Government Systems with Go Backdoors
A China-linked cyber group, dubbed GopherWhisper, has been targeting Mongolian government systems with a suite of Go-based backdoors, infecting at least 12 systems and potentially dozens more. The attackers used clever tactics, routing command-and-control traffic through compromised Discord and Slack servers.
Iran Escalates Ship Attacks in Strait of Hormuz
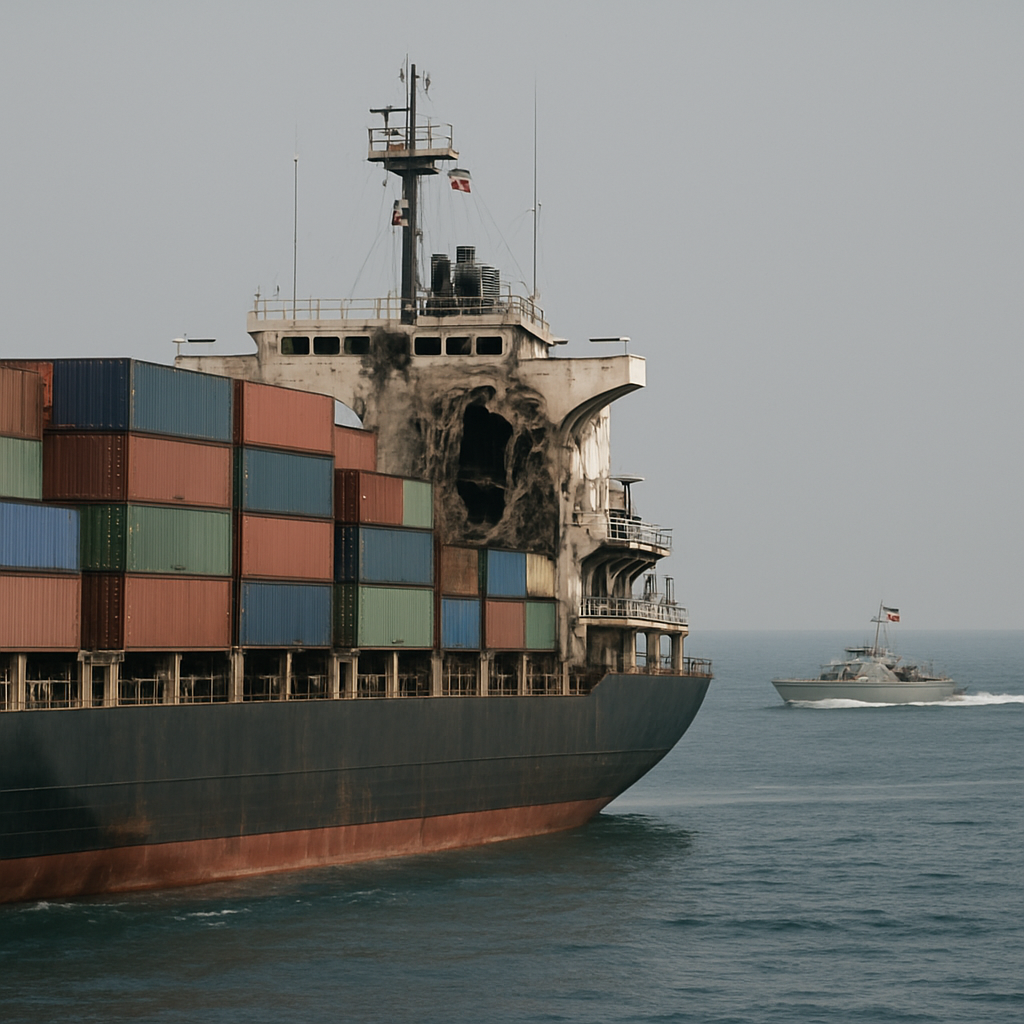
A container ship narrowly escaped disaster in the Strait of Hormuz after an Iranian gunboat fired on it, causing significant damage to the bridge, but thankfully no injuries or environmental harm. The alarming incident is the latest escalation in a series of attacks in the region, heightening tensions in this critical waterway.
Iran Outmaneuvers US in AI-Powered Meme Warfare
The White House is fighting back in meme warfare, racking up over 2 billion impressions with humorous clips from Call of Duty and SpongeBob SquarePants - but its goals differ greatly from Iran's strategic online tactics. While the US aims to energize its domestic supporters with lighthearted content, Iran is quietly shaping its own narrative.
AI-Driven Cyberthreats Expose Need for Advanced Threat Intelligence
In today's hyper-fast cyber threat landscape, operating at machine speed is no longer a choice - it's a necessity, as expert Tom Kellermann warns, highlighting the urgent need for advanced threat intelligence to combat AI-driven attacks.
UK Confronts Escalating Russian Cyber Hostility
The UK is facing a sharp rise in Russian cyber hostility, with the National Cyber Security Centre now investigating around four major attacks every week. This surge in threats has led to a significant increase in cases, with over 200 nationally significant incidents handled last year - more than double the previous year's total.
UK Battles Rising Russian Cyber Hostility
The UK is facing a surge in Russian cyber hostility, with the National Cyber Security Centre (NCSC) now handling around four major attacks every week and over 200 nationally significant incidents annually. This alarming trend highlights the growing importance of cyber operations in modern warfare.
Kyber Ransomware Targets Windows, VMware with Post-Quantum Encryption
Meet the Kyber Ransomware, a potent threat that targets both Windows and VMware environments with cutting-edge, post-quantum encryption. This sophisticated malware has been found to strike multiple systems at once, as seen in a March 2026 incident where two variants were deployed on the same network.
Harvester Expands Linux Arsenal with GoGra Backdoor in South Asia
Harvester's Linux arsenal just got a boost with the deployment of the GoGra backdoor in South Asia, enabling the threat actor to sneak past traditional network defenses by hijacking legitimate Microsoft Graph API and Outlook mailboxes. This latest move is linked to Harvester's earlier espionage campaigns targeting key sectors in the region.
China Fuels Iran's Conflict with Dual-Use Tech Transfers
China has reportedly supplied Iran with a commercial reconnaissance satellite, giving Tehran the capability to strike US military facilities in the Middle East with precision. This move has escalated tensions in the region, with Chinese companies Earth Eye Co and Emposat allegedly involved in the transfer.

Lotus Wiper Malware Disrupts Venezuelan Energy Sector
Cybersecurity researchers uncovered a highly destructive malware, known as Lotus Wiper, that was used to disrupt Venezuela's energy sector in a targeted attack. This powerful data wiper was deployed in a series of devastating attacks at the end of 2025 and beginning of 2026.

Former Ransomware Negotiator Pleads Guilty to Aiding BlackCat Cyber Gang
A former ransomware negotiator turned rogue, Angelo Martino has pleaded guilty to aiding the notorious BlackCat cyber gang, betraying his employer and the industry he was meant to serve. By secretly collaborating with BlackCat, Martino launched devastating ransomware attacks, causing harm to innocent victims and lining his own pockets.
Harvester Malware Exploits Microsoft Graph API for Stealthy Linux Attacks
Meet Harvester, a stealthy espionage group believed to be state-backed, that's been secretly targeting telecommunications, government, and IT organizations in South Asia since 2021. Their latest trick? A Linux-capable GoGra backdoor that uses Microsoft Graph API for covert communications.
Mustang Panda Expands LOTUSLITE Malware to Target India, Korea
Meet the evolved LOTUSLITE backdoor, now wielding dynamic DNS-based command-and-control over HTTPS, enabling its operators to remotely access and manipulate targeted systems for espionage purposes. This sophisticated malware supports remote shell access, file operations, and session management, a potent toolkit for data collection and access persistence.
UK Faces Rising Nation-State Cyber Threats Amid Tech Advances
The UK is bracing for a perfect storm of cyber threats, with the National Cyber Security Centre warning of a tumultuous decade ahead, driven by rapid technological change and rising geopolitical tensions. Nation-state threats from China, Russia, and Iran are already targeting UK firms, with 204 significant incidents recorded in the last review.
Lawmakers Weigh Terrorism Labels for Hospital Ransomware Attacks
Lawmakers are considering slapping terrorism labels on ransomware attacks targeting hospitals, a move that could lead to severe penalties for those responsible, as Rep. Michael Guest says there should be no penalties too severe for individuals that target the healthcare system. This tough stance comes as experts and officials discuss ways to deter the growing threat of hospital ransomware attacks.
Former Ransomware Negotiator Pleads Guilty to Extortion Scheme
A former ransomware negotiator has pleaded guilty to masterminding a brazen extortion scheme that raked in a staggering $75.3 million, exploiting his position to secretly collude with ransomware gangs and betray the very companies he was supposed to protect. Angelo John Martino III faces up to 20 years in prison for his role in the conspiracy.

Ex-FBI Chief Urges Homicide Charges for Ransomware Actors Tied to Patient Deaths
It's time to hold ransomware attackers accountable for their deadly actions - Cynthia Kaiser, ex-FBI chief, urges prosecutors to consider felony homicide charges when attacks on hospitals result in patient deaths. Closing the gap between crime severity and consequences is crucial, she stresses.

Lotus Malware Targets Venezuelan Energy Firms with Data-Wiping Attacks
A new, highly destructive malware called Lotus has been targeting Venezuela's energy sector, leaving systems completely unrecoverable after wiping data and disabling recovery mechanisms. This devastating attack systematically deletes files and overwrites physical drives, causing irreversible damage.
macOS ClickFix Attacks Harvest Credentials via AppleScript Stealers
macOS users beware: a sneaky ClickFix campaign is using AppleScript stealers to harvest credentials from 14 browsers, 16 cryptocurrency wallets, and over 200 extensions. This targeted attack has already made off with a staggering amount of sensitive info - and it's still on the loose.