Tag: nation state
1333 articles
China-Linked Hackers Expose Email Portal With Stolen Data
Meet Integrity Technology Group, a China-based company with ties to the government that's been caught red-handed running a web portal that lets others snoop on stolen emails. The US and UK have already slapped sanctions on the company, but the details of its shady operation are only now coming to light.
AI-Powered Pentesting Tool Exploited in South Korean Financial Data Heists
Meet ARTEX, an AI-powered pentesting tool that was originally designed for learning and research, but was repurposed by hackers to steal sensitive data from South Korean financial organizations. In a shocking campaign, attackers used ARTEX to breach security and get away with valuable information.
UAC-0099 Deploys ASHVEIN RAT in Targeted Attacks on Ukrainian Government Personnel
Meet ASHVEIN, a sneaky new malware that's helping Russia-aligned hackers steal sensitive info from Ukrainian government targets - and hiding their tracks in clever, invisible ways. This .NET infostealer and remote access trojan is a master of disguise, blending credential theft, surveillance, and remote control features to fly under the radar.
Pakistan Tests Fatah-4-ER, Hints at Future Missile Upgrades
Pakistan just took a major leap in its missile capabilities with the successful test of the Fatah-4-ER cruise missile, a move that signals its commitment to advancing its defense technology. This latest development hints at a future of upgraded missile variants, putting Pakistan at the forefront of modern military innovation.
Russia-Aligned UAC-0099 Refines MATCHBOIL Malware
The operators of UAC-0099, a group likely aligned with Russian interests, have been steadily refining their MATCHBOIL malware, making it a more potent tool for future attacks. This deliberate evolution shows a clear intent to evade detection and enhance the malware's flexibility.
UK, Germany Forge Cybersecurity Alliance to Counter Russian Threats
Britain and Germany are joining forces to tackle the growing threat of Russian cyberattacks, as Prime Minister Andy Burnham and Chancellor Friedrich Merz meet in Berlin to strengthen their countries' security partnership. The alliance aims to safeguard infrastructure, businesses, and democracies from the increasing danger of cyber sabotage.
Chinese Hacker Exploits AI in South Korean Bank Data Heist
Meet the new face of cybercrime: AI-powered hacking. A Chinese hacker recently used agentic AI tooling, alongside traditional tactics, to pull off a massive data heist at a South Korean bank.
FBI Warns of Ongoing FortiBleed Threat to Fortinet Devices
The FBI and US Secret Service have sounded the alarm: a whopping 86,644 Fortinet devices across 194 countries are compromised, and the FortiBleed threat is still very much active, leaving organizations at risk of being locked out of their own systems. This widespread campaign targets Fortinet FortiGate firewalls and SSL VPN gateways, putting businesses and individuals on high alert.
US Offers $10 Million Bounty for HAFNIUM Hacking Suspect
The US government is putting out a $10 million reward for information that leads to the identification or capture of Zhang Yu, a Chinese national accused of being involved in the notorious 2021 Microsoft Exchange Server attacks as part of the HAFNIUM hacking group. This move sends a strong message to others who help hide China's cyber operations: they could be next.
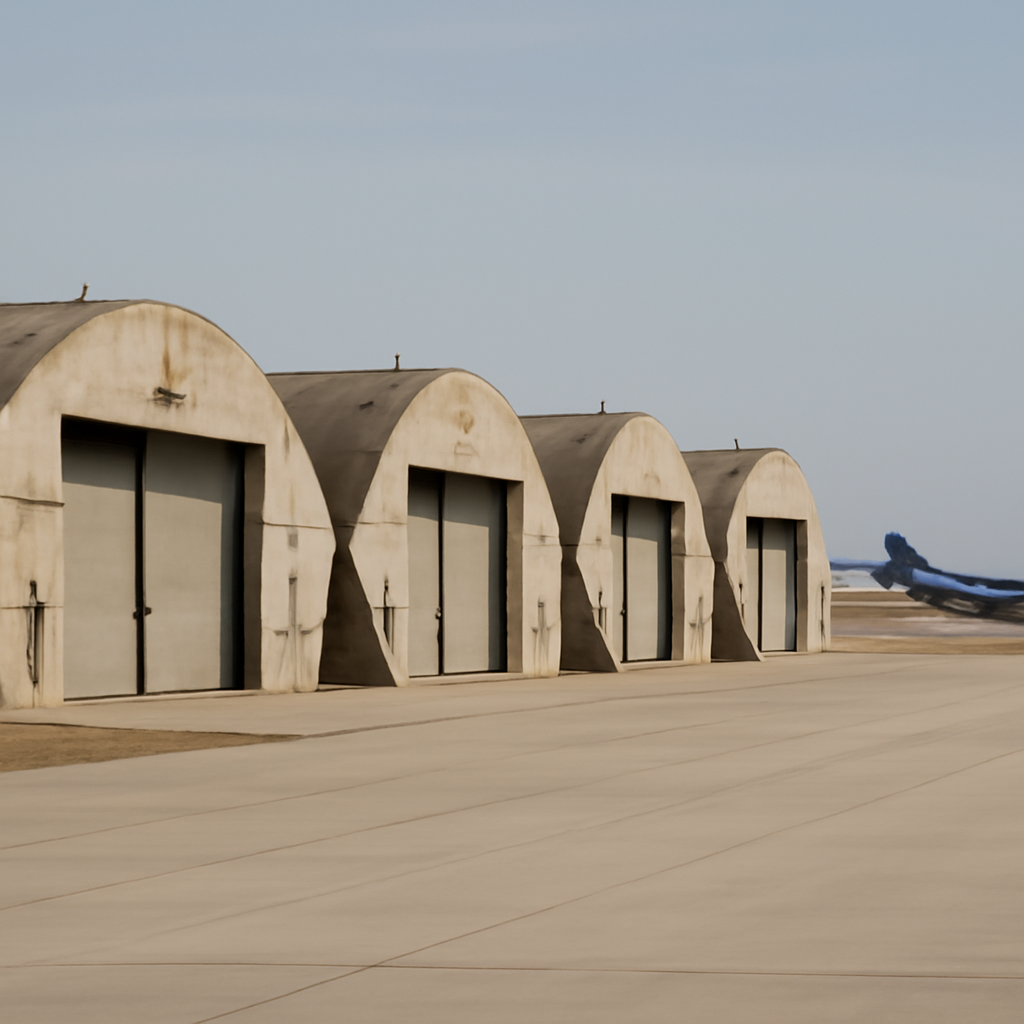
Pentagon Exposes Lagging Investment in Hardened Aircraft Shelters
The sudden departure of B-1 bombers from RAF Fairford in the UK was no coincidence - US President Donald Trump revealed that credible threats had prompted their removal, narrowly averting a potential attack on the base. The bombers had been stationed at the forward bomber hub since March, supporting operations against Iran.
FBI Warns of Ongoing FortiBleed Attacks Targeting Fortinet VPN Admins
Tens of thousands of Fortinet FortiGate firewalls and SSL VPN gateways are under active attack by hackers leveraging a massive June credential leak, putting countless networks at risk of disruption. The breach, known as FortiBleed, exposed a staggering 73,932 firewall URLs across 194 countries, giving attackers a treasure trove of vulnerable targets.
Hackers Exploit ccTLD Vulnerabilities to Hijack Google Domains
Google revealed that several top brands and online services were hit by the same attacks, following their initial mitigation efforts. Attackers exploited vulnerabilities in country-code top-level domain (ccTLD) registries and DNS to hijack Google domains, not by breaching Google's infrastructure, but by compromising third-party operators.
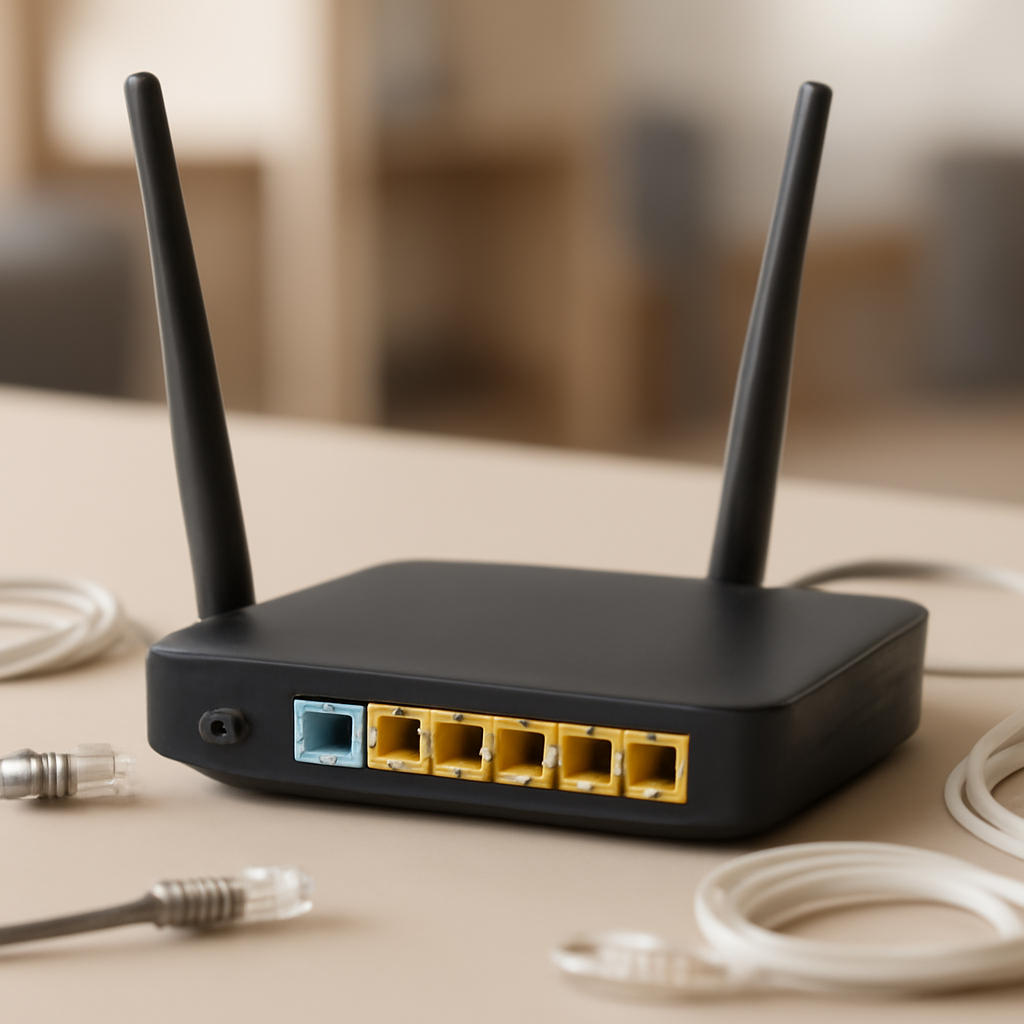
States Sue TP-Link, Citing China Ties and Router Security Risks
Four states are taking TP-Link to court, claiming the router maker has been dishonest about its security and hiding its ties to the Chinese government, putting sensitive data and national security at risk. Iowa's Attorney General Brenna Bird warns that Iowans' personal info is vulnerable due to TP-Link's alleged deception.
ShinyHunters' Teen Ringleader Detained Amid Extortion Attempt
A teenager known as "Rey," suspected of leading ShinyHunters, has been detained in Amman, Jordan, and is cooperating with the FBI after the group allegedly attempted to extort a Boeing business unit. The group's exploits began with a PeopleSoft vulnerability, fueling a wave of data thefts.
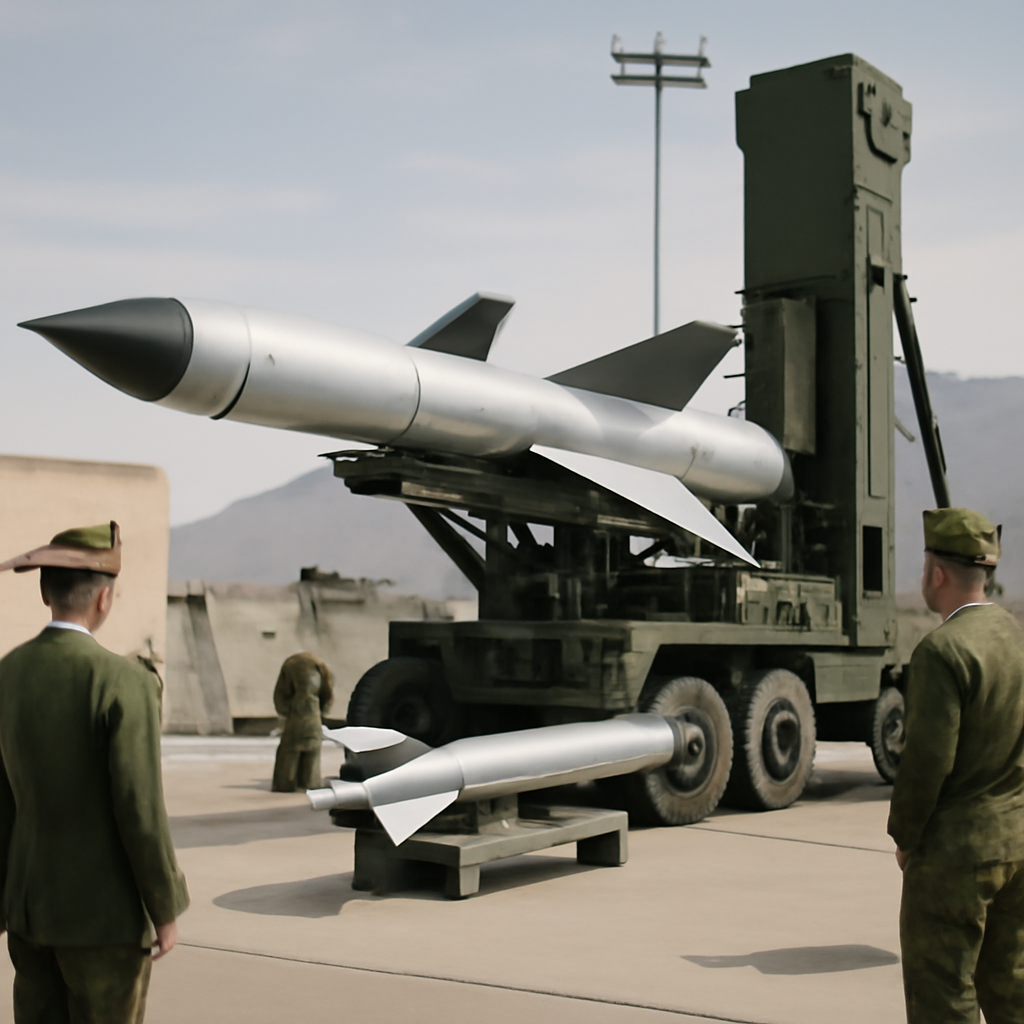
Pakistan Unveils Fatah-4 ER Cruise Missile with Extended Range Capabilities
Pakistan just took its military capabilities to the next level with the unveiling of the Fatah-4 ER cruise missile, a game-changing addition that can strike targets with pinpoint precision and devastating force at extended ranges. This powerful new missile was successfully test-fired on October 6, showcasing its impressive accuracy and survivability.
US Allies Expose Gaps in Nuclear Signaling Coordination
The real challenge isn't a lack of firepower, but a lack of common language and procedures among the US, Australia, Japan, and South Korea - a gap that's becoming increasingly critical as their advanced conventional capabilities start to intersect with nuclear strategies in the Indo-Pacific.
Ransomware Targets Backup Infrastructure, Pressuring Payouts
Ransomware attackers are now targeting backup infrastructure, leaving victims with a harrowing choice: pay up or lose everything. UnitedHealth's $22 million ransom payment was a stark reminder of this new reality, as they still didn't recover their data.
FBI Warns of Ongoing FortiBleed Threat Targeting Fortinet Devices
The FortiBleed threat is still on the loose, putting 86,644 vulnerable Fortinet devices across 194 countries at risk of being compromised, with attackers exploiting reused credentials and weak password storage to gain control.
FBI Warns of Ongoing FortiBleed Attacks Targeting Fortinet Firewalls
Beware: ongoing FortiBleed attacks are putting Fortinet firewalls at risk, with some victims potentially getting locked out of their own devices if attackers delete or change account passwords. The FBI and US Secret Service have issued a joint warning about this sustained threat.
Ransomware Attack Exposes Advantest Data
In a shocking cybersecurity breach, Advantest Corporation fell victim to a ransomware attack in February 2026, exposing sensitive data to an unauthorized third party. The Japanese tech giant revealed that threat actors infiltrated its network, deploying a ransomware payload and potentially compromising personal data.
CERT-UA Warns of 100+ Sites Serving LunexStealer via Fake Cloudflare Checks
Beware of over 100 compromised websites serving up the nasty LunexStealer malware by masquerading as a Cloudflare verification page - just a click away from trouble! When you visit these sites, you're tricked into executing a command that lets the malware swipe your sensitive info.
NSA Overhaul Seen as Necessary to Counter Faster Cyber Threats
The world has changed dramatically, and it's hard to imagine the NSA not evolving to keep pace with rapidly advancing cyber threats. A proposed overhaul is likely necessary, but its success will depend on careful execution.
FBI Warns of Ongoing FortiBleed Threat
The FBI and Secret Service are warning organizations that the FortiBleed threat is still active and can have a devastating impact, locking you out of your own systems if attackers disable accounts or change passwords. This is more than just a simple credential theft - it's a serious security risk that requires immediate attention.
Iranian State-Backed Actor Targets Iraqi Infrastructure
In a chilling move, Iranian state-backed hackers launched a stealthy campaign, dubbed Blinder Tunnel, that infiltrated Iraqi critical infrastructure by tricking developers into opening a booby-trapped Visual Studio project file. This cunning attack unfolded in three swift steps, allowing the hackers to execute malicious code without triggering a compile or user-run binary.