Tag: nation state
1333 articles
Australia Urges 'Sovereign Orchestration' to Bolster National Resilience
Australia is on a mission to strengthen its national resilience by mastering "sovereign orchestration" – the art of bringing together diverse capabilities across government, industry, and international partners to achieve a unified strategic impact. By coordinating without commanding and governing without owning, the nation aims to safeguard its critical interests with precision and agility.
China's People's Armed Police Bolster Aerial Capabilities with Militarized Helicopters
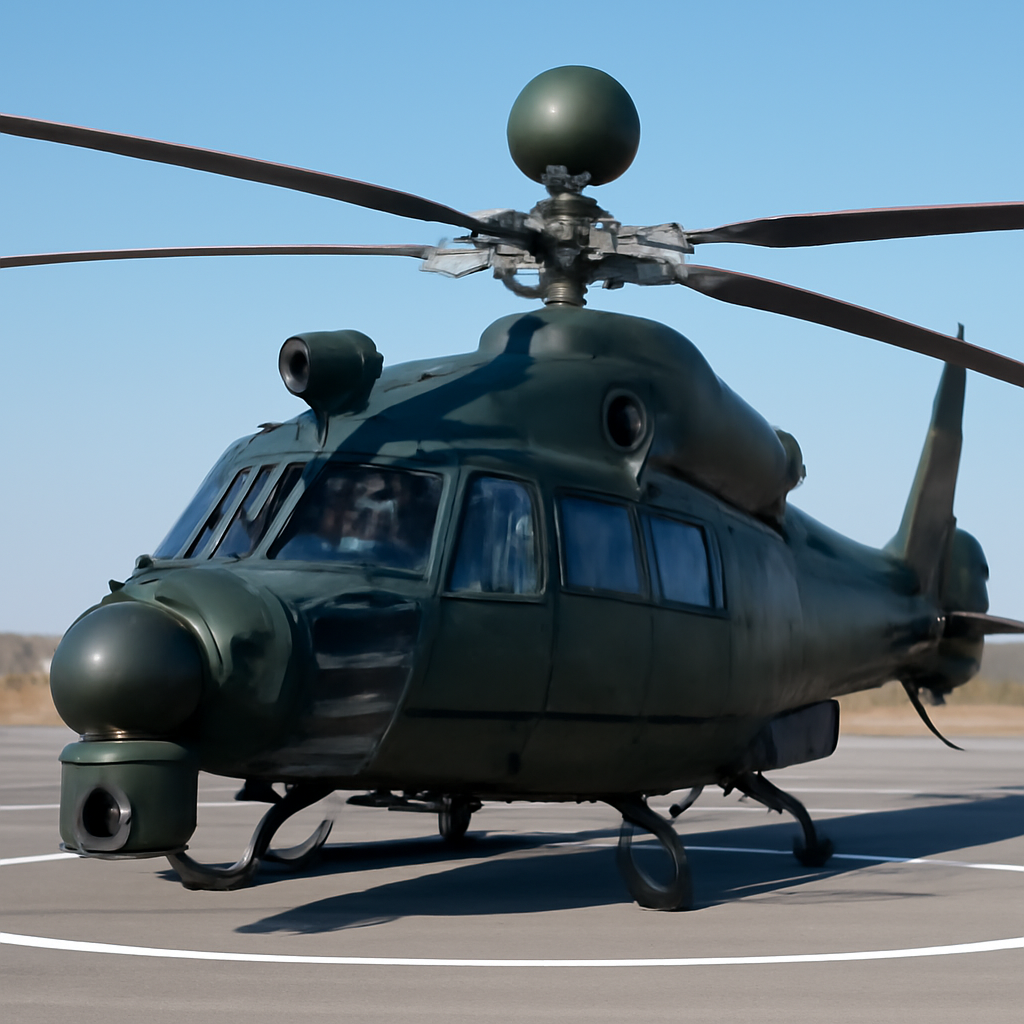
The People's Armed Police are taking their aerial capabilities to new heights with a fleet of militarized helicopters, including the Z-20, Z-8, Mi-171, and Z-9WA models, which are equipped with advanced features like mast-mounted sights, FLIR systems, and apparent weapon carriage. These helicopters, painted in the PAP's distinctive dark green color scheme, look more like a military force than a conventional police air support unit.
FBI Arrests Ransomware Negotiator in ShinyHunters Probe
In a major breakthrough in the ShinyHunters ransomware probe, the FBI has arrested a key player - a ransomware negotiator - in Pennsylvania, dealing a significant blow to the group that's extorted over $70 million from victims so far this year. The suspect, Edward Dobrovsky, faces charges of conspiracy and interference with commerce by threats.
FBI Arrests Cyber Exec Tied to ShinyHunters Hacking Group
In a stunning move, the FBI has arrested a Canadian cybersecurity executive with ties to the notorious ShinyHunters hacking group, taking another suspected co-conspirator off the streets. Edward Dubrovsky, 54, was taken into custody in Pennsylvania while attending a conference.
FBI Arrests Cybersecurity Executive in Extortion Case Tied to ShinyHunters Breach
A Canadian cybersecurity executive, Edward Dubrovsky, has been arrested in Pennsylvania on charges of conspiring to extort money through threats, linked to the ShinyHunters breach. The charges against him include violating federal computer fraud law and committing Hobbs Act extortion.
Chinese Hacker Exploits AI Tools in South Korean Bank Cyberattacks
A Chinese hacker recently unleashed a targeted cyberattack on South Korea's financial sector, leveraging a cutting-edge AI-powered penetration testing suite called ARTEX alongside clever Claude agents to breach defenses. The sophisticated attack used multiple AI tools, including DeepSeek and Grok, to outsmart security measures.
Autonomy Reshapes Modern Warfare with Multi-Domain ISR Capabilities
In today's high-stakes threat environment, where surveillance is constant and everything from ships to comms is vulnerable to attack, autonomy is revolutionizing modern warfare. With GPS and comms under siege, the future of combat relies on software and autonomy to stay one step ahead.
US Air Force to Arm B-52 with Stealthy LRASM Anti-Ship Missiles
The US Air Force is gearing up to supercharge its B-52 Stratofortress with the stealthy AGM-158C Long Range Anti-Ship Missile (LRASM), a move that will significantly boost the bomber's anti-ship capabilities. Lockheed Martin is set to be the sole partner in this high-stakes project, following a government notice signaling exclusive negotiations.
FBI Disrupts ShinyHunters Network with Third Arrest
The FBI has made a significant breakthrough in disrupting the notorious ShinyHunters group with the arrest of another suspected co-conspirator, bringing them one step closer to justice. This latest apprehension follows a series of efforts by the bureau to crack down on the group behind the recent FBIjobs.gov incident.
Germany Seizes Alleged Qilin Ransomware Leader After Japan Extradition
In a stunning display of international cooperation, Japanese authorities detained a Russian national who arrived in the country as a tourist and subsequently extradited them to Germany to face charges related to the notorious Qilin ransomware. This joint effort between Japan and Germany marks a significant breakthrough in the fight against cybercrime.
China's Type100 MTB Exposes Military Vulnerabilities
A recent PR video posted on china-defense.blogspot.com has inadvertently revealed some surprising military vulnerabilities, featuring China's Type100 MTB. The brief blog entry has sparked interest, despite its cryptic single-line credit and lack of commentary.
Australia's Afghan Legacy: Unresolved Debts and Unfinished Business
For over two decades, 39,000 Australian Defence Force members served bravely in Afghanistan, working alongside diplomats, police, aid workers, and civil officials to build a better future. Their remarkable journey began in 2001 with a special forces task group and ended with the closure of the Australian embassy in 2021.
Chinese Hackers Exploit AI-Powered Tool to Breach Korean Banks
Chinese hackers have breached South Korean financial institutions using an AI-powered tool, with CrowdStrike Intelligence uncovering evidence of exfiltrated data and a sophisticated campaign that went beyond mere reconnaissance. The alarming breach, active from late September to early October, highlights the growing threat of AI-fueled cyberattacks.
CISA Warns of Flax Typhoon Exploiting Five Vulnerabilities
Chinese government-affiliated hackers, known as Flax Typhoon, are exploiting five newly identified vulnerabilities to gain a foothold in critical infrastructure networks, including operational technology systems, with the potential to disrupt essential functions at a later time. This has prompted CISA to add these flaws to its Known Exploited Vulnerabilities catalog, triggering a federal remediation requirement.
Ransomware Attacks Soar to Record High in Q3 2026
Ransomware attacks have skyrocketed to a record high, with 2,627 claimed incidents in Q3 2026 - a 27% surge from the previous quarter and a 61% jump from the same period last year. This alarming trend signals a significant escalation of the threat landscape across all major sectors.
UK Warns of China's Integrity Tech Cyber Threat Tactics
China's Integrity Tech is raising red flags with its shady cyber activities, including building and selling malicious tools, hosting infrastructure, and compromising global networks. This tech group's ties to Beijing-backed cyber threats like Flax Typhoon have prompted a joint warning from the US, UK, and allied countries.
FBI Disrupts Flax Typhoon Tools Used in US Critical Infrastructure Intrusions
The FBI and Department of Justice have struck a major blow against a China-linked hacking group, seizing seven domains and blocking access to malicious tools used to infiltrate US and foreign critical infrastructure. This disruption targets Flax Typhoon, a notorious threat actor known for its widespread vulnerability scanning and intrusions.
OpenAI Disrupts Russian, Iranian AI Influence Ops Targeting Western Media
OpenAI just took down a massive AI influence operation that was spreading disinformation across Latin America, targeting Ukraine's reputation and fuelling heated debates in Argentina and Bolivia. The network, dubbed Dark Clark, was using a fake journalist persona and think tank to seed false narratives into mainstream reporting.
US Seizes Flax Typhoon Hacking Tools in Cyber Crackdown
In a major cyber crackdown, the US has seized hacking tools linked to the notorious Flax Typhoon group, dealing a significant blow to Chinese government-backed cyber threat actors. The seized tools, Microscan and FishHub, were used to steal sensitive data from organizations worldwide, including US critical infrastructure sectors.
US Exposed to Gaps in Cyberdefense Against China in Taiwan Scenario
The US is vulnerable to cyber defense gaps in the face of a potential Taiwan crisis with China, with a recent war game simulation revealing that federal agencies lack the budget and systematic process to effectively respond to such threats. This weakness could leave the country exposed to China's gray-zone strategy of cyberattacks and economic pressure.
Anthropic Launches Cybersecurity Program to Fortify Critical Infrastructure
Anthropic is stepping up to support defenders of critical infrastructure and open-source software, who are rich in experience but often low on resources, by launching a long-term cybersecurity program to identify and fix vulnerabilities. By combining its Claude models, engineering expertise, and threat research with partner cybersecurity firms, Anthropic aims to help safeguard critical infrastructure from exploitation.
Afghan Taliban Escalates Drone War Against Pakistan
Pakistan's air defenses went into overdrive on September 23, successfully taking down eight drones that had crossed into its airspace from Afghanistan. The incident sparked a fierce response from Islamabad, which launched strikes on 10 Taliban strongholds in Afghanistan.
FBI Disrupts Chinese Hacking Tools, Warns of PRC Spies Targeting Global Networks
The FBI has struck a blow against Chinese hackers, seizing seven web domains linked to a suite of hacking tools, including the notorious FishHub malware, which was used to target global networks, including roughly 20 Taiwanese universities. This malware was designed to facilitate phishing activity, allowing hackers to gain a foothold in vulnerable systems.
Ransomware Affiliate Betrayal Exposes Insider Threats
A shocking 94% of Internet of Medical Things devices are vulnerable to future "harvest-now, decrypt-later" attacks due to their inability to be upgraded to post-quantum cryptography, leaving sensitive health data at risk. This stark gap in security exposes a critical weakness in healthcare systems.