Tag: emerging threats
8214 articles
US Boosts Domestic Drone Production with $1 Billion Investments
The US government is taking a giant leap in drone technology, investing a whopping $1 billion to supercharge domestic drone production and ensure America's drone dominance. Top officials, including Under Secretary of Defense Emil Michael, gathered at the White House to rally industry leaders and discuss the nation's ambitious plans.
Army Expands Patriot Force Amid Golden Dome Integration Push
The US Army is ramping up its Patriot air-defense force to meet growing demands, all while integrating new technologies like the Golden Dome system. This strategic expansion aims to bolster the military's defenses now while preparing for future threats.
ASPI Celebrates 25 Years of Shaping National Security Debate
For 25 years, ASPI has been at the forefront of shaping Australia's national security debate, providing critical insights that challenge the status quo and inform government decision-making. From its roots in 2001, ASPI has remained committed to delivering contestable advice, fostering public discussion, and cultivating the next generation of security leaders.
NSA Deputy Warns of China's Pervasive Threat Across Domains
China's influence is a game-changer, touching every aspect of national security, and the competition is heating up, with artificial intelligence playing a major role. The NSA Deputy Director warns that Beijing is disrupting the status quo, acting as a spoiler from Greenland to the Korean Peninsula.
Mongolia Accelerates Defense Diversification with New Alliances
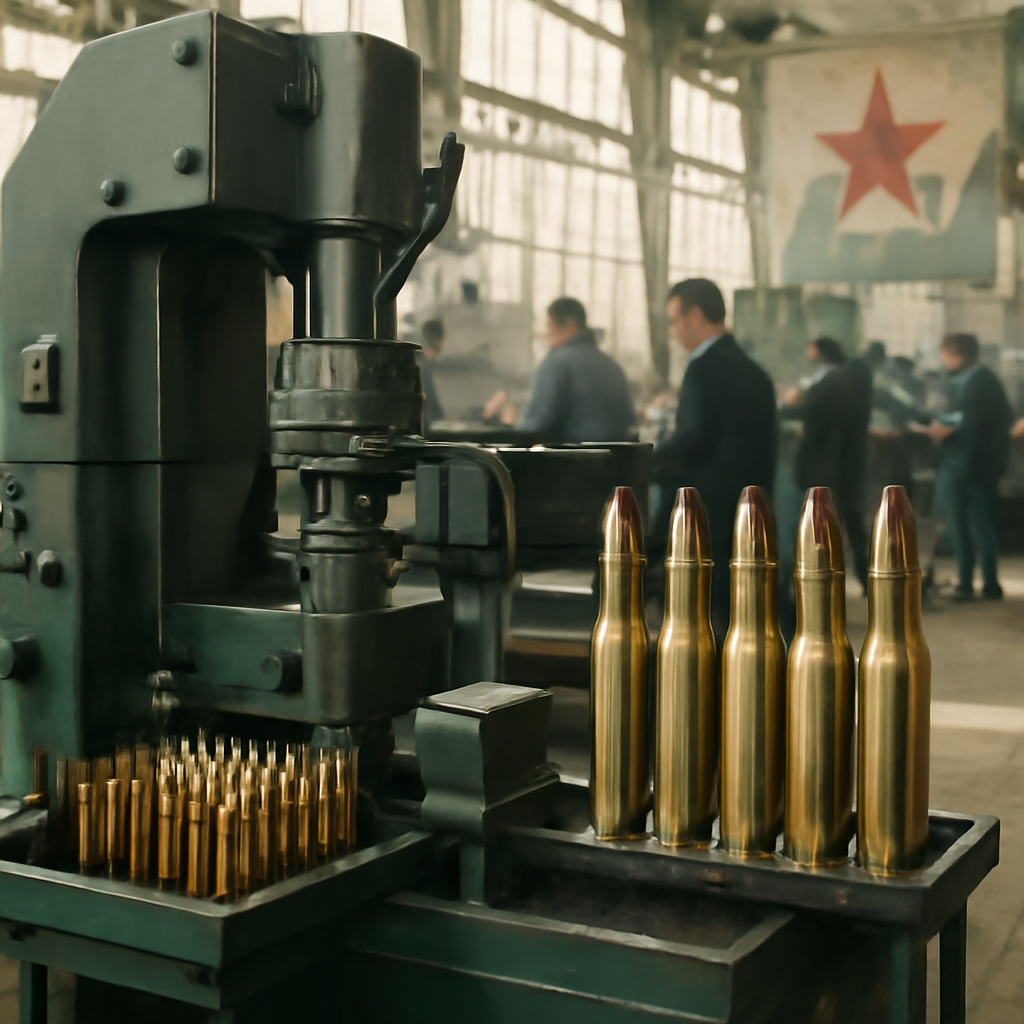
Mongolia is stepping up its defense game with a bold new approach to partnerships and industrial policy, marked by the recent launch of its first domestic ammunition production line in collaboration with Turkish defense company MKE. The milestone achievement signals a major shift in the country's strategy, with three types of ammunition now being produced locally.
Lawmakers Probe Federal Government's Hacking of Americans
Senators are demanding answers about the federal government's secretive hacking practices, and they're calling on the Government Accountability Office to shine a light on the scope, frequency, and safety measures behind these operations. They want to know how often and how extensively the government is using hacking and spyware to investigate Americans.
Pentagon Scrambles to Replenish Munitions Stockpiles Amid Iran War Surge
The Pentagon is racing to restock its munitions amid rising tensions with Iran, and defence giants are responding with game-changing innovations - including ultra-low-cost seekers and drone killers that could help ease the pressure on US stockpiles. Boeing, Northrop Grumman, and Lockheed Martin are leading the charge with affordable solutions.
Army Cyber Command Pursues Dedicated AI Funding for Enhanced Defenses
The Army Cyber Command is pushing for a dedicated AI funding line to supercharge its defensive cyber operations and stay ahead of emerging threats. This strategic move will likely become a top budget priority for the foreseeable future.
Malware Targets Automotive Head Units
Kaspersky uncovered a surprising new threat in June 2026: a piece of Android malware that targets the Android-based head units found in many cars, using a legitimate system app called TWCore as its unwitting accomplice. This sneaky malware piggybacks on TWCore's update process to spread its reach.
Malware Targets Android Car Systems Through Built-In Updaters
Malware is sneaking into Android car systems through built-in updaters, allowing hackers to wreak havoc on unsuspecting drivers. This sneaky attack was recently discovered by Kaspersky researchers, who linked it to a notorious ad-fraud operation called BADBOX.
Microsoft Defender Driver Exploited to Disable Security Software
Researchers at Check Point have uncovered a technique that exploits Microsoft Defender's own driver to disable security software, leaving Windows 7 to 11 users vulnerable to attack. This clever hack requires no external driver or software vulnerability, making it a worrying threat.
CISA Warns of Exploited Flaws in Russian Video Conferencing Platform TrueConf
The US Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning about two critical vulnerabilities in TrueConf, a Russian video conferencing platform, that have already been exploited in real-world attacks. Federal agencies have just until September 10 to patch these flaws and protect themselves.
Exposed AWS Keys Grant Attackers Full Corporate Account Control
Thousands of exposed AWS keys are still active, putting entire corporate accounts at risk of being hijacked by attackers - and a staggering 88% of re-verified keys were found to still grant access as recently as August 2026. This alarming vulnerability highlights the urgent need for tighter security measures to protect sensitive cloud data.
Rust Crates Targeted in Supply Chain Attack to Steal Developer Credentials
For a brief but alarming period, a widely-used Rust package was compromised, funneling malicious code into developer machines and putting sensitive credentials at risk. The attack was launched through a cleverly hidden payload in the build script of a popular crate called proc-macro1.
Microsoft Points to RGB Devices as Likely Cause of Windows Gaming Issues
If you're experiencing frustrating gaming issues on Windows, such as crashes, freezes, or failure to launch, after installing the August 11, 2026 update (KB5121003) or later, Microsoft may have identified the culprit: RGB devices.
Digital Identities Emerge as Key to Online Privacy Protection
Your online privacy is disappearing, piece by piece, as the internet quietly rebuilt itself around a business model that thrives on collecting and selling your personal data. Every click, every download, and every form you fill out is fueling a multibillion-dollar industry that tracks, profiles, and monetizes your online life.
North Korean Hackers Target Rust Supply Chain
North Korean hackers have been caught targeting the Rust supply chain, compromising a trusted open-source maintainer's account to sneak a backdoor into three popular Rust crates. The attackers cleverly modified package manifests to download and execute an unauthorized payload during automated builds.
CISA Mandates Patching of Exploited TrueConf Server Flaws
Don't wait until it's too late: CISA has issued a two-week deadline for U.S. federal agencies to patch two critical TrueConf Server vulnerabilities that hackers are actively exploiting to execute malicious scripts remotely. With a September 3 remediation deadline looming, prioritize patching now to safeguard your systems.
Agent Tesla Malware Evolves with Advanced Evasion Tactics
Researchers have uncovered a sneaky new tactic used by Agent Tesla Malware, where attackers use emoji obfuscation and spoofed emails to infect finance departments with a simple, yet cleverly designed, malicious attachment. This devious approach tricks victims into launching the infection chain with just a single reply.
Hackers Exploit FTP Server Banners to Deliver Windows Malware
Hackers have been cleverly using FTP server banners to spread Windows malware since July 2026, embedding commands in the greeting text that triggers an infection chain. This sneaky tactic, known as a dead-drop resolver, allows attackers to deliver malware via PowerShell scripts and other files.
Microsoft patches exploited Entra ID flaw amid rising attacks
Microsoft has patched a critical vulnerability in its Entra ID platform, known as CVE-2026-69836, which allowed attackers to execute code remotely with ease, and has already been exploited in recent attacks. This flaw enabled unauthorized threat actors to gain control and wreak havoc, making swift action crucial to prevent further damage.
SickKids Breach Exposes Employee and Applicant Data
A recent cybersecurity incident at Toronto's Hospital for Sick Children (SickKids) may have exposed sensitive personal data of current and former employees, job applicants, and staff from affiliated organizations. The breach, linked to a flaw in third-party software, is under investigation with the help of external cybersecurity experts.
AI Skills Become Mandatory in Over Half of Cybersecurity Job Ads
The demand for AI skills in cybersecurity is skyrocketing, with over half of job postings now requiring AI expertise - a number that's doubled in just one year, from 14.2% to 28.5%. This seismic shift signals a fundamental change in the way cybersecurity teams operate, combining human oversight with machine automation.
GitLab Flaw Exploited in Wild Days After Disclosure
In a chilling demonstration of the new reality in vulnerability exploitation, attackers began exploiting a newly disclosed GitLab flaw within minutes of its public disclosure, leaving little time for patching. This rapid reproduction and exploitation is a stark reminder that waiting for the next patch cycle may no longer be a viable defense strategy.