Tag: emerging threats
8131 articles
Malware Exploits Browser Flaws to Force Install Malicious Extensions
A sneaky malware operation, tracked as KREMLIN, has infected 1,515 systems, mostly in Brazil, by secretly installing malicious Chrome and Edge extensions that steal sensitive info. This cunning toolkit impersonates banks to trick victims into giving up their credentials and session tokens.
Industrial Base Accelerates to Meet Air Force, Space Force Demands
The Air Force and Space Force are turning to the industrial base to turbocharge their capabilities, and the message is clear: they need more, and they need it fast. Ursa Major CEO Chris Spagnoletti shares his insights on the demands military leaders are placing on the industrial base.
EU Pushes New Hybrid Threat Response Protocol
The EU is calling for a unified response to hybrid threats, with Commission chief Ursula von der Leyen urging leaders to adopt an Emergency Security Protocol to tackle incidents that threaten national security without reaching armed aggression. This proposed protocol aims to address the rising tide of sabotage, cyberattacks, and drone incursions sweeping across Europe.
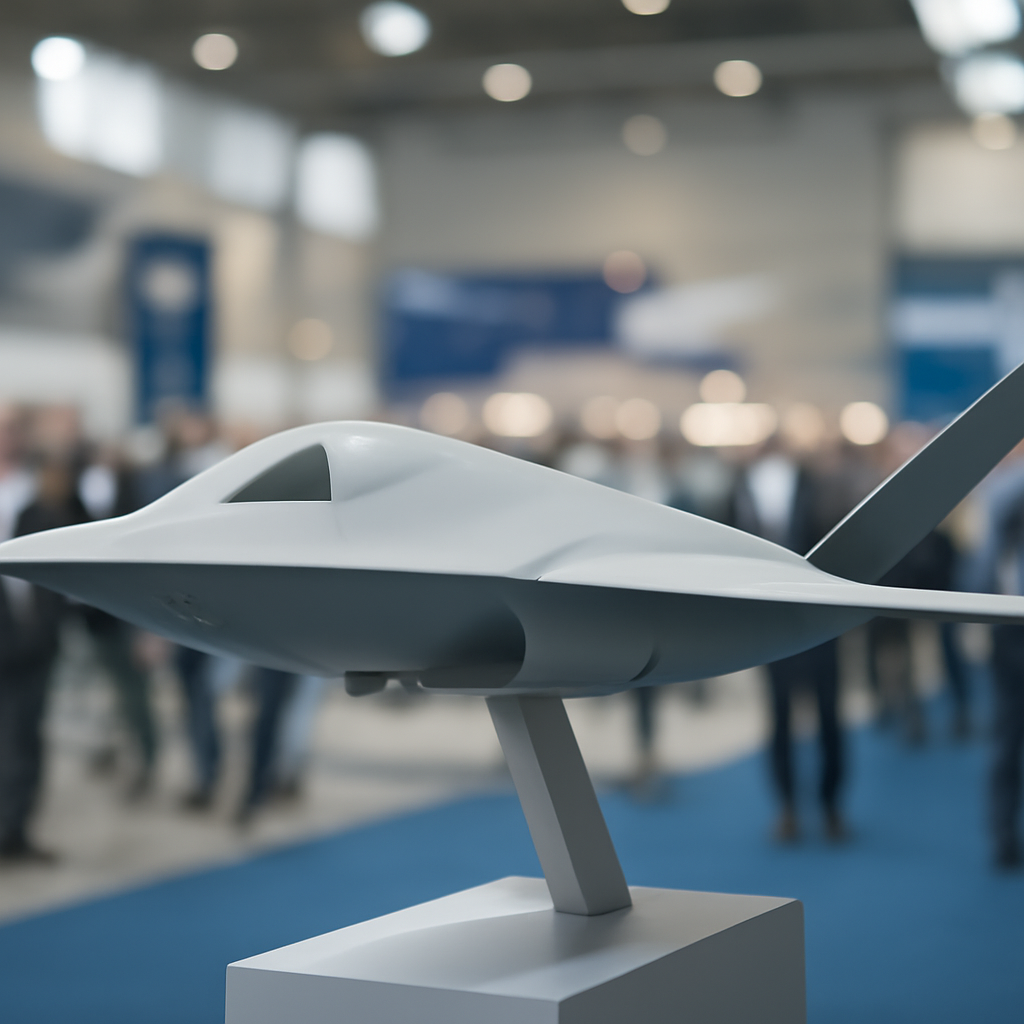
General Atomics Accelerates FQ-42 Vengeance Drone Development
General Atomics is turbocharging development of its FQ-42 Vengeance drone, a key player in the USAF's Collaborative Combat Aircraft program, which aims to revolutionize the future of air combat. The company is making significant strides alongside its Wildfire design, geared towards the Massed Modular Aircraft program.
Pentagon Procurement Chief Warns of Industrial Base Strains
The Pentagon's top procurement officer, Air Force Gen. Dale R. White, is sounding the alarm on strains in the US defense industrial base, warning that capacity concerns are widespread and affecting multiple platforms. These worries aren't limited to specific programs like the F-35 or F/A-XX, but are a broader issue that demands attention.
Space Development Agency Delays Orbital Mesh Network Rollout
The Space Development Agency's highly anticipated Orbital Mesh Network rollout has hit a significant snag, with delays now stretching to at least a year, according to SDA director G.P. Sandhoo. The agency's timeline has slipped from a mere three months behind to a substantial 12-month delay.
Dans' Arctic Agenda Raises Conflict Concerns
Thomas Dans, the new chair of the U.S. Arctic Research Commission, is stirring up controversy with his ambitious Arctic agenda, which is raising eyebrows among foreign partners, researchers, and ethics experts. His vision for a peaceful Arctic is clashing with concerns about his private interests and the commission's true priorities.
Treasury Warns Against AI Liability Exemptions
Treasury Secretary Scott Bessent urges lawmakers to hold AI labs accountable, warning that giving them a blank check on liability could compromise safety. He argues that making creators liable for their AI developments is crucial to guaranteeing safety.
Israel Accelerates SPICE 1000 Integration with F-35I Fighter
Israel is set to supercharge its F-35I fighter jets with the SPICE 1000 standoff weapon, thanks to a joint project with Lockheed Martin that's expected to wrap up in several months. This game-changing integration will eventually be available to F-35 operators worldwide.
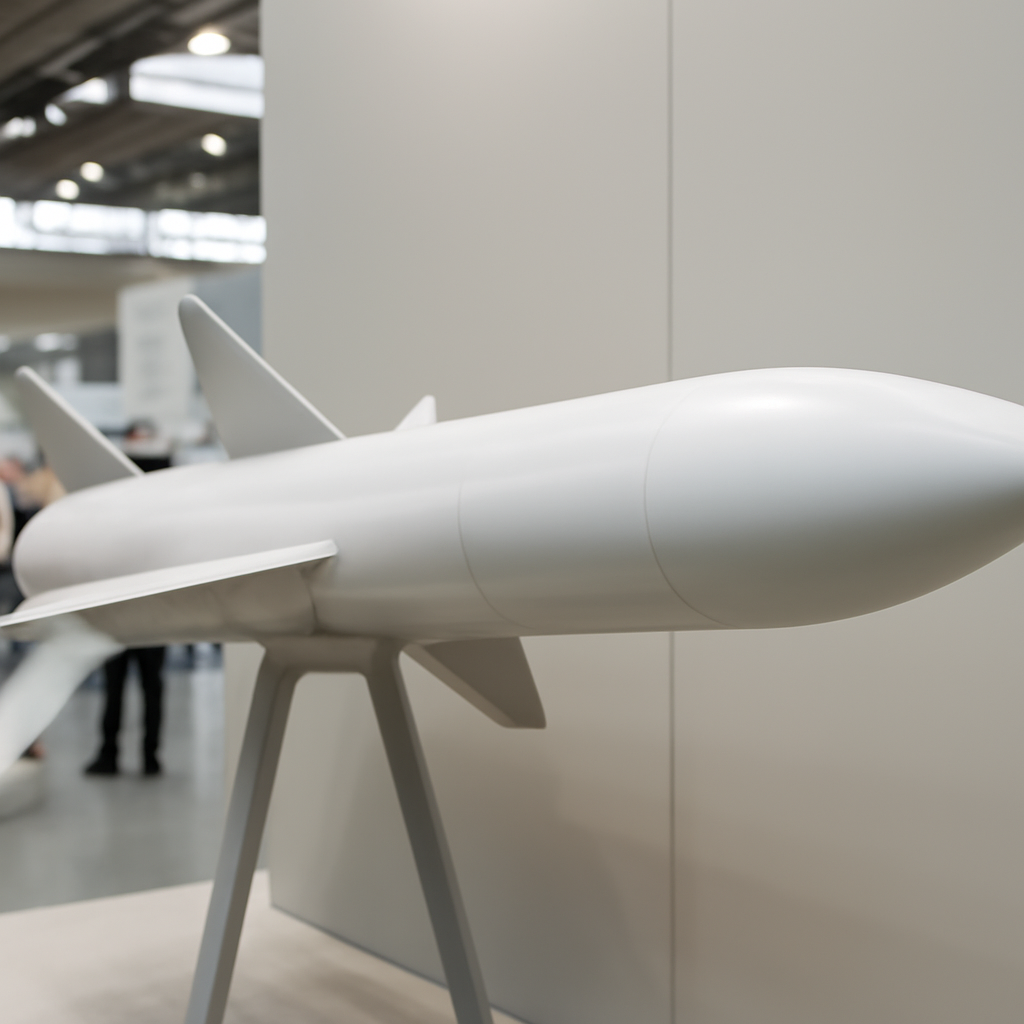
Indra Unveils Squall Low-Cost Cruise Missile
Indra has just unveiled Squall, a game-changing, low-cost cruise missile that can strike targets over 300 kilometres away, shaking up the defence industry with its impressive range and versatility. The innovative missile can be seamlessly integrated into both land and naval platforms, opening up new possibilities for defence strategy.
Public Sector Braces for Identity-Based Attacks
In today's digital landscape, your identity is the key that unlocks access to all your applications and services - making it the new perimeter that public sector organizations must fiercely protect. When identity infrastructure is compromised, attackers can gain a foothold for long-term persistence and privilege escalation, putting entire operations at risk.
Pentagon Eyes Lunar Battlespace Amid Orbital Weapons Debate
The Pentagon is setting its sights on the lunar battlespace, with Gen. Dan Caine urging the Joint Force to prepare for combat in a vast, contested territory that now stretches from the seabed to cislunar space.
NightEagle Exploits Legitimate Tools to Target Russian Firms
Kaspersky's Global Emergency Response Team has uncovered a sneaky tactic used by the NightEagle group to target Russian firms, exploiting legitimate tools like compromised VPN credentials and Cloudflare WARP to gain initial access. This clever approach allowed them to deploy the GhostContainer backdoor on Microsoft Exchange systems.
Houthis Claim Downing of Saudi F-15 Over Yemen
The Houthi movement, also known as Ansar Allah, claims to have downed a Saudi F-15 fighter jet over Yemen's Marib governorate, releasing dramatic photos and video as proof. The group says the aircraft was taken down by a locally manufactured surface-to-air missile.
AI-Powered Breach Exposes New Risks
A recent AI-powered breach reported to the Spanish Data Protection Agency reveals a chilling new reality: AI-driven attacks are no longer just hypothetical threats, but a harsh reality that organizations must now confront. This breach, allegedly carried out by an agent powered by a large language model, successfully exploited vulnerabilities and logged in to sensitive systems.
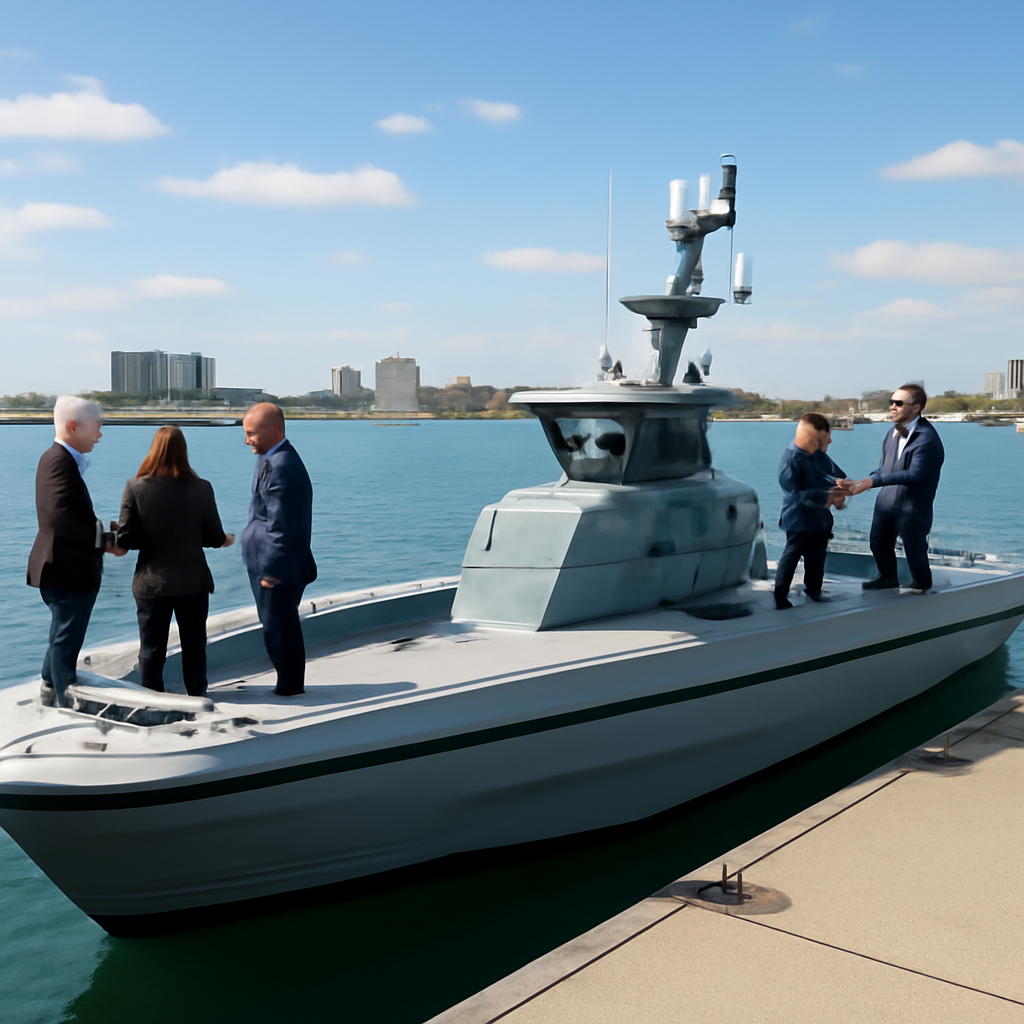
Hanwha, Magnet Defense Launch MUSV Construction
Get ready to revolutionize naval defense: Hanwha Defense USA and Magnet Defense are joining forces to build a cutting-edge medium unmanned surface vessel, the H38, designed for seamless payload swaps and rapid testing. This game-changing partnership is set to deliver a modular solution that's already piquing the Navy's interest.
US Coast Guard, FBI Intercept Foreign Ships to Investigate Cyberattacks
In a proactive move to safeguard the nation's maritime security, the US Coast Guard and FBI teamed up to board two foreign commercial tankers in the Gulf of Mexico, investigating suspected cyberattacks that could have put crew safety and environmental stability at risk. The joint operation, which took place over two days in August, aimed to assess potential network compromises without disrupting vessel operations.
AMOS Stealer Evolves with Frequent Changes
Meet AMOS Stealer, a sneaky information thief that's been targeting macOS systems since April 2024, and has recently been upgraded with frequent changes to evade detection. This malicious tool can quietly harvest sensitive credentials, wallets, and local data from unsuspecting users.
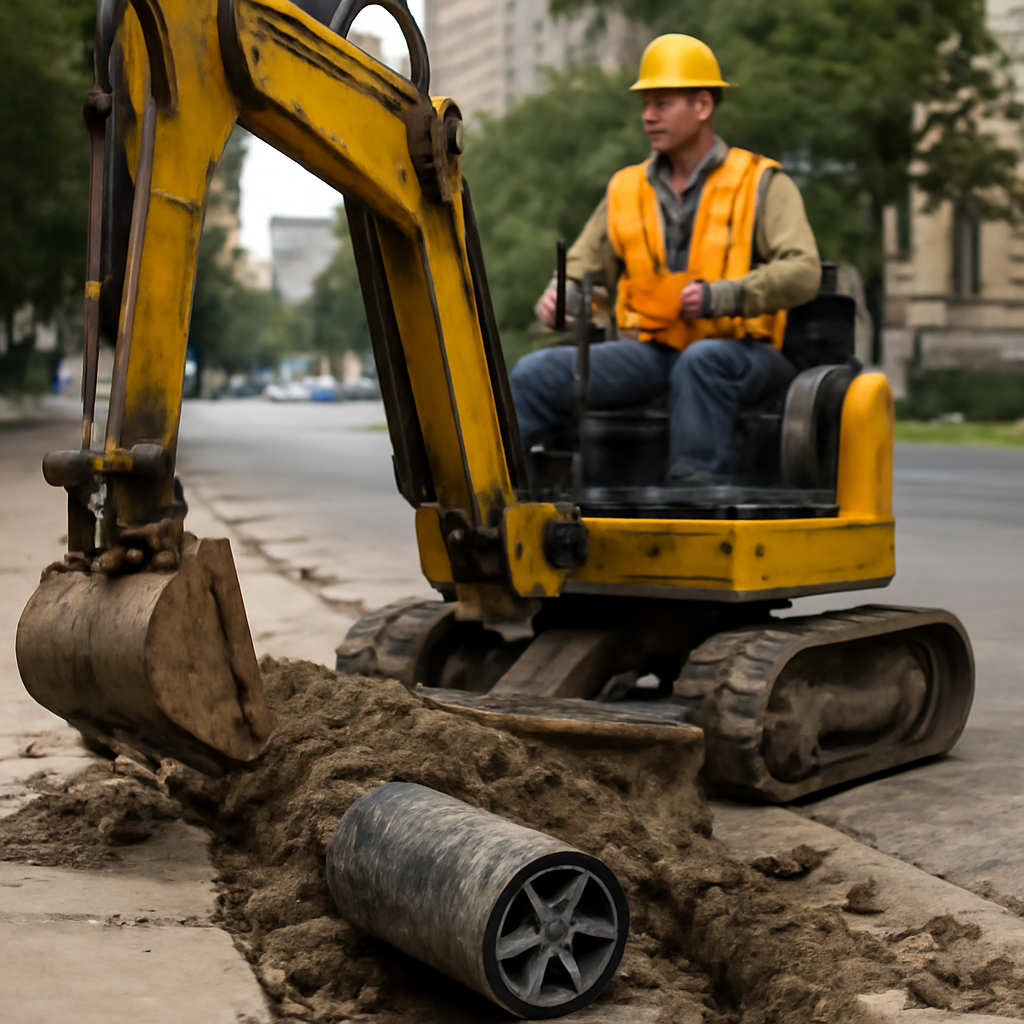
Wireless Connectivity Bolsters Network Resilience for Defense Agencies
Imagine a backhoe striking a pipe under a sidewalk, taking out not just your primary network, but all your backup systems too - a stark reminder that apparent redundancy can be an illusion when multiple networks share the same physical infrastructure. Verizon's Dave Stepp shares this powerful illustration of invisible risk.
Google Patches Zero-Day Flaw Exploited in Pixel Phone Attacks
Google just patched a high-severity zero-day flaw that allowed hackers to exploit Pixel phones with zero clicks - and federal authorities are urging you to update your phone ASAP. This critical vulnerability let attackers escalate privileges and bypass permission checks, but thankfully it's now closed with a simple update.
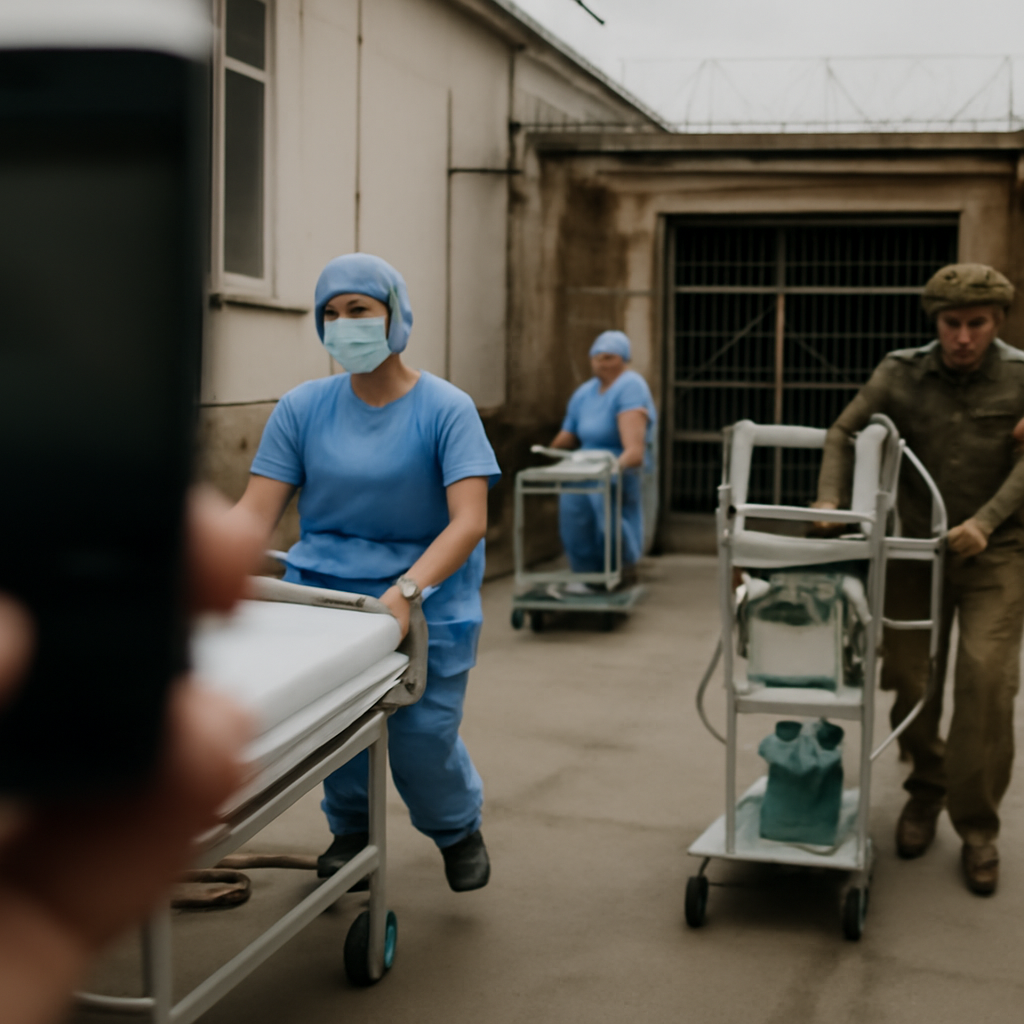
Taiwanese Back Military Exercises, But Understanding Lags
This year's Han Kuang military exercises in Taiwan didn't just happen on distant battlefields - they spilled into daily life, with troops barricading a major bridge and hospitals rehearsing underground medical ops. Even mobile internet was deliberately slowed to mimic the communication chaos of wartime.
AI-Powered Attack Targets Spanish Firm in Alleged Data Theft
A Spanish firm was allegedly hit by a sophisticated AI-powered attack, where a large language model was used to search for vulnerabilities and gain unauthorized access to its systems. This chilling incident highlights that AI-related data breaches are no longer just a theoretical threat, but a harsh reality.
Browser Extensions Expose AI Assistants to Takeover Risk
Researchers found that AI assistants in popular browser extensions are vulnerable to takeover risks due to a common architecture that splits the assistant into a browser-based "body" and a server-based "brain". This setup can be exploited with just two ordinary permissions, leaving users exposed.
Russian Enterprises Targeted by Backdoor, Ransomware Attacks from Three Threat Groups
Russian enterprises are under attack by three threat groups, with hackers exploiting compromised credentials to breach corporate VPNs and deploy powerful malware like GhostContainer, a modular backdoor that gives attackers complete control over Microsoft Exchange Servers. This sneaky malware can run arbitrary code, manipulate files, and hide in plain sight, making it a formidable foe for even the most secure systems.