Tag: emerging threats
8132 articles
Russian Enterprises Targeted by Backdoor, Ransomware Attacks from Three Threat Groups
Russian enterprises are under attack by three threat groups, with hackers exploiting compromised credentials to breach corporate VPNs and deploy powerful malware like GhostContainer, a modular backdoor that gives attackers complete control over Microsoft Exchange Servers. This sneaky malware can run arbitrary code, manipulate files, and hide in plain sight, making it a formidable foe for even the most secure systems.
Exploits Target Issabel Framework Flaw for Unauthenticated OS Command Execution
A critical flaw in the Issabel Framework, rated 9.8 out of 10 for severity, allows hackers to execute malicious commands on vulnerable systems without needing login credentials. This vulnerability can be exploited using a hard-coded security key, enabling attackers to forge tokens and gain control.
Parallels Desktop Flaw Exposes Macs to Root Access
A newly discovered flaw in Parallels Desktop, tracked as CVE-2026-90894, leaves Macs vulnerable to root access, allowing ordinary local accounts to run code as root. This security gap, dubbed ParaShells, was uncovered by JFrog's vulnerability team and rated 7.8 out of 10 in severity.
Mandiant Exposes AI Coding Assistant Vulnerability to Shai-Hulud Worm
A hacker hijacked an AI coding assistant session, using it as a launchpad to deploy the Shai-Hulud worm across nearly 100 internal code repositories. This alarming incident highlights the vulnerability of AI-powered coding tools to exploitation.
WooCommerce Plugin Flaw Exploited to Upload PHP Webshells on WordPress Sites
Hackers have been actively exploiting a critical flaw in the WooCommerce Wholesale Lead Capture plugin to upload malicious PHP webshells to WordPress sites, despite a patch being available since February. Over 100,000 exploitation attempts were blocked by Wordfence's firewall, with multiple waves of attacks occurring over several months.
Ransomware Costs Exceed Ransom Payments
The real cost of ransomware goes far beyond the initial payment, with average incidents costing a whopping $5.08 million - a number that dwarfs the median ransom payment of $139,875. Downtime is a major culprit, with organizations often underestimating the hours and days of lost productivity that add up to a hefty bill.
CISA and NIST Issue Guidance to Safeguard Cloud Identity Tokens
As cyber threats escalate, protecting cloud identity tokens has become crucial - and CISA and NIST have just released guidance to help safeguard these vulnerable targets. The new interagency report provides critical advice for federal agencies, cloud service providers, and organizations that rely on them to stay secure.
N0va Phishkit Targets Businesses with Legitimate Authentication Flows
Meet N0va, a sneaky phishkit that's duping businesses across North America and Europe by masquerading as trusted services and exploiting genuine authentication flows. Its clever attack chain can swiftly turn a single phishing click into persistent access to corporate resources.
Microsoft Probes Outlook Copilot Button Glitch
Microsoft has identified the culprit behind the missing Copilot button in Outlook: a pesky MAPI property that goes MIA after a recent software build, leaving users without access to this handy feature. The good news? The Outlook team is on the case, actively investigating and working to resolve the issue.
Acronis Plugin Vulnerability Exploited in Targeted Attacks
A high-severity vulnerability in Acronis' Backup plugin has been exploited in targeted attacks, allowing attackers to escalate privileges on Linux deployments - and a patch is available in update 1.9.3 HF3. Users are urged to install it immediately to avoid potential security breaches.
Threat Intel Struggles to Close Exploitation Gap
In today's AI-driven landscape, merely knowing about potential threats isn't enough - the real challenge lies in rapidly testing and validating defenses against them. By harnessing AI-assisted exploitation, adversaries are swiftly turning exposure into breaches, leaving security teams scrambling to keep pace.
Spain Confronts AI-Driven Data Breach in First Recorded Attack
Spain's data protection authority confirms the country's first personal data breach caused by an autonomous AI agent, highlighting the need for swift detection and response mechanisms to mitigate such threats. The breach was carried out by an individual using a large language model to attack an organization.
Google Discloses Pixel Modem Flaw Under Limited Targeted Exploitation
Google just sounded the alarm on a high-severity bug in Pixel devices that's being exploited in targeted attacks, and they're urging users to take action. The vulnerability, tracked as CVE-2026-58704, affects the Pixel Cellular Modem and could allow attackers to escalate privileges.
CISA Warns of Active ScreenConnect Exploit in Ongoing Attacks
Beware: hackers are actively exploiting a critical flaw in ConnectWise ScreenConnect, allowing them to transfer files and execute code on vulnerable systems without permission. The US Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent warning, ordering federal agencies to secure affected systems within three days.
Ministry of Justice Breach Exposes Southport Victims' Files
The Ministry of Justice has apologized for a shocking breach that exposed sensitive files of Southport murder victims and their families, describing the incident as completely unacceptable. The Prime Minister has stepped in, ordering an urgent investigation overseen by the Lord Chancellor, with promises of swift and firm action against any wrongdoing.
Cyber-Attacks Inflict $52,000 Average Cost on Organizations
Cyber attacks aren't just a minor setback - they can cost organizations around $52,000 on average, causing widespread disruption to services, employees, and customers. A recent report found that nearly a third of organizations globally fell victim to at least one successful cyber attack in the past year alone.
TP-Link Cameras Expose Users to Eavesdropping Risk via Zero-Day Flaw
Millions of TP-Link camera users may be vulnerable to eavesdropping due to a zero-day flaw that lets hackers gain admin access without a password. This critical vulnerability affects popular models like the TP-Link Tapo C200, commonly used for baby and pet monitoring, home security, and small business protection.
UK Warns of Iranian Spyware Campaign Targeting Dissidents
The UK's National Cyber Security Centre has warned that dissidents, activists, and journalists critical of the Iranian regime are being ruthlessly targeted by a Tehran-backed spyware campaign, which steals emails, messages, and device data to silence critics. This sinister campaign has even led to stolen info being leaked on pro-Iranian sites, putting lives at risk.
Cybersecurity Vendors Flock to UK's SE Labs Testing Program as MITRE ATT&CK Loses Momentum
As cybersecurity threats evolve at breakneck speed, SE Labs' innovative PIVOT testing program is drawing vendors in with its rigorous, adversary-driven approach to defense testing. By simulating real-world attacks, PIVOT helps vendors strengthen their defenses against the most devastating threats.
WSO2 API Manager Flaw Sees Active Exploitation Attempts
A critical flaw in WSO2 API Manager, tracked as CVE-2026-5430, is under active exploitation, allowing hackers to bypass JWT authentication and gain unauthorized access with a CVSS score of 9.8 out of 10.0, potentially leading to account takeover and compromise of administrative accounts.
WordPress Plugin Flaw Exploited to Plant PHP Web Shells
A critical flaw in the popular WooCommerce Wholesale Lead Capture plugin has left over 6,000 active installs vulnerable to attacks, with over 100,000 exploit attempts blocked since June 2026. This urgent security issue allows hackers to upload malicious files, putting websites at risk.
Google Fixes Exploited Android Zero-Day Flaw on Pixel Devices
Google just patched a high-severity zero-day flaw in its Pixel smartphones, warning that hackers may be using it to launch targeted attacks. The vulnerability, tracked as CVE-2026-58704, allows for a permission bypass in the device's modem, posing a significant risk to users.
US Military Exposes $38 Billion Tab for Iran Conflict
The US military's ongoing conflict with Iran has already racked up a staggering $38.1 billion price tag, with monthly costs expected to continue at a whopping $2-3 billion. Rebuilding depleted inventories of crucial interceptors could take a lengthy five years.
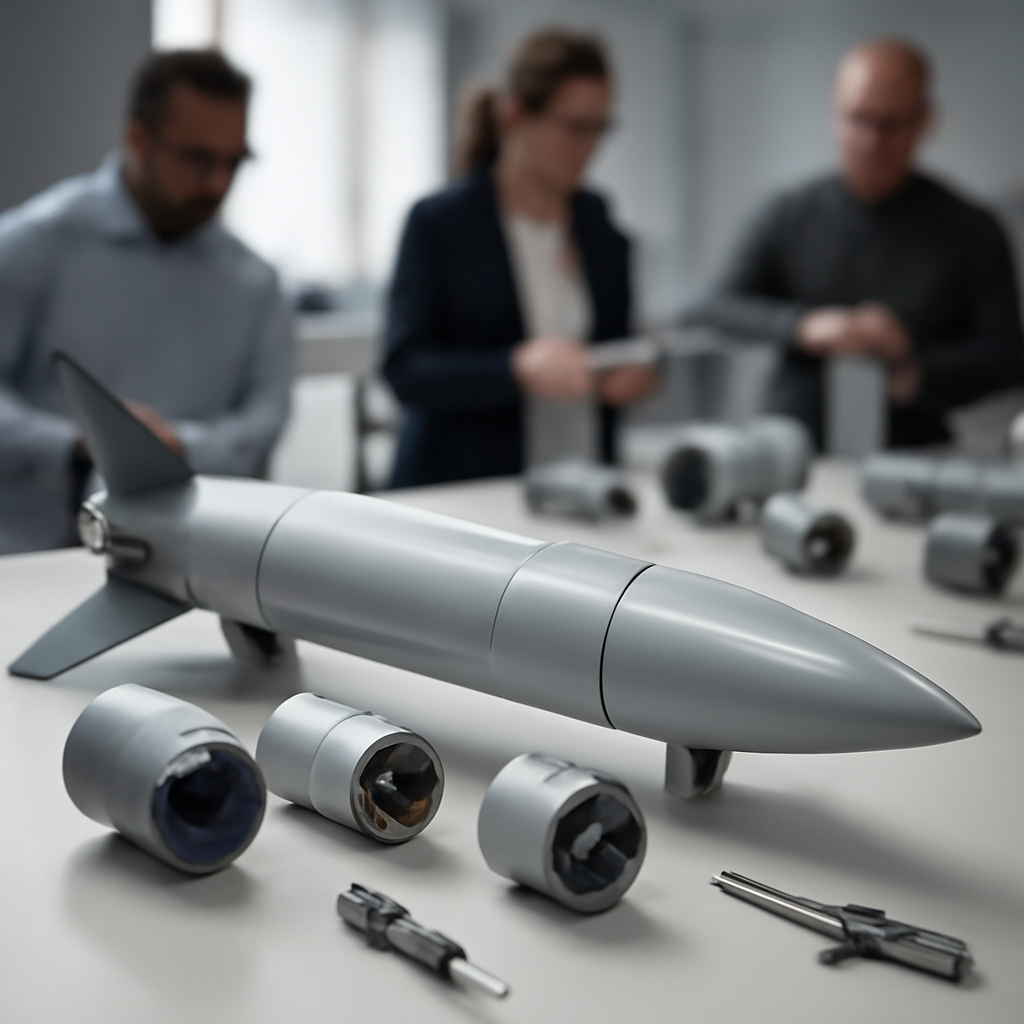
Lockheed Unveils Modular AGM-158 JASSM Missile Concept
Lockheed Martin is shaking things up with its AGM-158 FLEX concept, a game-changing modular airframe design that promises to unlock future cost savings and unleash a new era of versatility for the AGM-158 missile family. This innovative approach allows for interchangeable components and easy reconfiguration for different sensors, lengths, and launch methods.