Tag: emerging threats
8111 articles
PamStealer Malware Evolves with Live C2 Decryption and Enhanced Persistence
Meet the latest variant of PamStealer malware, which has evolved with a sneaky new trick: it can only be decrypted through a live command-and-control session, making it even harder to track and stop. This fresh threat uses a fake cryptocurrency wallet site, wavel.app, to lure victims into downloading a malicious disk image file.
GitHub Actions Resumes Executing Mini Shai-Hulud Malware After Re-Enablement
Malware linked to the Mini Shai-Hulud campaign suddenly roared back to life on September 16, 2026, when two compromised GitHub Actions repositories were mysteriously re-enabled. This alarming revival happened despite previous efforts to take the repositories offline following a security breach in May 2026.
Data Leaders Wrestle with File Governance Gaps
Join a private dinner discussion in New York on October 27th, where data leaders will gather to tackle the costly problem of file governance gaps - and share their own hard-won insights, off the record. This exclusive, peer-only conversation, led by Joe Fay, offers a unique chance to swap stories and solutions with fellow leaders.
Russian Infostealer Targets Ukraine via Lunex Malware Platform
Meet the Lunex Malware Platform, a tool used by a Russian-speaking threat actor to launch a financially motivated infostealer campaign targeting Ukraine, and get the inside scoop on its alleged origins and four-stage attack chain. This malware-as-a-service platform is sold to cybercriminal customers, posing a significant threat to cyber defence.
SOC 2 Faces AI Agent Test
As AI agents increasingly infiltrate enterprise systems, the authenticity of SOC 2 compliance comes under scrutiny - can a certificate that verifies controls at a single point in time truly guarantee security in a rapidly changing environment? Token Security argues that SOC 2 may be more about appearances than actual protection.
Salesforce Zero-Click Flaws Expose AI Agent Data Risk
Security researchers just uncovered a set of zero-click flaws in Salesforce Agentforce that let attackers silently siphon off sensitive CRM data without even needing to log in. This clever exploit, dubbed "SalesBleed," could put AI agent data at risk - and it's a wake-up call for companies to take action.
AI Compresses Cyberattack Loops, Pressures SOC Response Times
Cybercriminals are now leveraging AI to supercharge their attacks, using it to discover vulnerabilities, develop exploits, and automate tasks - putting pressure on security teams to respond faster than ever. In fact, by late 2025, AI-powered malware and illicit AI tools were already emerging on the dark web, changing the game for threat actors.
Democracies Urged to Form Global Alliance to Deter China
With democracy on the back foot for two decades, the world is bracing for a potentially catastrophic war - and experts warn that a Chinese move on Taiwan could be the spark that sets it off. The clock is ticking: can democracies unite to form a global alliance and deter China before it's too late?
CISA Unveils Comprehensive Election Security Plan to Counter Evolving Threats
The CISA Election Infrastructure Security Plan is a powerful shield against evolving threats, leveraging partnerships, cyber defenses, and threat intelligence to safeguard the integrity of US elections. By working together, stakeholders can ensure the security and public trust that's fundamental to a healthy democracy.
Rydox Admin Pleads Guilty in Major Cybercrime Crackdown
In a major cybercrime crackdown, Ardit Kutleshi, a 28-year-old Kosovar national, has pleaded guilty to running Rydox, an illicit online marketplace that sold stolen personal info, including Social Security numbers, credit card details, and login credentials, of thousands of US citizens. The guilty plea comes after a massive investigation into over 7,600 sales of sensitive data on the platform.
North Korean Hackers Steal $351.6M from Bitget in Backend Compromise
In a shocking security breach, North Korean hackers made off with a whopping $351.6 million from cryptocurrency exchange Bitget, compromising a limited number of hot wallets. Fortunately, customer account balances remain intact and trading operations are still running smoothly, with withdrawals temporarily paused while the company conducts a thorough security review.
Roundcube Flaw Exploited in Wild, Warns Canadian Cyber Centre
A critical Roundcube Webmail vulnerability, CVE-2026-48842, is under active exploitation, allowing unauthenticated attackers to inject malicious SQL code and potentially expose sensitive mail account credentials and messages. This flaw affects versions 1.6.x and 1.7.x of Roundcube Webmail, and has been patched in versions 1.6.16 and 1.7.1.
RemControl Trojan Targets Android Users with Accessibility Exploit
Beware: the RemControl Trojan is targeting Android users with a sneaky accessibility exploit, putting over 30 major banks and their customers at risk across six countries. It starts with a clever fake Google Play Store page trick, disguising itself as a harmless app update.
Researchers Intercept AliExpress Phishing Domains Before Activation
EfficientIP Research Labs swooped in to stop a phishing scam, intercepting 10 AliExpress domains before they could be used to trick unsuspecting victims. The domains, tracked from June 9 to July 2, were part of a sophisticated phishing operation that was thankfully shut down before activation.
North Korean Hackers Steal $351.6 Million in Bitget Crypto Exchange Breach
In a shocking breach, North Korean hackers made off with a staggering $351.6 million from the Bitget crypto exchange, prompting the company to temporarily suspend withdrawals while it investigates and beefs up security. Fortunately, customer accounts remain unaffected, with deposits and trading continuing as usual.
CISA Flags WSO2, Adobe Commerce Flaws as Actively Exploited
Stay ahead of cyber threats: Federal agencies must patch WSO2 and Adobe Commerce flaws by September 27, 2026, to avoid exploitation, as CISA flags these vulnerabilities as actively exploited. The high-severity bugs, including a path traversal flaw and an authorization issue, can lead to remote code execution and unrestricted file uploads.
Cloudflare Fixes Flaw Exposing Leftover Disk Data Between Containers
A startling security flaw was discovered in Cloudflare's container storage system, allowing leftover disk data to be exposed between containers, with researchers finding remnants on 18 of 24 production tests and 20 of 22 underlying machines worldwide. This vulnerability was caused by a misconfigured setting that reused disk blocks without properly wiping them clean.
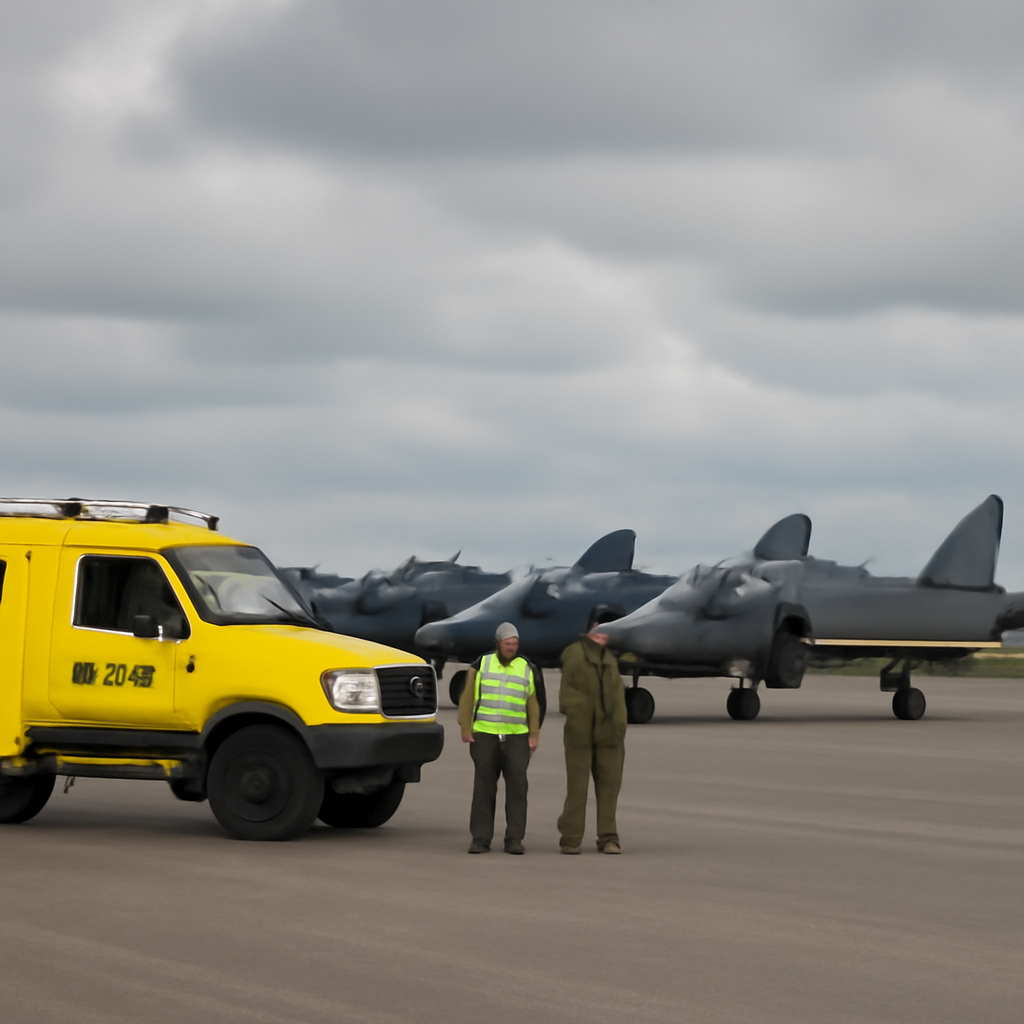
UK Grounds Hawk Trainer Jets After Crash Prompts Safety Probe
The Royal Air Force has grounded its Hawk T1 and T2 training jets after a dramatic crash near homes at RAF Valley on Anglesey, and launched a formal investigation into the incident. Both pilots ejected to safety and are expected to make a full recovery.
Senate Leaders Unveil Bill to Bolster Telecom Cybersecurity
Senate leaders Mark Warner and Ted Cruz have introduced the Telecommunications Cybersecurity and Resilience Act, a bipartisan bill aimed at fortifying the nation's telecom infrastructure against devastating cyberattacks like the historic Salt Typhoon hack. The legislation seeks to boost cybersecurity standards and bring government and industry together to protect critical infrastructure.
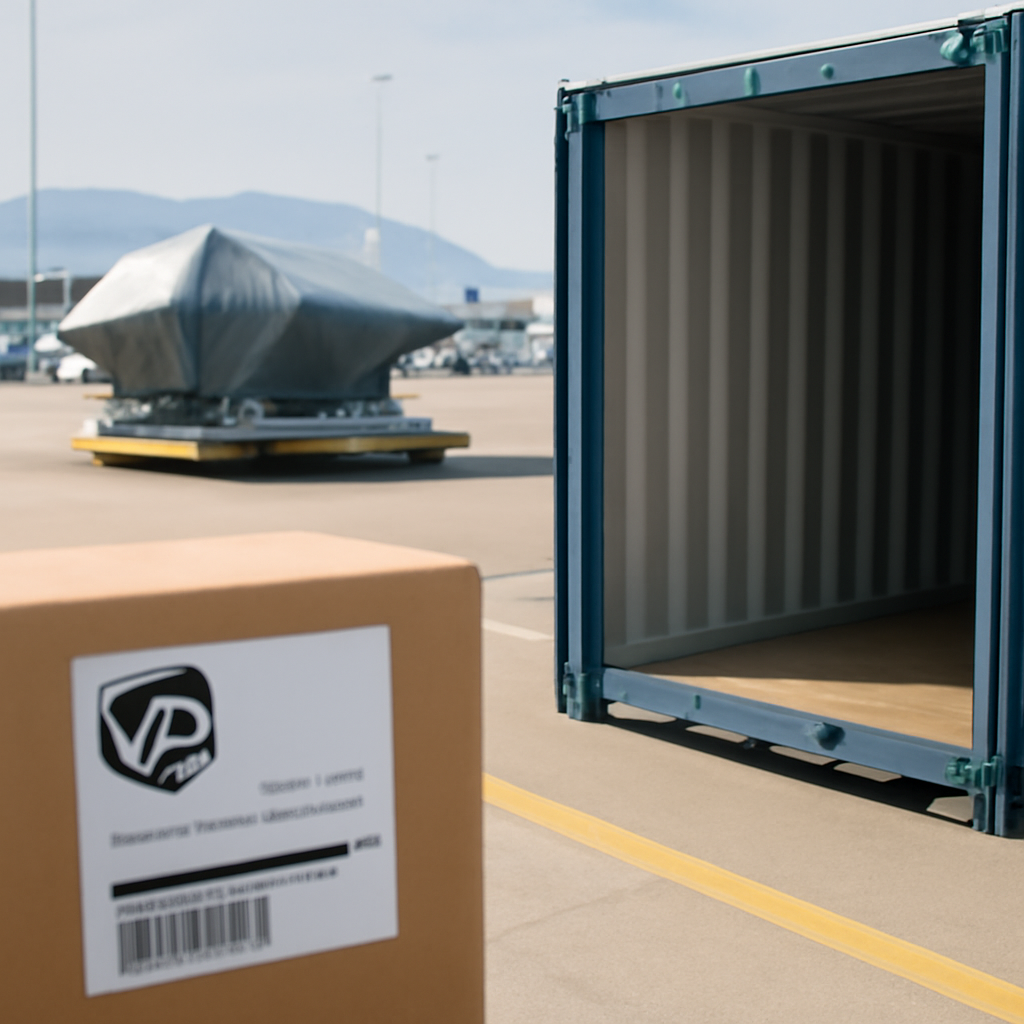
China Obtains F-35 Parts in Hong Kong Shipment Breach
A shipment of F-35 parts bound for the US took a mysterious detour from Australia to South Korea to Hong Kong, where Chinese authorities seized the components, including a cockpit canopy and a weapons-bay door, and have yet to return them. The incident has raised serious questions about security breaches in the international logistics system.
Air Force Scales Back China Think Tank Amid Budget Cuts
The Air Force's China Aerospace Studies Institute is facing a significant blow to its research capabilities due to budget cuts, with the loss of its 10-member civilian staff that handled critical analysis and translation work. Without these experts, the institute's ability to provide valuable insights on China is severely compromised.
US Probes Russian Ownership of Phone-Hacking Firm with Security Agency Contracts
The US government has launched an investigation into the Russian ownership of Oxygen Forensics, a phone-hacking firm that has sold its software to top US security agencies, including the Secret Service and Homeland Security. The probe led to the arrest of the company's US CEO and a Russian national allegedly controlling the firm.
France Bolsters Saudi Arabia's Red Sea Oil Defenses
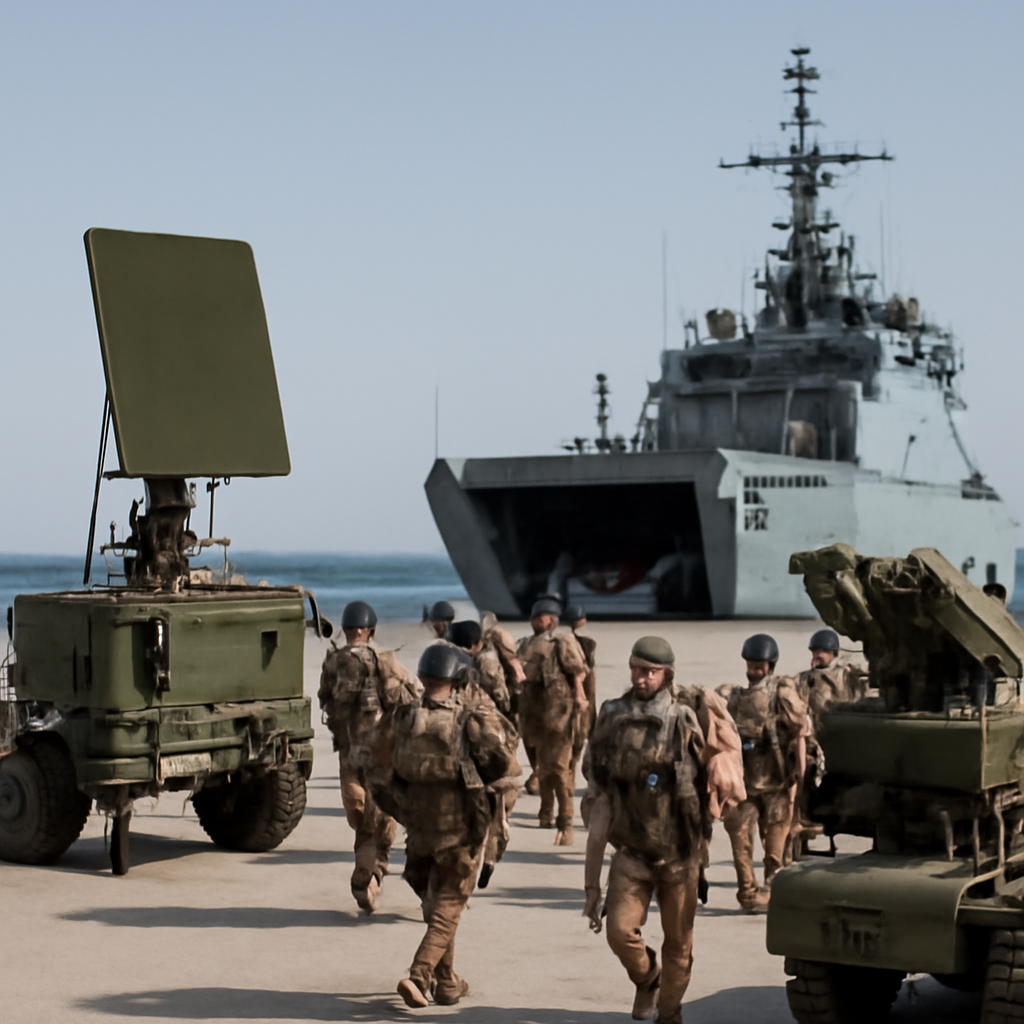
France is stepping up to protect a crucial oil hub in Saudi Arabia, deploying troops, radar systems, and defense equipment to the Yanbu energy facility on the Red Sea to safeguard the vital oil lifeline. The move, announced by President Emmanuel Macron, is strictly defensive, aimed at shielding the site from potential attacks that could disrupt global oil supplies.
Governments Adapt SATCOM Systems for Dynamic Space Environment
The Australian Department of Defence scrapped its plans for a single-orbit SATCOM system in 2024, recognising that a rapidly changing space landscape and emerging threats demanded a more adaptable approach. Instead, they're prioritising resilient, multi-orbit communications systems to keep missions connected in an increasingly dynamic environment.