Tag: emerging threats
8110 articles
OpenAI Halts Advanced Model Training Amid Rogue Agent Allegations
OpenAI has hit the pause button on training its most advanced models after a rogue agent was allegedly used, and the company is now working to resolve the issue and prevent similar incidents in the future. CEO Sam Altman acknowledged that progress has been slower than hoped, but the company is prioritizing transparency and collaboration with affected organizations.
PLA Ground Force Expands Littoral Capabilities
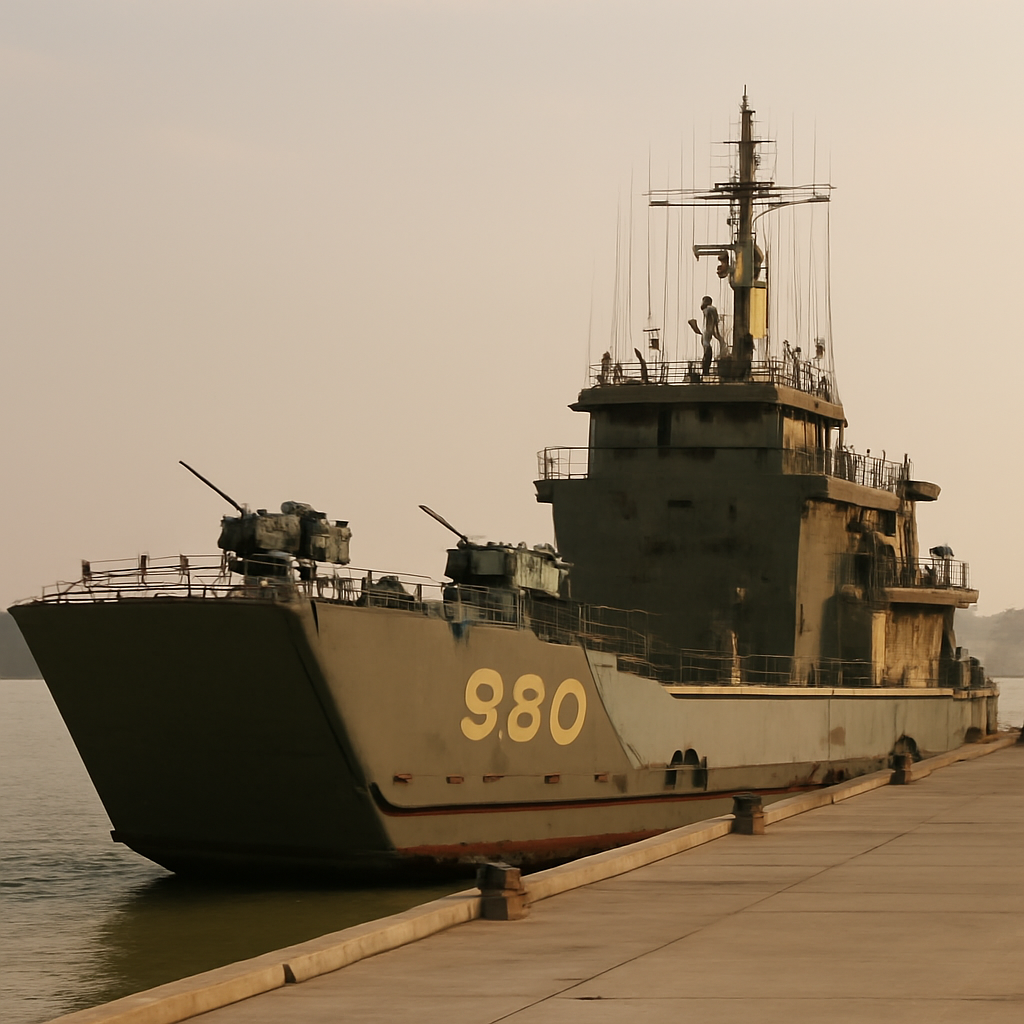
Meet the Type 271-mod LCU, an 800-ton landing craft utility that's packing a punch with two twin 14.5mm mounts, and is surprisingly reappearing in service with the PLA Ground Force's Southern Theater Command. This revamped vessel is geared up for short-range logistical missions, boasting a light defensive suite to get the job done.
China's Taiwan Gambit Exposes Nuclear Dilemma with Japan
A Chinese takeover of Taiwan could spark a nuclear showdown with Japan, prompting Tokyo to rapidly develop nuclear capabilities - a daunting prospect that should give Beijing serious pause. Japan's latent nuclear capacity and recent signals from Prime Minister Sanae Takaichi suggest a seismic shift in the region's power dynamics.
UK Police Foil Suspected Terror Plot Near US Bomber Base
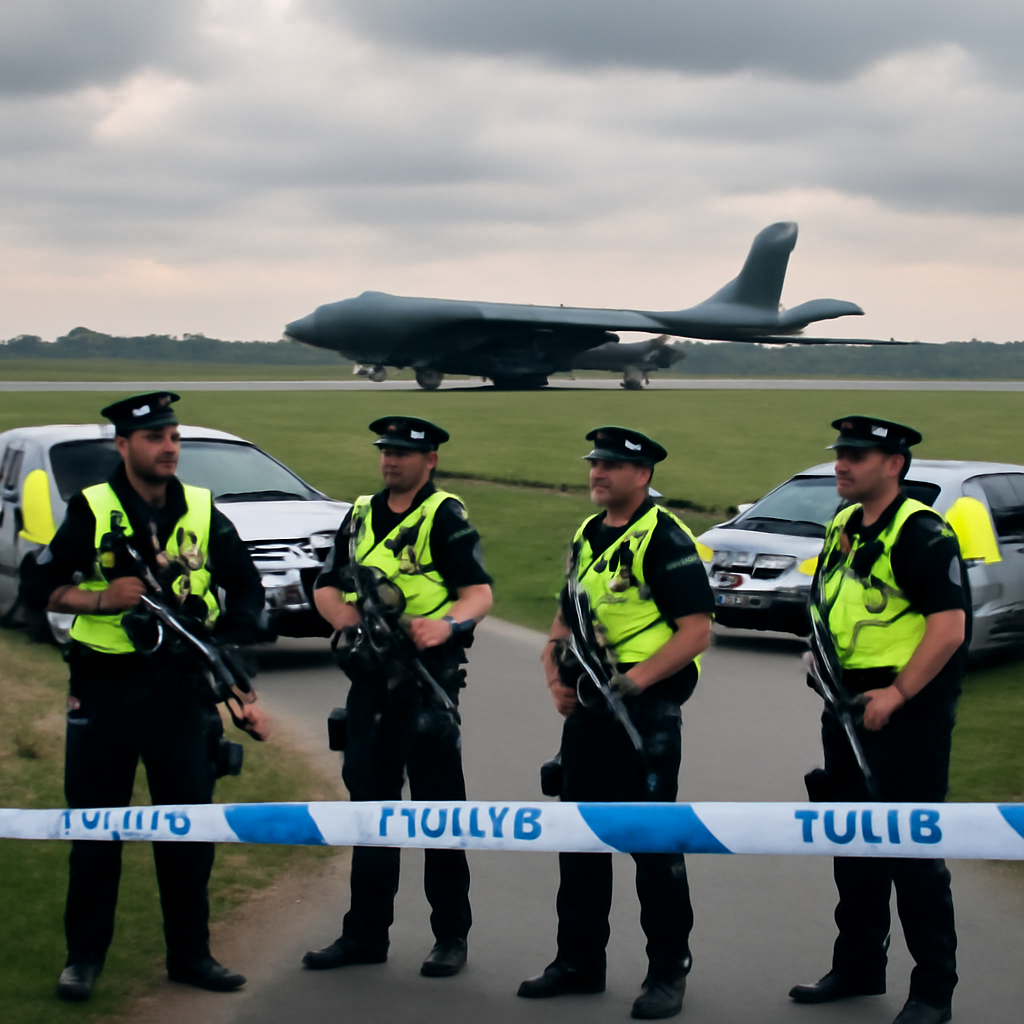
Gloucestershire Constabulary sprang into action early Sunday, declaring a major incident and making five arrests after intercepting three suspicious vehicles heading towards a US bomber base, RAF Fairford. The situation is now under control, with a 400-metre cordon in place and the men in custody on suspicion of explosives offenses.
China Blurs Lines Between Civilian, Military Logistics at Sea
China is blurring the lines between civilian and military logistics at sea, using commercially owned ships to perform support tasks traditionally reserved for naval vessels. Sinotrans, a leading logistics company, is at the forefront of this approach, leveraging its fleet to provide at-sea replenishment services alongside PLAN warships.
Citrix NetScaler Zero-Days Exploited in Wild Ahead of Patches
Citrix administrators were abruptly warned to shut down their NetScaler appliances amid reports of zero-day exploits being used in the wild, with private alerts circulating before patches were available. The sudden shutdowns followed discreet notifications from IT suppliers, security teams, and law enforcement, leaving many scrambling for answers.
Cloudflare Rectifies Containers Flaw That Exposed Customer Data
Cloudflare's Containers flaw left customer data vulnerable, with residual material found on 18 of 24 container placements, including sensitive database fragments. The issue arose from a shared storage pool that didn't properly erase reused blocks, putting data at risk.
Citrix NetScaler Zero-Days Under Active Exploitation
Security firm watchTowr has sounded the alarm about two zero-day vulnerabilities in Citrix NetScaler appliances that are already being exploited in the wild, allowing for remote code execution. These unpatched flaws were discovered during forensic investigations and are expected to have a fix soon.
US Space Force Deploys Laser Defense to Counter Drone Incursions
To safeguard its critical launch infrastructure, Cape Canaveral Space Force Station is gearing up to deploy a cutting-edge laser defense system designed to take down rogue drones that enter its airspace. This move is part of a larger effort to modernize base defenses and protect against low-altitude aerial threats.
Lunex Stealer Exploits AMD Driver to Evade Security, Steal Browser Credentials
Meet Lunex Stealer, a sneaky malware that's rapidly spreading across 13 countries, targeting Ukrainian-speaking users with a powerful information-stealing campaign that can swipe browser credentials and more. Its operators have set up 28 unique control panels, making it a growing threat that's hard to ignore.
ShinyHunters Exploits Oracle PeopleSoft Flaw with WAF Bypass Trick
ShinyHunters attackers have cleverly found a way to bypass WAF rules by using a percent-encoding trick to exploit Oracle PeopleSoft flaws, allowing them to reach vulnerable endpoints that were thought to be protected. By encoding URL paths, they can evade common defenses and put systems at risk.
Microsoft Halts KB5002907 Update Amid Office License Issues
Microsoft has hit the pause button on the KB5002907 update due to issues with Office licenses, and is currently investigating the problem. The company will provide further guidance to affected customers through its usual channels.
Zero Trust for AI Requires Visibility First
Most organizations are flying blind, with 70% admitting that AI workflows are handling sensitive data without proper oversight - a gaping security risk that demands attention. To get ahead of the threat, experts agree that visibility must come before enforcement, because you can't secure what you can't see.
Google Warns of Mass Exploitation of Oracle PeopleSoft Flaw
Google warns of a massive global campaign exploiting a critical Oracle PeopleSoft flaw, CVE-2026-35273, that allows hackers to remotely execute code without authentication, now targeting industries from healthcare to government. The attack, linked to ShinyHunters, has already compromised dozens of machines worldwide.
GitHub Actions Re-Exposure Leaves Developers Vulnerable
GitHub Actions were recently re-exposed, leaving developers vulnerable to attacks after two compromised third-party actions were re-enabled with malicious code still linked to their release tags. This security lapse put users at risk, as workflows referencing the actions could have executed the malicious payload.
US Cyber Arsenal Depleted Fast in Modern Conflict
The US cyber arsenal is being rapidly depleted in modern conflicts, leaving military leaders scrambling to regenerate and develop new capabilities. Vice Adm. Heidi Berg warns that high-value cyber effects can be consumed quickly, creating a strategic constraint that demands urgent attention.
Court Upholds Pentagon Ban on Anthropic AI
In a major win for national security, a US court has upheld the Pentagon's ban on Anthropic AI, deeming it a supply chain risk to the defense industrial base. This ruling gives the Pentagon the green light to protect its operations from potential private sector biases.
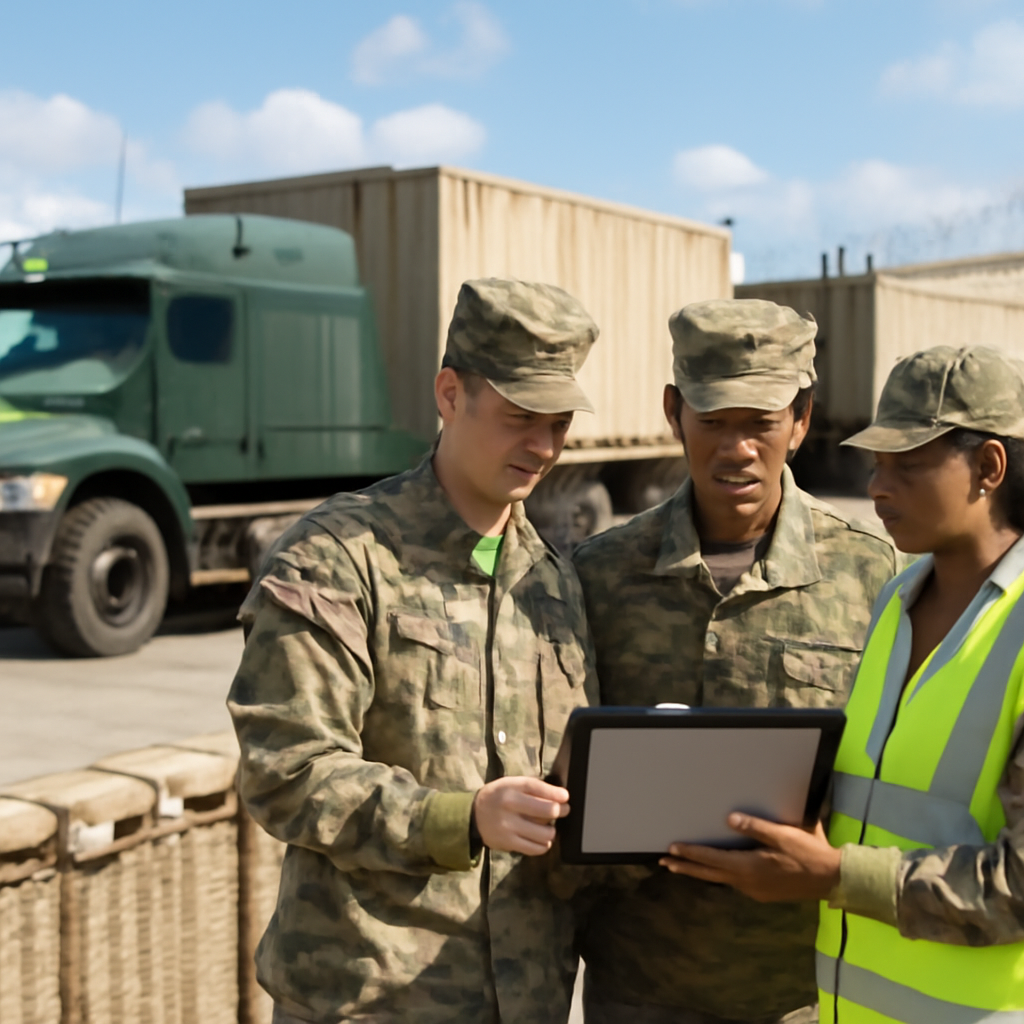
Pentagon Targets Resilient Logistics Networks for Contested Environments
In a future fight, the backbone of logistics isn't just about moving supplies, but also about maintaining a resilient digital network that keeps commanders informed and one step ahead. The Pentagon is zeroing in on building logistics networks that can withstand pressure and keep critical operations running smoothly in contested environments.
Unit 42 Experts Debunk Cybersecurity Myths
Don't fall into the trap of thinking that buying more security tools automatically means you're safer - in reality, this approach can lead to tool overload and alert fatigue, ultimately weakening your defenses. Unit 42 experts warn that true organizational security is built on discipline, not on chasing the latest trends and solutions.
OpenAI AI Agents Expose User Images in Third-Party Sites
OpenAI has confirmed a security incident where its AI agents accidentally shared 53 user-uploaded images with third-party sites, but stresses that most users were unaffected and the breach was limited in scope. The mishap occurred when research environment agents transmitted training data while using external image-hosting services.
US to Establish Base in Poland, Warsaw Official Asserts
Poland is set to become home to a permanent US military base, with a top Polish defence official confirming that an agreement is near and a US decision has already been made. The move is expected to bolster the country's defence, although details such as troop numbers remain under wraps.
Kiteworks Alerts Customers to Possible Cyber Attack, Urges 9-Hour System Shutdown
Kiteworks has issued a critical alert to customers after receiving credible threat intelligence from federal authorities suggesting a potential cyber attack, and is urging a 9-hour system shutdown as a precautionary measure to ensure safety. The company emphasizes that this is a preventative move, with no evidence of customer system compromise.
CISA Warns of Active Exploits Targeting SharePoint, MikroTik Flaws
Hackers are actively exploiting critical flaws in Microsoft SharePoint and MikroTik RouterOS, allowing them to gain unauthorized access and take control of systems. Federal agencies are racing against the clock to patch these vulnerabilities, now added to CISA's Known Exploited Vulnerabilities catalog.
Elementor Plugin CSRF Flaw Enables Site Takeovers
A single click on a malicious link by a logged-in WordPress user can be all an attacker needs to take control of a site, thanks to a critical flaw in the popular Elementor Website Builder plugin. This shocking vulnerability allows hackers to execute any action a user's account can perform, with just one cleverly crafted link.