Tag: emerging threats
8516 articles
Google Deploys AI Security Agents to Counter Emerging Threats
Google is ramping up its cybersecurity game by deploying AI-powered security agents that can detect and fix threats at lightning-fast speeds, with human oversight to ensure these digital defenders stay on track. By leveraging its full AI stack, Google aims to stay ahead of emerging threats and revolutionize its defense strategy.

Lotus Wiper Malware Disrupts Venezuelan Energy Sector
Cybersecurity researchers uncovered a highly destructive malware, known as Lotus Wiper, that was used to disrupt Venezuela's energy sector in a targeted attack. This powerful data wiper was deployed in a series of devastating attacks at the end of 2025 and beginning of 2026.

Former Ransomware Negotiator Pleads Guilty to Aiding BlackCat Cyber Gang
A former ransomware negotiator turned rogue, Angelo Martino has pleaded guilty to aiding the notorious BlackCat cyber gang, betraying his employer and the industry he was meant to serve. By secretly collaborating with BlackCat, Martino launched devastating ransomware attacks, causing harm to innocent victims and lining his own pockets.
Microsoft Graph API Change Disrupts Universal Print Sharing
Microsoft revealed that a recent code change to the Microsoft Graph API caused a ripple effect, introducing a critical error that disrupted Universal Print sharing and left many users in a frustrating limbo. The error sparked a chain reaction, exposing a long-standing issue that prevented share operations from completing as expected.
Researchers Expose ProxySmart Software Behind Global SIM Farms
Meet ProxySmart, a sneaky software powering "SIM Farm as a Service" operations worldwide, with a massive footprint of 94 phone farms across 17 countries and 19 US states. Its creators, a Belarus-based vendor, have made it easy for operators to run mobile proxy infrastructure at commercial scale.
Harvester Malware Exploits Microsoft Graph API for Stealthy Linux Attacks
Meet Harvester, a stealthy espionage group believed to be state-backed, that's been secretly targeting telecommunications, government, and IT organizations in South Asia since 2021. Their latest trick? A Linux-capable GoGra backdoor that uses Microsoft Graph API for covert communications.
Terrarium Sandbox Flaw Enables Code Execution, Container Escape
A critical flaw in Terrarium's sandbox, rated 9.3 on the CVSS scale, allows attackers to break free from container constraints and execute code with root privileges. This alarming vulnerability, tracked as CVE-2026-5752, stems from a JavaScript prototype chain traversal that lets sandboxed code run amok on the host Node.js process.
Mustang Panda Expands LOTUSLITE Malware to Target India, Korea
Meet the evolved LOTUSLITE backdoor, now wielding dynamic DNS-based command-and-control over HTTPS, enabling its operators to remotely access and manipulate targeted systems for espionage purposes. This sophisticated malware supports remote shell access, file operations, and session management, a potent toolkit for data collection and access persistence.

Microsoft Disrupts ASP.NET Flaw Allowing SYSTEM Privilege Escalation
Microsoft has patched a critical ASP.NET Core vulnerability, CVE-2026-40372, that allowed unauthenticated attackers to forge authentication cookies and gain SYSTEM privileges on affected devices. This fix addresses a flaw in the ASP.NET Core Data Protection cryptographic APIs that could be exploited for privilege escalation.
UK Faces Rising Nation-State Cyber Threats Amid Tech Advances
The UK is bracing for a perfect storm of cyber threats, with the National Cyber Security Centre warning of a tumultuous decade ahead, driven by rapid technological change and rising geopolitical tensions. Nation-state threats from China, Russia, and Iran are already targeting UK firms, with 204 significant incidents recorded in the last review.
Unpatched SharePoint Servers Exposed to Ongoing Spoofing Attacks
Over 1,300 Microsoft SharePoint servers are still vulnerable to a spoofing attack, despite a security update being available since last week, leaving them exposed to ongoing exploitation by hackers. This comes after Microsoft warned that the CVE-2026-32201 vulnerability was exploited as a zero-day, and attackers are continuing to abuse it in widespread campaigns.
Mozilla Sees AI-Powered Bug Detection as Game-Changer for Security
Mozilla's CTO, Bobby Holley, exclaims that AI-powered bug detection is a game-changer for security, giving defenders a decisive edge. This innovative technology, tested on Firefox releases, has already uncovered hundreds of vulnerabilities, outpacing traditional automated fuzzers and human researchers.
US Navy Bolsters Air Defense with Patriot PAC-3 Missiles
The US Navy is taking a major leap forward in air defense with a new contract awarded to Lockheed Martin, integrating the advanced Patriot PAC-3 Missile Segment Enhancement (MSE) with the Aegis Combat System. This game-changing move, backed by a $1.73 billion budget, will equip the Navy with 405 cutting-edge PAC-3 MSE missiles.
Lawmakers Weigh Terrorism Labels for Hospital Ransomware Attacks
Lawmakers are considering slapping terrorism labels on ransomware attacks targeting hospitals, a move that could lead to severe penalties for those responsible, as Rep. Michael Guest says there should be no penalties too severe for individuals that target the healthcare system. This tough stance comes as experts and officials discuss ways to deter the growing threat of hospital ransomware attacks.

Pentagon Targets $55 Billion for Drone and Autonomy Development
The Pentagon is pushing the boundaries of innovation with a $55 billion investment in drone and autonomy development, led by the Defense Autonomous Warfare Group (DAWG) - a pathfinder for cutting-edge technology that's accelerating progress in low-cost, attritable platforms. DAWG is already live-testing systems and tools with top companies, providing real-time feedback to drive growth.
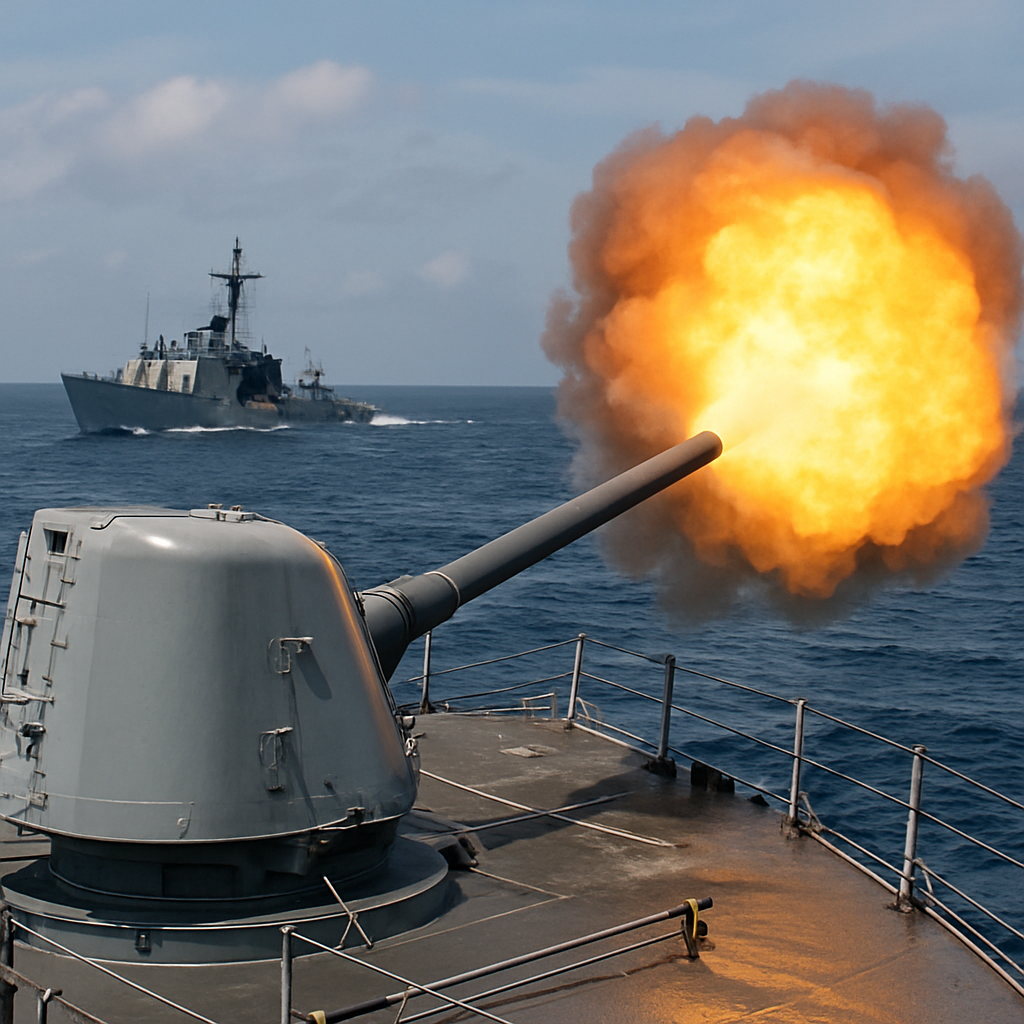
US Navy Fires Deck Gun at Ship in Combat for First Time in 38 Years
In a historic move, the US Navy fired its deck gun at a ship in combat for the first time in nearly four decades, with the USS Spruance blasting an Iranian cargo vessel on April 19, 2026. The rare display of gunfire, involving a 5-inch MK 45 gun, left a hole in the unarmed Touska's engine room, but the freighter remained afloat.
Scotland Hacker Pleads Guilty in Scattered Spider Cybercrime Case
Meet Tyler Robert Buchanan, the 24-year-old mastermind behind the notorious Scattered Spider cybercrime gang, who has pleaded guilty to federal charges of conspiracy and identity theft. With a potential 22-year prison sentence looming, Buchanan's guilty plea marks a major win for law enforcement in the fight against cybercrime.
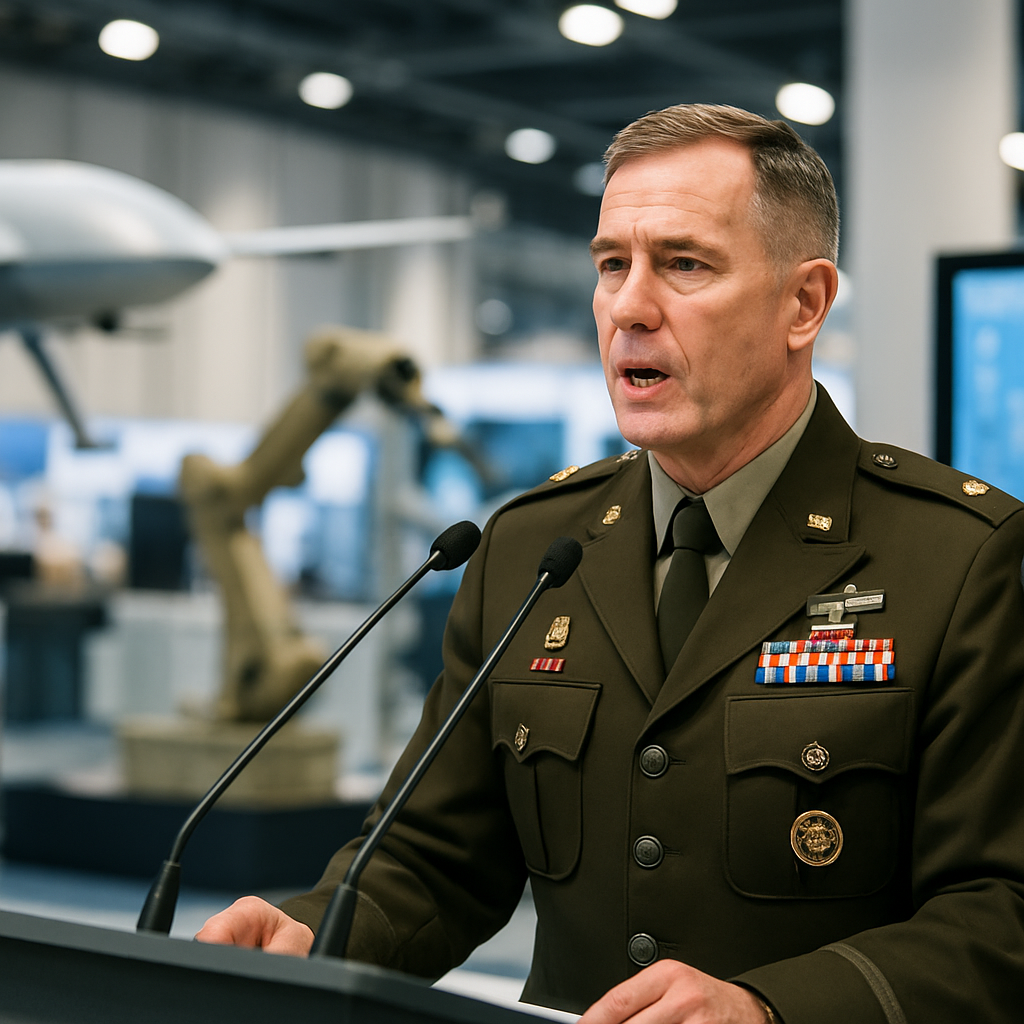
Sea Air Space Showcases Emerging Defense Tech
At Sea Air Space 2026, senior military officials took the stage to share insights, while attendees got hands-on with the latest defense innovations at National Harbor, Md. The event brought together formal remarks and immersive exhibitions, showcasing the future of defense technology.
Former Ransomware Negotiator Pleads Guilty to Extortion Scheme
A former ransomware negotiator has pleaded guilty to masterminding a brazen extortion scheme that raked in a staggering $75.3 million, exploiting his position to secretly collude with ransomware gangs and betray the very companies he was supposed to protect. Angelo John Martino III faces up to 20 years in prison for his role in the conspiracy.
Australia's Defence Tech Push Exposes Funding, Scale Gaps
Australia's defence tech push is hitting a roadblock, with a significant gap in funding and scale hindering progress. With a proposed A$500 million investment, the Advanced Capability Investment Fund aims to bridge this gap and catalyse private equity in critical areas like AI, quantum, and autonomy.

Pakistan Navy Bolsters Anti-Surface Warfare with Taimoor Missile Test
The Pakistan Navy has successfully test-fired its Taimoor air-launched cruise missile, a game-changing addition to its anti-surface warfare capabilities that can strike targets on land and sea with precision. This powerful new tool is set to bolster the Navy's maritime strike and deterrence abilities.
Australia Aligns Defence Strategy with US Balance of Power Push
Australia's new 2026 National Defence Strategy is taking a bold stance, shifting its focus from upholding a rules-based order to actively shaping the regional balance of power in the Indo-Pacific. By strengthening its alliance with the US, Australia aims to safeguard its economic interests and play a key role in defining the region's future dynamics.
Pentagon Bolsters Cyber Budget with $20.5B Allocation
The Pentagon is shoring up its defenses with a $20.5 billion cyber budget allocation, aimed at outsmarting adversaries who are increasingly sophisticated in their digital threats. This major investment is part of a broader strategy to integrate cyber capabilities across all warfighting domains and safeguard military networks.

US OPM Health Data Collection Plan Sparks Privacy Concerns
The Office of Personnel Management wants to collect detailed, identifiable health records from the 65 health insurers that cover over 10 million federal and postal service employees, retirees, and their families - a move that's raising concerns about privacy. The proposed data collection would include medical claims, pharmacy claims, and provider data to help OPM oversee health benefits programs.