Tag: emerging threats
8516 articles
Discord Group Exploits Claude's Secret AI Model
A fresh controversy is brewing over Anthropic's highly touted AI model, Mythos, after a Discord group exploited a secret pathway to access the powerful technology. The AI Security Institute had praised Mythos as a significant leap forward, but its limited release to select partners like Nvidia and Apple has raised new questions about access control.
UK Battles Rising Russian Cyber Hostility
The UK is facing a surge in Russian cyber hostility, with the National Cyber Security Centre (NCSC) now handling around four major attacks every week and over 200 nationally significant incidents annually. This alarming trend highlights the growing importance of cyber operations in modern warfare.
Kyber Ransomware Targets Windows, VMware with Post-Quantum Encryption
Meet the Kyber Ransomware, a potent threat that targets both Windows and VMware environments with cutting-edge, post-quantum encryption. This sophisticated malware has been found to strike multiple systems at once, as seen in a March 2026 incident where two variants were deployed on the same network.
Malicious Docker Images Compromise Checkmarx Supply Chain
Malicious Docker images compromised the Checkmarx supply chain by embedding a tampered KICS binary that secretly collected and sent sensitive data to an external endpoint. This sneaky data-exfiltration risk put users at risk, thanks to an altered scan report generated by the poisoned image.
Malware Worm Exploits npm Packages to Hijack Developer Tokens
Meet CanisterSprawl, a sneaky self-propagating worm that's compromising npm packages and using stolen developer tokens to spread its reach. This malware goes beyond just stealing credentials, turning one infected environment into a web of additional package compromises.
Breach Exposes Anthropic's AI Model Vulnerability
A shocking security breach has exposed a vulnerability in Anthropic's advanced AI model, Mythos, allowing unauthorized users to gain access by simply changing a model name. This incident raises serious concerns about the safety and reliability of cutting-edge AI technology.
MacOS Attacks Evolve, Exploiting Native Tools for Stealth
As macOS use surges in enterprise environments, accounting for over 45% of organizations, attackers are getting creative - exploiting native tools like Remote Application Scripting, Terminal, and AppleScript to stealthily run code, move undetected, and evade security measures. Cisco Talos warns that these tactics allow hackers to issue malicious instructions across processes and systems without triggering conventional monitoring.
Harvester Expands Linux Arsenal with GoGra Backdoor in South Asia
Harvester's Linux arsenal just got a boost with the deployment of the GoGra backdoor in South Asia, enabling the threat actor to sneak past traditional network defenses by hijacking legitimate Microsoft Graph API and Outlook mailboxes. This latest move is linked to Harvester's earlier espionage campaigns targeting key sectors in the region.
Hackers Expose 19M Records in French Government Agency Breach
A recent data breach at France's Agence nationale des titres sécurisés (ANTS) may have compromised 19 million records, but thankfully, no action is required from users - for now. The agency is notifying affected individuals and advising them to stay vigilant for suspicious contacts.

Spanish Police Disrupts $4.7M Manga Piracy Platform, Arrests Four
In a major crackdown on piracy, Spanish police have shut down a massive manga piracy platform that had been illegally providing access to millions of copyrighted works since 2014, and arrested four individuals in connection with the operation. The platform's systematic infringement had amassed a huge following, but ultimately led to the authorities taking action.
NCSC Unveils SilentGlass to Secure Monitors from Cyber-Attacks
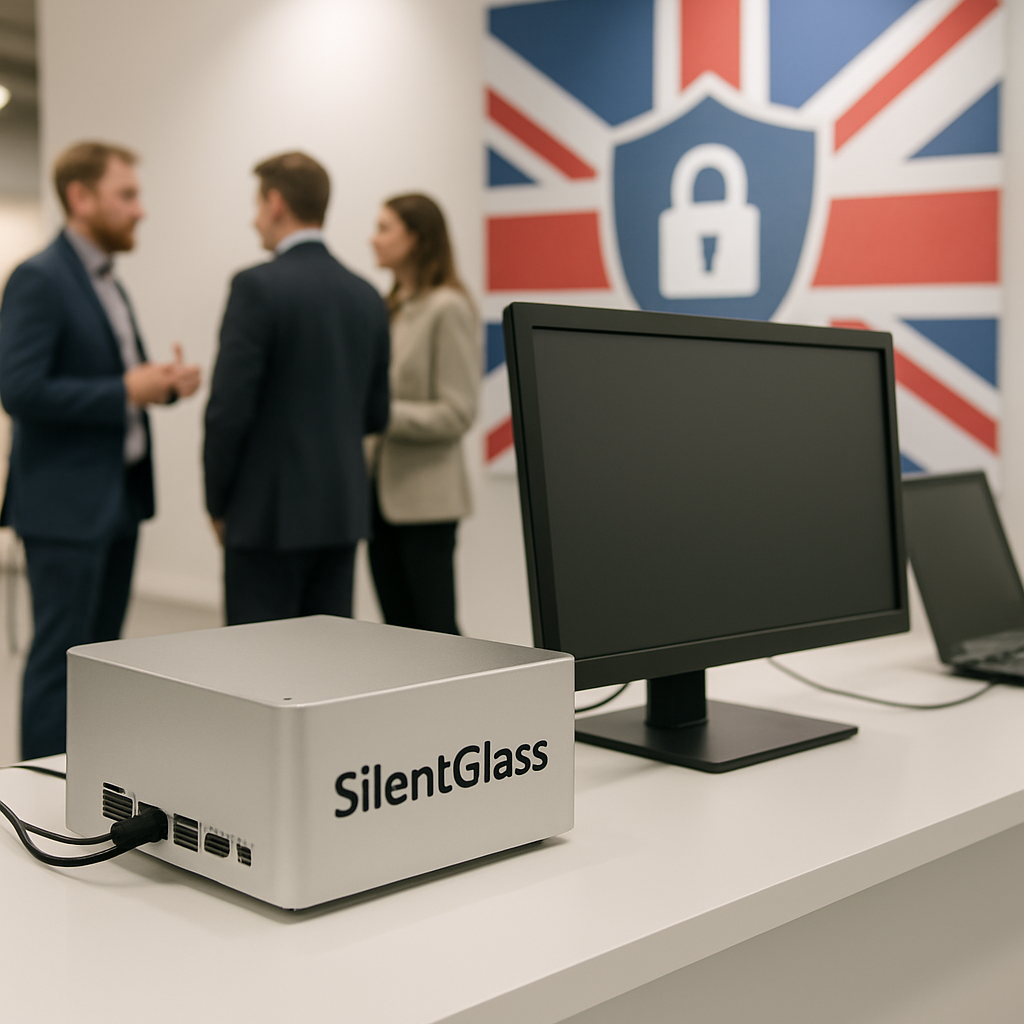
Meet SilentGlass, a game-changing plug-and-play device that shields your monitors from cyber threats with unprecedented ease, protecting your business's vulnerable IT infrastructure. This innovative solution actively blocks malicious attacks between HDMI or DisplayPort connections and monitor screens, safeguarding even the most high-threat cybersecurity environments.
Cybercrime Shifts to Caller-as-a-Service Model
US elderly citizens alone lost a staggering $3.4B in 2023 to phone-based scams, highlighting the alarming rise of a highly organized and profitable fraud economy. This Caller-as-a-Service model has made it easier for scammers to specialize and scale their operations, putting even more people at risk.
UK Bolsters Cybersecurity with £90m Funding and Resilience Push
The UK government is stepping up its cyber defence game with a £90m funding boost to help small and medium-sized businesses bolster their cyber resilience and protect against growing online threats. This move aims to support organisations in implementing essential cyber security standards.
US Space Force Grapples with Workforce Rebuild Amid $71 Billion Budget Surge
The US Space Force is making a bold move with a proposed $71.1 billion budget for 2027, more than doubling its current allocation to supercharge the development of new space-based capabilities and accelerate key programs. This massive investment surge aims to propel the service's ambitious plans for national security space launches, missile warning systems, and cutting-edge GPS technology.
CISOs Face New Era of AI-Driven Threats
The old security measures are no longer enough - a 'passed' audit only tells you where you've been, not where you are now, in a threat landscape rapidly changed by AI-driven attacks. Advanced AI tools can now discover and exploit weaknesses at unprecedented speeds and scales, outpacing traditional security methods.
Wi-Fi Encryption Flaws Expose Enterprises to AirSnitch Attacks
Enterprises are in grave danger of being hacked through their Wi-Fi networks, as newly discovered AirSnitch attacks can bypass WPA2 and WPA3-Enterprise encryption, exposing sensitive credentials and backend systems to both insider and remote threats. This critical vulnerability undermines the very foundations of wireless network security.
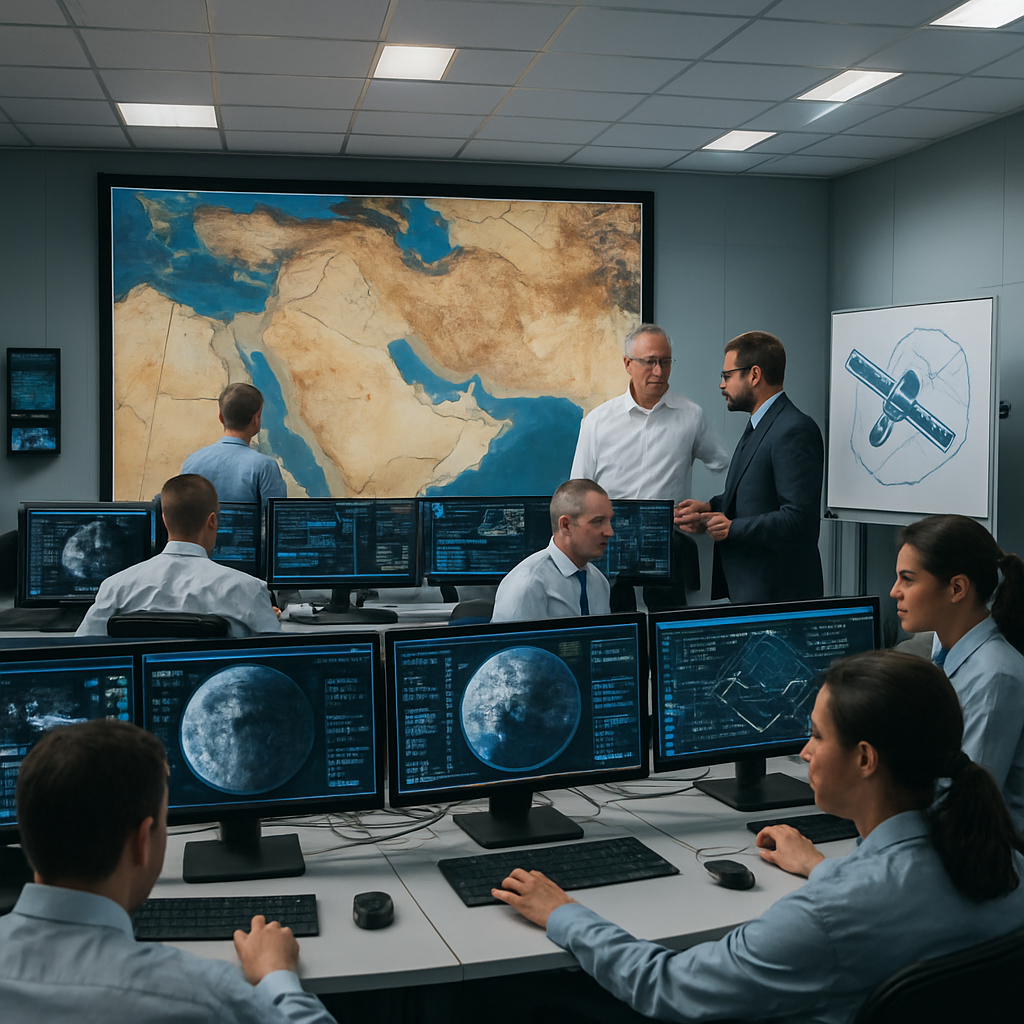
China Fuels Iran's Conflict with Dual-Use Tech Transfers
China has reportedly supplied Iran with a commercial reconnaissance satellite, giving Tehran the capability to strike US military facilities in the Middle East with precision. This move has escalated tensions in the region, with Chinese companies Earth Eye Co and Emposat allegedly involved in the transfer.

AI Reshapes Cybersecurity With Renewed Focus on Fundamentals
Artificial intelligence is revolutionizing cybersecurity by refocusing efforts on timeless fundamentals, empowering agencies to make informed decisions with the help of established frameworks like the NIST Cybersecurity Framework. By layering new AI-related risks over existing ones, Cheri Pascoe, Director of the National Cybersecurity Center of Excellence at NIST, highlights the need for a strategic approach to tackle these emerging threats.
ICE Taps Graphite Spyware for Operations
US Immigration and Customs Enforcement (ICE) has confirmed it uses spyware from Israeli company Graphite, raising questions about the scope and implications of this partnership. The admission is a significant revelation, but many details remain unclear.
Phishing Attacks Exploit Email Blind Spots with Silent Subject Lines
Phishing attacks are on the rise, with a 13.9% surge in January and February, followed by a 7% increase in March, and cybercriminals are getting sneaky by using empty subject lines to bypass email defenses and pique human curiosity. By ditching the subject line, attackers are exploiting a blind spot that can trick both automated filters and human instincts.
npm Ecosystem Targets New Supply-Chain Attack to Steal Auth Tokens
Researchers have uncovered a sneaky supply-chain worm that can hijack auth tokens and spread malware through the npm ecosystem, putting countless packages at risk. This stealthy threat can inject itself into every package it can publish, creating a ripple effect of compromised code.

UK Judges Uphold Police Use of Live Facial Recognition in London
The High Court has ruled that the Metropolitan Police Service can continue using live facial recognition in London, confirming that the technology is lawful and effective in keeping the public safe. This decision is a major win for the MPS, which has been using LFR to tackle crime and protect Londoners.
France's ID Agency Probes Breach Claiming 19M Records Stolen
A massive data breach at France's ID agency may have exposed a staggering 19 million records, putting the personal info of nearly a third of the country's population at risk. The breach, detected on April 15, involves the theft of sensitive data, including login IDs, names, email addresses, and dates of birth.
Cross-App Permissions Expose Hidden Risks in AI-Driven SaaS Environments
Imagine a single security slip-up exposing 1.5 million API tokens and 35,000 email addresses, leaving AI agents and their users vulnerable to hijacking and misuse. The recent Moltbook breach reveals the hidden risks of cross-app permissions in AI-driven SaaS environments.